---
version: "Working version"
language: "en"
---
# Soteri Support Home
## Soteri Support Home
Soteri's support team is here to answer your questions about our products!
*
### [Trials and Evaluations of Soteri's Atlassian Apps](https://docs.soteri.io/support/latest/atlassian-app-trials-evaluations.md)
*
#### [Licensing and Pricing for Soteri's Atlassian Apps](https://docs.soteri.io/support/latest/licensing-and-pricing-for-soteri-s-atlassian-apps.md)
*
#### [Soteri's Security Practices](https://docs.soteri.io/support/latest/soteri-s-security-practices.md)
*
#### [Software End User License Agreement](https://docs.soteri.io/support/latest/software-end-user-license-agreement.md)
*
#### [Service Level Agreement](https://docs.soteri.io/support/latest/service-level-agreement.md)
*
#### [Privacy Policy](https://docs.soteri.io/support/latest/privacy-policy.md)
*
#### [Data Processing Addendum](https://docs.soteri.io/support/latest/data-processing-addendum.md)
*
#### [Financial Services Addendum](https://docs.soteri.io/support/latest/financial-services-addendum.md)
*
#### [Soteri's Cloud App Data Subprocessors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md)
---
version: "Working version"
language: "en"
---
# Trials and Evaluations of Soteri's Atlassian Apps
You can try any of [Soteri's apps for Atlassian host products](https://marketplace.atlassian.com/vendors/1219549/soteri) for free for 30 days on both Data Center and Cloud.
## How to start a trial of a Soteri app
Use the "Try it now" button on any of our Atlassian Marketplace listings to get a 30-day evaluation license. Be sure to select "Data Center" or "Cloud", depending on which app version you want to try.
* [Soteri Security for Confluence](https://marketplace.atlassian.com/apps/1224167/security-for-confluence-enhanced-secret-scanner-by-soteri)
* [Soteri Security for Jira](https://marketplace.atlassian.com/apps/1229376/security-for-jira-enhanced-secret-scanner-by-soteri)
* [Soteri Security for Bitbucket](https://marketplace.atlassian.com/apps/1221399/security-for-bitbucket-enhanced-secret-scanner-by-soteri)
You'll need administrator privileges to install the app. Reference Atlassian's documentation [Installing Marketplace apps](https://confluence.atlassian.com/upm/installing-add-ons-273875715.html) for more information.
## What an evaluation license includes
30-day trials give you **full access** to Soteri's apps. You'll also have access to Soteri's support team via our [support portal](https://support.soteri.io/).
## Extending a trial / renewing an evaluation license
Evaluation licenses end automatically after 30 days. If you need more time, you can to reach out to the [Atlassian Customer Advocate team](https://www.atlassian.com/company/contact/purchasing-licensing?utm_medium=docs&utm_source=easy-agile-user-story-maps&utm_campaign=trial-installation#/). They'll also require approval from Soteri. You can [open a ticket in our support portal](https://support.soteri.io/) to explain the situation.
### Why am I seeing a "You have reached the maximum number of trial licenses" message?
The Atlassian Marketplace only allows our customers to extend Data Center app trials with explicit approval.
To continue using the app, you'll need to purchase a license. Generating excessive numbers of data center evaluation licenses [constitutes a violation of our EULA](https://docs.soteri.io/support/latest/software-end-user-license-agreement.md).
## Help with trials / evaluations
**Billing and licensing for Soteri's Atlassian apps are handled via the Atlassian Marketplace.** Most issues with billing or licensing will have to be handled by [Atlassian's billing and licensing team](https://www.atlassian.com/company/contact/purchasing-licensing#/), including:
* Generating new evaluation licenses
* Renewing evaluation licenses
* Generating quotes or purchase orders
* Issues with payments, bills, or refunds
If you have issues with any of the above, please contact [Atlassian's billing and licensing team](https://www.atlassian.com/company/contact/purchasing-licensing#/).
For other questions, you can reach out to Soteri's support team via our [support portal](https://support.soteri.io/).
---
version: "Working version"
language: "en"
---
# Data Processing Addendum
*Effective Date* : 2026-04-22
This Data Processing Addendum ("DPA") forms part of the End User License Agreement (the "Agreement" or "EULA") between Soteri LLC ("Processor", "Soteri", "we", "us") and the customer entity identified ("Controller", "Customer", "you"). This DPA applies to the extent that Soteri processes Personal Data on behalf of Customer in providing the following products (the "Services"):
* **Security for Confluence PII \& Secret Scanner -** Confluence Cloud edition
* **Security for Jira PII \& Secret Scanner** - Jira Cloud edition
Terms not defined in this DPA have the meaning given to them in the Agreement. In the event of a conflict between this DPA and the Agreement, this DPA shall prevail with respect to the processing of Personal Data.
*** ** * ** ***
## 1. Definitions
**"Personal Data"** means any information relating to an identified or identifiable natural person that Soteri processes on behalf of Customer in connection with the Services.
**"Processing"** means any operation performed on Personal Data, including collection, use, storage, transmission, and deletion.
**"Data Protection Laws"** means all applicable laws relating to the processing of Personal Data, including the EU General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), and any other applicable privacy legislation.
**"Sub-processor"** means a third party engaged by Soteri to process Personal Data on behalf of Customer.
**"Security Incident"** means a confirmed unauthorized access to, or unauthorized disclosure of, Customer Personal Data.
*** ** * ** ***
## 2. Scope and Purpose of Processing
### 2.1 Nature of Processing
The Services scan content within Customer's Atlassian Cloud instance for passwords, API keys, PII, and other secrets. Content is processed (scanned) but **not stored** by Soteri. Soteri stores only metadata related to findings --- specifically, the location of a detected secret, the type of secret, and when it was introduced or remediated.
### 2.2 Categories of Personal Data
As disclosed on the Atlassian Marketplace Privacy \& Security tab for each app, the following types of End-User Data may be processed and stored:
* Content metadata (e.g., Issue IDs, Content IDs)
* User IDs (but not PII like email addresses)
* Base URL (Account data)
* Application-specific configuration (e.g., scanning rule configuration)
Content scanned by the Services is processed but not stored.
### 2.3 Categories of Data Subjects
* Users of Customer's Atlassian Cloud instance (Confluence and/or Jira)
### 2.4 Duration of Processing
Processing continues for the term of the Agreement. Upon termination or uninstallation, stored End-User Data (metadata) is retained for a minimum of 35 days and a maximum of 90 days post-uninstall, after which it is deleted.
*** ** * ** ***
## 3. Obligations of Soteri as Processor
### 3.1 Instructions
Soteri shall process Personal Data only in accordance with Customer's documented instructions as set out in this DPA and the Agreement, unless required to do so by applicable law. If Soteri becomes aware that an instruction infringes Data Protection Laws, it shall promptly notify Customer.
### 3.2 Confidentiality
Soteri ensures that all personnel authorized to process Personal Data are bound by confidentiality obligations. Soteri requires employees to sign confidentiality agreements during onboarding, as described in Section 5.1 of the SOC 2 report.
### 3.3 Security Measures
Soteri implements appropriate technical and organizational measures to protect Personal Data. These measures are described in Soteri's SOC 2 Type II report, available upon approval from the [Soteri Trust Center](https://soteri.safebase.us/). Key measures include:
* Encryption of data at rest and in transit
* Role-based access controls with least-privilege principles
* Multi-factor authentication for production systems
* Regular vulnerability scanning
* Formal incident response procedures
* Full-disk encryption on all employee devices via MDM
* Network segmentation to prevent unauthorized access to customer data
For full details, refer to the SOC 2 Type II report (Section 3: System Description).
### 3.4 Security Incidents
Soteri shall notify Customer without undue delay upon becoming aware of a Security Incident. Notification shall include, to the extent available, the nature of the incident, categories and approximate number of data subjects affected, likely consequences, and measures taken or proposed to address the incident.
### 3.5 Data Subject Requests
Soteri shall assist Customer in responding to requests from data subjects exercising their rights under Data Protection Laws, to the extent Soteri is able to do so given the nature of the Processing.
### 3.6 Deletion and Return of Data
Upon termination of the Agreement or upon Customer's written request, Soteri shall delete Personal Data in accordance with the retention periods described in Section 2.4 and the [Data Management Policy](https://soteri.safebase.us/), unless retention is required by applicable law.
*** ** * ** ***
## 4. Sub-processors
### 4.1 Authorized Sub-processors
Customer grants Soteri general authorization to engage Sub-processors. A current list of Sub-processors engaged by Soteri in providing the Services, including their function and location, is maintained at [Soteri's Cloud App Data Sub-processors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md). That list is incorporated by reference into this DPA.
### 4.2 Changes to Sub-processors
Soteri will provide notice of material changes to its Sub-processors through the [Soteri Trust Center](https://soteri.safebase.us/). Customers are encouraged to subscribe to Trust Center updates to receive such notifications. Customer may object to a new Sub-processor by notifying Soteri at [hello@soteri.io](mailto:hello@soteri.io) within 30 days of being informed of the change. If Soteri is unable to reasonably accommodate the objection, Customer may terminate the affected Services.
### 4.3 Sub-processor Obligations
Soteri imposes data protection obligations on each Sub-processor no less protective than those in this DPA. Soteri reviews Sub-processor compliance attestation reports at least annually, as described in the SOC 2 report (Section 3.5.1 and DC 7).
*** ** * ** ***
## 5. International Data Transfers
Personal Data is processed and stored in the **United States** . For transfers of Personal Data from the European Economic Area, the United Kingdom, and Switzerland to the United States, Soteri relies on its certification under the **EU-U.S. Data Privacy Framework (EU-U.S. DPF)** , the **UK Extension to the EU-U.S. DPF** , and the **Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF)** , as administered by the U.S. Department of Commerce. Soteri has certified that it adheres to the DPF Principles with respect to Personal Data received from the EU, UK, and Switzerland. For more information, see Soteri's [Privacy Policy](https://docs.soteri.io/support/latest/privacy-policy.md) and the DPF program website at [www.dataprivacyframework.gov](https://www.dataprivacyframework.gov/).
Soteri additionally maintains a SOC 2 Type II certification which provides assurance that appropriate security controls are in place. Google Cloud Platform, Soteri's hosting sub-processor, also maintains independent SOC 2 and ISO 27001 certifications.
*** ** * ** ***
## 6. Audits
Soteri shall make available to Customer, upon request, the SOC 2 Type II report and other information reasonably necessary to demonstrate compliance with this DPA. The SOC 2 report is available upon approval from the [Soteri Trust Center](https://soteri.safebase.us/). The parties agree that the SOC 2 report shall satisfy any audit rights granted to Customer under Data Protection Laws.
*** ** * ** ***
## 7. Compliance Certifications
Soteri holds the following certifications and participates in the following programs:
* **SOC 2 Type II** --- Yearly audits by an independent auditor
* **EU-U.S., UK Extension, and Swiss-U.S. Data Privacy Framework** --- self-certified with the U.S. Department of Commerce ([www.dataprivacyframework.gov](https://www.dataprivacyframework.gov/))
* **Atlassian Cloud Fortified** --- meeting the highest Marketplace standards for security, reliability, and support
* **Atlassian Marketplace Security Bug Bounty Program** participant
* **CAIQ Lite** respondent
Current certifications and attestations are available at the [Soteri Trust Center](https://soteri.safebase.us/).
*** ** * ** ***
## 8. Liability
Liability under this DPA is subject to the limitations set forth in the Agreement (EULA, Section 15).
*** ** * ** ***
## 9. General
### 9.1 Governing Law
This DPA shall be governed by the laws of the State of California, consistent with Section 19(a) of Soteri's EULA.
### 9.2 Contact
For data protection inquiries: [hello@soteri.io](mailto:hello@soteri.io)
For security issues: [security@soteri.io](mailto:security@soteri.io)
### 9.3 Updates
Soteri may update this DPA from time to time. The current version will always be available in Soteri's public facing documentation website.
### 9.4 Precedence
This DPA is incorporated into and forms part of the Agreement. In the event of a conflict between this DPA and the Agreement regarding the processing of Personal Data, this DPA shall control.
*** ** * ** ***
## Reference Documents
| Document | Location |
|-------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| End User License Agreement (EULA) | [EULA](https://docs.soteri.io/support/latest/software-end-user-license-agreement.md) |
| Privacy Policy | [Privacy Policy](https://docs.soteri.io/support/latest/privacy-policy.md) |
| Sub-processor List | [Soteri's Cloud App Data Sub-processors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md) |
| SOC 2 Type II Report | Available upon approval from [Soteri Trust Center](https://soteri.safebase.us/) |
| Data Privacy Framework Participation List | [www.dataprivacyframework.gov](https://www.dataprivacyframework.gov/) |
| Secure Development Policy | [Soteri Trust Center](https://soteri.safebase.us/) |
| Data Management Policy | [Soteri Trust Center](https://soteri.safebase.us/) |
| Security for Jira --- Marketplace Privacy \& Security | [Atlassian Marketplace](https://marketplace.atlassian.com/apps/1229376/security-for-jira-pii-secret-scanner-by-soteri?hosting=cloud&tab=privacy-and-security) |
| Security for Confluence --- Marketplace Privacy \& Security | [Atlassian Marketplace](https://marketplace.atlassian.com/apps/1224167/security-for-confluence-pii-secret-scanner-by-soteri?hosting=cloud&tab=privacy-and-security) |
---
version: "Working version"
language: "en"
---
# Financial Services Addendum
*Effective Date* : 2026-04-22
## 1. Purpose and Scope
This Financial Services Addendum (the "**Addendum** ") supplements the agreement between Soteri LLC ("**Soteri** ") and a customer that is a regulated financial entity (the "**Customer** ") for the use of Soteri's cloud-based security scanning and access control products (the "**Services**"). It is intended to support the Customer's compliance with:
* Regulation (EU) 2022/2554 on digital operational resilience for the financial sector ("**DORA**"), in particular Article 30;
* the European Banking Authority Guidelines on Outsourcing Arrangements (EBA/GL/2019/02) (the "**EBA Guidelines**"); and
* analogous requirements imposed on financial entities by their competent authorities.
This Addendum is incorporated by reference into the Customer's agreement with Soteri and applies only to the extent the Customer is subject to DORA, the EBA Guidelines, or equivalent financial-services regulation. In the event of conflict between this Addendum and any other agreement between the parties, this Addendum controls for matters within its scope.
## 2. Relationship to Other Soteri Documents
This Addendum does not restate obligations already addressed in other Soteri documents. The following documents are incorporated by reference and, taken together with this Addendum, constitute Soteri's contractual framework for regulated financial customers:
| Topic | Source Document | Location |
|------------------------------------|------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------|
| End User License Agreement | Soteri EULA | [Soteri EULA](https://docs.soteri.io/support/latest/software-end-user-license-agreement.md) |
| Personal data processing (GDPR) | Soteri Data Processing Addendum | [Data Processing Addendum](https://docs.soteri.io/support/latest/data-processing-addendum.md) |
| International data transfers | EU-U.S. Data Privacy Framework (incl. UK Extension and Swiss-U.S. framework) | |
| Security controls and attestations | SOC 2 Type II report; security documentation | [https://soteri.safebase.us](https://soteri.safebase.us/) |
| Sub-processor list | Sub-processor register | [Soteri's Cloud App Data Subprocessors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md) |
| Service levels | Soteri Service Level Agreement | [Service Level Agreement](https://docs.soteri.io/support/latest/service-level-agreement.md) |
## 3. Description of Services and Service Locations
**3.1 Services.** Soteri provides cloud-based security scanning and access control products delivered as applications that operate within the Customer's instance of a third-party collaboration platform (e.g., Atlassian Cloud). The Services scan content and configuration within the Customer's instance to detect security issues and enforce access policies. A current description of each product, including functional scope, is maintained at [soteri.io](https://soteri.io/).
**3.2 Service Locations.** The Services are operated from data centers located in the United States. A current list of sub-processors, including the jurisdictions in which they process Customer data, is maintained at [Soteri's Cloud App Data Subprocessors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md).
**3.3 Data Processed.** The categories of data processed by the Services, and the purposes of processing, are described in the Soteri Data Processing Addendum.
## 4. Sub-outsourcing
Soteri's engagement of sub-processors in the provision of the Services --- including the current sub-processor register, advance notice of changes, the Customer's right to object, and the data protection and security obligations imposed on sub-processors --- is governed by Section 4 of the [Soteri Data Processing Addendum](https://docs.soteri.io/support/latest/data-processing-addendum.md) and the [Soteri's Cloud App Data Subprocessors](https://docs.soteri.io/support/latest/soteri-s-cloud-app-data-subprocessors.md) page incorporated therein.
## 5. Data Availability, Integrity, Confidentiality, and Return
**5.1 Security.** Soteri maintains a written information security program consistent with its SOC 2 Type II attestation. A description of technical and organizational measures is available through the Trust Center.
**5.2 Availability and Integrity.** Soteri operates the Services with redundancy and monitoring appropriate to the nature of the Services.
**5.3 Return and Deletion.** Upon termination or expiration of the Services, Soteri will, at the Customer's election, return or delete Customer data in accordance with the Soteri Data Processing Addendum. This obligation applies equally in the event of Soteri's insolvency, resolution, or discontinuation of the Services.
**5.4 Continuity of Access.** Soteri will not assert any right of retention over Customer data. The Customer's ability to access, export, and retrieve Customer data in accordance with Section 5.3 and the Soteri Data Processing Addendum will not be impaired by a fee dispute, by Soteri's insolvency or resolution, or by Soteri's discontinuation of the Services.
## 6. Incident Reporting
**6.1 Notification.** Soteri will notify the Customer without undue delay after becoming aware of a personal data breach or security incident affecting the Customer's data, in accordance with the Soteri Data Processing Addendum.
**6.2 DORA-Aligned Information.** To support the Customer's incident reporting obligations under DORA, Soteri's notifications will include, to the extent known at the time of reporting and updated as further information becomes available: a description of the incident, the systems and data categories affected, the actual or estimated impact, measures taken or proposed, and a point of contact.
**6.3 Cooperation.** Soteri will cooperate reasonably with the Customer in the Customer's investigation and reporting of incidents to competent authorities.
## 7. Cooperation with Competent Authorities
Soteri will cooperate with the Customer's competent authorities (including, as applicable, the European Central Bank, the European Banking Authority, the European Supervisory Authorities, national competent authorities, and resolution authorities) to the extent required by applicable law. This includes providing information reasonably necessary to enable supervision of the Customer's use of the Services, subject to applicable confidentiality obligations.
## 8. Audit and Inspection Rights
**8.1 Primary Evidence.** Soteri provides its SOC 2 Type II report, security documentation, and other assurance materials through its Trust Center. The parties agree that these materials are intended to satisfy the Customer's routine audit and assessment needs.
**8.2 Customer Audits.** Where the Customer, acting reasonably and on the basis of a documented regulatory requirement, determines that the materials described in Section 8.1 are insufficient, Soteri will respond in good faith to reasonable additional information requests and will cooperate with an audit conducted by the Customer or a qualified third-party auditor (other than a competitor of Soteri) subject to reasonable notice, scope, frequency, and confidentiality limitations.
**8.3 Regulatory Audits.** Soteri will grant the Customer's competent authorities and resolution authorities (and any persons appointed by them) the access, information, and inspection rights required by DORA, the EBA Guidelines, or other applicable law, including, where legally required, the right to conduct on-site inspections of Soteri's premises.
**8.4 Costs.** Each party bears its own costs in connection with audits conducted under this Section, except that excessive or repetitive audits requested by the Customer may be subject to reasonable cost recovery by Soteri.
## 9. Exit
Data return and deletion obligations on termination or expiration of the Services are addressed in Section 5.3. Continuity of Customer access to Customer data is addressed in Section 5.4.
## 10. Termination
**10.1 Customer Termination Rights.** In addition to any termination rights in the Customer's agreement with Soteri, the Customer may terminate the Services on written notice if:
(a) Soteri commits a material breach of this Addendum or the Soteri Data Processing Addendum that is not cured within thirty (30) days of written notice;
(b) a competent authority of the Customer issues a binding order or direction requiring termination;
(c) Soteri becomes subject to insolvency proceedings; or
(d) the Customer reasonably determines, on the basis of a documented regulatory requirement, that continued use of the Services would place the Customer in breach of applicable law.
**10.2 Effect of Termination.** The obligations in Sections 5.3 (Return and Deletion) and 5.4 (Continuity of Access) survive termination.
**10.3 No Modification of Commercial Terms.** Termination under this Section grants the Customer the right to discontinue use of the Services. Refunds, credits, and other commercial settlements on termination are governed by the Customer's agreement with Soteri and applicable billing arrangements (including with Atlassian Marketplace or another authorized reseller), and are not modified by this Addendum.
## 11. Service Levels
Service levels applicable to the Services are set forth in the [Service Level Agreement](https://docs.soteri.io/support/latest/service-level-agreement.md).
## 12. Security Awareness and Training
**12.1 Soteri Personnel Training.** Soteri maintains an internal ICT security awareness and digital operational resilience training program for its personnel, as described in its SOC 2 Type II report. This program is intended to meet the training expectations applicable to Soteri's role in providing the Services.
**12.2 Participation in Customer Programs.** Where the Customer determines, in accordance with Article 13(6) of DORA, that participation by Soteri personnel in the Customer's ICT security awareness or digital operational resilience training programs is appropriate, Soteri will cooperate in good faith. Trainings will be charged with a fee of $150 per hour. Participation will be conducted remotely and asynchronously where reasonably practicable.
## 13. Governing Law
This Addendum is governed by the law specified in the Customer's agreement with Soteri, without prejudice to mandatory provisions of Union or member state law applicable to the Customer as a financial entity.
## 14. Changes to this Addendum
Soteri may update this Addendum from time to time to reflect changes in applicable law, Soteri's operations, or industry practice. Material changes will be communicated through the Trust Center at least thirty (30) days in advance of their effective date. Continued use of the Services following the effective date of an update constitutes acceptance of the updated Addendum.
---
version: "Working version"
language: "en"
---
# Licensing and Pricing for Soteri's Atlassian Apps
All of [Soteri's apps for Atlassian host products are available through the Atlassian Marketplace](https://marketplace.atlassian.com/vendors/1219549/soteri).
* **Data Center** apps are sold as an annual subscription.
* **Cloud** apps are sold as a monthly or annual subscription, matching the host site's billing cycle.
## Pricing By User Tier
Soteri's app pricing is subscription-based and varies based on the number of users on your host platform. **The user tier of your app license needs to match the user tier of the host site.** E.g., if your Confluence license is for 20,000 users, you will also need a 20,000 user license for Soteri Security for Confluence.
Atlassian offers a pricing calculator which can help you figure out what a particular Soteri app will cost, based on the number of users you have:
* Data Center
* [Security for Bitbucket Data Center](https://marketplace.atlassian.com/apps/1221399/security-for-bitbucket-enhanced-secret-scanner-by-soteri?hosting=datacenter&tab=pricing)
* [Security for Confluence Data Center](https://marketplace.atlassian.com/apps/1224167/security-for-confluence-enhanced-secret-scanner-by-soteri?hosting=datacenter&tab=pricing)
* [Security for Jira Data Center](https://marketplace.atlassian.com/apps/1229376/security-for-jira-enhanced-secret-scanner-by-soteri?hosting=datacenter&tab=pricing)
* Cloud
* [Security for Confluence Cloud](https://marketplace.atlassian.com/apps/1224167/security-for-confluence-enhanced-secret-scanner-by-soteri?hosting=cloud&tab=pricing)
* [Security for Jira Cloud](https://marketplace.atlassian.com/apps/1229376/security-for-jira-enhanced-secret-scanner-by-soteri?hosting=cloud&tab=pricing)
## Help with Licensing and Pricing
**Billing and licensing for Soteri's Atlassian apps are handled via the Atlassian Marketplace.** Most issues with billing or licensing will have to be handled by [Atlassian's billing and licensing team](https://www.atlassian.com/company/contact/purchasing-licensing#/), including:
* Generating new evaluation licenses
* Renewing evaluation licenses
* Generating quotes or purchase orders
* Issues with payments, bills, or refunds
If you have issues with any of the above, please contact [Atlassian's billing and licensing team](https://www.atlassian.com/company/contact/purchasing-licensing#/).
For other questions, you can reach out to Soteri's support team via our [support portal](https://support.soteri.io/).
## Do you offer discount/promotional codes?
We are unable to offer discount or promotional codes on our apps at this time.
---
version: "Working version"
language: "en"
---
# Privacy Policy
*EFFECTIVE DATE: April 15, 2026*
This Privacy Policy ("Policy") describes how Soteri LLC ("we," "us," or "our") collects, uses, and discloses information that we obtain about your use of the [soteri.io](https://soteri.io/) website (the "Site") and Soteri products and hosted services, collectively the "Service."
We store your information in the United States. By using or downloading the Service you agree that your personal information may be transferred to and stored in the United States and handled as described in this Policy.
## Data Privacy Framework Participation
Soteri LLC has certified to the U.S. Department of Commerce that it adheres to with the EU-U.S. Data Privacy Framework (EU-U.S. DPF), the UK Extension to the EU-U.S. DPF, and the Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF) as set forth by the U.S. Department of Commerce. Soteri LLC has certified to the U.S. Department of Commerce that it adheres to the EU-U.S. Data Privacy Framework Principles (EU-U.S. DPF Principles) with regard to the processing of personal data received from the European Union and the United Kingdom in reliance on the EU-U.S. DPF and the UK Extension to the EU-U.S. DPF. Soteri LLC has certified to the U.S. Department of Commerce that it adheres to the Swiss-U.S. Data Privacy Framework Principles (Swiss-U.S. DPF Principles) with regard to the processing of personal data received from Switzerland in reliance on the Swiss-U.S. DPF. If there is any conflict between the terms in this privacy policy and the EU-U.S. DPF Principles and/or the Swiss-U.S. DPF Principles, the Principles shall govern. To learn more about the Data Privacy Framework (DPF) program and to verify Soteri LLC's participation, please visit .
## Scope of DPF Coverage
The EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF apply to the following categories of personal data that Soteri receives from the EU, UK, and Switzerland: name, email address, account information, usage data, and communications data as further described in "The Information We Collect About You" section below, as well as personal data contained within customer content processed by Soteri's scanning services on behalf of customer organizations as described in "Customer Content and Our Role as Data Processor" below.
## The Information We Collect About You
We collect information directly from you, from devices and third party services you connect, as well as automatically through your use of our Service. If you purchase a Service that will be hosted on your server, Soteri does not collect any information from the device it is installed upon.
***When You Create, Update, or add information to Your Profile.*** When you register to use the Service, we collect the personal information you provide us, including your name and email address. We may also collect information that you provide to Atlassian and which Atlassian sends to us on your behalf.
AND
***We collect additional information from Devices you connect to the Service:***
* ***When You Contact Us.*** When you contact Soteri directly, such as when you contact our Customer Support team, we will receive the contents of your message or any attachments you may send to us, as well as any additional information you choose to provide.
* ***Third Party Analytics.*** We use automated devices and applications, such as Google Analytics, to evaluate usage of our Service. We also may use other analytic means to evaluate our Service. Soteri does not use any analytic software for Services that are hosted by you on your server.
## Customer Content and Our Role as Data Processor
Soteri's products (including Security for Confluence and Security for Jira) scan customer content --- including Confluence pages, Jira issues, and associated metadata --- to detect secrets, credentials, and other sensitive data. For cloud-hosted versions of our products, this scanning is performed on Soteri's servers in the United States.
When performing these scanning services, Soteri acts as a **data processor** on behalf of its customers, who are the data controllers. Customer content processed during scanning may contain personal data, such as names, email addresses, or other identifying information present in pages, issues, or comments authored by end users. Soteri processes this content solely for the purpose of providing the scanning service and does not use it for any secondary purpose, including marketing, analytics, or model training.
Soteri retains scan metadata --- such as issue or page identifiers and character offsets indicating the location of detected findings --- necessary to provide the service. Soteri does not retain the underlying text content of scanned pages or issues beyond what is transiently required for service operation. Operational logs, which may include user identifiers and system activity records, are retained for a limited period and are used solely for security, debugging, and service reliability purposes.
Soteri's security controls applicable to customer content, including our SOC 2 Type II certification, are described in our Trust Center at .
Customers who are subject to GDPR or other data protection laws and who use Soteri's cloud-hosted services to process personal data may view our Data Processing Addendum (DPA) at . For questions about the DPA, please contact [privacy@soteri.io](mailto:privacy@soteri.io).
## How We Use Your Information
We process your information, including your personal information, for the following purposes:
* To provide our Service to you, to communicate with you about your use of our Service, to respond to your inquiries, and for other customer service purposes.
* For marketing and promotional purposes, to the extent permitted by law and, where required, with your consent. For example, we may use your information, such as your email address, to send you news and newsletters, special offers, and promotions, or to otherwise contact you about products or information we think may interest you. We also may use the information that we learn about you to assist us in advertising our services on third party websites. You can opt-out of receiving marketing at any time as described below.
* To better understand how users access and use our Service, both on an aggregated and individualized basis, in order to improve our Service and respond to user desires and preferences, and for other analytical purposes.
* To administer surveys and questionnaires.
* To comply with legal obligations, as part of our general business operations, and for other business administration purposes.
* Where we believe necessary to investigate, prevent or take action regarding illegal activities, suspected fraud, situations involving potential threats to the safety of any person or violations of our End User License Agreement or this Privacy Policy.
## How We Share Your Information
We may share your information, including personal information, as follows:
* ***With Your Consent.*** With your prior consent, we may share information from the Service with other third-party partners, including your personal information and data collected from your devices.
* ***Aggregate and De-Identified Information.*** We may share aggregate or de-identified information---so that it cannot reasonably be used to identify an individual---with third parties for marketing, advertising, research or similar purposes.
* We may disclose the information we collect from you to our affiliates or subsidiaries; however, if we do so, their use and disclosure of your personal information will be subject to this Policy.
* ***Service Providers.*** We may disclose the information we collect from you to third party vendors, service providers, contractors or agents who perform functions on our behalf, such as *providers of hosting, email communication, customer support services, analytics, marketing, and advertising,* based on our instructions, and in compliance with this policy and any other appropriate confidentiality and security measures.
* ***Business Transfers.*** If we are acquired by or merged with another company, if substantially all of our assets are transferred to another company, or as part of a bankruptcy proceeding or reorganization, we will give affected users notice before transferring any personal information to a new entity.
* ***In Response to Legal Process.*** We also may disclose the information we collect from you in order to comply with the law, a judicial proceeding, court order, or other legal process, such as in response to a court order or a subpoena.
*Please note*: Our policy is to notify you of legal process seeking access to your information, such as search warrants, court orders, or subpoenas, unless we are prohibited by law from doing so. In cases where a court order specifies a non-disclosure period, we provide delayed notice after the expiration of the non-disclosure period. Exceptions to our notice policy include exigent or counterproductive circumstances, for example, when there is an emergency involving a danger of death or serious physical injury to a person.
* ***To Protect Us and Others.*** We also may disclose the information we collect from you where we believe it is necessary to investigate, prevent, or take action regarding illegal activities, suspected fraud, situations involving potential threats to the safety of any person, violations of our Terms of Use or this Policy, or as evidence in litigation in which Soteri is involved.
***Accountability for Onward Transfers.*** With respect to personal data received or transferred pursuant to the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF, Soteri LLC requires third-party agents that process personal data on our behalf to do so in a manner consistent with the DPF Principles. If Soteri LLC has knowledge that an agent is processing personal data in a manner contrary to the DPF Principles, Soteri LLC will take reasonable steps to stop and remediate such processing. Soteri LLC is potentially liable in cases of onward transfer of personal data received pursuant to the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF to third parties.
## Cookies
Cookies are small text files stored on your device and used by web browsers to deliver personalized content and remember logins and account settings. In addition to improving user experience, we use cookies and similar technologies for analytic and advertising purposes. You can manage your cookies locally by adjusting your browser settings, or you can opt-out of targeted advertising through cookies by visiting or . We honor opt-out preference signals such as the Global Privacy Control (GPC), where required by applicable law. For more information about GPC, visit .
## Third-Party Links
Our Service may contain links to third-party websites. Any access to and use of such linked websites is not governed by this Policy, but instead is governed by the privacy policies of those third party websites. We are not responsible for the information practices of such third party websites. Specifically, use of the Service will require a subscription to services provided by Atlassian, and the access and use of Atlassian services is not governed by this policy.
## Security of My Personal Information
We have implemented reasonable precautions to protect the information we collect from loss, misuse, and unauthorized access, disclosure, alteration, and destruction. Please be aware that despite our best efforts, no data security measures can guarantee security.
You should take steps to protect against unauthorized access to your password, phone, and computer by, among other things, signing off after using a shared computer, choosing a robust password that nobody else knows or can easily guess, and keeping your log-in and password private. We are not responsible for any lost, stolen, or compromised passwords or for any activity on your account via unauthorized password activity.
## Access to and Deleting My Personal Information
In accordance with the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF Principles, we acknowledge the right of EU, UK, and Swiss individuals to access their personal data. You may modify personal information that you have submitted by logging into your account and updating your profile information. Please note that copies of information that you have updated, modified or deleted may remain viewable in cached and archived pages of the Service for a period of time.
We store information associated with your account until your account is deleted. You can delete your account at any time by contacting Customer Support at [support@soteri.io](mailto:support@soteri.io). Please note that it may take a bit of time to delete your account information, and we may preserve it for legal reasons or to prevent harm, including as described in the How Information Is Shared section.
## What Choices Do I Have Regarding Promotional Emails?
We may send periodic promotional emails to you. You may opt-out of such communications by following the opt-out instructions contained in the email. Please note that it may take up to 10 business days for us to process opt-out requests. We may still send you emails about your account or any services you have requested or received from us.
## Users Under 18
Our services are not designed for users under 18. If we discover that a user under 18 has provided us with personal information, we will delete such information from our systems.
## GDPR -- Rights For EEA Users and Soteri's Capabilities for Worldwide Users
***What Rights Do I Have?*** Individuals located in the European Economic Area (EEA) have certain rights in respect of your personal information and Soteri will provide these capabilities to all our worldwide users, including:
* the right of access to your personal data;
* the right to correct or rectify any inaccurate personal data;
* the right to restrict or oppose processing of personal data;
* the right to erase your personal data; and
* the right to receive your personal data in a portable format.
We rely on your consent as a lawful basis processing personal data for the following purposes:
* initial collection of personal data through the Service;
* providing you with marketing or promotional communications. You may opt out of such communications at any time by clicking the "unsubscribe" link found within Soteri email updates and changing your contact preferences.
We process personal data in order to perform our contract with you.
Additionally, we process personal data based on our "legitimate interests" in providing you the Service as described in the section "**How We Use Your Information"**, including:
* To enable the Service to function as expected; and
* To communicate with you in response to customer service inquiries, to deliver non-promotional, service-related emails, or to administer surveys and questionnaires.
* In some cases, Soteri may process personal information pursuant to a legal obligation or to protect your vital interests or those of another person.
***How May I Exercise My Individual Rights?*** Soteri users located worldwide may access and update their personal information as follows:
* Account holders may access and update personal information through their account settings in Atlassian;
* Account holders may exercise their rights to data deletion and data portability by contacting Soteri's Data Controller Representative at [privacy@soteri.io](mailto:privacy@soteri.io).
* Soteri does not retain any personal information from users who do not evaluate or purchase Services.
Please note that Soteri may request additional information from you to verify your identity before we disclose any personal or account information.
## EU-U.S. Data Privacy Framework, UK Extension, and Swiss-U.S. Data Privacy Framework --- Complaints and Dispute Resolution
In compliance with the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF Principles, Soteri LLC commits to resolve DPF Principles-related complaints about our collection and use of your personal information. EU, UK, and Swiss individuals with inquiries or complaints regarding our handling of personal data received in reliance on the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF should first contact Soteri LLC at: [privacy@soteri.io](mailto:privacy@soteri.io).
Soteri LLC has further committed to refer unresolved complaints concerning our handling of personal data received in reliance on the EU-U.S. DPF, UK Extension, and Swiss-U.S. DPF to JAMS, an alternative dispute resolution provider located in the United States. If you do not receive timely acknowledgment of your DPF Principles-related complaint from us, or if we have not addressed your DPF Principles-related complaint to your satisfaction, please visit for more information or to file a complaint. The services of JAMS are provided at no cost to you.
## FTC Jurisdiction
Soteri LLC is subject to the investigatory and enforcement powers of the U.S. Federal Trade Commission (FTC).
## Binding Arbitration
Under certain conditions, more fully described on the Data Privacy Framework website at , you may invoke binding arbitration when other dispute resolution procedures have been exhausted.
## Your California Privacy Rights
Under the California Consumer Privacy Act, as amended by the California Privacy Rights Act (collectively, "CCPA"), California residents have certain rights regarding their Personal Information. You may exercise these rights by contacting us through the form at , and Soteri will respond upon verification of your identity.
***Your Rights.*** California residents have the right to:
* Know what Personal Information Soteri collects about you, the sources from which it is collected, the business purposes for collecting it, the categories of third parties with whom it is shared, and the specific pieces of Personal Information Soteri holds about you;
* Delete your Personal Information, subject to certain exceptions;
* Correct inaccurate Personal Information that Soteri maintains about you;
* Opt out of the sale or sharing of your Personal Information; and
* Limit the use and disclosure of Sensitive Personal Information to purposes necessary to provide the Service.
For additional detail on the categories of information we collect, how we use it, and how we share it, please see the sections of this Privacy Policy titled **The Information We Collect About You** , **How We Use Your Information** , and **How We Share Your Information**.
**Sale and Sharing of Personal Information.** Soteri does not sell your Personal Information, and Soteri does not share your Personal Information for cross-context behavioral advertising purposes. If you are 16 years of age or older, you have the right to direct us not to sell or share your Personal Information at any time. We do not sell or share the Personal Information of consumers we actually know are less than 16 years of age, unless we receive affirmative authorization from either the consumer who is at least 13 but not yet 16 years of age, or the parent or guardian of a consumer less than 13 years of age.
**Sensitive Personal Information.** To the extent Soteri processes Sensitive Personal Information as defined under the CCPA, Soteri uses it only for purposes necessary to provide the Service and as otherwise permitted by law.
**Non-Discrimination.** Soteri will not discriminate against you for exercising any of your rights under the CCPA. We will not deny you goods or services, charge you a different price or rate, or provide you a different level or quality of goods or services because you exercised such rights.
**Financial Incentives.** We may offer certain financial incentives, as permitted by the CCPA, in exchange for your providing us certain information. Any such incentive will reasonably relate to the value of your Personal Information and will include written terms describing the program's material aspects. Participation requires your prior opt-in consent, which you may revoke at any time.
**Authorized Agents.** You may designate an authorized agent to submit a request on your behalf. We may require the agent to provide proof of your written authorization, and we may require you to verify your identity directly with us.
## Contact Us
If you have questions about our privacy practices, please contact us at [privacy@soteri.io](mailto:privacy@soteri.io).
Soteri LLC
6201 W 87th St
Ste D #322
Los Angeles, California 90045
If you are an EEA, UK, or Swiss customer and are unable to reach Soteri at the contact information provided above regarding your issue, you have the right to contact your local Data Protection Authority.
## Changes to this Policy
This Policy is current as of the Effective Date set forth above. We may change this Policy from time to time, so please be sure to check back periodically. We will post any changes to this Policy on our Service. If we make any changes to this Policy that materially affect our practices with regard to the personal information we have previously collected from you, we will endeavor to provide you with notice in advance of such change.
---
version: "Working version"
language: "en"
---
# Service Level Agreement
To contact our support team, please open a [ticket in our support portal](https://support.soteri.io/).
| Classification | Criteria | Time to first response for issues ||
|----------------|-----------------------------------------------------------------------------------------------------------------------------------|---|---|
| Level 1 | * Critical loss of add-on functionality * Performance resulting in high number of users unable to perform their normal functions. | **Reported during business hours (10 a.m. - 6 p.m. PST, Monday - Friday)** within 5 hours ||
| Level 2 | * Moderate loss of add-on functionality * Performance resulting in multiple users impacted in their normal functions. | within 1 business day ||
| Level 3 | * Minor loss of add-on functionality * Issues encountered in a non-production environment. | within 3 business days ||
| Level 4 | * Product feature questions * Product modification or enhancement requests | within 5 business days ||
For security related bugs, our apps sold on the Atlassian Marketplace are subject to [Atlassian's Security Bug Fix Policy](https://developer.atlassian.com/platform/marketplace/security-bugfix-policy/), which defines severities and SLAs for fixing those bugs.
---
version: "Working version"
language: "en"
---
# Software End User License Agreement
*Effective* 2026-06-03
This End User License Agreement, including the Order Form which by this reference is incorporated herein (this **"Agreement"** ), is a binding agreement between Soteri LLC (**"Licensor", "Soteri", "we", "our"** ) and the person or entity identified on the Order Form as the licensee of the Products (**"Licensee", "you", "your"**).
LICENSOR PROVIDES THE SOFTWARE SOLELY ON THE TERMS AND CONDITIONS SET FORTH IN THIS AGREEMENT AND ON THE CONDITION THAT LICENSEE ACCEPTS AND COMPLIES WITH THEM. BY CLICKING THE "ACCEPT" BUTTON/CHECKING THE "ACCEPT" BOX ON THE ORDER FORM YOU (A) ACCEPT THIS AGREEMENT AND AGREE THAT LICENSEE IS LEGALLY BOUND BY ITS TERMS; AND (B) REPRESENT AND WARRANT THAT: (I) YOU ARE 18 YEARS OF AGE OR OLDER/OF LEGAL AGE TO ENTER INTO A BINDING AGREEMENT; AND (II) IF LICENSEE IS A CORPORATION, GOVERNMENTAL ORGANIZATION, OR OTHER LEGAL ENTITY, YOU HAVE THE RIGHT, POWER, AND AUTHORITY TO ENTER INTO THIS AGREEMENT ON BEHALF OF LICENSEE AND BIND LICENSEE TO ITS TERMS. IF LICENSEE DOES NOT AGREE TO THE TERMS OF THIS AGREEMENT, LICENSOR WILL NOT AND DOES NOT LICENSE THE SOFTWARE TO LICENSEE AND YOU MUST NOT DOWNLOAD/INSTALL THE SOFTWARE OR DOCUMENTATION.
NOTWITHSTANDING ANYTHING TO THE CONTRARY IN THIS AGREEMENT OR YOUR OR LICENSEE'S ACCEPTANCE OF THE TERMS AND CONDITIONS OF THIS AGREEMENT, NO LICENSE IS GRANTED (WHETHER EXPRESSLY, BY IMPLICATION, OR OTHERWISE) UNDER THIS AGREEMENT, AND THIS AGREEMENT EXPRESSLY EXCLUDES ANY RIGHT, CONCERNING ANY SOFTWARE THAT LICENSEE DID NOT ACQUIRE LAWFULLY OR THAT IS NOT A LEGITIMATE, AUTHORIZED COPY OF LICENSOR'S SOFTWARE.
## 1. Definitions
For purposes of this Agreement, the following terms have the following meanings:
**"Authorized Users"** means the specific individuals for whom you have paid the required fees and whom you designate through the applicable Product.
**"Documentation"** means user manuals, technical manuals, and any other materials provided by us, in printed, electronic, or other form, that describe the installation, operation, use, or technical specifications of the Products.
**"Hosted Services"** means any Soteri hosted or cloud-based solutions for which you are purchasing a license, as expressly set forth in the Order Form.
**"Intellectual Property Rights"** means any and all registered and unregistered rights granted, applied for, or otherwise now or hereafter in existence under or related to any patent, copyright, trademark, trade secret, database protection, or other intellectual property rights laws, and all similar or equivalent rights or forms of protection, in any part of the world.
**"Order Form"** means the order form filled out and submitted by or on behalf of you, and accepted by us, for your purchase of the license for the Products granted under this Agreement.
**"Person"** means an individual, corporation, partnership, joint venture, limited liability company, governmental authority, unincorporated organization, trust, association, or other entity.
**"Product"** means Software or Hosted Services.
**"Software"** means the software programs for which Licensee is purchasing a license, as expressly set forth in the Order Form.
## 2. License Grant and Scope
Subject to and conditioned upon your payment of the License Fees and your strict compliance with all terms and conditions set forth in this Agreement, we grant to you a non-exclusive, non-transferable, non-sublicensable, limited license during the Term to use, solely by and through your Authorized Users, the Products and Documentation, solely as set forth in this Section 2 and subject to all conditions and limitations set forth in Section 4 or elsewhere in this Agreement. This license grants you the right, exercisable solely by and through your Authorized Users, to:
(a) Download, copy, and install in accordance with the Documentation one (1) copy of the Software on one instance owned or leased, and controlled by, you. All copies of the Software made by the you:
(i) will be the exclusive property of Soteri;
(ii) will be subject to the terms and conditions of this Agreement; and
(iii) must include all trademark, copyright, patent, and other Intellectual Property Rights notices contained in the original.
(b) Use and run the Software as properly installed in accordance with this Agreement and the Documentation, solely as set forth in the Documentation and solely for Licensee's internal business purposes.
Licenses granted by Soteri are subject to the condition that you must ensure the maximum number of Authorized Users that are able to access and use the Products concurrently is equal to the number of User Licenses for which the necessary fees have been paid to Atlassian and/or its authorized partners (each, an "Atlassian Expert"). You may purchase additional User Licenses at any time on payment of the appropriate fees to Atlassian or an Atlassian Expert. "User License" means a license granted under this Agreement to you to permit an Authorized User to use the Product. The number of User Licenses granted to you is dependent on the fees paid by you.
## 3. Evaluation of Marketplace products
Soteri may offer free evaluation and/or other limited versions of Products so you can preview Products before you purchase the full version (**"Evaluation Products"** ). If the Product is only provided for evaluation purposes, your rights are limited to an evaluation license which permits you to use, download, install, and/or operate the Evaluation Product for a limited period of time (**"Evaluation Period"**), and it will only be accessible by a limited number of temporary users, in each case as determined by Soteri. On the expiration of the Evaluation Period, the Evaluation Product will cease to function, and you will remove and delete all copies of such Marketplace Product in your possession or control. Soteri may require you to purchase a full license to the Products before providing any maintenance or support services under this Agreement, including any Updates. If you attempt to use successive Evaluation Periods as an abuse of this section, Soteri has the right to inhibit the functioning of the Evaluation Products.
## 4. Third-Party Materials
The Products may require other software, content, data, or other materials, including related documentation, that are owned by Persons other than Licensor (**"Third-Party Materials"**). Licensee has the obligation to acquire any necessary rights to such Third-Party Materials that are required to operate the Products, including entering into separate agreements with the licensor of such materials. Specifically, the use of Products requires a license to use the Atlassian products that the Products are intended to be used with. This Agreement does not provide Licensee with any rights to Atlassian products, and Licensee must seek a separate license from Atlassian for any Third-Party Materials required to operate the Products.
## 5. Use Restrictions
You shall not, and shall require your Authorized Users to not, directly or indirectly:
(a) Use, in any way, (including creating any copies of) the Products or Documentation beyond the scope of the license granted under Section 2;
(b) modify, translate, adapt, or otherwise create derivative works or improvements, whether or not patentable, of the Products or Documentation or any part thereof;
(c) reverse engineer, attempt to reverse engineer, disassemble, decompile, decode, attempt to decode, or otherwise attempt to derive or gain access to the source code of the Products or any part thereof;
(d) remove, delete, alter, or obscure any trademarks or any copyright, trademark, patent, or other intellectual property or proprietary rights notices provided on or with the Products or Documentation, including any copy thereof;
(e) rent, lease, lend, sell, sublicense, assign, distribute, publish, transfer, or otherwise make available the Products, or any features or functionality of the Products, to anyone who is not an Authorized User for any reason, whether or not over a network or on a hosted basis, including in connection with the internet or any web hosting, wide area network (WAN), virtual private network (VPN), virtualization, time-sharing, service bureau, software as a service, cloud, or other technology or service;
(f) use the Products or Documentation in violation of any law, regulation, or rule; or
(g) use the Products or Documentation for purposes of competitive analysis of the Products, the development of a competing software product or service, or any other purpose that is to the Licensor's commercial disadvantage.
## 6. Responsibility for Use of Products
You are responsible and liable for all uses of the Products and Documentation through access thereto provided by Soteri, directly or indirectly. Specifically, and without limiting the generality of the foregoing, You are responsible and liable for all actions and failures to take required actions with respect to the Products and Documentation by its Authorized Users or by any other Person to whom you or an Authorized User may provide access to or use of the Products and/or Documentation, whether such access or use is permitted by or in violation of this Agreement.
## 7. Software Maintenance and Support
(a) Subject to Section 2, the license granted hereunder entitles Licensee to basic software maintenance and support services as defined herein:
(i) for one (1) year following the date set forth on the Order Form; and
(ii) thereafter, solely if Licensee purchases additional support services.
(b) Maintenance and support services will include provision of such updates, upgrades, bug fixes, patches, and other error corrections (collectively, **"Updates"**) as we make generally available free of charge to all licensees of the Software then entitled to maintenance and support services. We may develop and provide Updates in our sole discretion, and you agree that we have no obligation to develop any Updates at all or for particular issues. You further agree that all Updates will be deemed Software, and related documentation will be deemed Documentation, all subject to all terms and conditions of this Agreement. You acknowledge that Soteri may provide all Updates via download from a website designated by us and that your receipt thereof will require an internet connection, which connection is your sole responsibility. Soteri has no obligation to provide Updates via any other media. Maintenance and support services do not include any new version or new release of the Software that we may issue as a separate or new product, and we may determine whether any issuance qualifies as a new version, new release, or Update in our sole discretion.
(c) Soteri maintains a Service Level Agreement Policy at . This is a non-binding policy setting forth Soteri's support services for the Products, and may be changed, without notice, at Soteri's sole discretion.
(d) We reserve the right to condition the provision of maintenance and support services, including all or any Updates, on your registration of the copy of Software for which support is requested. Licensor has no obligation to provide maintenance and support services, including Updates:
(i) for any but the most current version or release of the Software and any Third-Party Material that the Software interacts with;
(ii) for any copy of Software for which all previously issued Updates have not been installed;
(iii) if you are in breach under this Agreement; or
(iv) for any Software that has been modified other than by or with the authorization of Licensor, or that is being used with any hardware, software, configuration, or operating system not specified in the Documentation or expressly authorized by Licensor in writing.
## 8. Hosted Services Terms
(a) Authorized Users access Hosted Services through a web client with user IDs and passwords. You are responsible for ensuring that such login information is kept strictly confidential and are not shared. You are also responsible for any and all actions taken using Licensee or Authorized User accounts and passwords, and you agree to immediately notify us of any unauthorized use of which it becomes aware.
(b) You may upload data, content, code, video, images, or other materials of any type to or through the Hosted Services (**"Licensee Data"**). You will retain all right, title, and interest in and to Licensee Data, subject to a non-exclusive, worldwide, royalty-free right for us to:
(i) Collect, use, copy, store, transmit, modify, and create derivative works of Licensee Data, in each case solely to the extent necessary to provide the applicable Hosted Service; and
(ii) For Hosted Services that enable interactions with other people, to distribute, publicly perform, and display Licensee Data as Authorized Users direct or enable through the Hosted Service. We may also access your account or instance in order to respond to your support requests.
(c) Soteri implements security procedures to help protect Licensee Data from security attacks. However, using the Hosted Services necessarily involves transmission of data over networks that are not owned, operated, or controlled by us, and we are not responsible for any data lost, altered, intercepted, or stored across such networks. We cannot guarantee that our security procedures will be error-free, that transmissions of data will always be secure, or that unauthorized third parties will never be able to defeat our security measures or those of third party service providers.
(d) Soteri may remove or delete Licensee Data within a reasonable period of time after the termination of Hosted Services as provided on the Order Form.
(e) To the extent Soteri processes Personal Data on Licensee's behalf in connection with the Hosted Services, such processing is governed by Soteri's Data Processing Addendum, available at (the **"DPA"**), which is hereby incorporated into this Agreement by reference. In the event of a conflict between the DPA and this Agreement with respect to the processing of Personal Data, the DPA shall control.
## 9. Collection and Use of Information
We will collect, retain, and use information provided by and about you in accordance with our privacy policy, which is available at . Such privacy policy is hereby incorporated into this agreement and each party agrees to be bound by it.
## 10. Feedback
Products are made available on a limited license or access basis, and no ownership right is conveyed to you, irrespective of the use of terms such as "purchase" or "sale". From time to time, you may choose to submit comments, information, questions, data, ideas, description of processes, or other information to us, including sharing your modifications or in the course of receiving maintenance and support services (**"Feedback"**). Soteri may freely use, copy, disclose, license, distribute and exploit any Feedback in any manner without any obligation, royalty or restriction based on intellectual property rights or otherwise. No Feedback will be considered your confidential information, and nothing in this Agreement limits Soteri's right to independently use, develop, evaluate, or market products, whether incorporating Feedback or otherwise. Soteri has and retains all right, title and interest, including all intellectual property rights, in and to the Products, their "look and feel", any and all related or underlying technology, and any modifications or derivative works of the foregoing created by or for Soteri, including without limitation as they may incorporate Feedback.
## 11. Intellectual Property Rights
Licensee acknowledges and agrees that the Products and Documentation are provided under license, and not sold, to Licensee. Licensee does not acquire any ownership interest in the Products or Documentation under this Agreement, or any other rights thereto, other than to use the same in accordance with the license granted and subject to all terms, conditions, and restrictions under this Agreement. Licensor reserves and shall retain its entire right, title, and interest in and to the Products and all Intellectual Property Rights arising out of or relating to the Products, except as expressly granted to the Licensee in this Agreement. Licensee shall use commercially reasonable efforts to safeguard all Products (including all copies thereof) from infringement, misappropriation, theft, misuse, or unauthorized access. Licensee shall promptly notify Licensor if Licensee becomes aware of any infringement of the Licensor's Intellectual Property Rights in the Products and fully cooperate with Licensor, at Licensor's sole expense, in any legal action taken by Licensor to enforce its Intellectual Property Rights.
## 12. PAYMENT
All License Fees are due payable in advance in the manner set forth in the Order Form and are non-refundable, except as may be expressly set forth herein. Any renewal of the license hereunder shall not be effective until the fees for such renewal have been paid in full. License Fees shall be paid to Atlassian or an Atlassian Expert. Soteri is not responsible for processing the payment of any License Fees, and Soteri will not be responsible for any interruption in service that results from delays by Atlassian or an Atlassian Expert in processing payments.
## 13. Term and Termination
(a) This Agreement and the license granted hereunder shall remain in effect for the term set forth on the Order Form or until earlier terminated as set forth herein (the **"Term"**). This Agreement will automatically renew for subsequent equal terms unless you elect not to renew through the Atlassian website or provide written notice to Soteri.
(b) You may terminate this Agreement by ceasing to use and destroying all copies of the Products and Documentation.
(c) We may terminate this Agreement, effective upon written notice to you, if you breach this Agreement and such breach: (i) is incapable of cure; or (ii) being capable of cure, remains uncured fifteen (15) days after we provide written notice thereof.
(d) We may terminate this Agreement, effective immediately, if you file, or have filed against you, a petition for voluntary or involuntary bankruptcy or pursuant to any other insolvency law, makes or seeks to make a general assignment for the benefit of its creditors or applies for, or consents to, the appointment of a trustee, receiver, or custodian for a substantial part of your property.
(e) Upon expiration or earlier termination of this Agreement, the license granted hereunder shall also terminate, and you shall cease using and destroy all copies of the Products and Documentation. No expiration or termination shall affect your obligation to pay all Licensee Fees that may have become due before such expiration or termination, or entitle you to any refund.
## 14. Limited Warranties, Exclusive Remedy, and Disclaimer/Warranty Disclaimer
THE SOFTWARE AND DOCUMENTATION ARE PROVIDED TO LICENSEE "AS IS" AND WITH ALL FAULTS AND DEFECTS WITHOUT WARRANTY OF ANY KIND. TO THE MAXIMUM EXTENT PERMITTED UNDER APPLICABLE LAW, LICENSOR, ON ITS OWN BEHALF AND ON BEHALF OF ITS AFFILIATES AND ITS AND THEIR RESPECTIVE LICENSORS AND SERVICE PROVIDERS, EXPRESSLY DISCLAIMS ALL WARRANTIES, WHETHER EXPRESS, IMPLIED, STATUTORY, OR OTHERWISE, WITH RESPECT TO THE SOFTWARE AND DOCUMENTATION, INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE, TITLE, AND NON-INFRINGEMENT, AND WARRANTIES THAT MAY ARISE OUT OF COURSE OF DEALING, COURSE OF PERFORMANCE, USAGE, OR TRADE PRACTICE. WITHOUT LIMITATION TO THE FOREGOING, THE LICENSOR PROVIDES NO WARRANTY OR UNDERTAKING, AND MAKES NO REPRESENTATION OF ANY KIND THAT THE LICENSED SOFTWARE WILL MEET THE LICENSEE'S REQUIREMENTS, ACHIEVE ANY INTENDED RESULTS, BE COMPATIBLE, OR WORK WITH ANY OTHER SOFTWARE, APPLICATIONS, SYSTEMS, OR SERVICES, OPERATE WITHOUT INTERRUPTION, MEET ANY PERFORMANCE OR RELIABILITY STANDARDS OR BE ERROR FREE, OR THAT ANY ERRORS OR DEFECTS CAN OR WILL BE CORRECTED.
## 15. Limitation of Liability
TO THE FULLEST EXTENT PERMITTED UNDER APPLICABLE LAW:
(a) IN NO EVENT WILL LICENSOR OR ITS AFFILIATES, OR ANY OF ITS OR THEIR RESPECTIVE LICENSORS OR SERVICE PROVIDERS, BE LIABLE TO LICENSEE OR ANY THIRD PARTY FOR ANY USE, INTERRUPTION, DELAY, OR INABILITY TO USE THE SOFTWARE; LOST REVENUES OR PROFITS; DELAYS, INTERRUPTION, OR LOSS OF SERVICES, BUSINESS, OR GOODWILL; LOSS OR CORRUPTION OF DATA; LOSS RESULTING FROM SYSTEM OR SYSTEM SERVICE FAILURE, MALFUNCTION, OR SHUTDOWN; FAILURE TO ACCURATELY TRANSFER, READ, OR TRANSMIT INFORMATION; FAILURE TO UPDATE OR PROVIDE CORRECT INFORMATION; SYSTEM INCOMPATIBILITY OR PROVISION OF INCORRECT COMPATIBILITY INFORMATION; OR BREACHES IN SYSTEM SECURITY; OR FOR ANY CONSEQUENTIAL, INCIDENTAL, INDIRECT, EXEMPLARY, SPECIAL, OR PUNITIVE DAMAGES, WHETHER ARISING OUT OF OR IN CONNECTION WITH THIS AGREEMENT, BREACH OF CONTRACT, TORT (INCLUDING NEGLIGENCE), OR OTHERWISE, REGARDLESS OF WHETHER SUCH DAMAGES WERE FORESEEABLE AND WHETHER OR NOT THE LICENSOR WAS ADVISED OF THE POSSIBILITY OF SUCH DAMAGES.
(b) IN NO EVENT WILL LICENSOR'S AND ITS AFFILIATES', INCLUDING ANY OF ITS OR THEIR RESPECTIVE LICENSORS' AND SERVICE PROVIDERS', COLLECTIVE AGGREGATE LIABILITY UNDER OR IN CONNECTION WITH THIS AGREEMENT OR ITS SUBJECT MATTER, UNDER ANY LEGAL OR EQUITABLE THEORY, INCLUDING BREACH OF CONTRACT, TORT (INCLUDING NEGLIGENCE), STRICT LIABILITY, AND OTHERWISE, EXCEED THE TOTAL AMOUNT PAID TO THE LICENSOR PURSUANT TO THIS AGREEMENT FOR (i) THE SOFTWARE OR (ii) UP TO TWELVE (12) MONTHS OF THE SPECIFIC SERVICES, THAT IS OR ARE THE SUBJECT OF THE CLAIM.
(c) THE LIMITATIONS SET FORTH IN SECTION 15(a) AND SECTION 15(b) SHALL APPLY EVEN IF THE LICENSEE'S REMEDIES UNDER THIS AGREEMENT FAIL OF THEIR ESSENTIAL PURPOSE.
## 16. Export Regulation
The Products and Documentation may be subject to US export control laws, including the US Export Administration Act and its associated regulations. You shall not, directly or indirectly, export, re-export, or release the Products or Documentation to, or make the Products or Documentation accessible from, any jurisdiction or country to which export, re-export, or release is prohibited by law, rule, or regulation. You shall comply with all applicable federal laws, regulations, and rules, and complete all required undertakings (including obtaining any necessary export license or other governmental approval), prior to exporting, re-exporting, releasing, or otherwise making the Products or Documentation available outside the US.
## 17. US Government Rights
The Products is commercial computer software, as such term is defined in 48 C.F.R. §2.101. Accordingly, if the Licensee is the US Government or any contractor therefor, Licensee shall receive only those rights with respect to the Products and Documentation as are granted to all other end users under license, in accordance with (a) 48 C.F.R. §227.7201 through 48 C.F.R. §227.7204, with respect to the Department of Defense and their contractors, or (b) 48 C.F.R. §12.212, with respect to all other US Government licensees and their contractors.
## 18. Publicity Rights
Soteri may identify Licensee as a customer in promotional materials. You may request that we stop doing so by submitting an email to [++hello@soteri.io++](mailto:hello@soteri.io) at any time. Please note that it may take us up to thirty (30) days to process your request.
## 19. Miscellaneous
(a) All matters arising out of or relating to this Agreement shall be governed by and construed in accordance with the internal laws of the State of California without giving effect to any choice or conflict of law provision or rule. Any legal suit, action, or proceeding arising out of or relating to this Agreement or the transactions contemplated hereby shall be instituted in the federal courts of the United States of America or the courts of the State of California in each case located in the City of Los Angeles and County of Los Angeles, and each party irrevocably submits to the exclusive jurisdiction of such courts in any such legal suit, action, or proceeding. Service of process, summons, notice, or other document by mail to such party's address set forth herein shall be effective service of process for any suit, action, or other proceeding brought in any such court.
(b) We will not be responsible or liable to you, or deemed in default or breach hereunder by reason of any failure or delay in the performance of its obligations hereunder where such failure or delay is due to strikes, labor disputes, civil disturbances, riot, rebellion, invasion, epidemic, hostilities, war, terrorist attack, embargo, natural disaster, acts of God, flood, fire, sabotage, fluctuations or non-availability of electrical power, heat, light, air conditioning, or Licensee equipment, loss and destruction of property, or any other circumstances or causes beyond Licensor's reasonable control.
(c) All notices, requests, consents, claims, demands, waivers, and other communications hereunder shall be in writing and shall be deemed to have been given: (i) when delivered by hand (with written confirmation of receipt); (ii) when received by the addressee if sent by a nationally recognized overnight courier (receipt requested); (iii) on the date sent by facsimile \[or email\] (with confirmation of transmission) if sent during normal business hours of the recipient, and on the next business day if sent after normal business hours of the recipient; or (iv) on the third day after the date mailed, by certified or registered mail, return receipt requested, postage prepaid. Such communications must be sent to the respective parties at the addresses set forth on the Order Form (or to such other address as may be designated by a party from time to time in accordance with this Section 19(c)).
(d) This Agreement, together with the Order Form, and all other documents that are incorporated by reference herein, constitutes the sole and entire agreement between Licensee and Licensor with respect to the subject matter contained herein, and supersedes all prior and contemporaneous understandings, agreements, representations, and warranties, both written and oral, with respect to such subject matter.
(e) You shall not assign or otherwise transfer any of its rights, or delegate or otherwise transfer any of its obligations or performance, under this Agreement, in each case whether voluntarily, involuntarily, by operation of law, or otherwise, without Soteri's prior written consent, which consent Licensor may give or withhold in its sole discretion. No delegation or other transfer will relieve you of any of your obligations or performance under this Agreement. Any purported assignment, delegation, or transfer in violation of this Section 19(e) is void. Licensor may freely assign or otherwise transfer all or any of its rights, or delegate or otherwise transfer all or any of its obligations or performance, under this Agreement without Licensee's consent. This Agreement is binding upon and inures to the benefit of the parties hereto and their respective permitted successors and assigns.
(f) This Agreement is for the sole benefit of the parties hereto and their respective successors and permitted assigns and nothing herein, express or implied, is intended to or shall confer on any other Person any legal or equitable right, benefit, or remedy of any nature whatsoever under or by reason of this Agreement.
(g) This Agreement may only be amended, modified, or supplemented by an agreement in writing signed by each party hereto. No waiver by any party of any of the provisions hereof shall be effective unless explicitly set forth in writing and signed by the party so waiving. Except as otherwise set forth in this Agreement, no failure to exercise, or delay in exercising, any right, remedy, power, or privilege arising from this Agreement shall operate or be construed as a waiver thereof; nor shall any single or partial exercise of any right, remedy, power, or privilege hereunder preclude any other or further exercise thereof or the exercise of any other right, remedy, power, or privilege.
(h) If any term or provision of this Agreement is invalid, illegal, or unenforceable in any jurisdiction, such invalidity, illegality, or unenforceability shall not affect any other term or provision of this Agreement or invalidate or render unenforceable such term or provision in any other jurisdiction.
*** ** * ** ***
## Previous Versions of this Agreement
This Agreement may be updated from time to time. The version currently in effect is the version presented above. The table below lists prior versions for reference, together with their effective dates and a summary of the changes made in each. Except where Soteri and Licensee have agreed otherwise in writing, the version of this Agreement that governs Licensee is the version in effect at the time of Licensee's acceptance or most recent renewal, and the prior versions are provided for historical and reference purposes only. Nothing in this Section 20 amends, or operates as a waiver of, Section 19(g).
| **Version** | **Effective Date** | **Notes** | **Document** |
|-------------|--------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| V2 | 2026-06-03 | Minor non-material fixes, including: * Inclusion of a reference to our Data Processing Addendum * Fixing links to the current versions of things like our Privacy Policy and Service Level Agreement. * Fixes for some incorrect clause references internal to the EULA. | This document as presently constituted. |
| V1 | 2021-01-17 | Initial Soteri EULA | [SOTERIA EULA 01_17_22.pdf](https://docs.soteri.io/__attachments/a_2fd75374c3bca873f78450920d7e907e4188b6f060b2f551097c5a7f1ae6ba8b/SOTERIA%2520EULA%252001_17_22.pdf.md?cb=4080e6392ed55fb535febe4e28337403) |
---
version: "Working version"
language: "en"
---
# Soteri's Cloud App Data Subprocessors
*Effective Date* : 2026-04-21
This page lists the Sub-processors that Soteri LLC ("Soteri") engages in providing its cloud-based security scanning products (the "Cloud Services"), including:
* **Security for Confluence PII \& Secret Scanner** (Confluence Cloud edition)
* **Security for Jira PII \& Secret Scanner** (Jira Cloud edition)
This list is incorporated by reference into the [Soteri Data Processing Addendum](https://docs.soteri.io/support/latest/data-processing-addendum.md) ("DPA"). See Section 4 of the DPA for the terms governing Sub-processor changes, customer objections, and Soteri's obligations with respect to Sub-processors. Capitalized terms not defined here have the meaning given to them in the DPA.
*** ** * ** ***
## Current Sub-processors
| Sub-processor | Purpose | Location |
|-----------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------|
| Google Cloud Platform (GCP) | Cloud hosting and infrastructure for the Services | United States |
| Atlassian Pty Ltd | Forge runtime --- transient processing of requests routed through the Forge platform; no persistent storage of Customer data on Atlassian infrastructure | Region of Customer's Atlassian Cloud instance |
---
version: "Working version"
language: "en"
---
# Soteri's Security Practices
Soteri takes security very seriously. For up to date information about Soteri's security practices, please [visit our Trust Center](https://soteri.safebase.us/).
If you've found a security vulnerability in a Soteri product, please contact us via email: [security@soteri.io](mailto:security@soteri.io).
---
version: "latest"
language: "en"
---
# Security Scanner for IntelliJ
## Security Scanner for IntelliJ
Detect API keys, passwords, and more before you commit them. Protect your developers against accidental credential leaks.
*
### [Overview](https://docs.soteri.io/security-scanner-for-intellij/latest/overview.md)
*
#### [Built-In Scanning Rules](https://docs.soteri.io/security-scanner-for-intellij/latest/built-in-scanning-rules.md)
---
version: "latest"
language: "en"
---
# Built-In Scanning Rules
Here is the list of vulnerabilities that are currently detected by [Soteri](https://marketplace.atlassian.com/vendors/1219549/soteri)'s built-in scanning rules.
## IT Services
| **Rule Name** | **Description** |
|------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| `AWS_CLIENT_ID` | [**AWS Identity and Access Management Client IDs**](https://docs.aws.amazon.com/IAM/latest/UserGuide/reference_identifiers.html#identifiers-unique-ids)uniquely reference users, access keys. These unique IDs can provide access to your AWS instance by allowing users to get keys. |
| `AWS_MWS_KEY` | [**AWS Marketplace Web Service API Keys**](https://docs.developer.amazonservices.com/en_US/dev_guide/DG_Registering.html)allow programmatic interfaces to Amazon Seller stores. |
| `AWS_SECRET_ACCESS_KEY` | [**AWS Secret Access Keys**](https://aws.amazon.com/blogs/security/wheres-my-secret-access-key/)allow for authenticated AWS CLI, SDK, and API access. |
| `AZURE_ACCESS_KEY` | [**Azure Access Keys**](https://docs.microsoft.com/en-us/azure/storage/common/storage-account-keys-manage?tabs=azure-portal)provide access to all data stored in Microsoft Azure. |
| `DYNATRACE_CLIENT_SECRET` | [**Dynatrace Client Secrets**](https://www.dynatrace.com/support/help/dynatrace-api/basics/dynatrace-api-authentication/)allow for access to your Dynatrace instance API. |
| `EC_PRIVATE_KEY` | **Elliptical Curve Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `FACEBOOK_CLIENT_ID` | **Facebook Application IDs** |
| `FACEBOOK_SECRET_KEY` | **Facebook Application Secrets** |
| `GENERIC_API_KEY` | **Generic API Key -**Contains logic to detect generic API Keys. |
| `GENERIC_PASSWORD` | **Generic Passwords** - Contains logic to detect generic passwords. *Note that this rule may generate many false positives, and is disabled by default.* |
| `GENERIC_SECRET` | **Generic Secrets** - Contains logic to detect generic secrets. |
| `GITHUB_KEY` | **Github Authentication Tokens** - This rule detects classic Github Authentication Tokens for [personal use](https://docs.github.com/en/github/authenticating-to-github/keeping-your-account-and-data-secure/creating-a-personal-access-token) (both "[classic](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-personal-access-token-classic)" and "[fine-grained](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-fine-grained-personal-access-token)"), as well as for Github Application OAuth. |
| `GOOGLE_API_KEY` | **Google API Keys** |
| `GOOGLE_OAUTH` | **Google OAuth URLs** |
| `GOOGLE_OAUTH_ACCESS_TOKEN` | **Google OAuth Tokens** |
| `HEROKU_API_KEY` | **Heroku API Keys** |
| `LINKEDIN_CLIENT_ID` | **LinkedIn Client IDs** |
| `LINKEDIN_CLIENT_SECRET` | **LinkedIn Client Secrets** |
| `MAILCHIMP_API_KEY` | **Mailchimp API Key** |
| `MAILGUN_API_KEY` | **Mailgun API Key** |
| `PASSWORD_IN_URL` | **Generic Password in URL**- Contains logic to detect passwords embedded in URLs |
| `PAYPAL_BRAINTREE_ACCESS_TOKEN` | [**Paypal's Braintree Access Token**](https://developer.paypal.com/braintree/docs/guides/authorization/tokenization-key) |
| `PGP_PRIVATE_KEY` | [**PGP**](https://en.wikipedia.org/wiki/Pretty_Good_Privacy)**Private Keys** |
| `PKCS8_PRIVATE_KEY` | **PKSC8 Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `PYPI_UPLOAD_TOKEN` | [**Python Package Index (PyPI) Upload Tokens**](https://pypi.org/help/#apitoken)allow verified publishing of python package to the global repository. |
| `RSA_PRIVATE_KEY` | We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SENDGRID_API_KEY` | [**Sendgrid API Keys**](https://docs.sendgrid.com/api-reference/api-keys/create-api-keys) |
| `SHOPIFY_PARTNER_API_ACCESS_TOKEN` | [**Shopify Partner API access Tokens**](https://shopify.dev/api/partner/getting-started)provide access to the a given store's API. |
| `SHOPIFY_SECRETS` | [**Shopify API Secrets**](https://shopify.dev/api/partner/getting-started) give access to all aspects of the general Shopify API -- this rule contains logic to detect Shared Secrets and Access Tokens for regular, Custom, and Private applications. |
| `SLACK` | [**Slack API Tokens**](https://api.slack.com/authentication/token-types) give access to various API features. |
| `SLACK_WEBHOOK` | [**Slack Webhooks**](https://api.slack.com/messaging/webhooks)are secret URLs which give similar access as API Tokens. |
| `SQUARE_ACCESS_TOKEN` | **Square Access Tokens** |
| `SQUARE_OAUTH_SECRET` | **Square OAuth Secrets** |
| `SSH_PRIVATE_KEY` | **Generic SSH Private Key** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SSH_PUBLIC_KEY` | **Public Key** -half of key-based authentication. Weak public keys can be brute-force cracked by modern computers, and can represent equal vulnerability to the private-key half of the pair. *Since properly-generated public keys are not a threat, this rule is disabled by default.* |
| `TROJAN_SOURCE` | **Trojan Source** detects left-to-right and right-to-left unicode control characters which can be used to obscure malicious code. For more information, see the [Trojan Source paper](https://www.trojansource.codes/trojan-source.pdf) and [CVE-2021-42574 in the NIST Database](https://nvd.nist.gov/vuln/detail/CVE-2021-42574). *Note:* the homoglyph attack described in this paper, and tracked as CVE-2021-42694 in the NIST Database, is **not** detected by this rule, as it can generate a lot of false positives for non-English languages. See "[Mitigating Trojan Source Attacks](https://docs.soteri.io/security-for-bitbucket/latest/mitigating-trojan-source-attacks)" for Soteri's recommendations if you're interested in detecting potential homoglyph attacks. |
| `STRIPE_API_KEY` | **Stripe API Key** |
| `TWILIO_ACCOUNT_ID` | **Twilio Account ID** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWILIO_API_KEY` | **Twilio API Key** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWITTER_CLIENT_ID` | **Twitter Client ID** |
| `TWITTER_SECRET_KEY` | **Twitter Secret Key** |
## Financial
| **Rule Name** | **Description** |
|---------------------------|-------------------------------------------------------------------------------------------------------------|
| `BANK_INFORMATION` | Detects bank account information like routing numbers, etc. which may accompany more sensitive information. |
| `CREDIT_CARD_NUMBERS` | Detects credit card numbers. |
| `SOCIAL_SECURITY_NUMBERS` | Detects United States Social Security Numbers. |
---
version: "latest"
language: "en"
---
# Overview
## Basic Usage
Simply by installing the plugin, secrets in code and other text files will be highlighted as a warning. You can configure the error level of the inspection in your [inspection profile settings](https://www.jetbrains.com/help/idea/code-inspection.html).
You will also be given the option to delete the secret in any text file that is inspected via the context popup when your caret is over the inspected secret.
In contexts detected to be code that supports the allowlist pragma, you will also be given the option to append the relevant comment to the end of the line.
## Installation
### Installing from the JetBrains Marketplace
Follow the [instructions created by JetBrains](https://www.jetbrains.com/help/idea/managing-plugins.html#install_plugin_from_repo) to install a plugin from the Marketplace. "Soteri Security Scanner" is the name of the plugin to search for. You can also use this interface to pay for a license.
### Installing a custom build
Follow the [instructions created by JetBrains](https://www.jetbrains.com/help/idea/managing-plugins.html#install_plugin_from_disk) to install any custom build given to you by Soteri support. Your existing license from the marketplace should work the same.
---
version: "Working version"
language: "en"
---
# Scanning Service Documentation
## Scanning Service Documentation
Soteri's Scanning Service is currently in its Beta Phase. Use to get direct access to the powerful secret scanning behind Soteri's products.
*
### [Overview](https://docs.soteri.io/scanning-service/latest/overview.md)
*
#### [Scanning Content via REST API](https://docs.soteri.io/scanning-service/latest/scanning-content-via-rest-api.md)
*
#### [Parsing Scan REST API Responses](https://docs.soteri.io/scanning-service/latest/parsing-scan-rest-api-responses.md)
*
#### [Allow-listing False Positives](https://docs.soteri.io/scanning-service/latest/allow-listing-false-positives.md)
*
#### [Built-In Scanning Rules](https://docs.soteri.io/scanning-service/latest/built-in-scanning-rules.md)
*
#### [What is the GENERIC_PASSWORD rule and why is it disabled by default?](https://docs.soteri.io/scanning-service/latest/what-is-the-generic_password-rule-and-why-is-it-di.md)
*
#### [Generating client libraries via OpenAPI](https://docs.soteri.io/scanning-service/latest/generating-client-libraries-via-openapi.md)
*
#### [HTTP/2 Support](https://docs.soteri.io/scanning-service/latest/http-2-support.md)
*
#### [Quotas and Limits](https://docs.soteri.io/scanning-service/latest/quotas-and-limits.md)
---
version: "Working version"
language: "en"
---
# Allow-listing False Positives
Sometimes, Soteri Scanning can flag things which are not actually of concern. Though Soteri is always working to reduce false positives, in the meantime, you can disposition these false positives in your content by using an in-line allow-list pragma. These pragmas will not hide the finding in your scanning service results, but will set the `allowlisted` boolean in the finding to true.
## List of supported pragmas
* `# pragma: allowlist-secret`
* `// pragma: allowlist-secret`
* `/* pragma: allowlist-secret */`
* `' pragma: allowlist-secret`
* ``
To construct an allowlist pragma, insert one of the above lines exactly as shown as part of a comment that resides *on the same line* as the false positive.
There must also be a space between the code and either side of the pragma.
For ease of use, the pragma delimiters are chosen to be comment delimiters for a wide variety of environments.
### Python allow-listing example
API_KEY = "a0b1c2d3e4f5g6h7i8j9k0lMnOpQrStUvW" # pragma: allowlist-secret
#### Java allow-listing example
String myApprovedSecret = "ThisIsAnExampleSecret"; // pragma: allowlist-secret not actually a secret
#### C++ allow-listing example
int key = theSecretCredential; /* pragma: allowlist-secret */
#### HTML allow-listing example
#### MySQL allow-listing example
select * from users where cred='theSecretCredential'; -- # pragma: allowlist-secret
In this example, we're using the `#` approved pragma delimiter but embedding it in a single-line SQL comment delimited by `--`, so that this line is still functional. (Note the space between the `--` and the `#`.)
#### XML example with embedded character data representing an executable MySQL command
Make sure that the allow-listing is inline! Multi-line allow-listing is not supported.
---
version: "Working version"
language: "en"
---
# Built-In Scanning Rules
Here is the list of vulnerabilities that are currently detected by [Soteri](https://marketplace.atlassian.com/vendors/1219549/soteri)'s built-in scanning rules.
## IT Services
| **Rule Name** | **Description** |
|------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| `AWS_CLIENT_ID` | [**AWS Identity and Access Management Client IDs**](https://docs.aws.amazon.com/IAM/latest/UserGuide/reference_identifiers.html#identifiers-unique-ids)uniquely reference users, access keys. These unique IDs can provide access to your AWS instance by allowing users to get keys. |
| `AWS_MWS_KEY` | [**AWS Marketplace Web Service API Keys**](https://docs.developer.amazonservices.com/en_US/dev_guide/DG_Registering.html)allow programmatic interfaces to Amazon Seller stores. |
| `AWS_SECRET_ACCESS_KEY` | [**AWS Secret Access Keys**](https://aws.amazon.com/blogs/security/wheres-my-secret-access-key/)allow for authenticated AWS CLI, SDK, and API access. |
| `AZURE_ACCESS_KEY` | [**Azure Access Keys**](https://docs.microsoft.com/en-us/azure/storage/common/storage-account-keys-manage?tabs=azure-portal)provide access to all data stored in Microsoft Azure. |
| `DYNATRACE_CLIENT_SECRET` | [**Dynatrace Client Secrets**](https://www.dynatrace.com/support/help/dynatrace-api/basics/dynatrace-api-authentication/)allow for access to your Dynatrace instance API. |
| `EC_PRIVATE_KEY` | **Elliptical Curve Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `FACEBOOK_CLIENT_ID` | **Facebook Application IDs** |
| `FACEBOOK_SECRET_KEY` | **Facebook Application Secrets** |
| `GENERIC_API_KEY` | **Generic API Key -**Contains logic to detect generic API Keys. |
| `GENERIC_PASSWORD` | **Generic Passwords** - Contains logic to detect generic passwords. *Note that this rule may generate many false positives, and is disabled by default.* |
| `GENERIC_SECRET` | **Generic Secrets** - Contains logic to detect generic secrets. |
| `GITHUB_KEY` | **Github Authentication Tokens** - This rule detects classic Github Authentication Tokens for [personal use](https://docs.github.com/en/github/authenticating-to-github/keeping-your-account-and-data-secure/creating-a-personal-access-token) (both "[classic](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-personal-access-token-classic)" and "[fine-grained](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-fine-grained-personal-access-token)"), as well as for Github Application OAuth. |
| `GOOGLE_API_KEY` | **Google API Keys** |
| `GOOGLE_OAUTH` | **Google OAuth URLs** |
| `GOOGLE_OAUTH_ACCESS_TOKEN` | **Google OAuth Tokens** |
| `HEROKU_API_KEY` | **Heroku API Keys** |
| `LINKEDIN_CLIENT_ID` | **LinkedIn Client IDs** |
| `LINKEDIN_CLIENT_SECRET` | **LinkedIn Client Secrets** |
| `MAILCHIMP_API_KEY` | **Mailchimp API Key** |
| `MAILGUN_API_KEY` | **Mailgun API Key** |
| `PASSWORD_IN_URL` | **Generic Password in URL**- Contains logic to detect passwords embedded in URLs |
| `PAYPAL_BRAINTREE_ACCESS_TOKEN` | [**Paypal's Braintree Access Token**](https://developer.paypal.com/braintree/docs/guides/authorization/tokenization-key) |
| `PGP_PRIVATE_KEY` | [**PGP**](https://en.wikipedia.org/wiki/Pretty_Good_Privacy)**Private Keys** |
| `PKCS8_PRIVATE_KEY` | **PKSC8 Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `PYPI_UPLOAD_TOKEN` | [**Python Package Index (PyPI) Upload Tokens**](https://pypi.org/help/#apitoken)allow verified publishing of python package to the global repository. |
| `RSA_PRIVATE_KEY` | We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SENDGRID_API_KEY` | [**Sendgrid API Keys**](https://docs.sendgrid.com/api-reference/api-keys/create-api-keys) |
| `SHOPIFY_PARTNER_API_ACCESS_TOKEN` | [**Shopify Partner API access Tokens**](https://shopify.dev/api/partner/getting-started)provide access to the a given store's API. |
| `SHOPIFY_SECRETS` | [**Shopify API Secrets**](https://shopify.dev/api/partner/getting-started) give access to all aspects of the general Shopify API -- this rule contains logic to detect Shared Secrets and Access Tokens for regular, Custom, and Private applications. |
| `SLACK` | [**Slack API Tokens**](https://api.slack.com/authentication/token-types) give access to various API features. |
| `SLACK_WEBHOOK` | [**Slack Webhooks**](https://api.slack.com/messaging/webhooks)are secret URLs which give similar access as API Tokens. |
| `SQUARE_ACCESS_TOKEN` | **Square Access Tokens** |
| `SQUARE_OAUTH_SECRET` | **Square OAuth Secrets** |
| `SSH_PRIVATE_KEY` | **Generic SSH Private Key** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SSH_PUBLIC_KEY` | **Public Key** -half of key-based authentication. Weak public keys can be brute-force cracked by modern computers, and can represent equal vulnerability to the private-key half of the pair. *Since properly-generated public keys are not a threat, this rule is disabled by default.* |
| `TROJAN_SOURCE` | **Trojan Source** detects left-to-right and right-to-left unicode control characters which can be used to obscure malicious code. For more information, see the [Trojan Source paper](https://www.trojansource.codes/trojan-source.pdf) and [CVE-2021-42574 in the NIST Database](https://nvd.nist.gov/vuln/detail/CVE-2021-42574). *Note:* the homoglyph attack described in this paper, and tracked as CVE-2021-42694 in the NIST Database, is **not** detected by this rule, as it can generate a lot of false positives for non-English languages. See "[Mitigating Trojan Source Attacks](https://docs.soteri.io/security-for-bitbucket/latest/mitigating-trojan-source-attacks)" for Soteri's recommendations if you're interested in detecting potential homoglyph attacks. |
| `STRIPE_API_KEY` | **Stripe API Key** |
| `TWILIO_ACCOUNT_ID` | **Twilio Account ID** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWILIO_API_KEY` | **Twilio API Key** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWITTER_CLIENT_ID` | **Twitter Client ID** |
| `TWITTER_SECRET_KEY` | **Twitter Secret Key** |
## Financial
| **Rule Name** | **Description** |
|---------------------------|-------------------------------------------------------------------------------------------------------------|
| `BANK_INFORMATION` | Detects bank account information like routing numbers, etc. which may accompany more sensitive information. |
| `CREDIT_CARD_NUMBERS` | Detects credit card numbers. |
| `SOCIAL_SECURITY_NUMBERS` | Detects United States Social Security Numbers. |
---
version: "Working version"
language: "en"
---
# Generating client libraries via OpenAPI
Soteri's Scanning Service publishes an [OpenAPI 3.0 Schema](https://swagger.io/specification/) at .
You can interactively browse this schema [here](https://api.soteri.io/).
## Generating API Clients
You can use [OpenAPI Generator](https://github.com/OpenAPITools/openapi-generator) to generate API client libraries in a variety of languages.
### Install OpenAPI Generator
See the OpenAPI Generator [README](https://github.com/OpenAPITools/openapi-generator#1---installation). On mac, you can use [homebrew](https://brew.sh/):
Bash
brew install openapi-generator
### Generate a client library of your preferred language
To generate a client (for example, with python):
Bash
openapi-generator generate -i https//api.soteri.io/api-schema -g python -o soteri-api-client
The generated client has a `README`, which includes examples of how to use the client library. For example, the generated python client would be used like this:
Python
import time
import openapi_client
from openapi_client.api import scanning_api_api
from openapi_client.model.overall_response import OverallResponse
from pprint import pprint
# Defining the host is optional and defaults to https://api.soteri.io
# See configuration.py for a list of all supported configuration parameters.
configuration = openapi_client.Configuration(
host = "https://api.soteri.io"
)
# Enter a context with an instance of the API client
with openapi_client.ApiClient() as api_client:
# Create an instance of the API class
api_instance = scanning_api_api.ScanningAPIApi(api_client)
include_allowlisted = False # bool | If true, include allowlisted findings. (optional) if omitted the server will use the default value of False
file = [
open('/path/to/file', 'rb'),
] # [file_type] | The files to be scanned. (optional)
# example passing only required values which don't have defaults set
# and optional values
try:
api_response = api_instance.scan(include_allowlisted=include_allowlisted, file=file)
pprint(api_response)
except openapi_client.ApiException as e:
print("Exception when calling ScanningAPIApi->scan: %s\n" % e)
---
version: "Working version"
language: "en"
---
# HTTP/2 Support
Soteri's Scanning Service supports HTTP/2. To take advantage, use a HTTP/2 compatible client.
## curl
curl 7.47.0 and greater [enables HTTP/2 by default](https://curl.se/docs/http2.html). You can pass `--http2-prior-knowledge` to skip the HTTP/1.1 negotiation up to HTTP/2:
Bash
curl --http2-prior-knowledge -F file=@"file.txt" https://api.soteri.io/rest/scan
## python
[HTTPX](https://www.python-httpx.org/) is a python library which provides [support](https://www.python-httpx.org/http2/) for HTTP/2 requests. ([requests](https://docs.python-requests.org/en/latest/) does not currently provide this support). First, install optional HTTP/2 requirements in your environment:
Bash
pip install httpx[http2]
Then, you can make requests like so:
Python
import asyncio
import httpx
from pprint import pprint
async def request():
params = {
'includeAllowlisted': 'true',
}
files = [
('file', ('file-1.txt', open('file-1.txt', 'rb'))),
('file', ('file-2.txt', open('file-2.txt', 'rb'))),
]
async with httpx.AsyncClient(http2=True) as client:
response = await client.post("https://api.soteri.io/rest/scan", params=params, files=files)
response.raise_for_status()
return response.json()
response = asyncio.run(request())
pprint(response)
---
version: "Working version"
language: "en"
---
# Overview
Soteri's Scanning Service gives access to the powerful scanning technology behind Soteri's products, like [Security for Bitbucket](https://marketplace.atlassian.com/apps/1221399/security-for-bitbucket-soteri) and [Security for Confluence](https://marketplace.atlassian.com/apps/1224167/security-for-confluence-soteri). Use Soteri Scanning to audit for login credentials, API keys, banking information, personally identifiable information (PII), and more. See [Built-In Scanning Rules](https://docs.soteri.io/scanning-service/latest/built-in-scanning-rules.md) for more details.
## Try It Out!
Visit our [API browser](https://api.soteri.io/) to try it out today!
## Examples
For examples of how to use Soteri's Scanning API:
* Learn how to use our REST API: [Scanning Content via REST API](https://docs.soteri.io/scanning-service/latest/scanning-content-via-rest-api.md)
* Find [example applications on Github](https://github.com/soteri-security/scanning-service-examples).
* Generate client libraries using OpenAPI: [Generating client libraries via OpenAPI](https://docs.soteri.io/scanning-service/latest/generating-client-libraries-via-openapi.md)
*** ** * ** ***
## On User Data
Soteri's Scanning Service does not store any user data. All content sent to the Scanning API is immediately discarded after scanning.
*** ** * ** ***
Soteri's Scanning Service is in its Beta phase. This means the API is subject to change.
---
version: "Working version"
language: "en"
---
# Parsing Scan REST API Responses
The Soteri Scanning Service REST API returns JSON-formatted responses. For examples of responses and a full schema, visit our [API browser](https://api.soteri.io/).
---
version: "Working version"
language: "en"
---
# Quotas and Limits
The following limits are imposed on REST API calls to Soteri's Scanning Service:
* Scan Requests
* HTTP 1 requests are limited to \~32MB. This includes the size of all files which are to be scanned.
* HTTP 2 requests are not limited in size.
* Single scan responses are limited to \~32MB.
* Scan jobs in general should not hit this limit. Please contact [Soteri Support](https://support.soteri.io/) if you do.
* Currently, only UTF-8 encoded text files can be scanned. Any other files will be skipped.
* The number of findings per-file is limited to 10,000. Further findings will not be reported, and the rest of the file will not be scanned.
---
version: "Working version"
language: "en"
---
# Scanning Content via REST API
Currently, the only way to use Soteri's Scanning Service is via the rest API.
**Try it out by visiting our** [**API browser**](https://api.soteri.io/)**!**
Soteri's Scanning Service does not store any user data. All content sent to the Scanning API is immediately discarded after scanning.
## Scan a Single File
Using [curl](https://curl.se/):
Bash
curl -F file=@"file.txt" https://api.soteri.io/rest/scan
Using python's [Requests](https://docs.python-requests.org/en/latest/) library:
Python
import requests
files = {
'file': ('file.txt', open('file.txt', 'rb')),
}
response = requests.post('https://api.soteri.io/rest/scan', files=files)
## Scan Multiple Files
The same endpoint can be used to scan multiple files. Please note the [Quotas and Limits](https://docs.soteri.io/scanning-service/latest/quotas-and-limits.md) imposed.
Using curl:
Bash
curl -F file=@"file-1.txt" -F file=@"file-2.txt" https://api.soteri.io/rest/scan
Using python's Requests library:
Python
import requests
files = [
('file', ('file-1.txt', open('file-1.txt', 'rb'))),
('file', ('file-2.txt', open('file-2.txt', 'rb'))),
]
response = requests.post('https://api.soteri.io/rest/scan', files=files)
## Request Query Parameters
By default:
* Files which have no findings are not included in results. To see the, include them `includeEmpty` query parameter.
* Files which were skipped (could not be scanned because they were not in a supported file format) are not included in results. To see them, include the `includeSkipped` query parameter.
* Allow-listed findings are not included in results. To see them, include the `includeAllowlisted` query parameter. For more information on allow-listing, see [Allow-listing False Positives](https://docs.soteri.io/scanning-service/latest/allow-listing-false-positives.md).
Bash
curl -F file=@"file.txt" https://api.soteri.io/rest/scan?includeEmpty=true&includeSkipped=true&includeAllowlisted=true
Using python's Requests library:
Python
import requests
params = {
'includeEmpty': 'true',
'includeSkipped': 'true',
'includeAllowlisted': 'true',
}
files = {
'file': ('file.txt', open('file.txt', 'rb')),
}
response = requests.post('https://api.soteri.io/rest/scan', params=params, files=files)
## More Complete Examples
More complete examples can be found in our example [application repository on Github](https://github.com/soteri-security/scanning-service-examples).
---
version: "Working version"
language: "en"
---
# What is the GENERIC\_PASSWORD rule and why is it disabled by default?
The GENERIC_PASSWORD rule is off by default because it's a bit different than the other rules -- rather than matching a very specific key type, with minimal false positives, it searches for general occurrences and variations of the term "password". This rule is meant to catch the unintentional use of passwords in code or documentation.
However, due to its broad nature, this rule generates many false positives; to enable it would require your organization to set up a process to review and disposition them. We feel that you would better know if your organization would have the resources available for such a process.
---
version: "latest"
language: "en"
---
# Security for Confluence Data Center Documentation
## Security for Confluence Data Center Documentation
Add extra security to your Confluence workflow. Scan pages and blog posts for leaked passwords, private keys, cloud credentials, etc.
*
### [Overview](https://docs.soteri.io/security-for-confluence-dc/latest/overview.md)
*
#### [Built-In Scanning Rules](https://docs.soteri.io/security-for-confluence-dc/latest/built-in-scanning-rules.md)
*
#### [Security Analysis: Viewing scan results for a space](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md)
*
#### [The Soteri Dashboard: Viewing Confluence's overall security status](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md)
*
#### [Granting Access to Additional Users and Groups](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md)
*
#### [Hiding false positives, revoked credentials, etc.](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md)
*
#### [Exporting Findings](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md)
*
#### [Enabling and Disabling Scanning Rules](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-and-disabling-global-scanning-rules.md)
*
#### [Defining Custom Detection Rules](https://docs.soteri.io/security-for-confluence-dc/latest/defining-custom-detection-rules.md)
*
#### [Automatically Scanning Content](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md)
*
#### [Email notifications for content authors](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md)
*
#### [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md)
*
#### [Scanning Files Attached to Pages](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-files-attached-to-pages.md)
*
#### [Scanning Comments](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-comments.md)
*
#### [REST API For Scripting and Automation](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md)
#### [Frequently Asked Questions (FAQ) and Troubleshooting](https://docs.soteri.io/security-for-confluence-dc/latest/frequently-asked-questions-faq-and-troubleshooting.md)
*
#### [Security for Confluence Data Center Cookbook](https://docs.soteri.io/security-for-confluence-dc/latest/security-for-confluence-data-center-cookbook.md)
---
version: "latest"
language: "en"
---
# Accessing the Settings Page
The Security for Confluence Settings page allows you to adjust a variety of important administration settings.
Only Confluence administrators, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), can access these settings.
The easiest way to access the Settings page is directly from the Security Analysis Page, by clicking the gear icon:
Administrators may also access the Security for Confluence settings by first going to the Confluence General configuration settings:
and then selecting "Settings" under "Soteri Security" in the left side of the window:
---
version: "latest"
language: "en"
---
# Automatically Scanning Content
By default, Security for Confluence will automatically scan newly created spaces, spaces copied via the Confluence built-in copy-space functionality, and imported spaces. For existing spaces *which have been scanned at least once*, Security for Confluence can automatically scan new and updated content.
If an existing space has **not** been scanned, Security for Confluence will **not** automatically scan new and updated content for it. This gives administrators more control over the available computing resources, preventing a potentially large scan from running unexpectedly.
If a space is created by a third-party app, Security for Confluence is not guaranteed to completely scan the space. Administrators are strongly encouraged to manually scan the space at least once.
The automatic scanning status of a given space can be seen in its [Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md).
Auto-scanning can be disabled by a Confluence administrator or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md). Simply visit the [Settings Page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md) and toggle the "Keep space scans up-to-date" switch.
Only Confluence administrators and any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) have access to these settings.
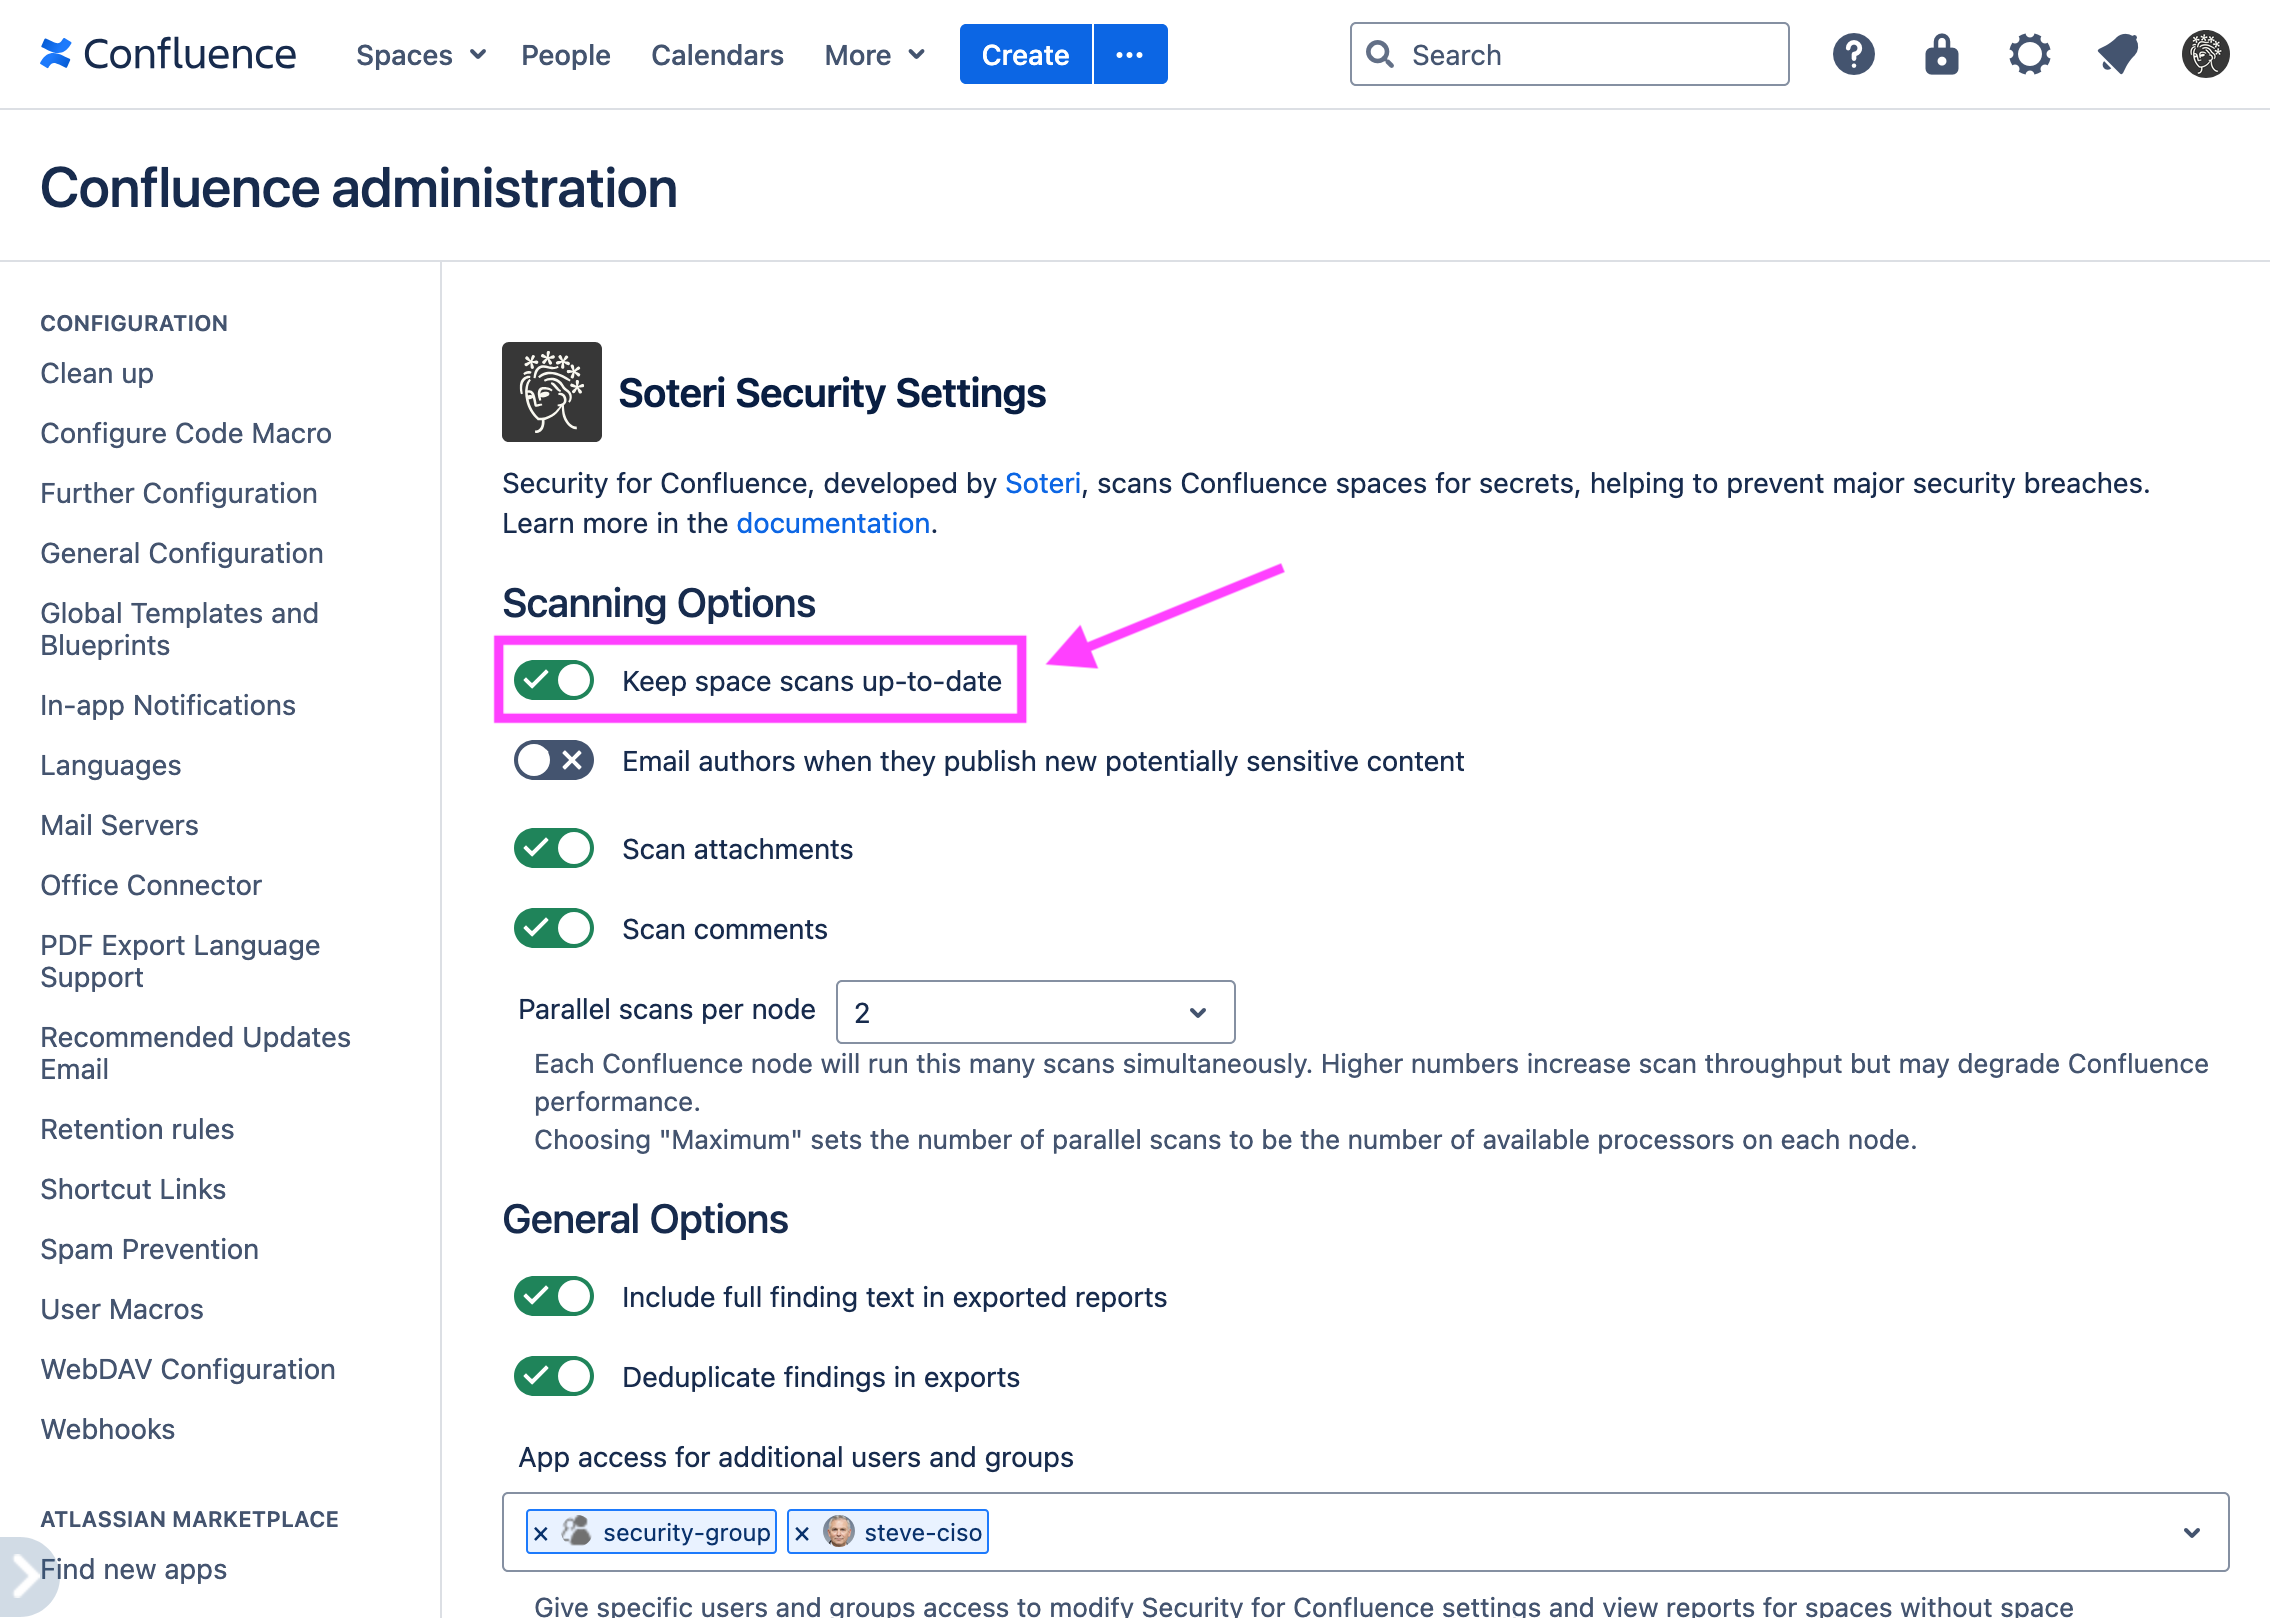
If "Keep space scans up-to-date" is disabled, no [audit log event](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md#new-finding-event) will be published when users publish content containing new findings.
If auto-scanning is changed, reloading the Security Analysis for a space will reflect the change.
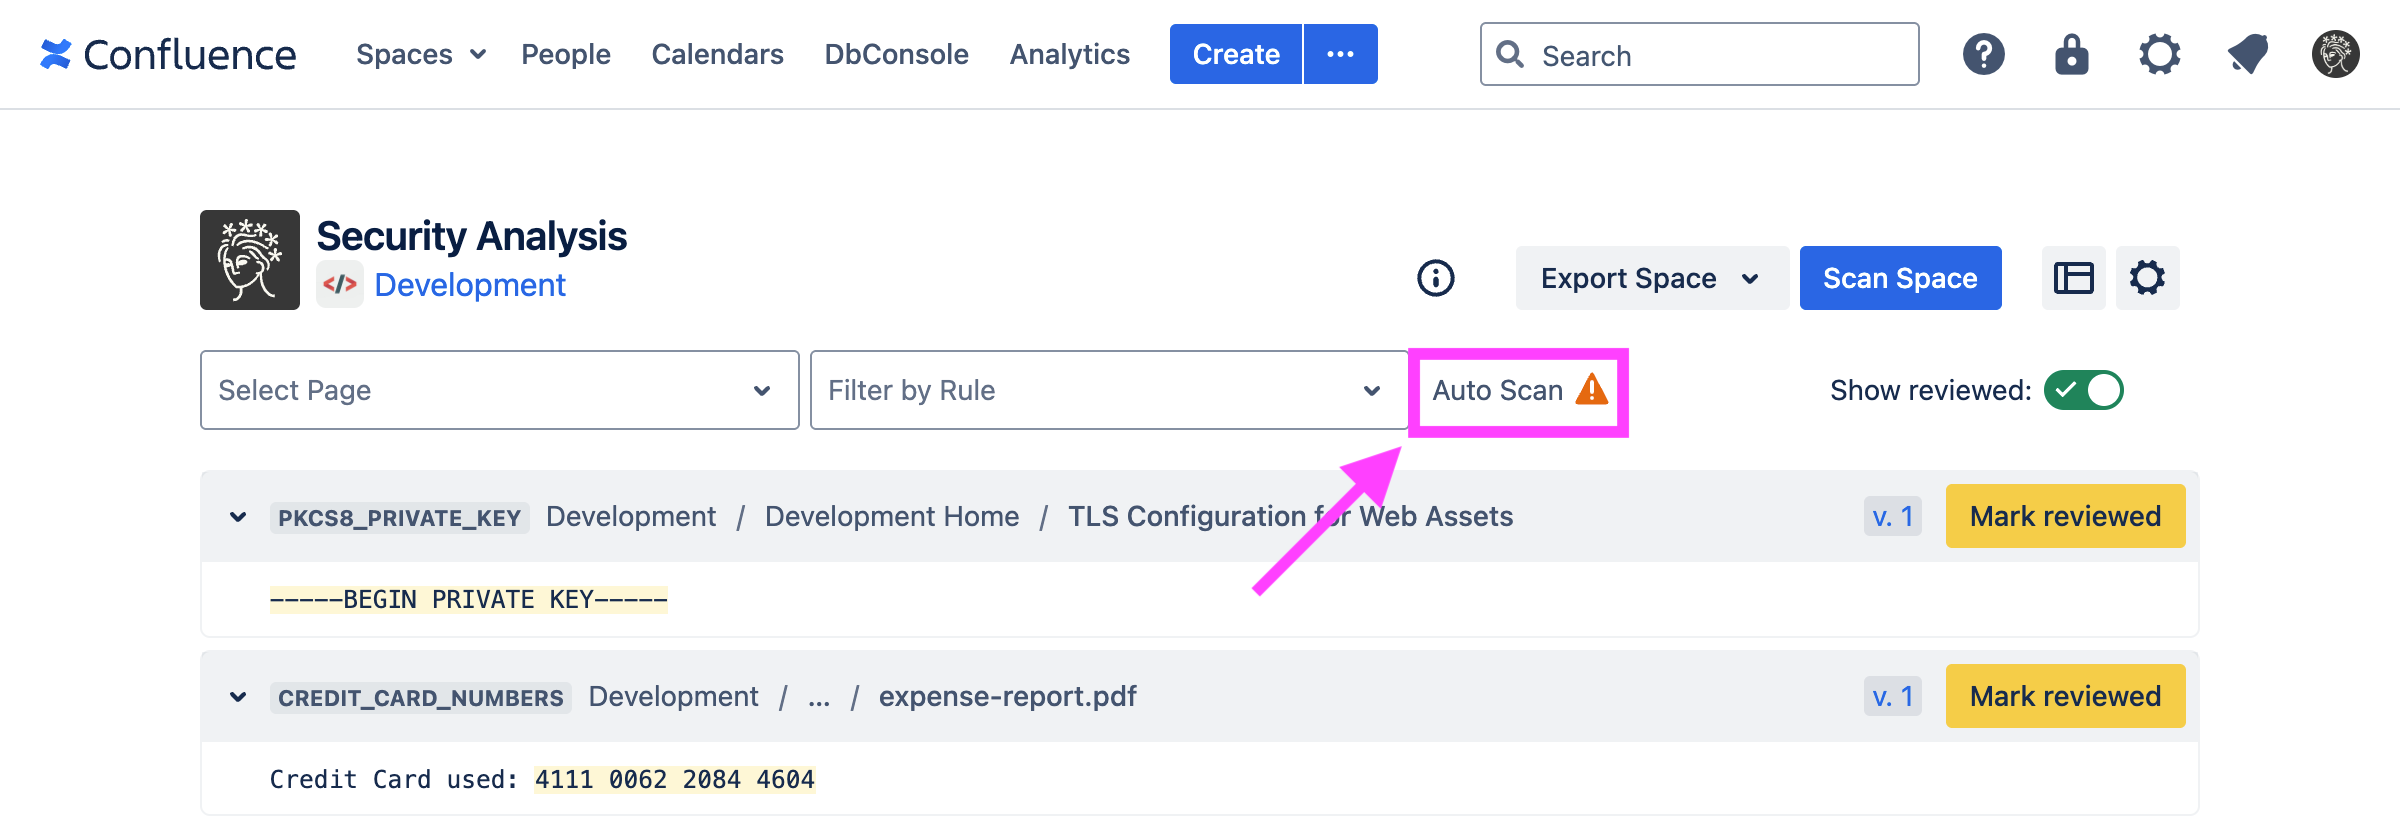
When auto-scanning is enabled, Security for Confluence can also notify content authors when they publish potentially sensitive information automatically. See [Email notifications for content authors](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md) for more details.
---
version: "latest"
language: "en"
---
# Built-In Scanning Rules
Here is the list of vulnerabilities that are currently detected by [Soteri](https://marketplace.atlassian.com/vendors/1219549/soteri)'s built-in scanning rules.
## IT Services
| **Rule Name** | **Description** |
|------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| `AWS_CLIENT_ID` | [**AWS Identity and Access Management Client IDs**](https://docs.aws.amazon.com/IAM/latest/UserGuide/reference_identifiers.html#identifiers-unique-ids)uniquely reference users, access keys. These unique IDs can provide access to your AWS instance by allowing users to get keys. |
| `AWS_MWS_KEY` | [**AWS Marketplace Web Service API Keys**](https://docs.developer.amazonservices.com/en_US/dev_guide/DG_Registering.html)allow programmatic interfaces to Amazon Seller stores. |
| `AWS_SECRET_ACCESS_KEY` | [**AWS Secret Access Keys**](https://aws.amazon.com/blogs/security/wheres-my-secret-access-key/)allow for authenticated AWS CLI, SDK, and API access. |
| `AZURE_ACCESS_KEY` | [**Azure Access Keys**](https://docs.microsoft.com/en-us/azure/storage/common/storage-account-keys-manage?tabs=azure-portal)provide access to all data stored in Microsoft Azure. |
| `DYNATRACE_CLIENT_SECRET` | [**Dynatrace Client Secrets**](https://www.dynatrace.com/support/help/dynatrace-api/basics/dynatrace-api-authentication/)allow for access to your Dynatrace instance API. |
| `EC_PRIVATE_KEY` | **Elliptical Curve Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `FACEBOOK_CLIENT_ID` | **Facebook Application IDs** |
| `FACEBOOK_SECRET_KEY` | **Facebook Application Secrets** |
| `GENERIC_API_KEY` | **Generic API Key -**Contains logic to detect generic API Keys. |
| `GENERIC_PASSWORD` | **Generic Passwords** - Contains logic to detect generic passwords. *Note that this rule may generate many false positives, and is disabled by default.* |
| `GENERIC_SECRET` | **Generic Secrets** - Contains logic to detect generic secrets. |
| `GITHUB_KEY` | **Github Authentication Tokens** - This rule detects classic Github Authentication Tokens for [personal use](https://docs.github.com/en/github/authenticating-to-github/keeping-your-account-and-data-secure/creating-a-personal-access-token) (both "[classic](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-personal-access-token-classic)" and "[fine-grained](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-fine-grained-personal-access-token)"), as well as for Github Application OAuth. |
| `GOOGLE_API_KEY` | **Google API Keys** |
| `GOOGLE_OAUTH` | **Google OAuth URLs** |
| `GOOGLE_OAUTH_ACCESS_TOKEN` | **Google OAuth Tokens** |
| `HEROKU_API_KEY` | **Heroku API Keys** |
| `LINKEDIN_CLIENT_ID` | **LinkedIn Client IDs** |
| `LINKEDIN_CLIENT_SECRET` | **LinkedIn Client Secrets** |
| `MAILCHIMP_API_KEY` | **Mailchimp API Key** |
| `MAILGUN_API_KEY` | **Mailgun API Key** |
| `PASSWORD_IN_URL` | **Generic Password in URL**- Contains logic to detect passwords embedded in URLs |
| `PAYPAL_BRAINTREE_ACCESS_TOKEN` | [**Paypal's Braintree Access Token**](https://developer.paypal.com/braintree/docs/guides/authorization/tokenization-key) |
| `PGP_PRIVATE_KEY` | [**PGP**](https://en.wikipedia.org/wiki/Pretty_Good_Privacy)**Private Keys** |
| `PKCS8_PRIVATE_KEY` | **PKSC8 Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `PYPI_UPLOAD_TOKEN` | [**Python Package Index (PyPI) Upload Tokens**](https://pypi.org/help/#apitoken)allow verified publishing of python package to the global repository. |
| `RSA_PRIVATE_KEY` | We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SENDGRID_API_KEY` | [**Sendgrid API Keys**](https://docs.sendgrid.com/api-reference/api-keys/create-api-keys) |
| `SHOPIFY_PARTNER_API_ACCESS_TOKEN` | [**Shopify Partner API access Tokens**](https://shopify.dev/api/partner/getting-started)provide access to the a given store's API. |
| `SHOPIFY_SECRETS` | [**Shopify API Secrets**](https://shopify.dev/api/partner/getting-started) give access to all aspects of the general Shopify API -- this rule contains logic to detect Shared Secrets and Access Tokens for regular, Custom, and Private applications. |
| `SLACK` | [**Slack API Tokens**](https://api.slack.com/authentication/token-types) give access to various API features. |
| `SLACK_WEBHOOK` | [**Slack Webhooks**](https://api.slack.com/messaging/webhooks)are secret URLs which give similar access as API Tokens. |
| `SQUARE_ACCESS_TOKEN` | **Square Access Tokens** |
| `SQUARE_OAUTH_SECRET` | **Square OAuth Secrets** |
| `SSH_PRIVATE_KEY` | **Generic SSH Private Key** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SSH_PUBLIC_KEY` | **Public Key** -half of key-based authentication. Weak public keys can be brute-force cracked by modern computers, and can represent equal vulnerability to the private-key half of the pair. *Since properly-generated public keys are not a threat, this rule is disabled by default.* |
| `TROJAN_SOURCE` | **Trojan Source** detects left-to-right and right-to-left unicode control characters which can be used to obscure malicious code. For more information, see the [Trojan Source paper](https://www.trojansource.codes/trojan-source.pdf) and [CVE-2021-42574 in the NIST Database](https://nvd.nist.gov/vuln/detail/CVE-2021-42574). *Note:* the homoglyph attack described in this paper, and tracked as CVE-2021-42694 in the NIST Database, is **not** detected by this rule, as it can generate a lot of false positives for non-English languages. See "[Mitigating Trojan Source Attacks](https://docs.soteri.io/security-for-bitbucket/latest/mitigating-trojan-source-attacks)" for Soteri's recommendations if you're interested in detecting potential homoglyph attacks. |
| `STRIPE_API_KEY` | **Stripe API Key** |
| `TWILIO_ACCOUNT_ID` | **Twilio Account ID** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWILIO_API_KEY` | **Twilio API Key** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWITTER_CLIENT_ID` | **Twitter Client ID** |
| `TWITTER_SECRET_KEY` | **Twitter Secret Key** |
## Financial
| **Rule Name** | **Description** |
|---------------------------|-------------------------------------------------------------------------------------------------------------|
| `BANK_INFORMATION` | Detects bank account information like routing numbers, etc. which may accompany more sensitive information. |
| `CREDIT_CARD_NUMBERS` | Detects credit card numbers. |
| `SOCIAL_SECURITY_NUMBERS` | Detects United States Social Security Numbers. |
---
version: "latest"
language: "en"
---
# Creating support zips
When something goes wrong with Soteri's apps, our customers can take advantage of our [world-class support](https://support.soteri.io/). In order for our team to troubleshoot most issues with our Atlassian Data Center apps, we need **support zips** . To generate a support zip, [we recommend following Atlassian's instructions](https://confluence.atlassian.com/support/create-a-support-zip-790796819.html), and attaching it to your Soteri support ticket.
## What's in a support zip?
Atlassian support zips contain:
* Application \& servlet log files
* Access log files containing basic HTTP request information
* Information about the host platform, like JVM flags, database type, etc.
* Soteri Security for Confluence specific information in the `soteri-security-for-confluence` folder. This consists of selected global settings, and scanning rule configuration information.
## Why is it safe to send support zips to Soteri's support team?
* Soteri's apps never log sensitive data to host product logs.
* Atlassian's support zip utility automatically sanitizes **all** sensitive data and configuration, like database passwords. Here's an example of what the utility will do to sensitive data in configuration files:
Sanitized by Support UtilitySanitized by Support Utility
* We treat all support zip data as confidential, and our customers across sectors including banking and healthcare trust us with support zips for troubleshooting, as is standard practice with all Atlassian marketplace vendors.
If you have any questions, we recommend first reviewing the generated security zip contents with your organization's security team, and asking us any remaining questions you have.
---
version: "latest"
language: "en"
---
# Defining Custom Detection Rules
Security for Confluence allows you to create custom scanning rules using regular expressions. You can create and edit custom rules from the [Settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md), under "Custom rules":
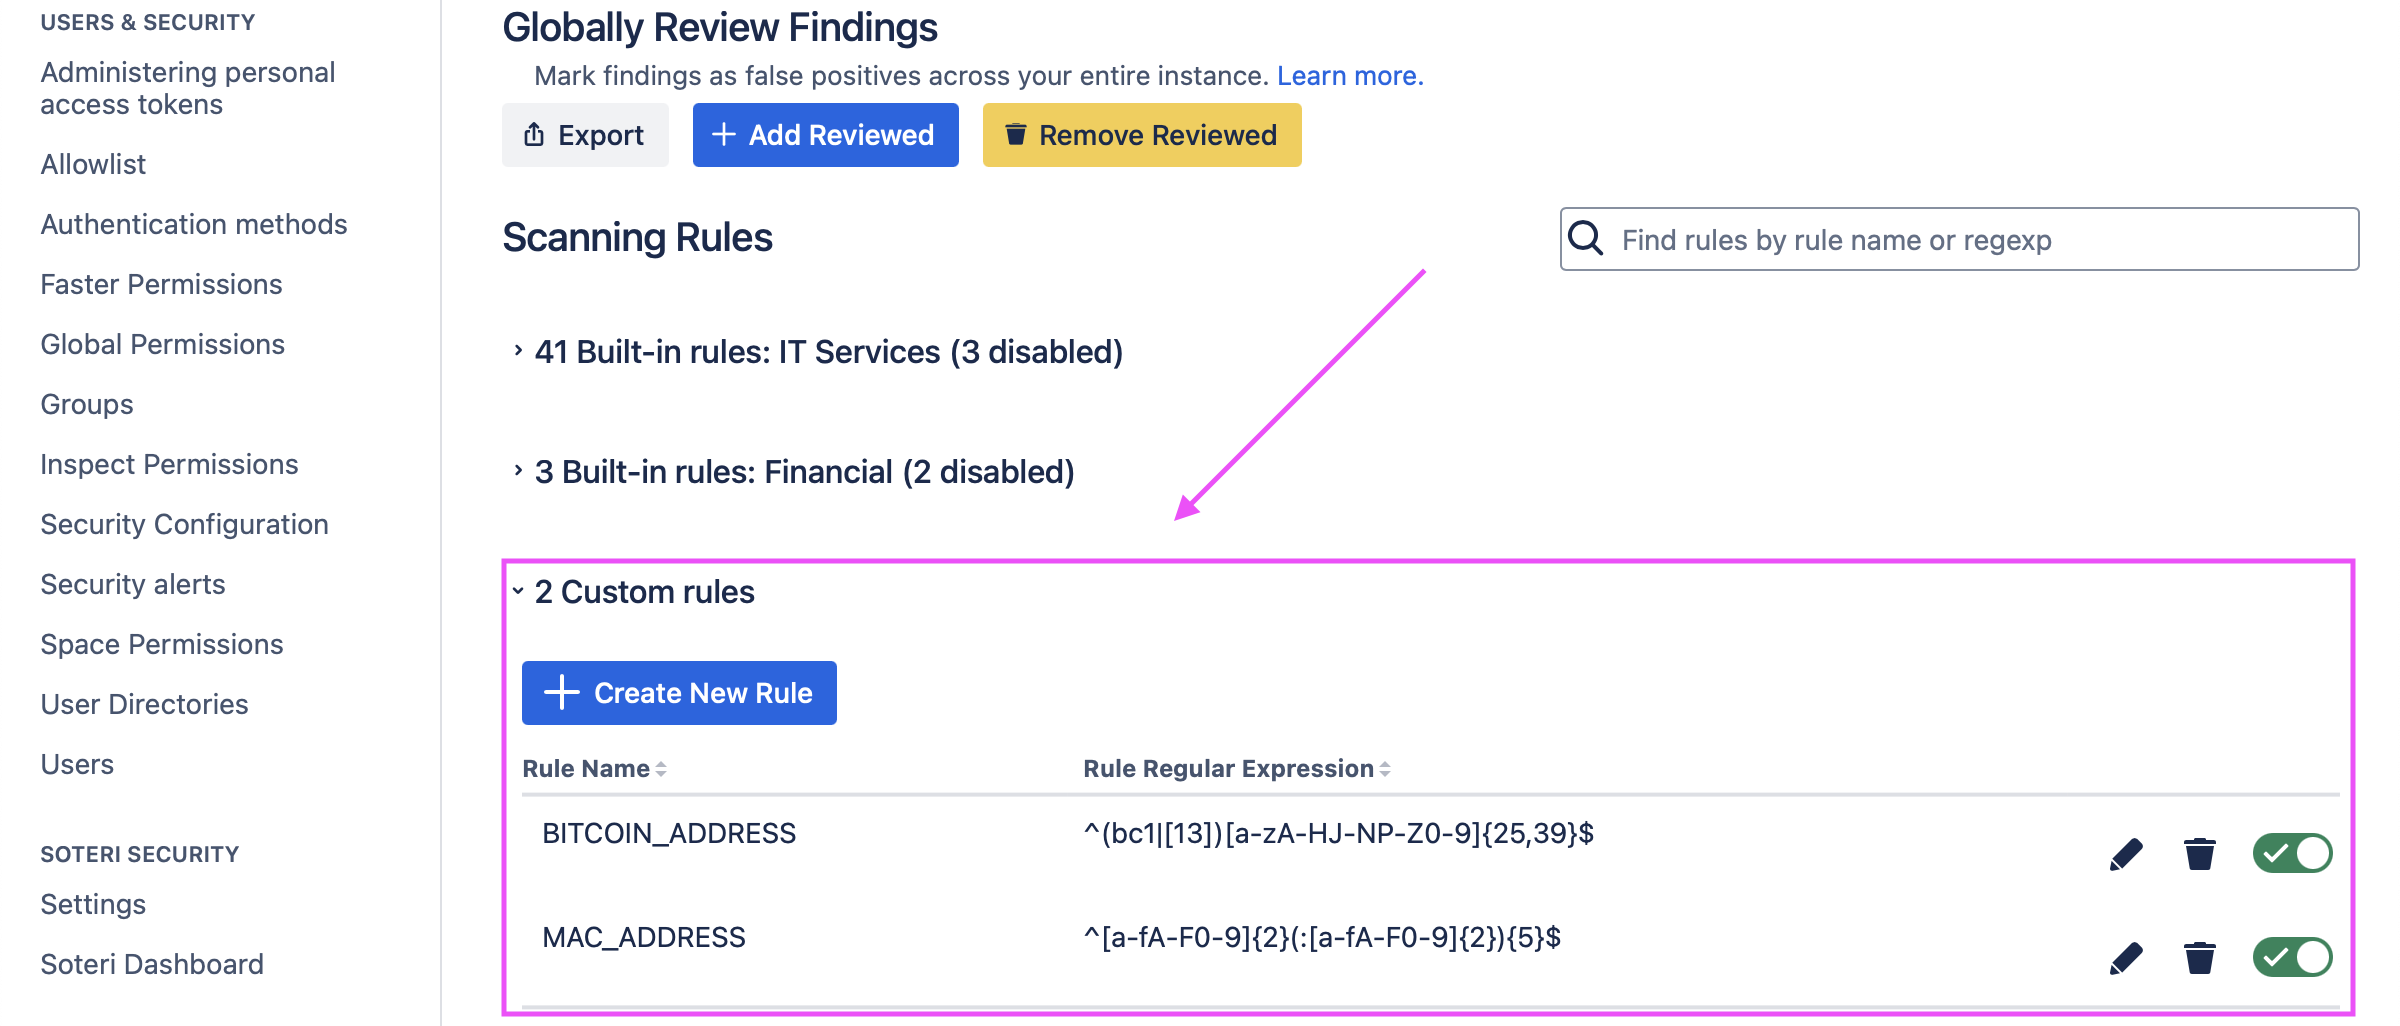
Only Confluence administrators and any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can access these settings.
Security for Confluence imposes limits on how much memory a rule can use and how long a rule can take to scan a page fragment. **Scanning rules which exceed these limits will be automatically disabled**, and the scan will be marked as failed.
If a secret in a single page fragment matches more than one rule (built-in or custom), only the first match will be reported.
## Developing custom rules
Our application uses the built-in JDK java regex library (Java 8). The supported regex constructs are [documented here](https://docs.oracle.com/javase/8/docs/api/java/util/regex/Pattern.html).
When creating or modifying a custom regex rule, a preview of matches that would be caught by a scan will be shown.
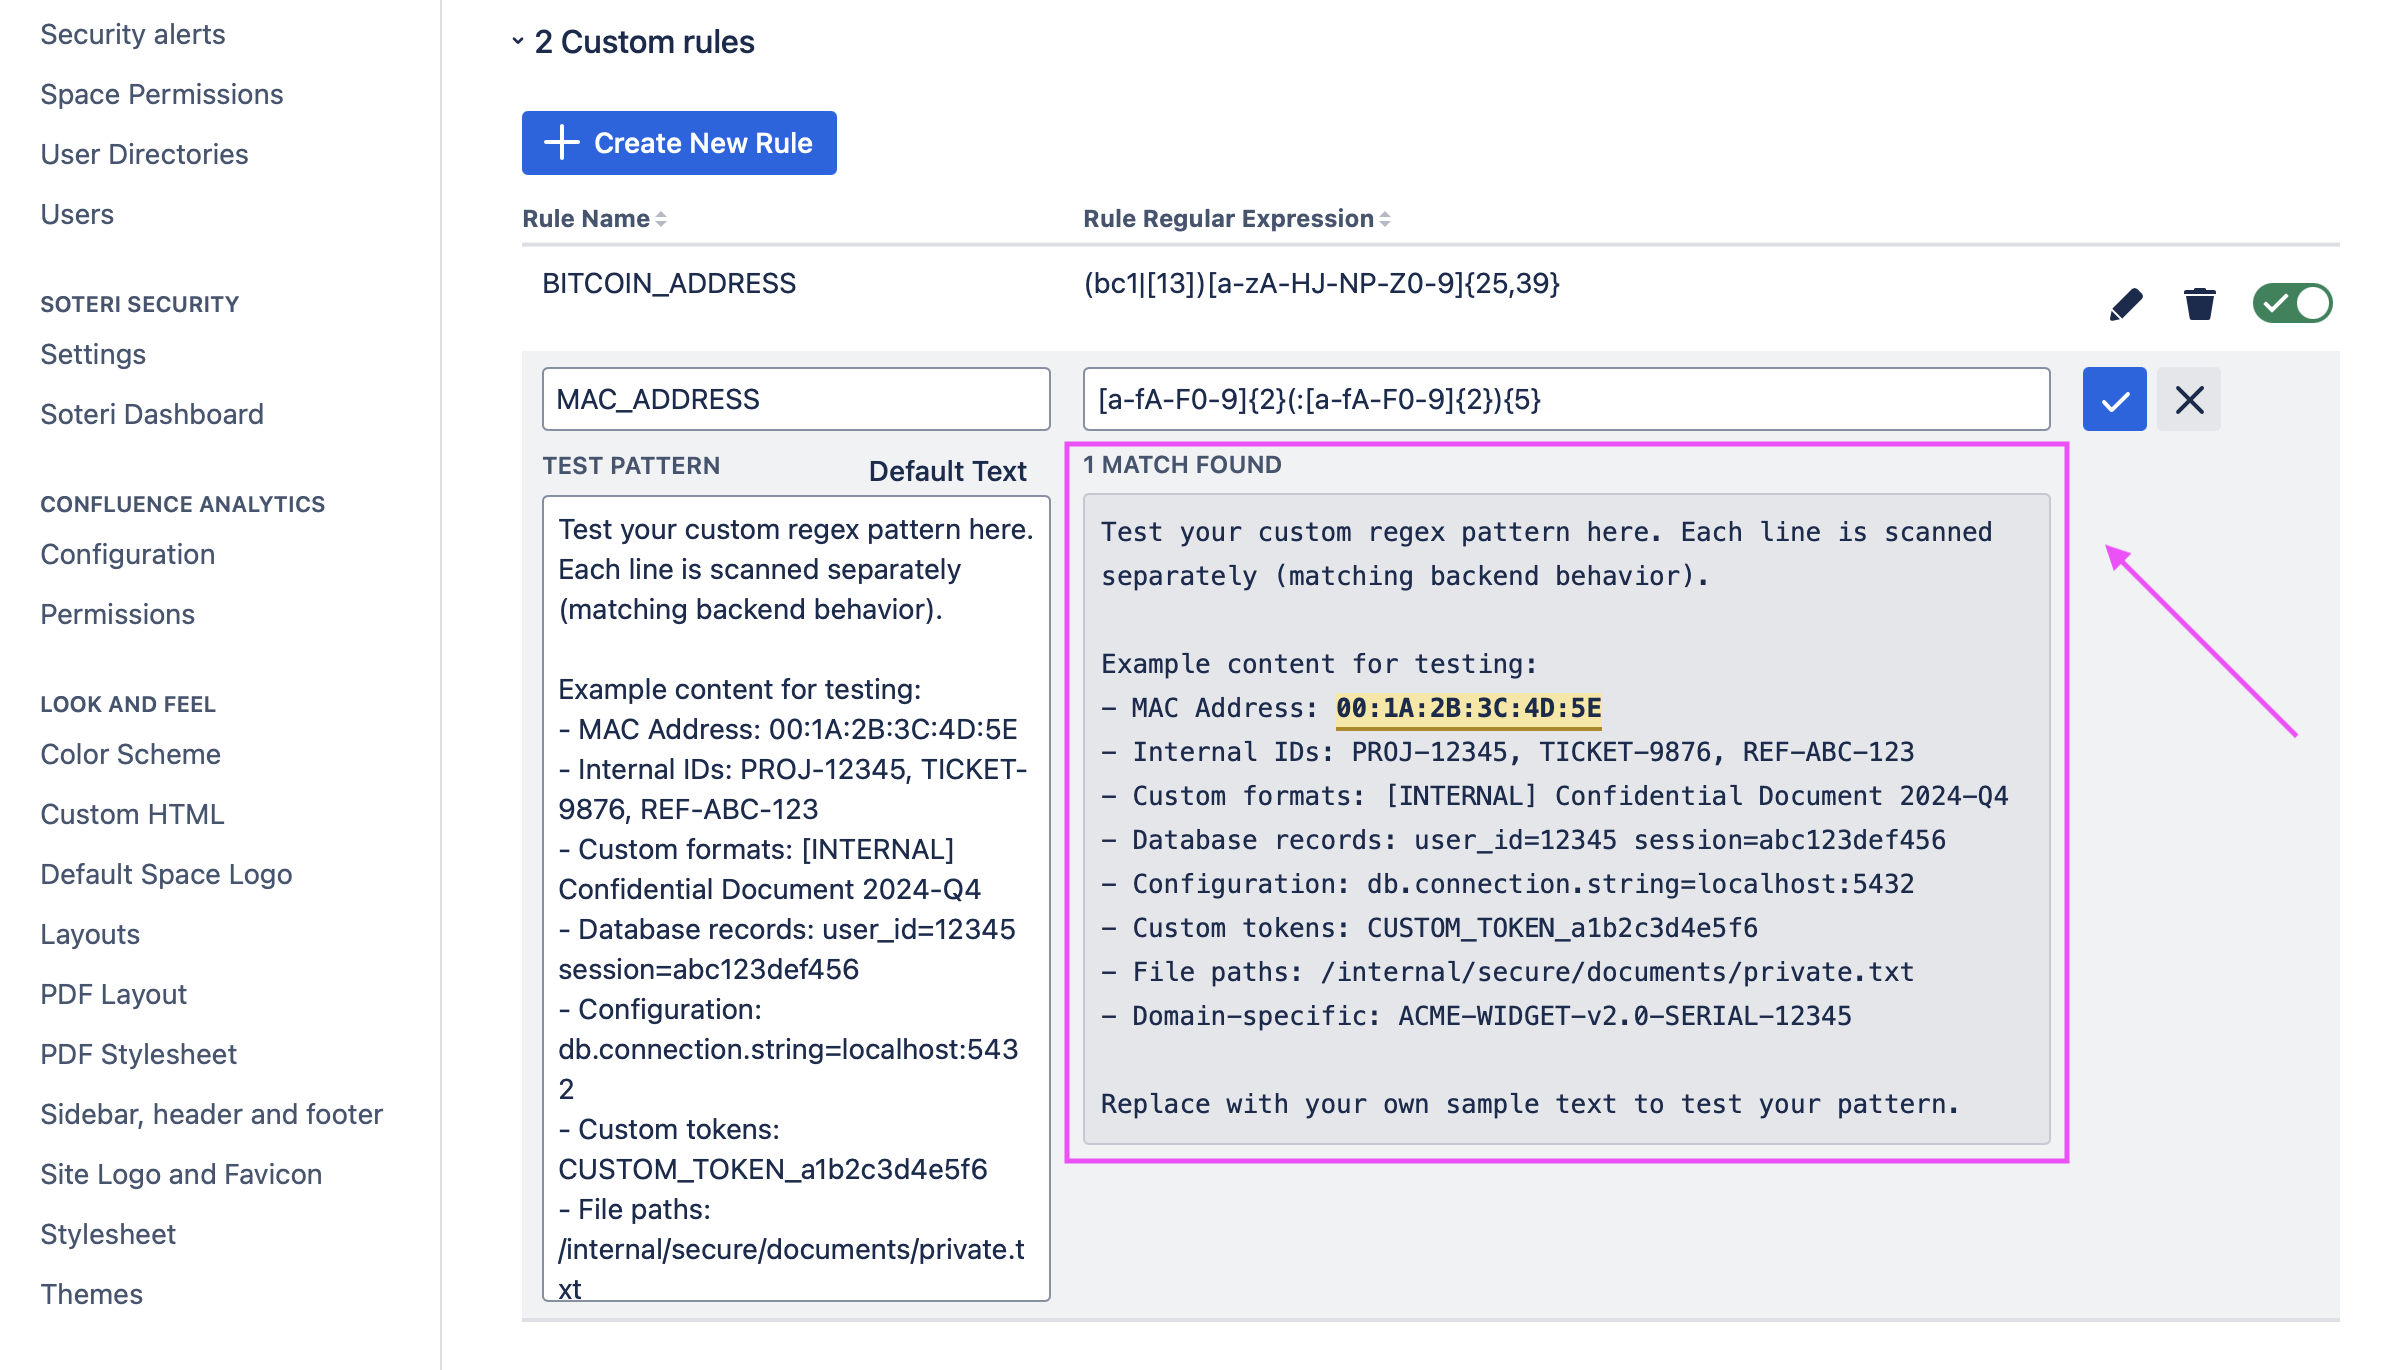
### Example custom rules
**Bitcoin Address**
^[13][a-km-zA-HJ-NP-Z0-9]{26,33}$
**Youtube Links**
]*)href=\"((?:https|http):\/\/\w{0,3}.youtube+\.\w{2,3}\/watch\?v=[\w-]{11})">(?:.*?)<\/a>
### Auditing changes to custom rules
All custom rule creation, deletion, and updates (including enabling/disabling), are logged to the Confluence Audit log. See [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md) for more information.
---
version: "latest"
language: "en"
---
# Email notifications for content authors
When Security for Confluence is configured to automatically scan new content, it can also send emails to authors of pages and blog posts notifying them when they publish potentially sensitive content. This functionality can be enabled by Confluence administrators, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), on the [Security for Confluence settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md).
When the "Keep space scans up-to-date" option is turned on, the option to turn on emails to content authors can also be enabled.
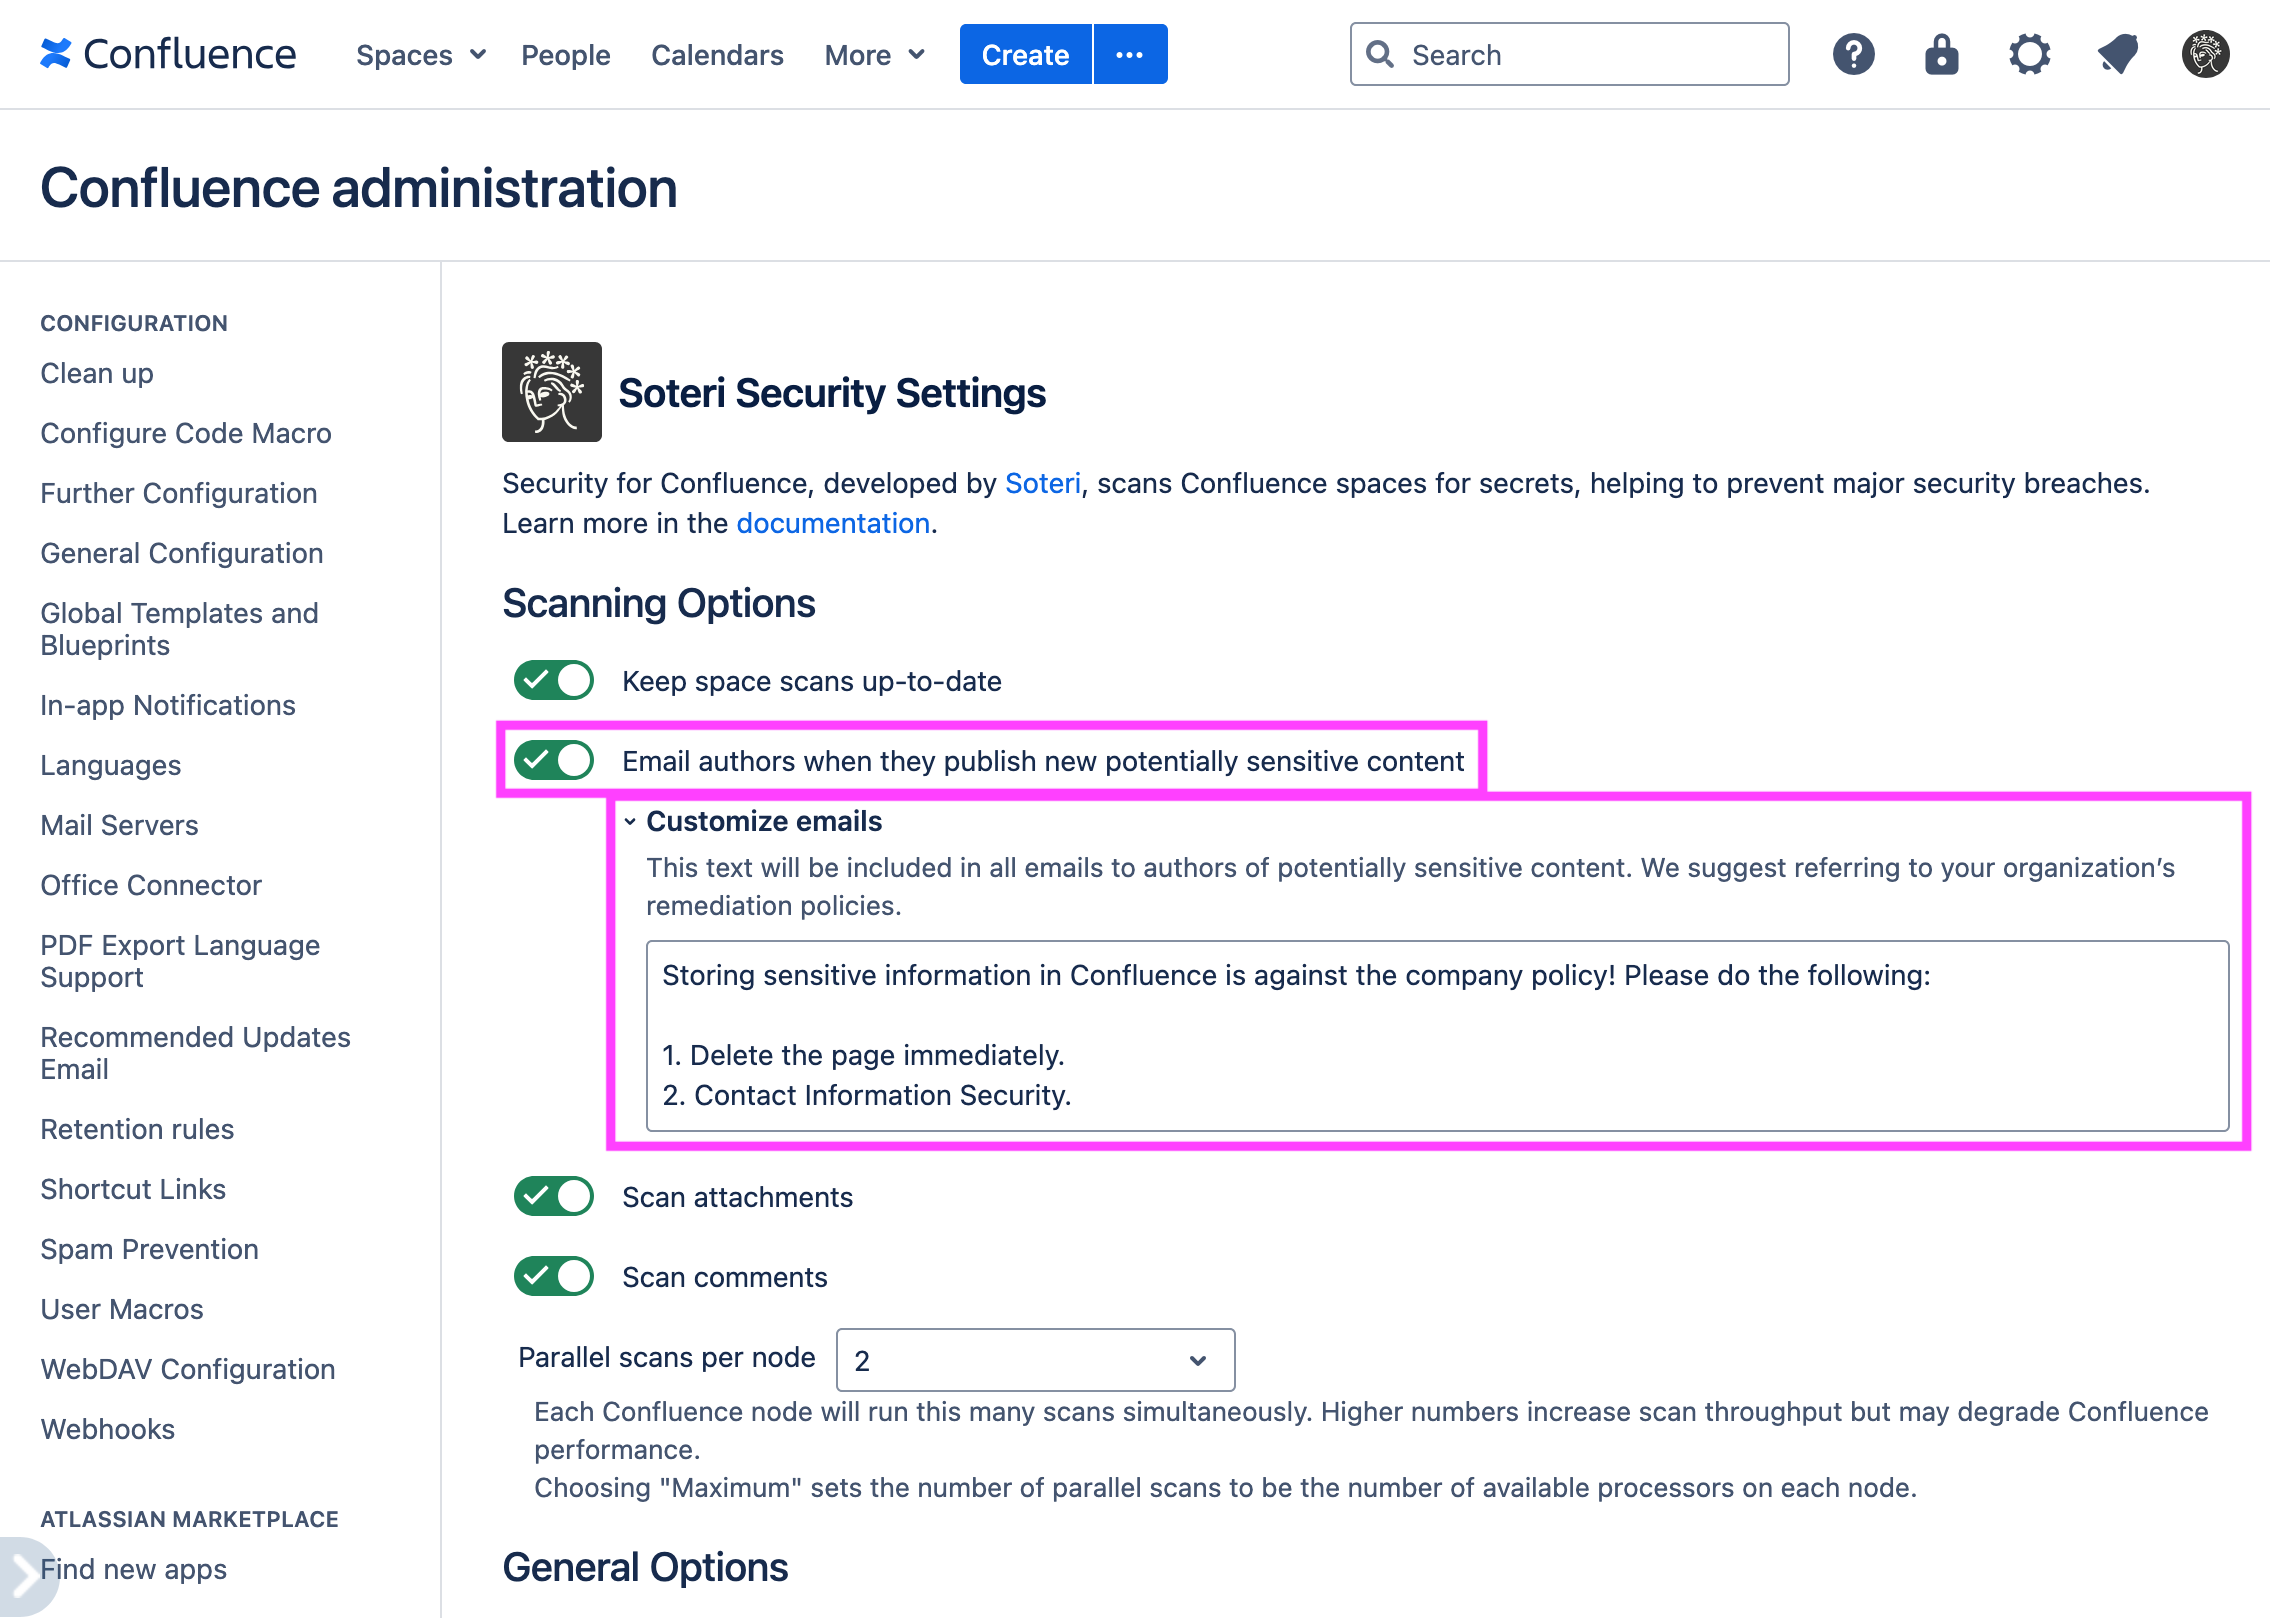
These emails contain:
* Links to the page, the space, and the diff which introduced the potentially sensitive content.
* A list of rules which were flagged.
* A link to the Security Analysis so page authors can see what was flagged, and [mark it as reviewed](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md) if appropriate.
* Any custom information your organization wants to include (see above). We recommend referring to your organization's remediation policies.
If the "Keep space scans up-to-date" option was previously disabled, then content authors might not get notifications until a full space scan is triggered.
Emails are **only** sent for new page or blog post versions, **not** for new attachment uploads or comments.
When an email is sent, this event is logged to the Confluence Audit Log. See [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md) for more information.
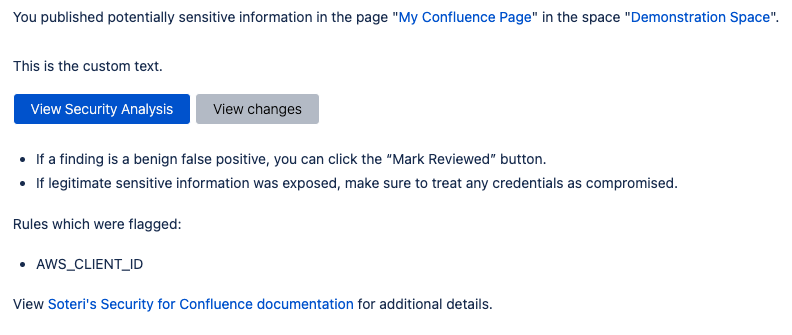
Screenshot of an example email to a content author, notifying them of potentially sensitive content.
---
version: "latest"
language: "en"
---
# Enabling and Disabling Scanning Rules
Security for Confluence allows you to disable scanning rules that don't fit the needs of your organization.
To enable or disable rules, visit the [Settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md), expand the relevant section under "Scanning Rules", and use the toggle switches as needed.
Only Confluence administrators and users granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can access these settings.
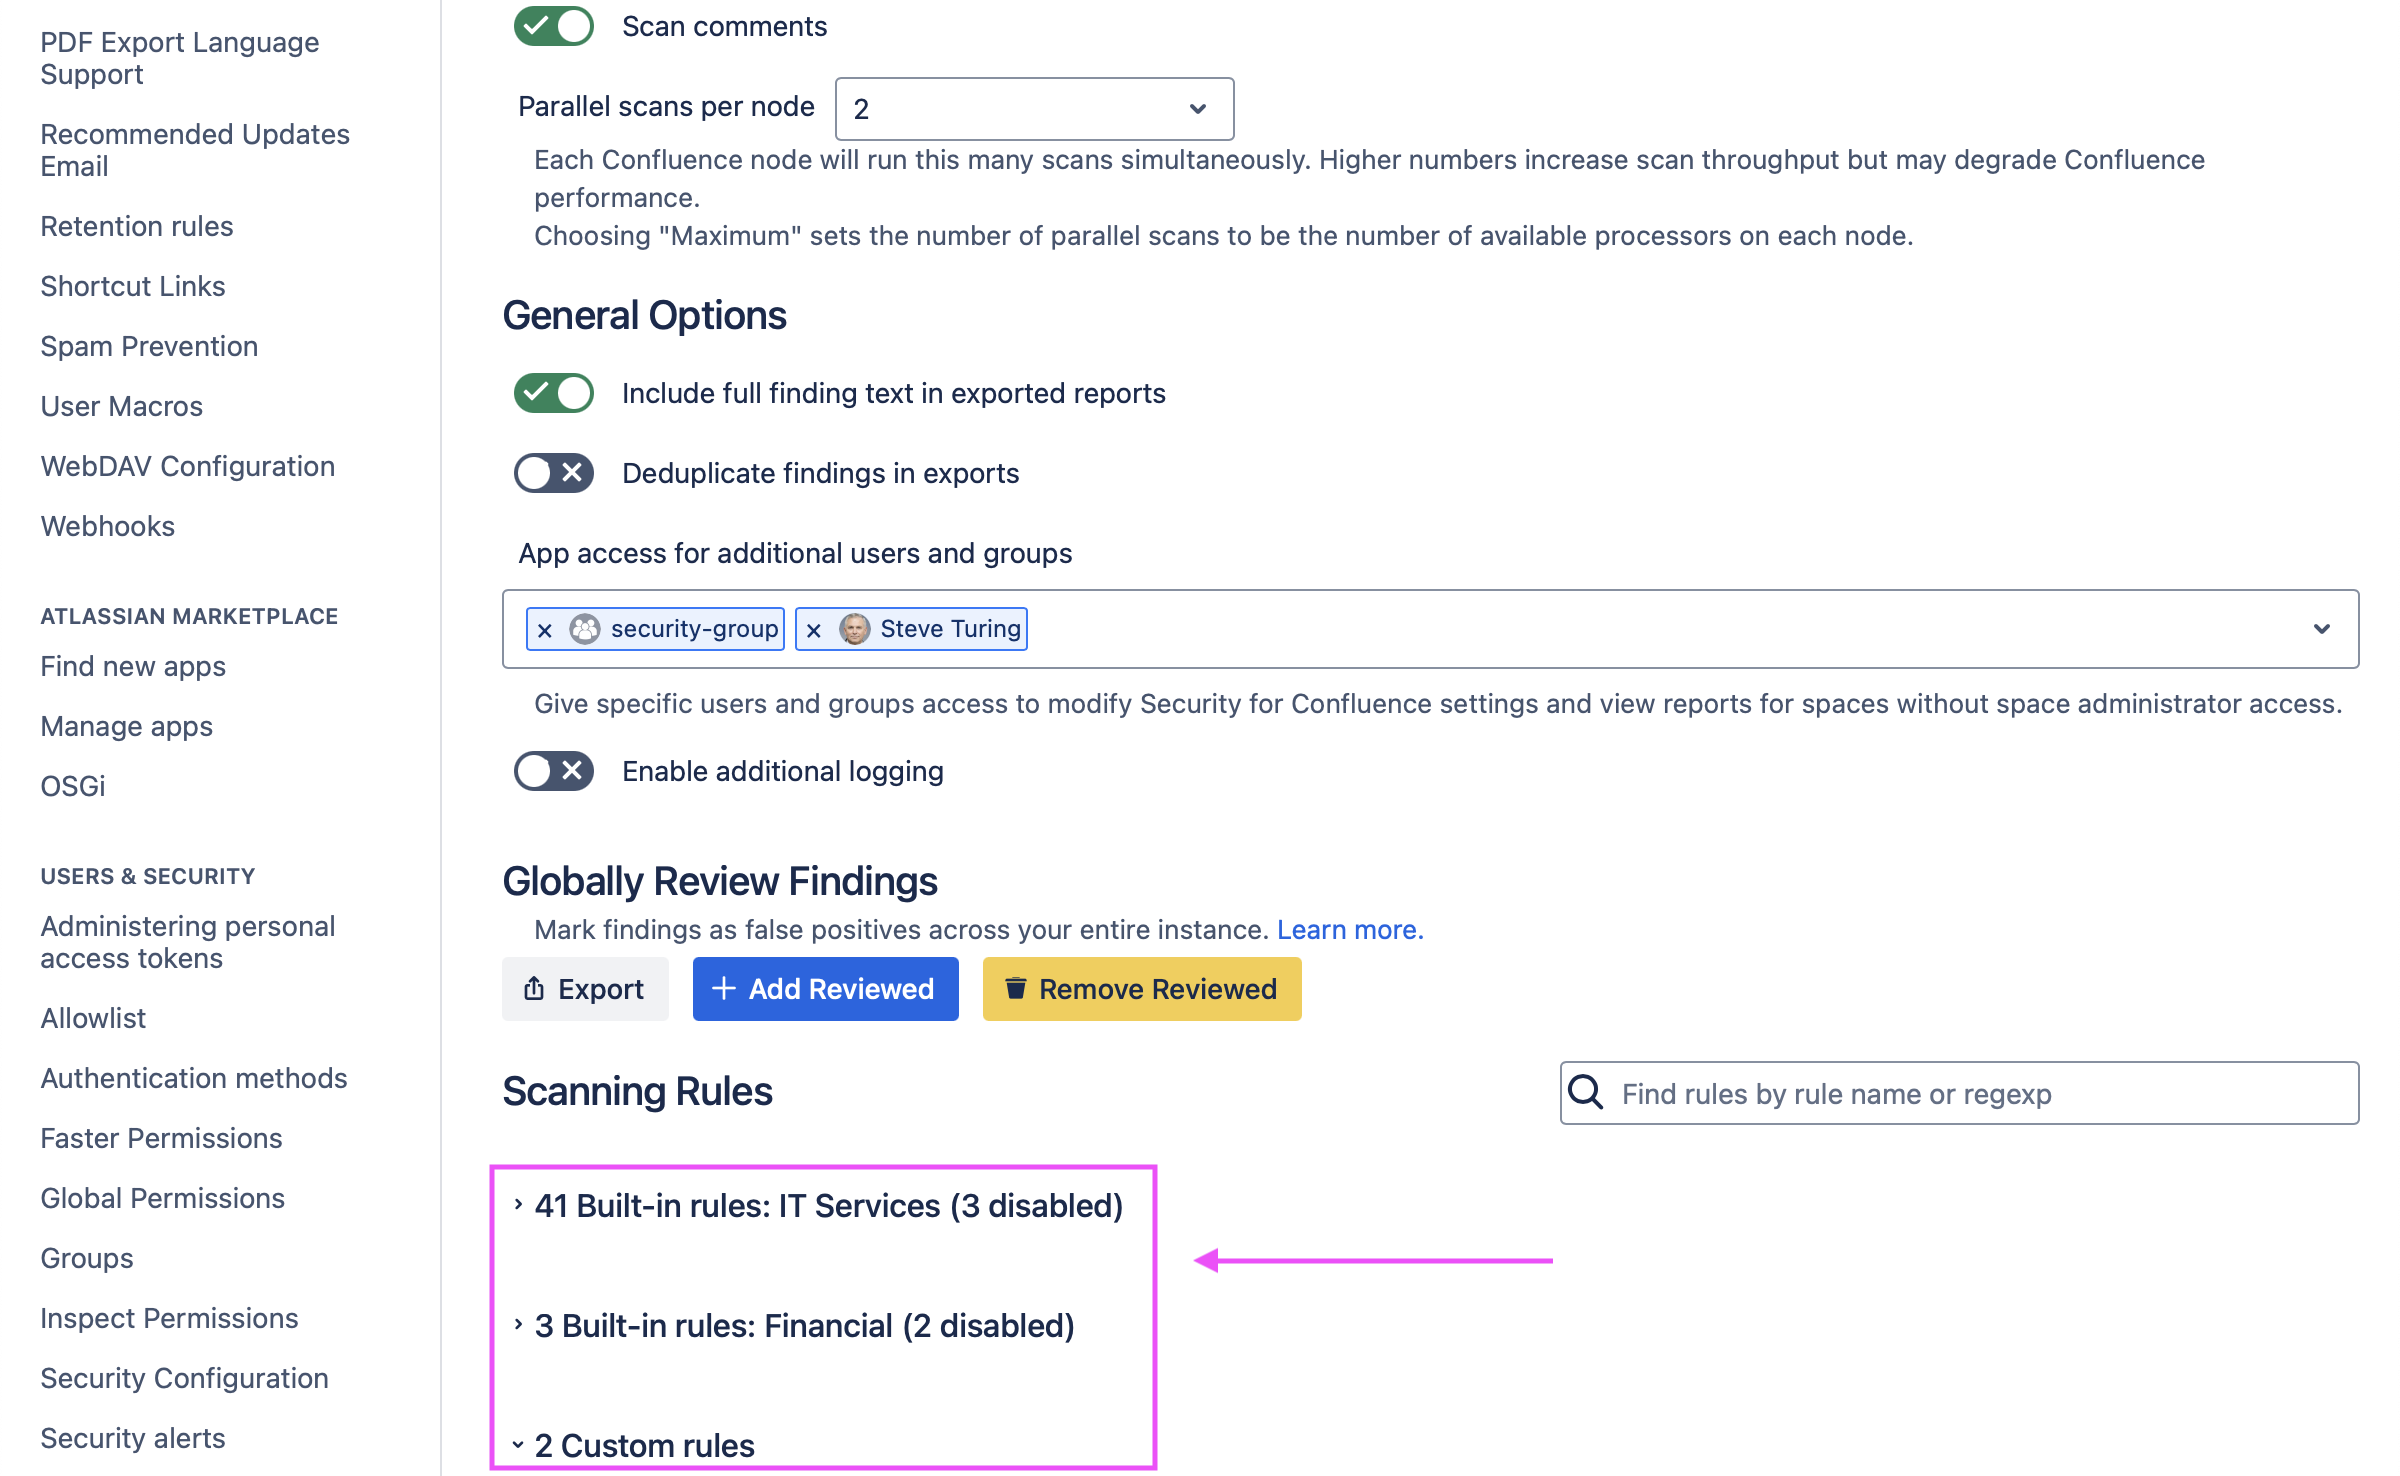
Who changed rules and when can be audited using the Audit Log. More information can be found in [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md).
---
version: "latest"
language: "en"
---
# Enabling debug logging
Should you have issues with Security for Confluence, turning on debug logging can help to troubleshoot and diagnose them.
## Additional Logging Setting
Only Confluence administrators and users granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can access these settings.
In the plugin configuration, you can enable additional logging under the **Scanning Options** heading by toggling the **Enable additional logging** switch.
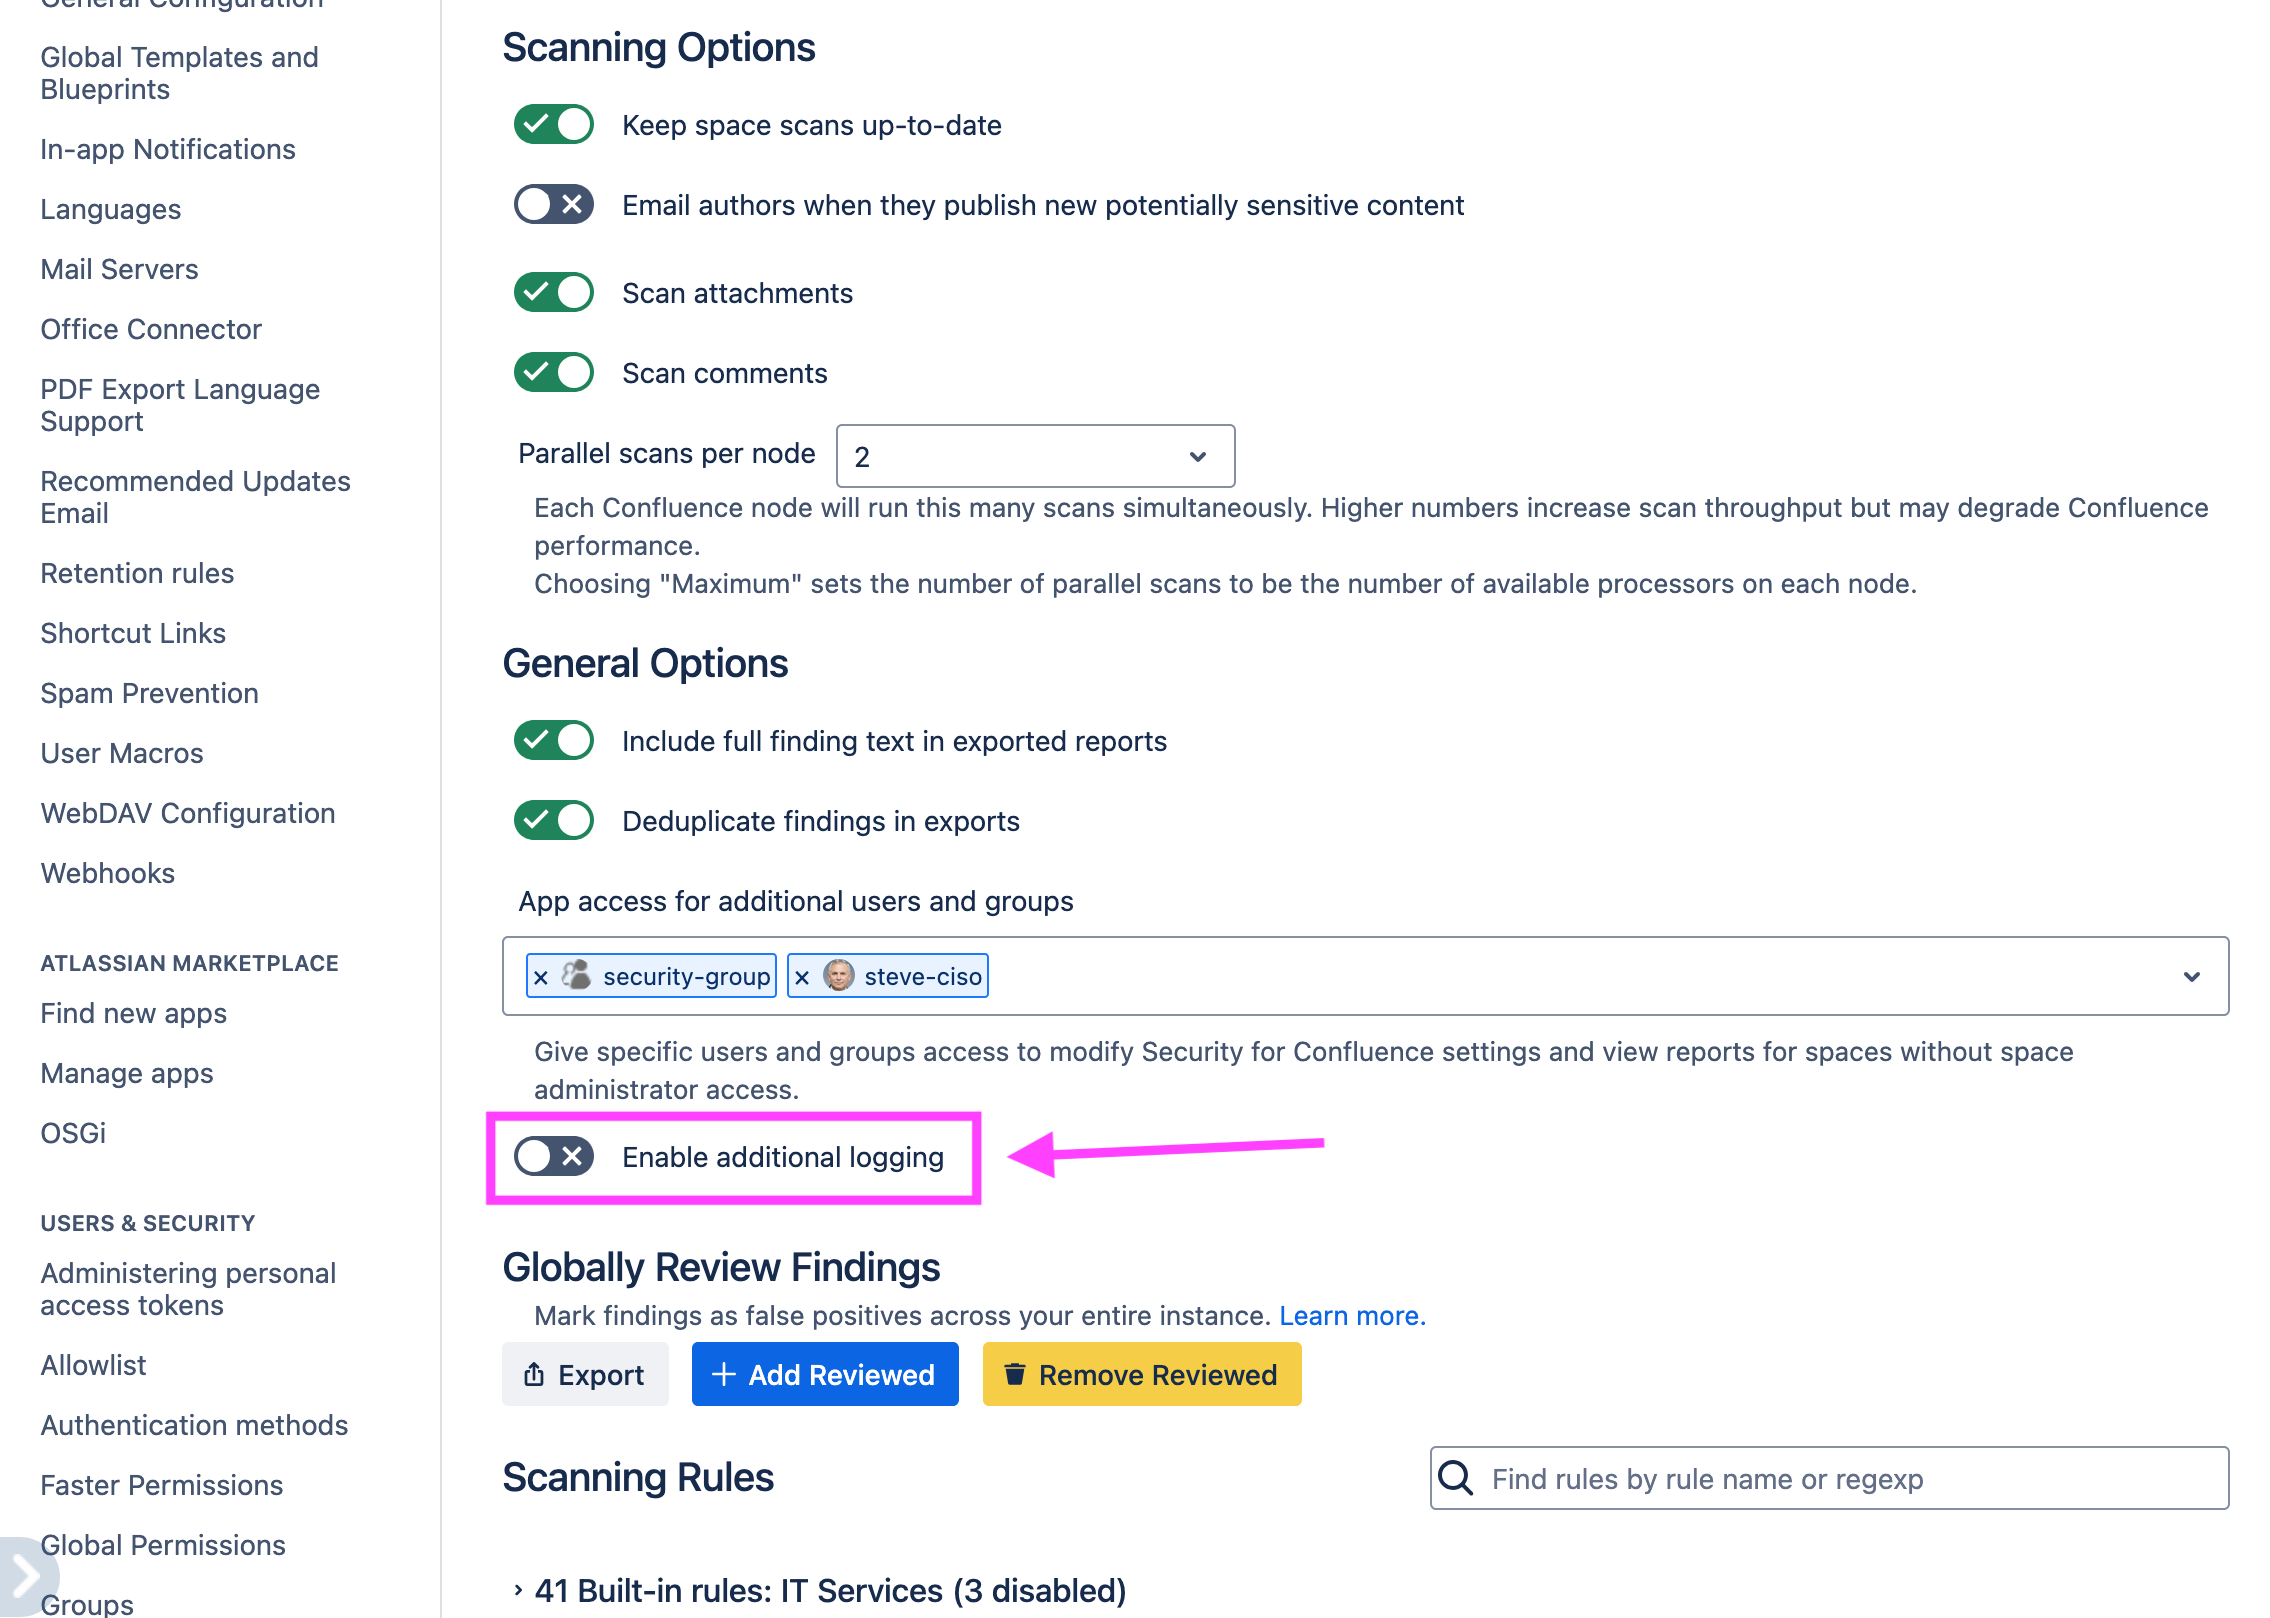
This makes all **Debug** and **Info** level messages log as **Warn** messages on all nodes until the setting is turned off.
Turning on additional logging can generate extremely verbose logs, especially during scanning. It should only be enabled temporarily, at the instruction of our support team.
### Interaction With Confluence Logging Configuration
Confluence allows [more granular configuration of logging](https://confluence.atlassian.com/doc/configuring-logging-181535215.html). **Soteri recommends using the "Enable additional logging" setting to troubleshoot any issue with Security for Confluence.** However, if for any reason you decide to use the Confluence logging configuration, it will not conflict with the **Additional Logging Setting**.
## Enabling logging for database SQL commands
Logging all SQL commands will generate extremely verbose logs. It should only be enabled temporarily, at the instruction of our support team.
1. Go to ⚙️ → **General Configuration** → **Logging and Profiling**.
2. Under **Add New Entry** enter `org.hibernate.SQL` at `DEBUG` level and click **Add entry**
3. Under **Add New Entry** enter `net.java.ao` at `DEBUG` level and click **Add entry**
4. Under **Add New Entry** enter `com.querydsl.sql` at `DEBUG` level and click **Add entry**
Reference:
---
version: "latest"
language: "en"
---
# Exporting Findings
Security for Confluence allows users to export CSV files containing findings in the spaces for which they have administration privileges. This can be done when viewing a space's Security Analysis by clicking the **Export Space** dropdown at the top:
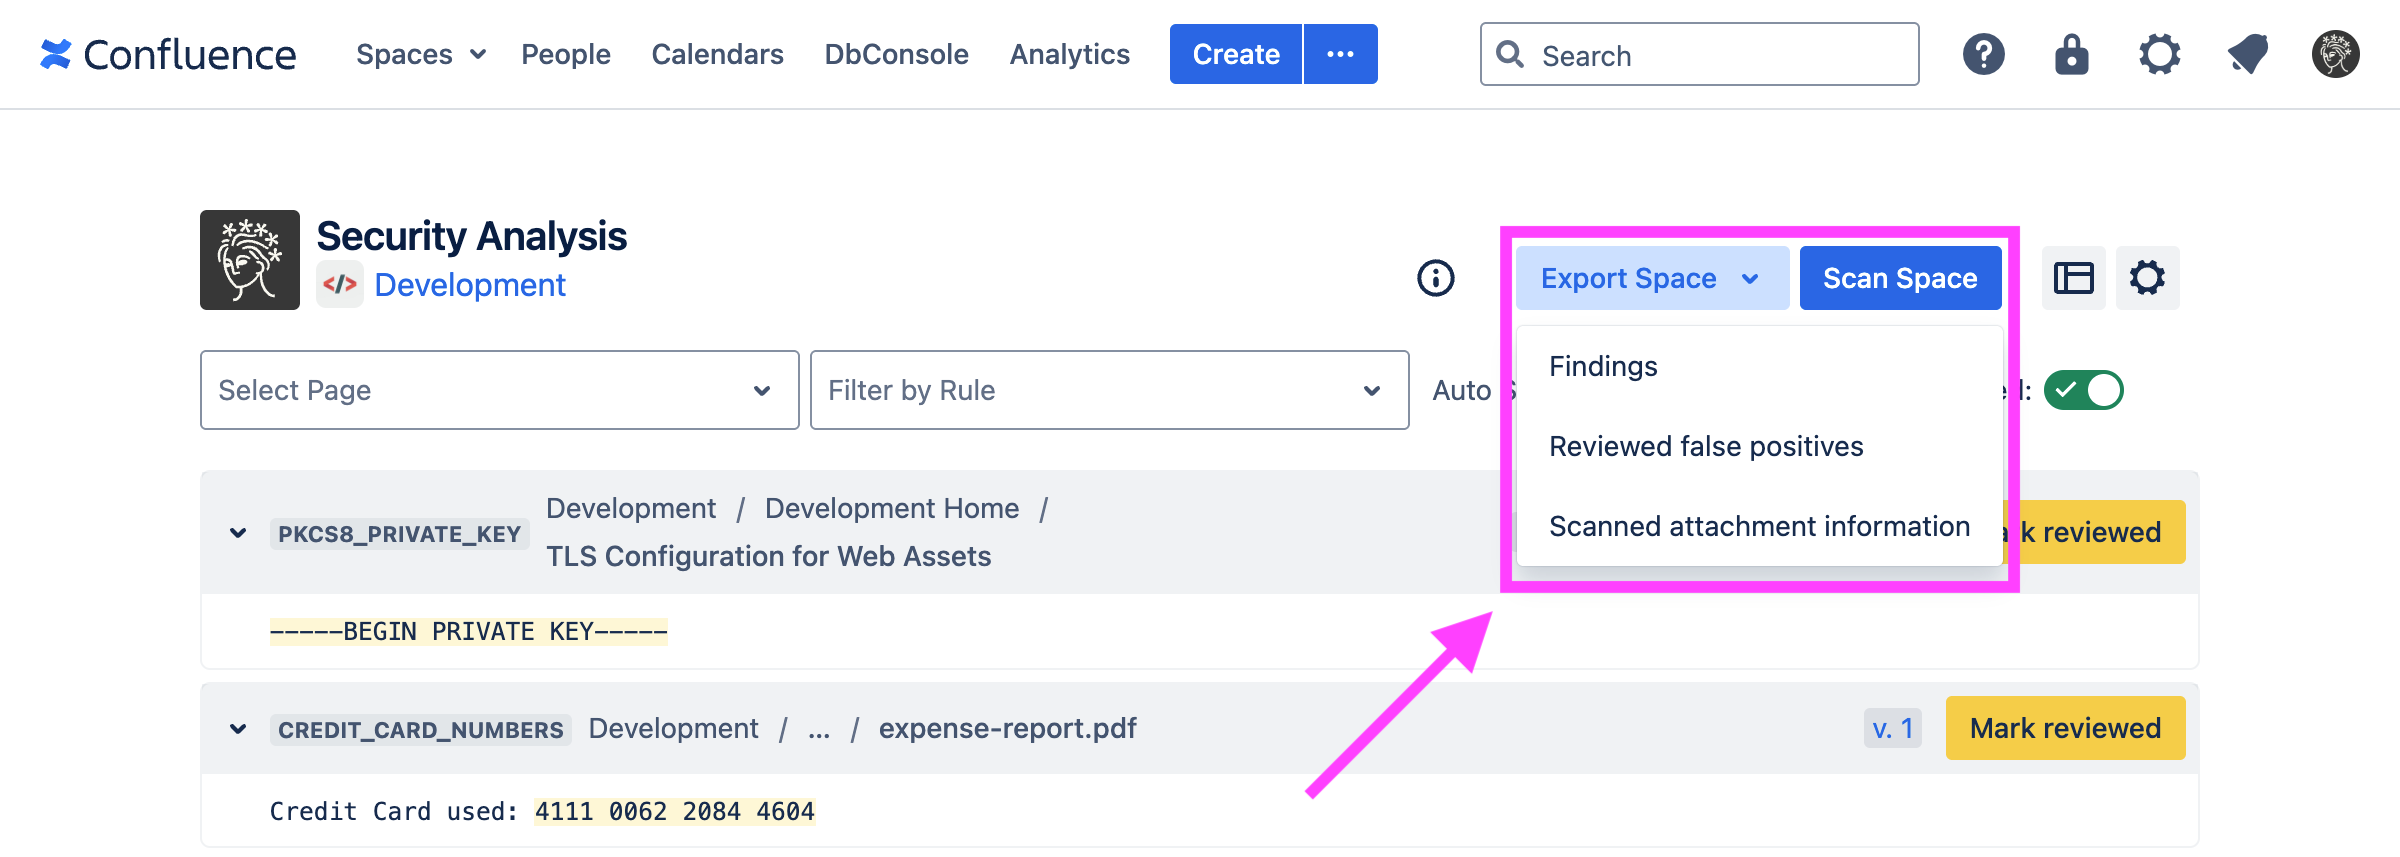
There are three options, all of which are in CSV format:
* A **Findings** export contains the scan results for the space
* A **Reviewed false positives** export contains reviewed false positives, including who reviewed them and when they were reviewed. Reviewed false positives are scoped per-space and apply to all future and past findings in the space that match exactly.
* A **Scanned attachment information** export contains information about scanned files attached to pages or blog posts. See [Scanning Files Attached to Pages](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-files-attached-to-pages.md) for more information.
You can also export findings for a particular space or for all spaces for which you have administration privileges, using the [REST API](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Exporting-Findings).
For performance reasons, each node is limited to one running export at a time. App admins can cancel long running exports from the settings page or via the [REST API](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Cancel-running-exports).
## Redacting findings in exported reports
If you want to keep the full text of findings from appearing in exported reports, you can disable the **Include full finding text in exported reports** setting in the plugin settings page:
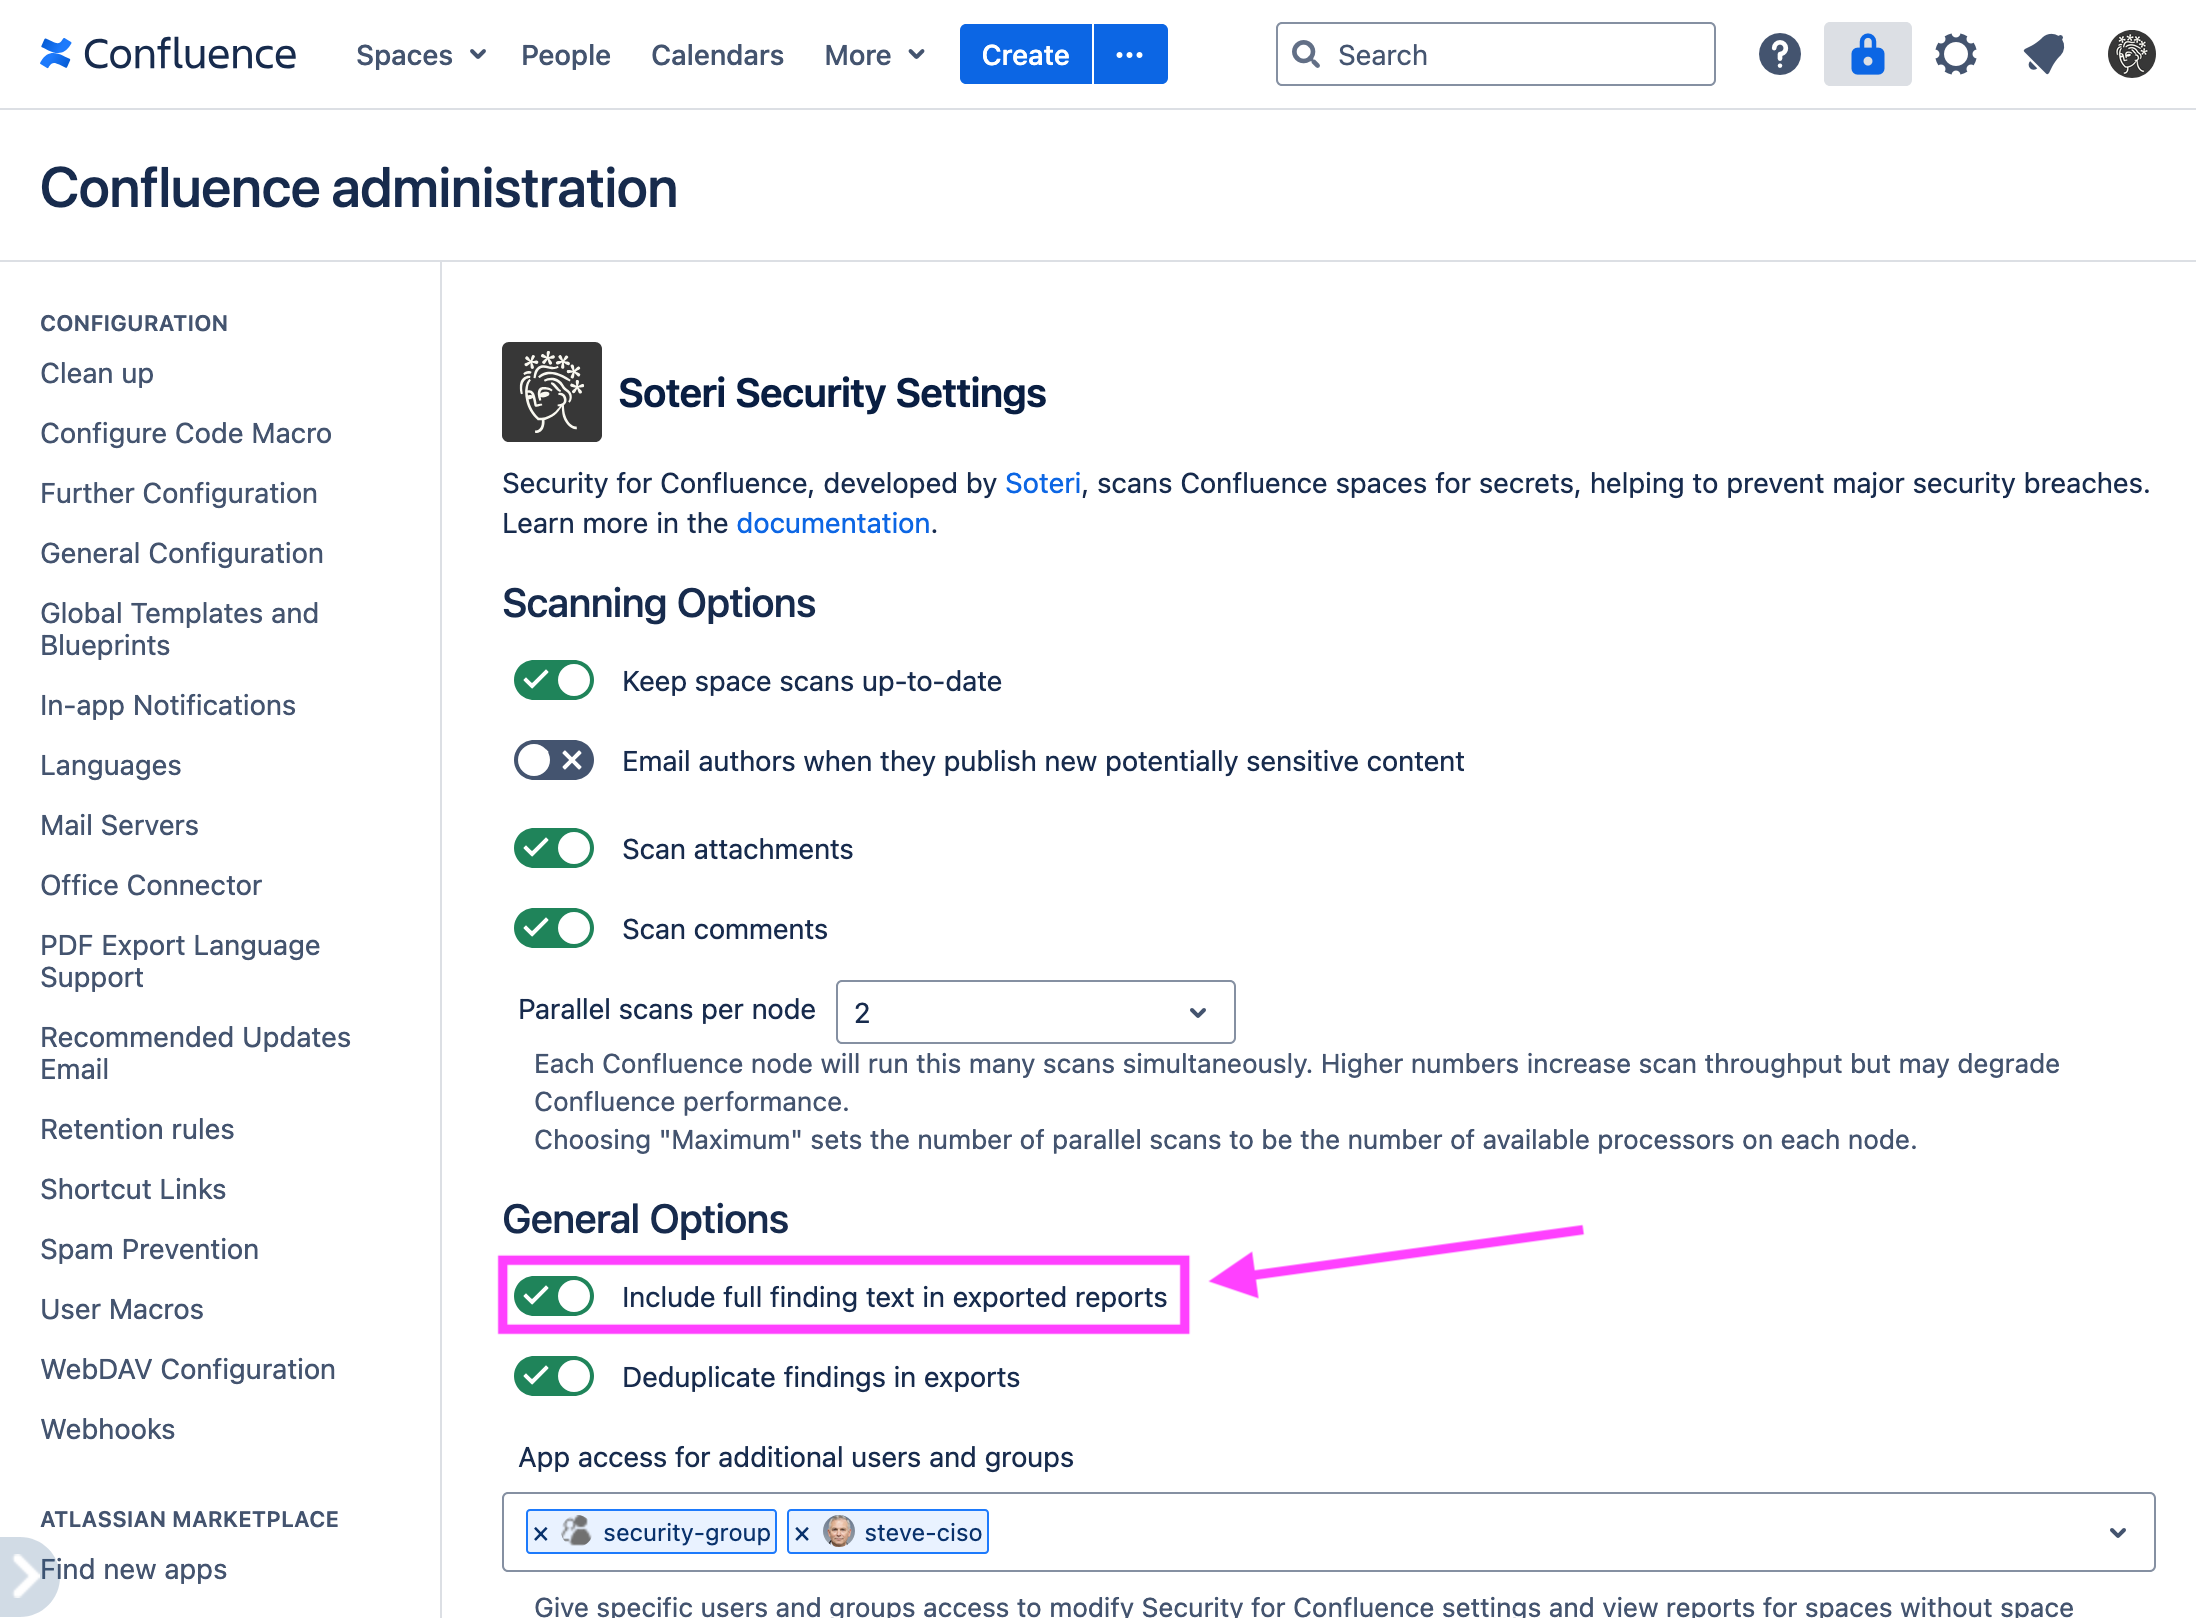
Disabling this option will remove the **Finding text** and **Full text** columns from CSV exports, and will add a URL column, **Report link** -- a link to the Security Analysis containing the finding.
## Deduplicate findings in exports
If you want to show every finding occurrence in your export reports, you can disable the **Deduplicate findings in exports** setting. Otherwise, findings will be presented once for every page they're discovered in, even if the are discovered more than once in the history of that page, blog post, or attachment. This behavior presents an export similar to the layout of the [Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md) page.
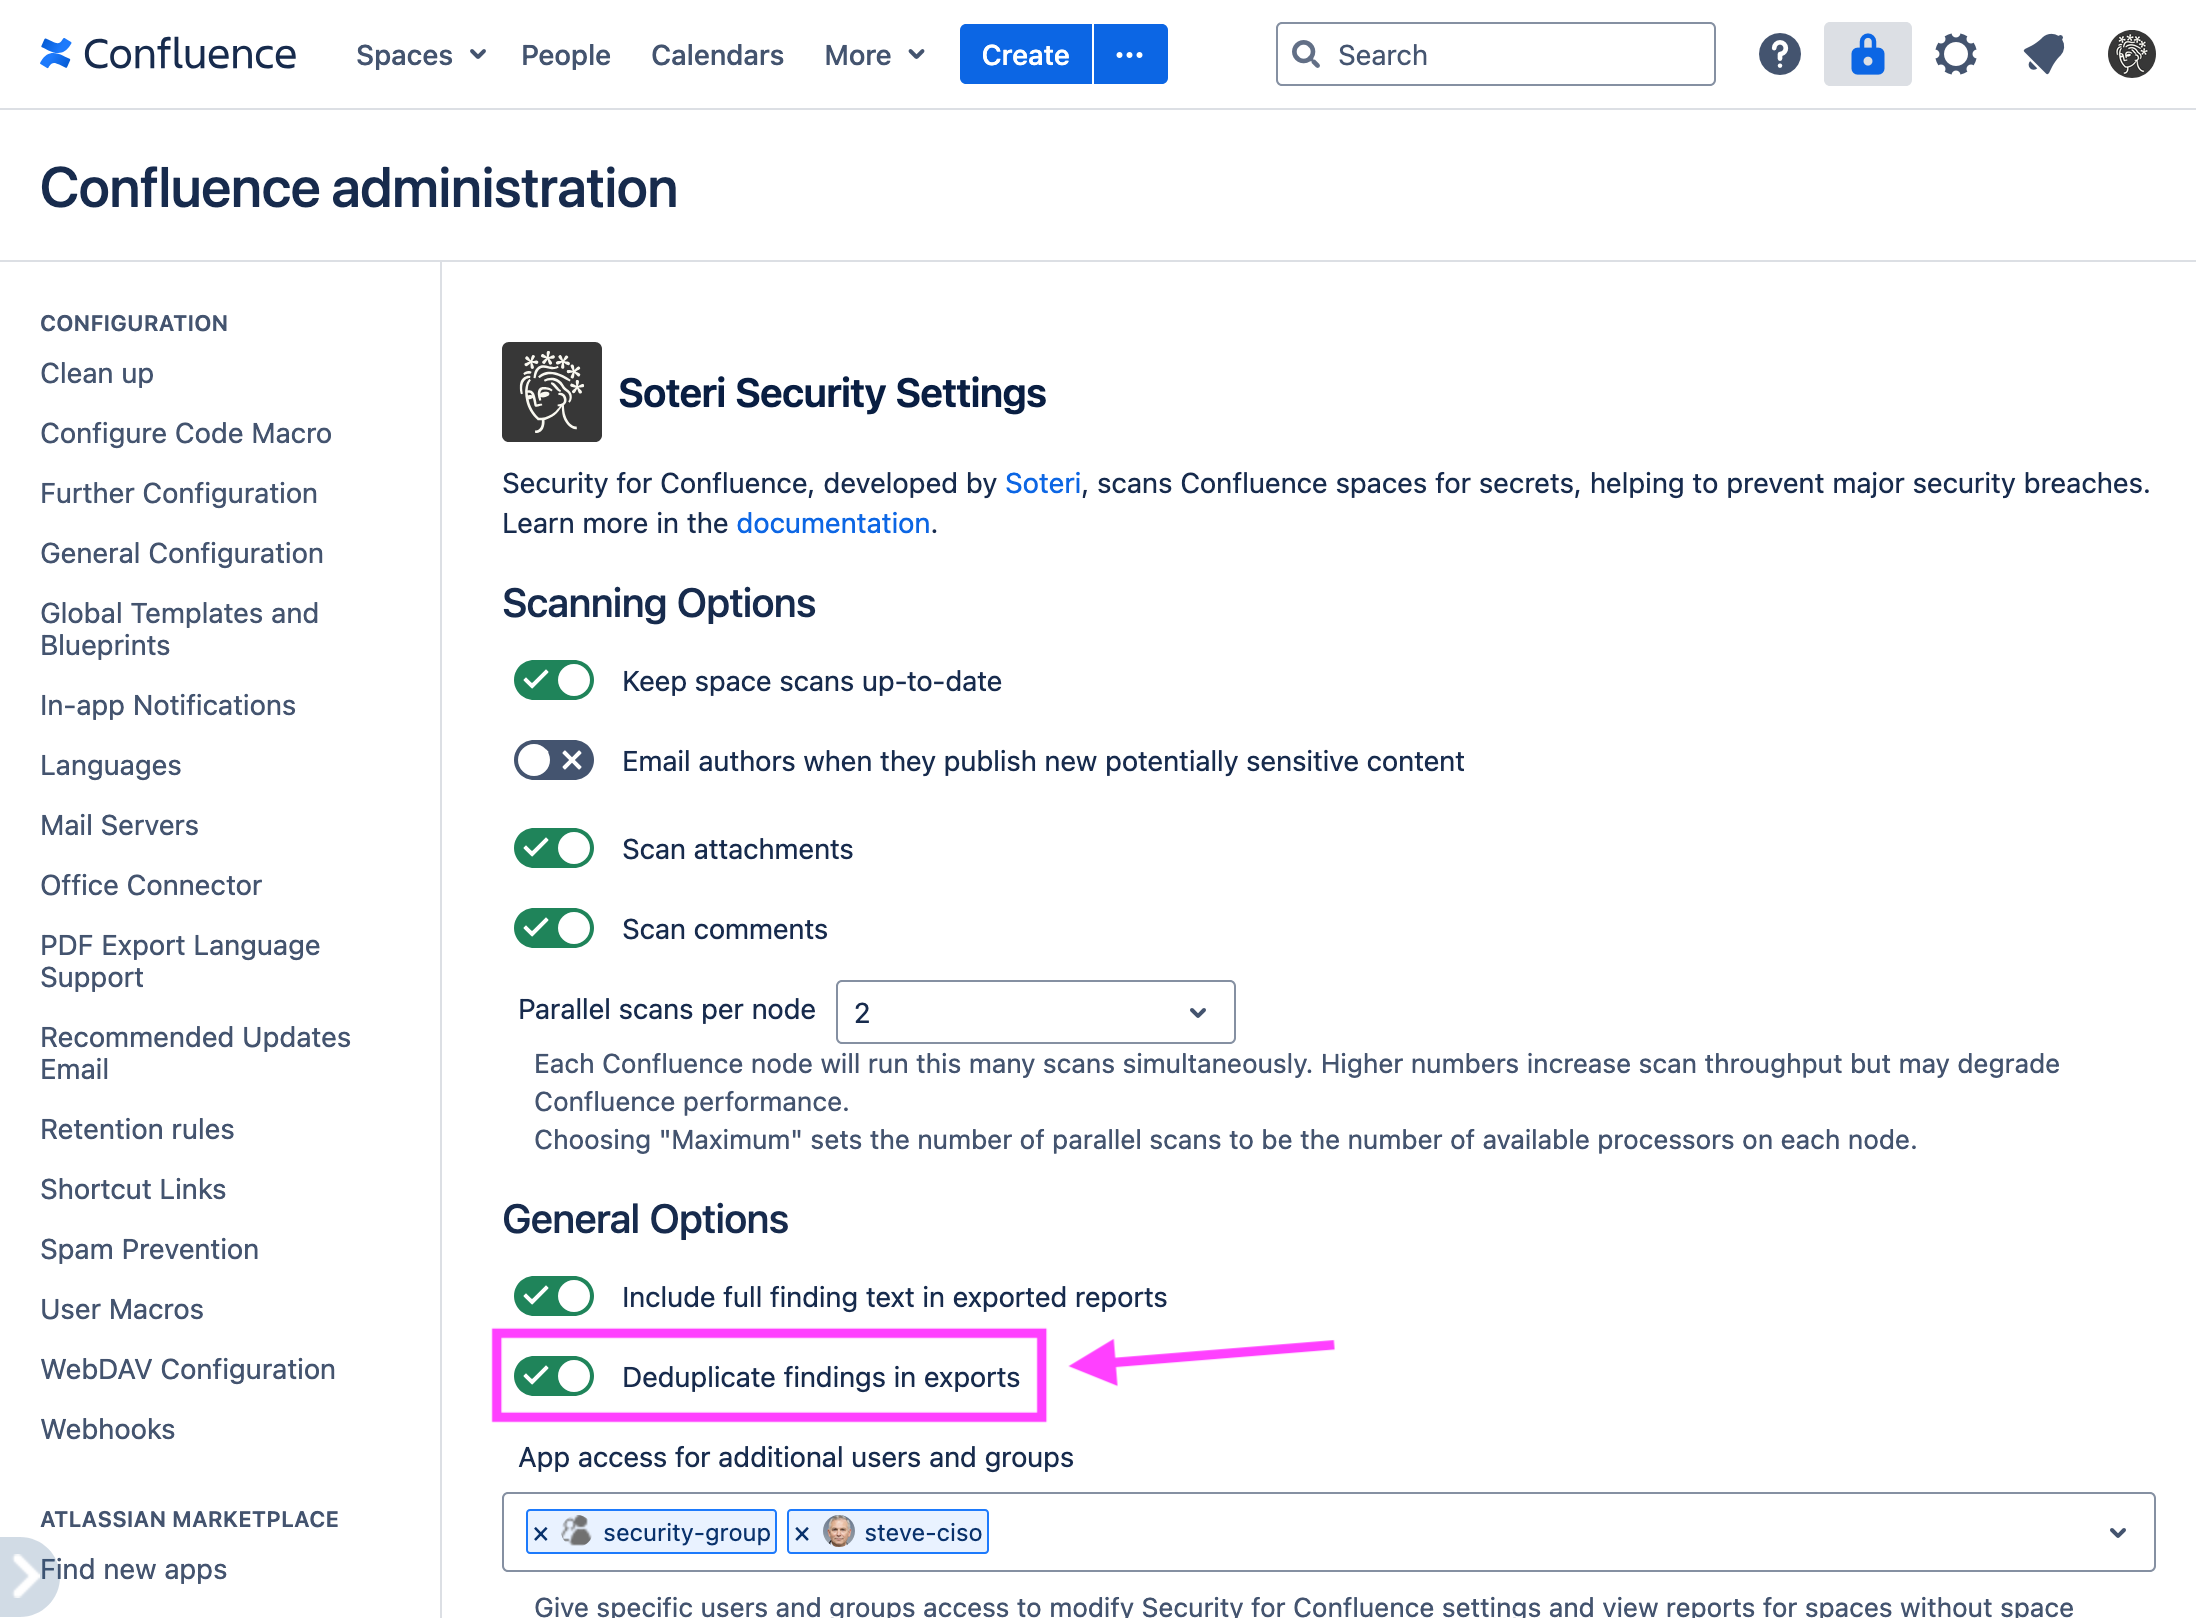
## Columns in exported findings reports
Following are the column names in the exported reports, in order, most of which are self-explanatory:
1. **Space key**
2. **Location type**: PAGE, BLOG_POST, ATTACHMENT, or COMMENT
3. **Content title**
4. **Content ID**
5. **First and latest content versions** (two separate columns), or **Content version** if the "[Deduplicate findings in exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Deduplicatefindingsinexports)" setting is disabled.
6. **Historical** : if this scan finding is [historical](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities#id-(latest)SecurityAnalysis:Viewingscanresultsforaspace-HistoricalFindings).
7. **Rule name**
8. **Match text** : the exact match text of the finding. This can be used to review the finding; see [Hiding false positives, revoked credentials, etc.](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md). Excluded if the "[Include full finding text in exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Redactingfindingsinexportedreports)" setting is disabled.
9. **Reviewed?**
10. **Individually Reviewed?**
11. **Globally Reviewed?**
12. **Publication time**
13. **Author**: included for deduplicated exports only.
14. **Report link** : included if the "[Include full finding text in exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Redactingfindingsinexportedreports)" setting is enabled.
15. **Content link**
16. **Diff link**: included for deduplicated exports only. Confluence doesn't provide a way to view a diff for attachment versions, so this is only populated for findings in pages and blog posts.
17. **Full text** : the complete text of the fragment, **or** , if it is too long, then *only* the specific text that triggered the finding. Excluded if the "[Include full finding text in exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Redactingfindingsinexportedreports)" setting is disabled.
---
version: "latest"
language: "en"
---
# Frequently Asked Questions (FAQ) and Troubleshooting
* [What content can Security for Confluence Scan?](https://docs.soteri.io/security-for-confluence-dc/latest/what-content-can-security-for-confluence-scan.md)
* [What do I do if a security scan finds a secret?](https://docs.soteri.io/security-for-confluence-dc/latest/what-do-i-do-if-a-security-scan-finds-a-secret.md)
* [How do I make sure all spaces are scanned, remain scanned, and remain secret-free?](https://docs.soteri.io/security-for-confluence-dc/latest/how-do-i-make-sure-all-spaces-are-scanned-remain-s.md)
* [Accessing the Settings Page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md)
* [What is the GENERIC_PASSWORD rule and why is it disabled by default?](https://docs.soteri.io/security-for-confluence-dc/latest/what-is-the-generic_password-rule-and-why-is-it-di.md)
* [Scan Performance](https://docs.soteri.io/security-for-confluence-dc/latest/scan-performance.md)
* [Why isn't Security for Confluence finding my passwords?](https://docs.soteri.io/security-for-confluence-dc/latest/why-isn-t-security-for-confluence-finding-my-passw.md)
* [Why are some scanning rules disabled by default?](https://docs.soteri.io/security-for-confluence-dc/latest/why-are-some-scanning-rules-disabled-by-default.md)
* [Enabling debug logging](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-debug-logging.md)
* [Creating support zips](https://docs.soteri.io/security-for-confluence-dc/latest/creating-support-zips.md)
* [Why are newline matchers not allowed in custom rules?](https://docs.soteri.io/security-for-confluence-dc/latest/why-are-newline-matchers-not-allowed-in-custom-rul.md)
---
version: "latest"
language: "en"
---
# Granting Access to Additional Users and Groups
By default, Security for Confluence Data Center enforces the following permissions:
1. Confluence Administrators can view finding reports, mark findings reviewed, and change settings in the Security for Confluence settings page.
2. Space Administrators can view finding reports and mark findings reviewed for the spaces they administer.
3. Content Authors can view scan results for their content from notification emails, when the "Keep space scans up-to-date" and "Email authors when they publish new potentially sensitive content" settings are enabled.
You may grant additional users and groups the ability to become App Administrators, which will allow them to view finding reports, mark findings reviewed, and change settings in the Security for Confluence setting page.
Even if a user or group is granted access to the global Soteri Dashboard, they will only see spaces and content for which they have **Read** permissions.
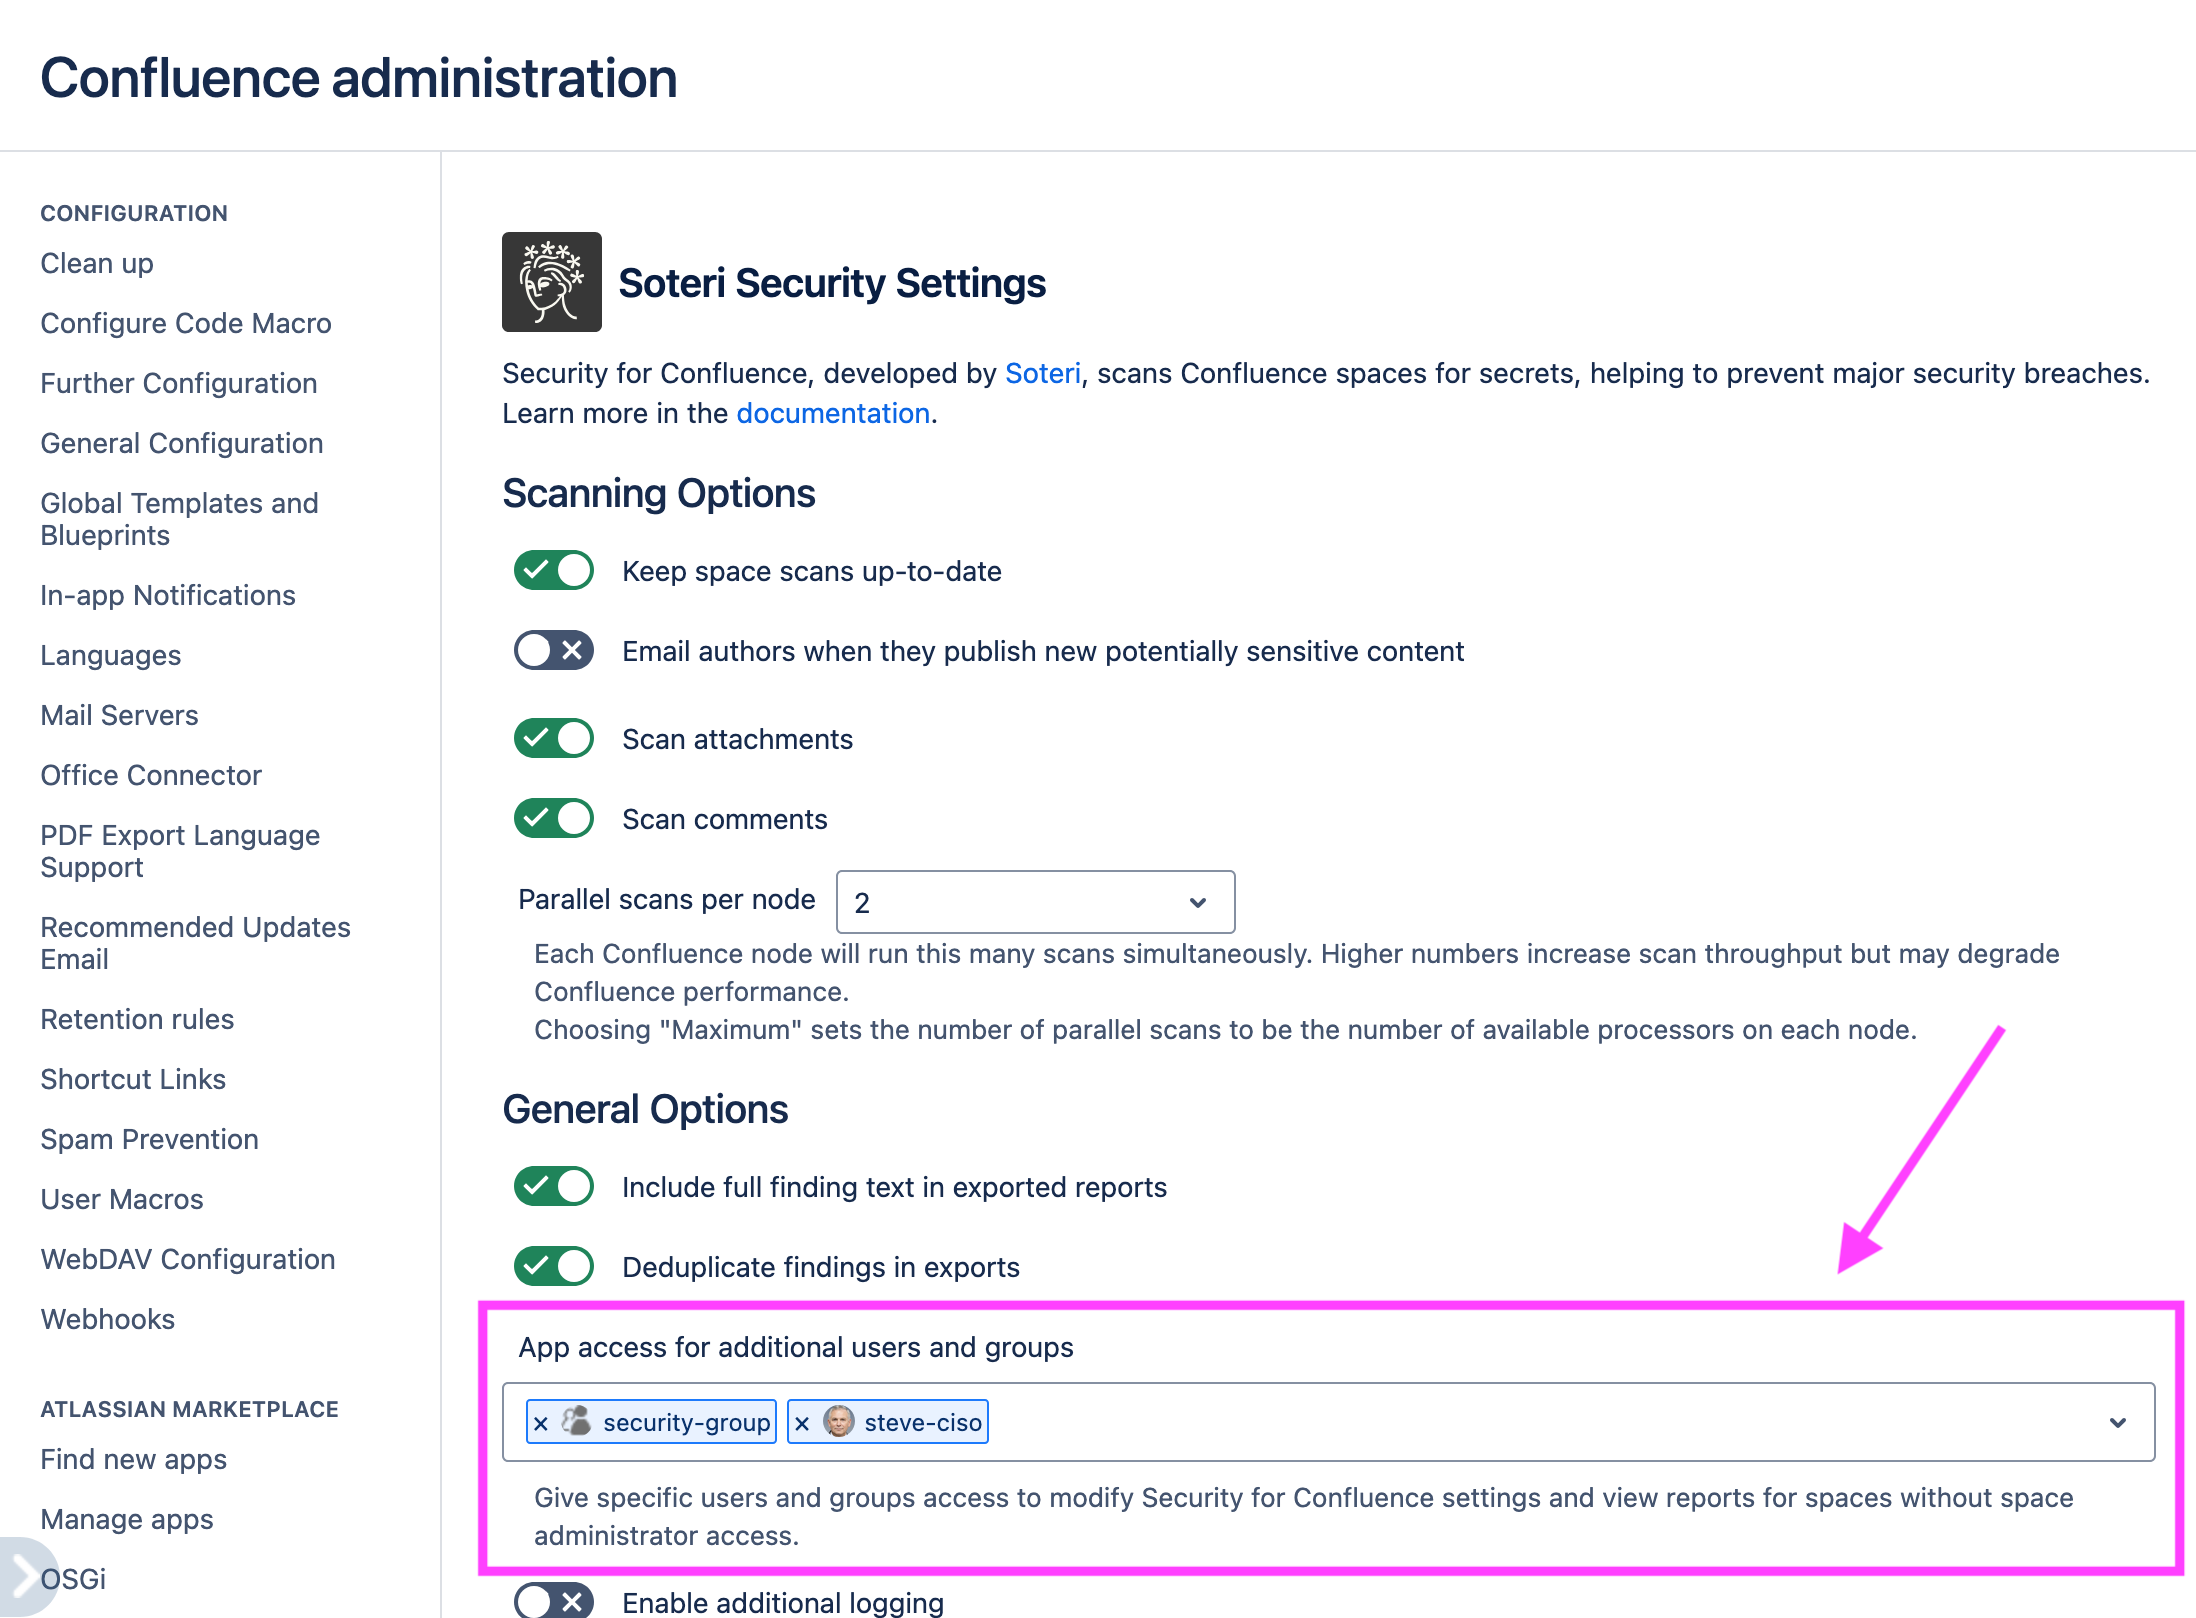
1. As a Confluence Administrator or an App Administrator, access the Security for Confluence Settings page.
2. In the field under "App access for additional users and groups", search for users and groups to become App Administrators. You can also remove App Administrators by clicking the `x` icon next to their name.
Any changes made to the App Administrator list will be visible in the Audit Log. For more information, see: [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md)
---
version: "latest"
language: "en"
---
# Hiding false positives, revoked credentials, etc.
Sometimes, Security for Confluence will find false positives, credentials which have already been revoked, etc. If this happens, you can mark the finding as reviewed. This prevents the finding, as well as any other findings which exactly match it, as reviews the current and future scans.
Security for Confluence has two ways to do this:
* Confluence users with contributor permissions can review findings from their alerts, and space administrators, Confluence administrators, and users with read permissions who have been granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can review findings from the [Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md) page. Findings reviewed this way are scoped to the space the finding is in.
* Confluence administrators and anyone [granted explicit access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can review findings globally, on the [Soteri Security Settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md).
On the Soteri Dashboard, reviewed false positives are not counted towards the total finding count per space.
## Reviewing in the scope of a Space
Users with space contributor permissions can review findings for a particular space.
### Reviewing a finding from the Security Analysis
Click the **Mark reviewed** button on the finding you want to review. This opens a confirmation window.
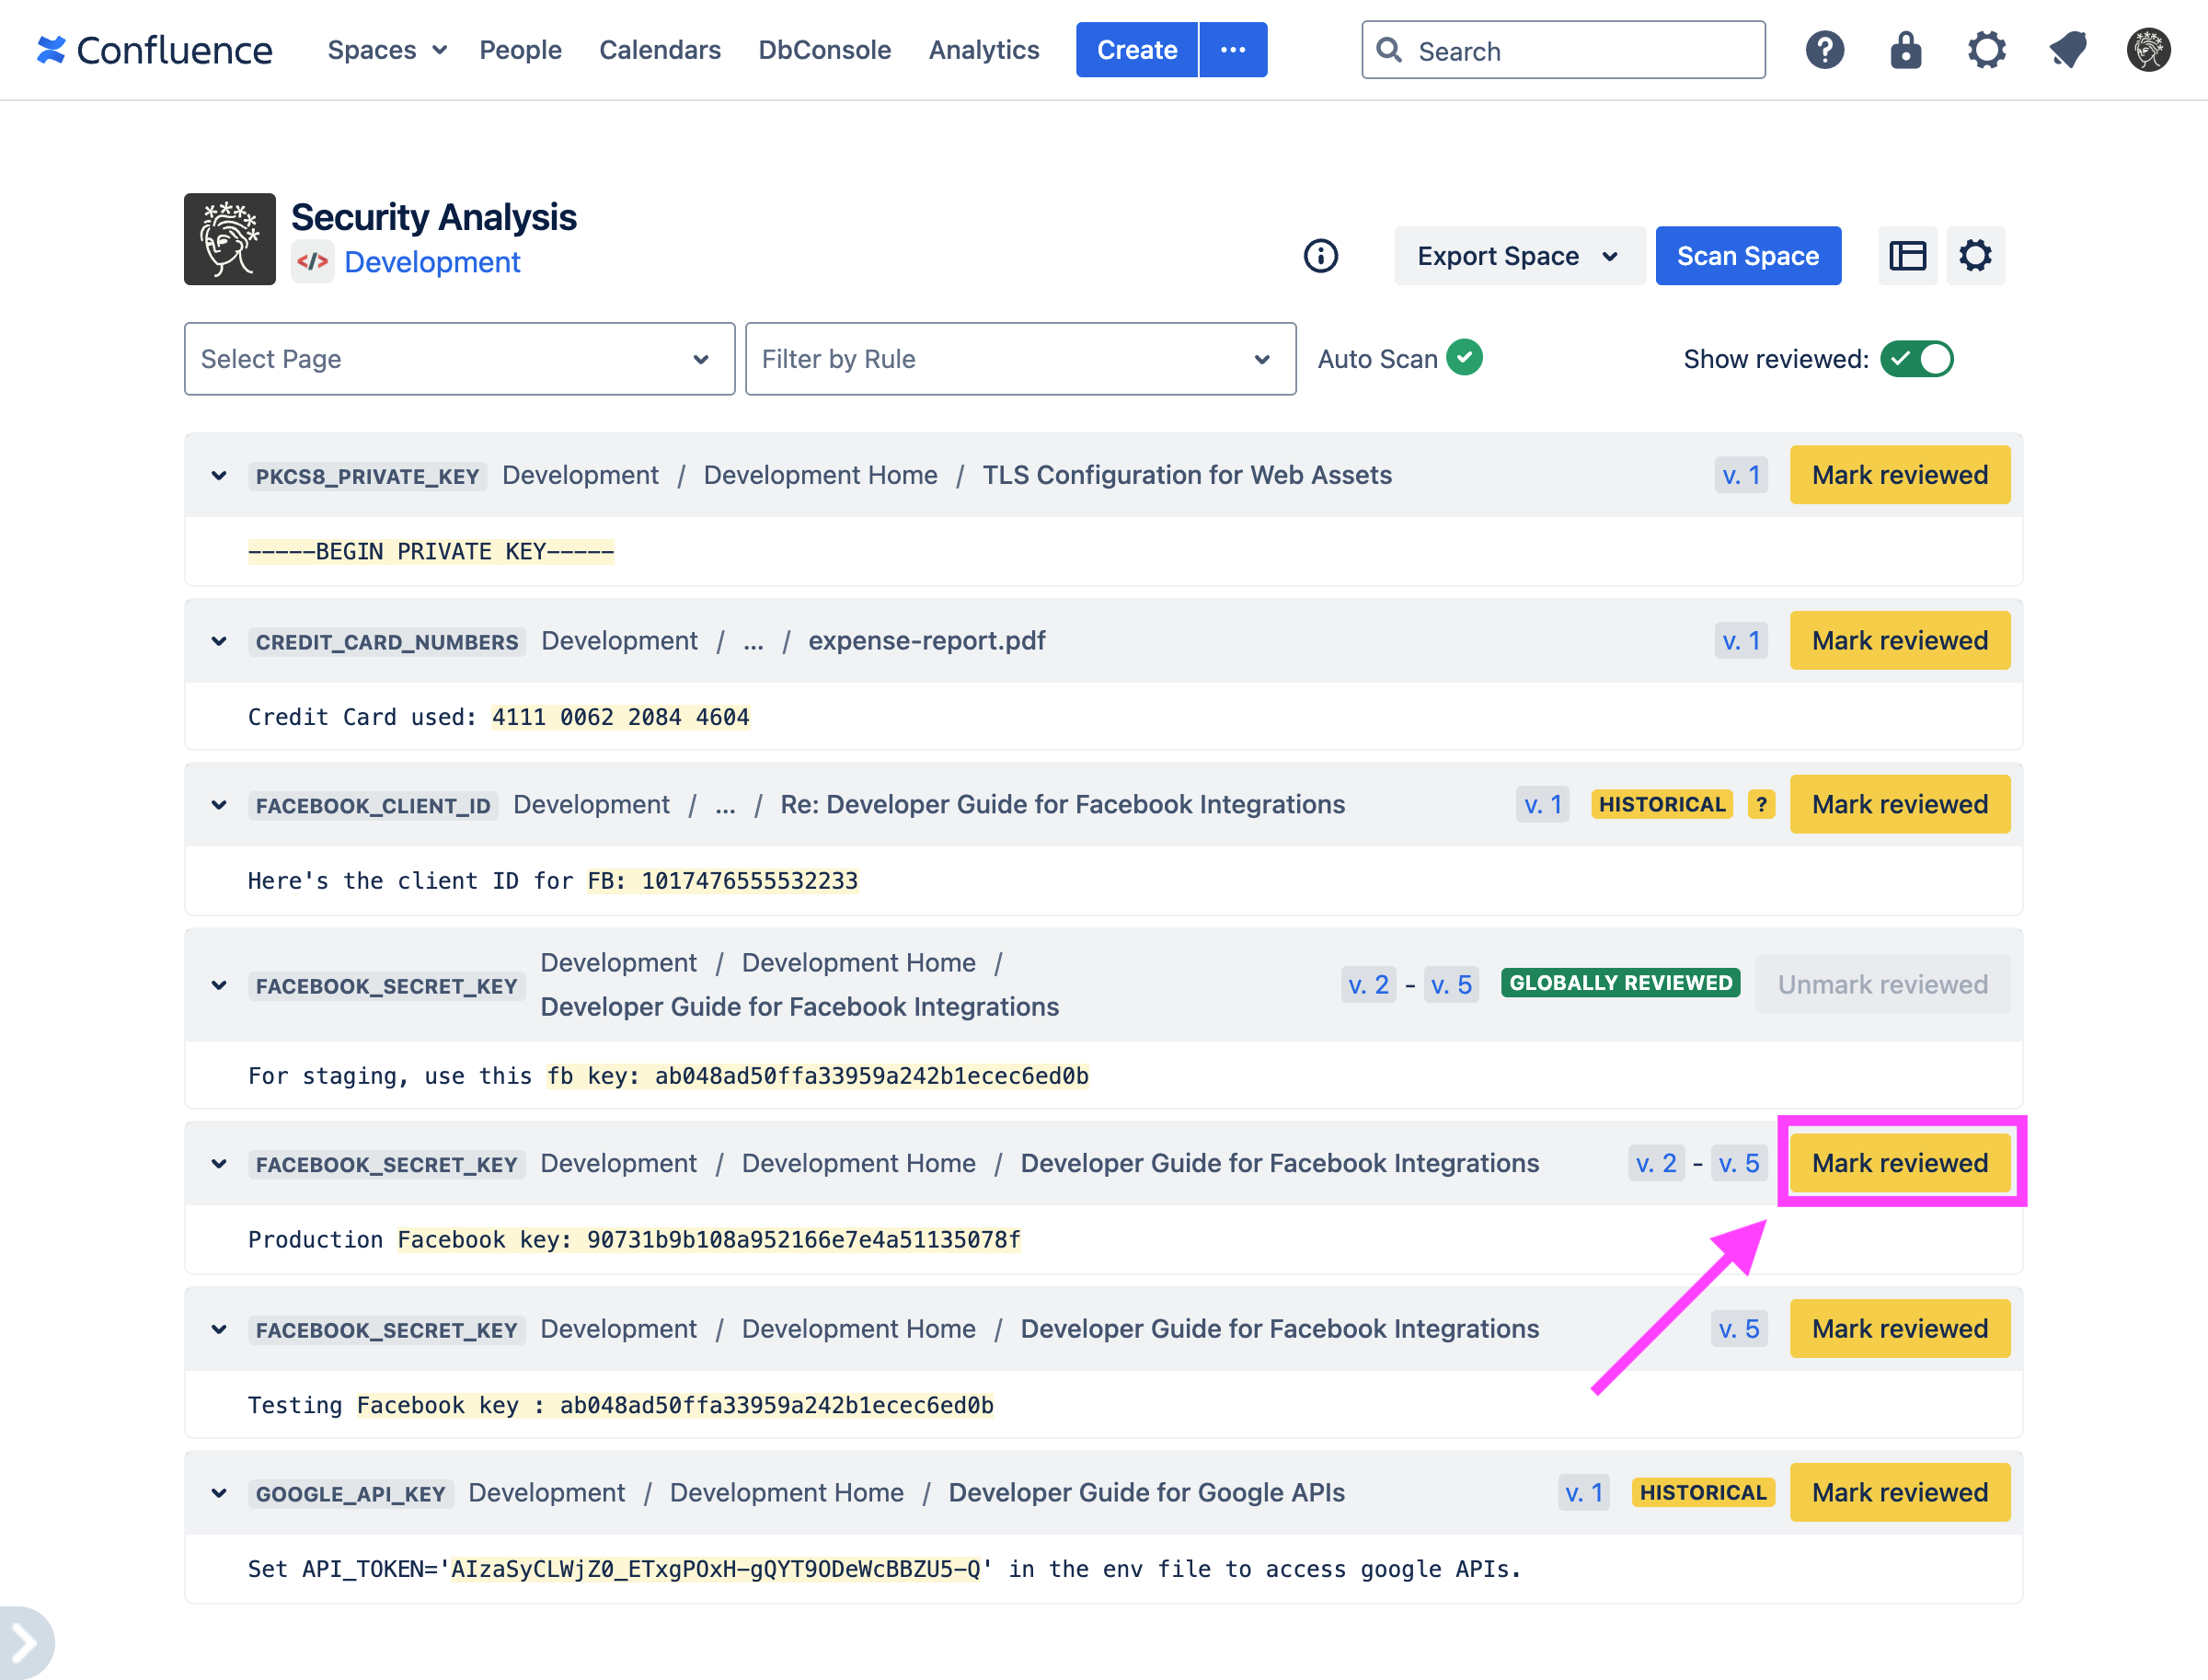
Marking a finding as reviewed saves the **exact string** captured by the rule (in this case,
`fb key: ab048ad50ffa33959a242b1ecec6ed0b`). That exact string will be marked as reviewed for all existing and future scans, even if the original finding is deleted.
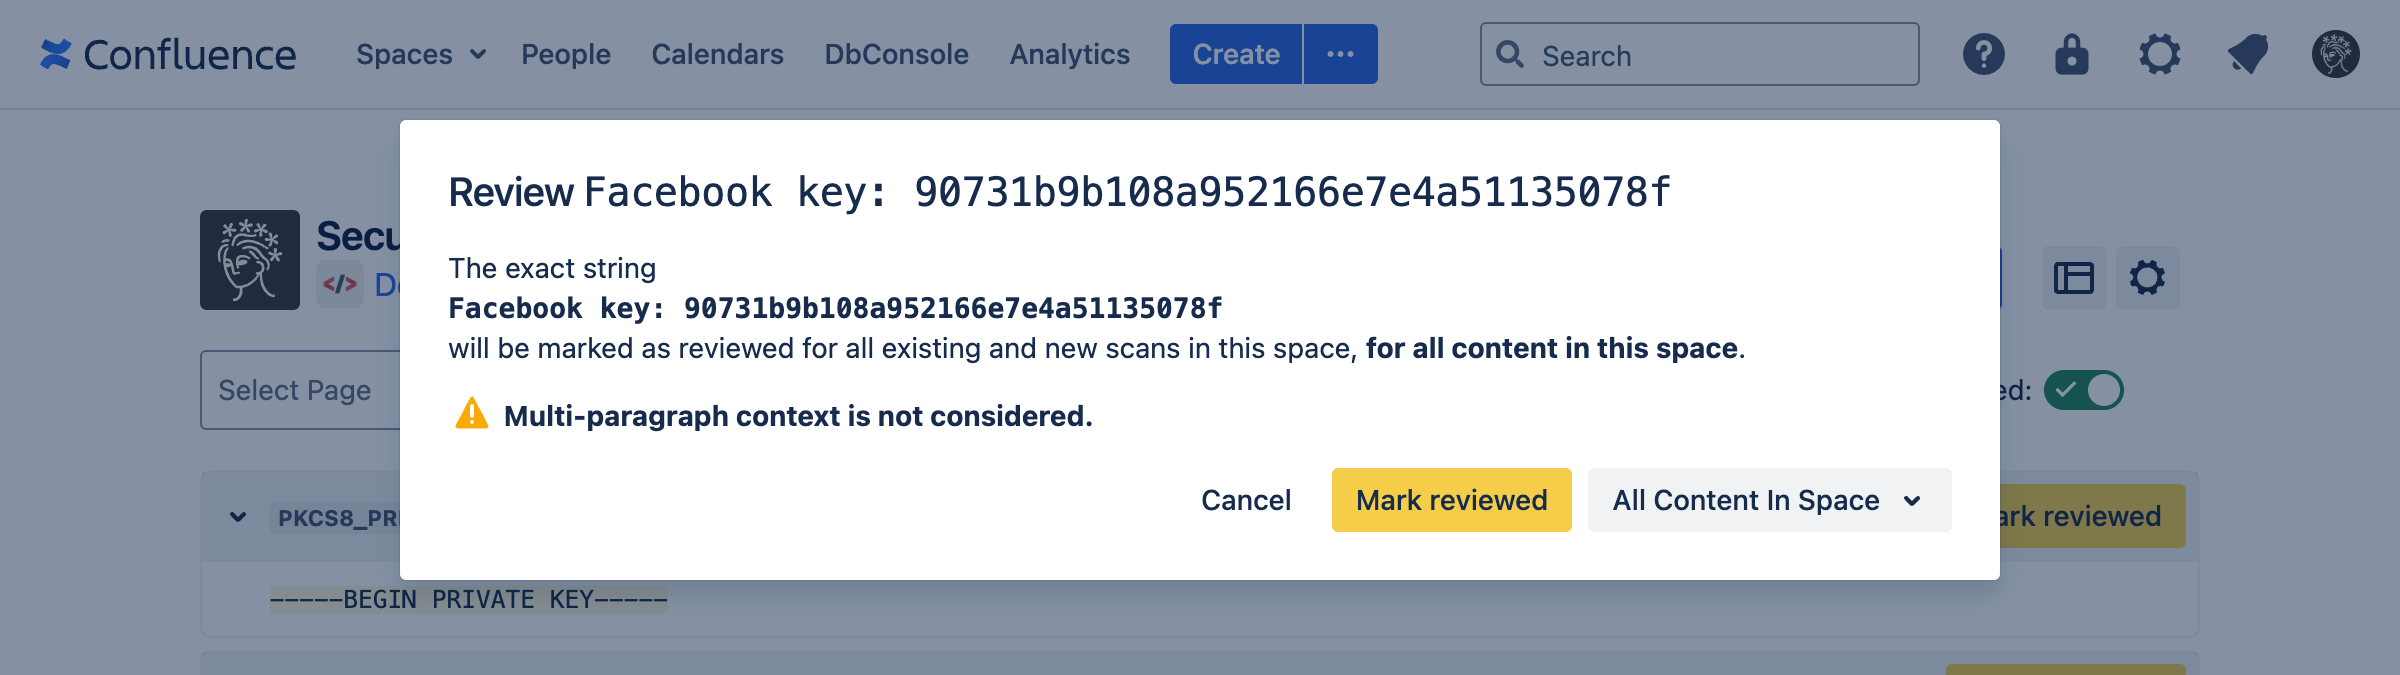
After the finding is marked as reviewed, all other findings of that exact string will disappear from the Security Analysis.
You can also mark a finding as reviewed just for the page, comment, or attachment it appears in.
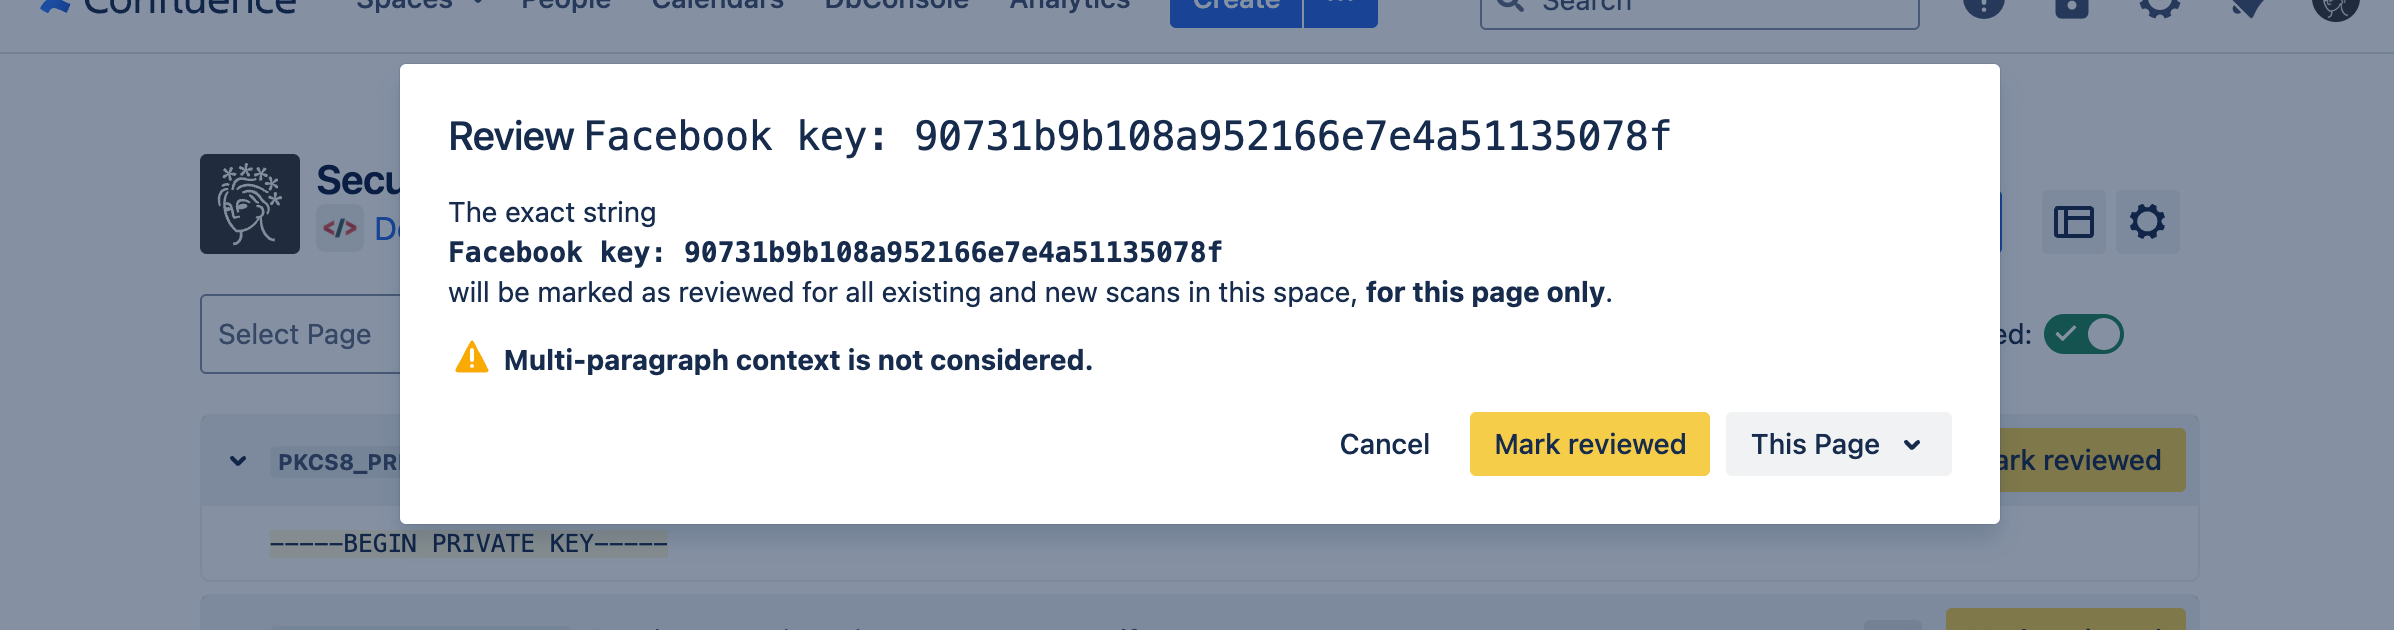
After the finding is marked as reviewed, all other findings of that exact string will be considered reviewed for the same page, comment, or attachment, and will disappear from the Security Analysis.
### Reviewing findings in the scope of a page, comment, or attachment only
Some findings cannot be reviewed for the entire space - for example, they may not capture the exact secret - and as a result can only be reviewed individually.
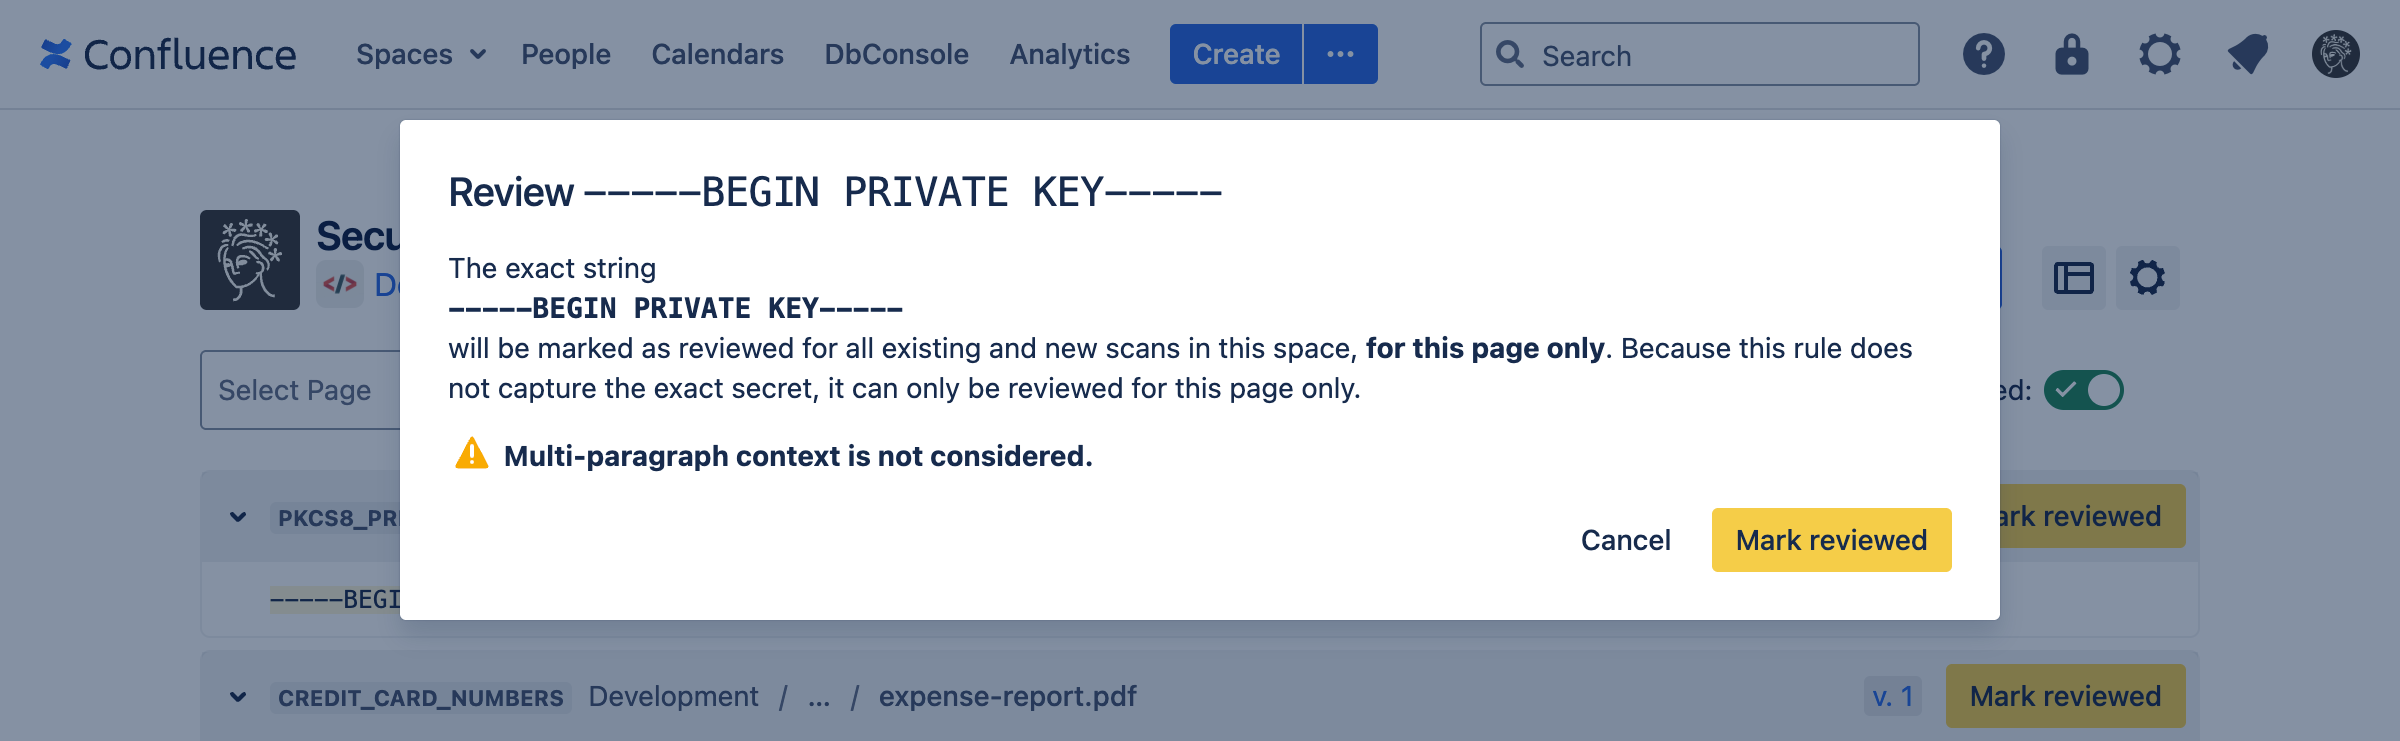
Reviewed findings can be shown again with the **Show reviewed** toggle, where they can also be unmarked or changed.
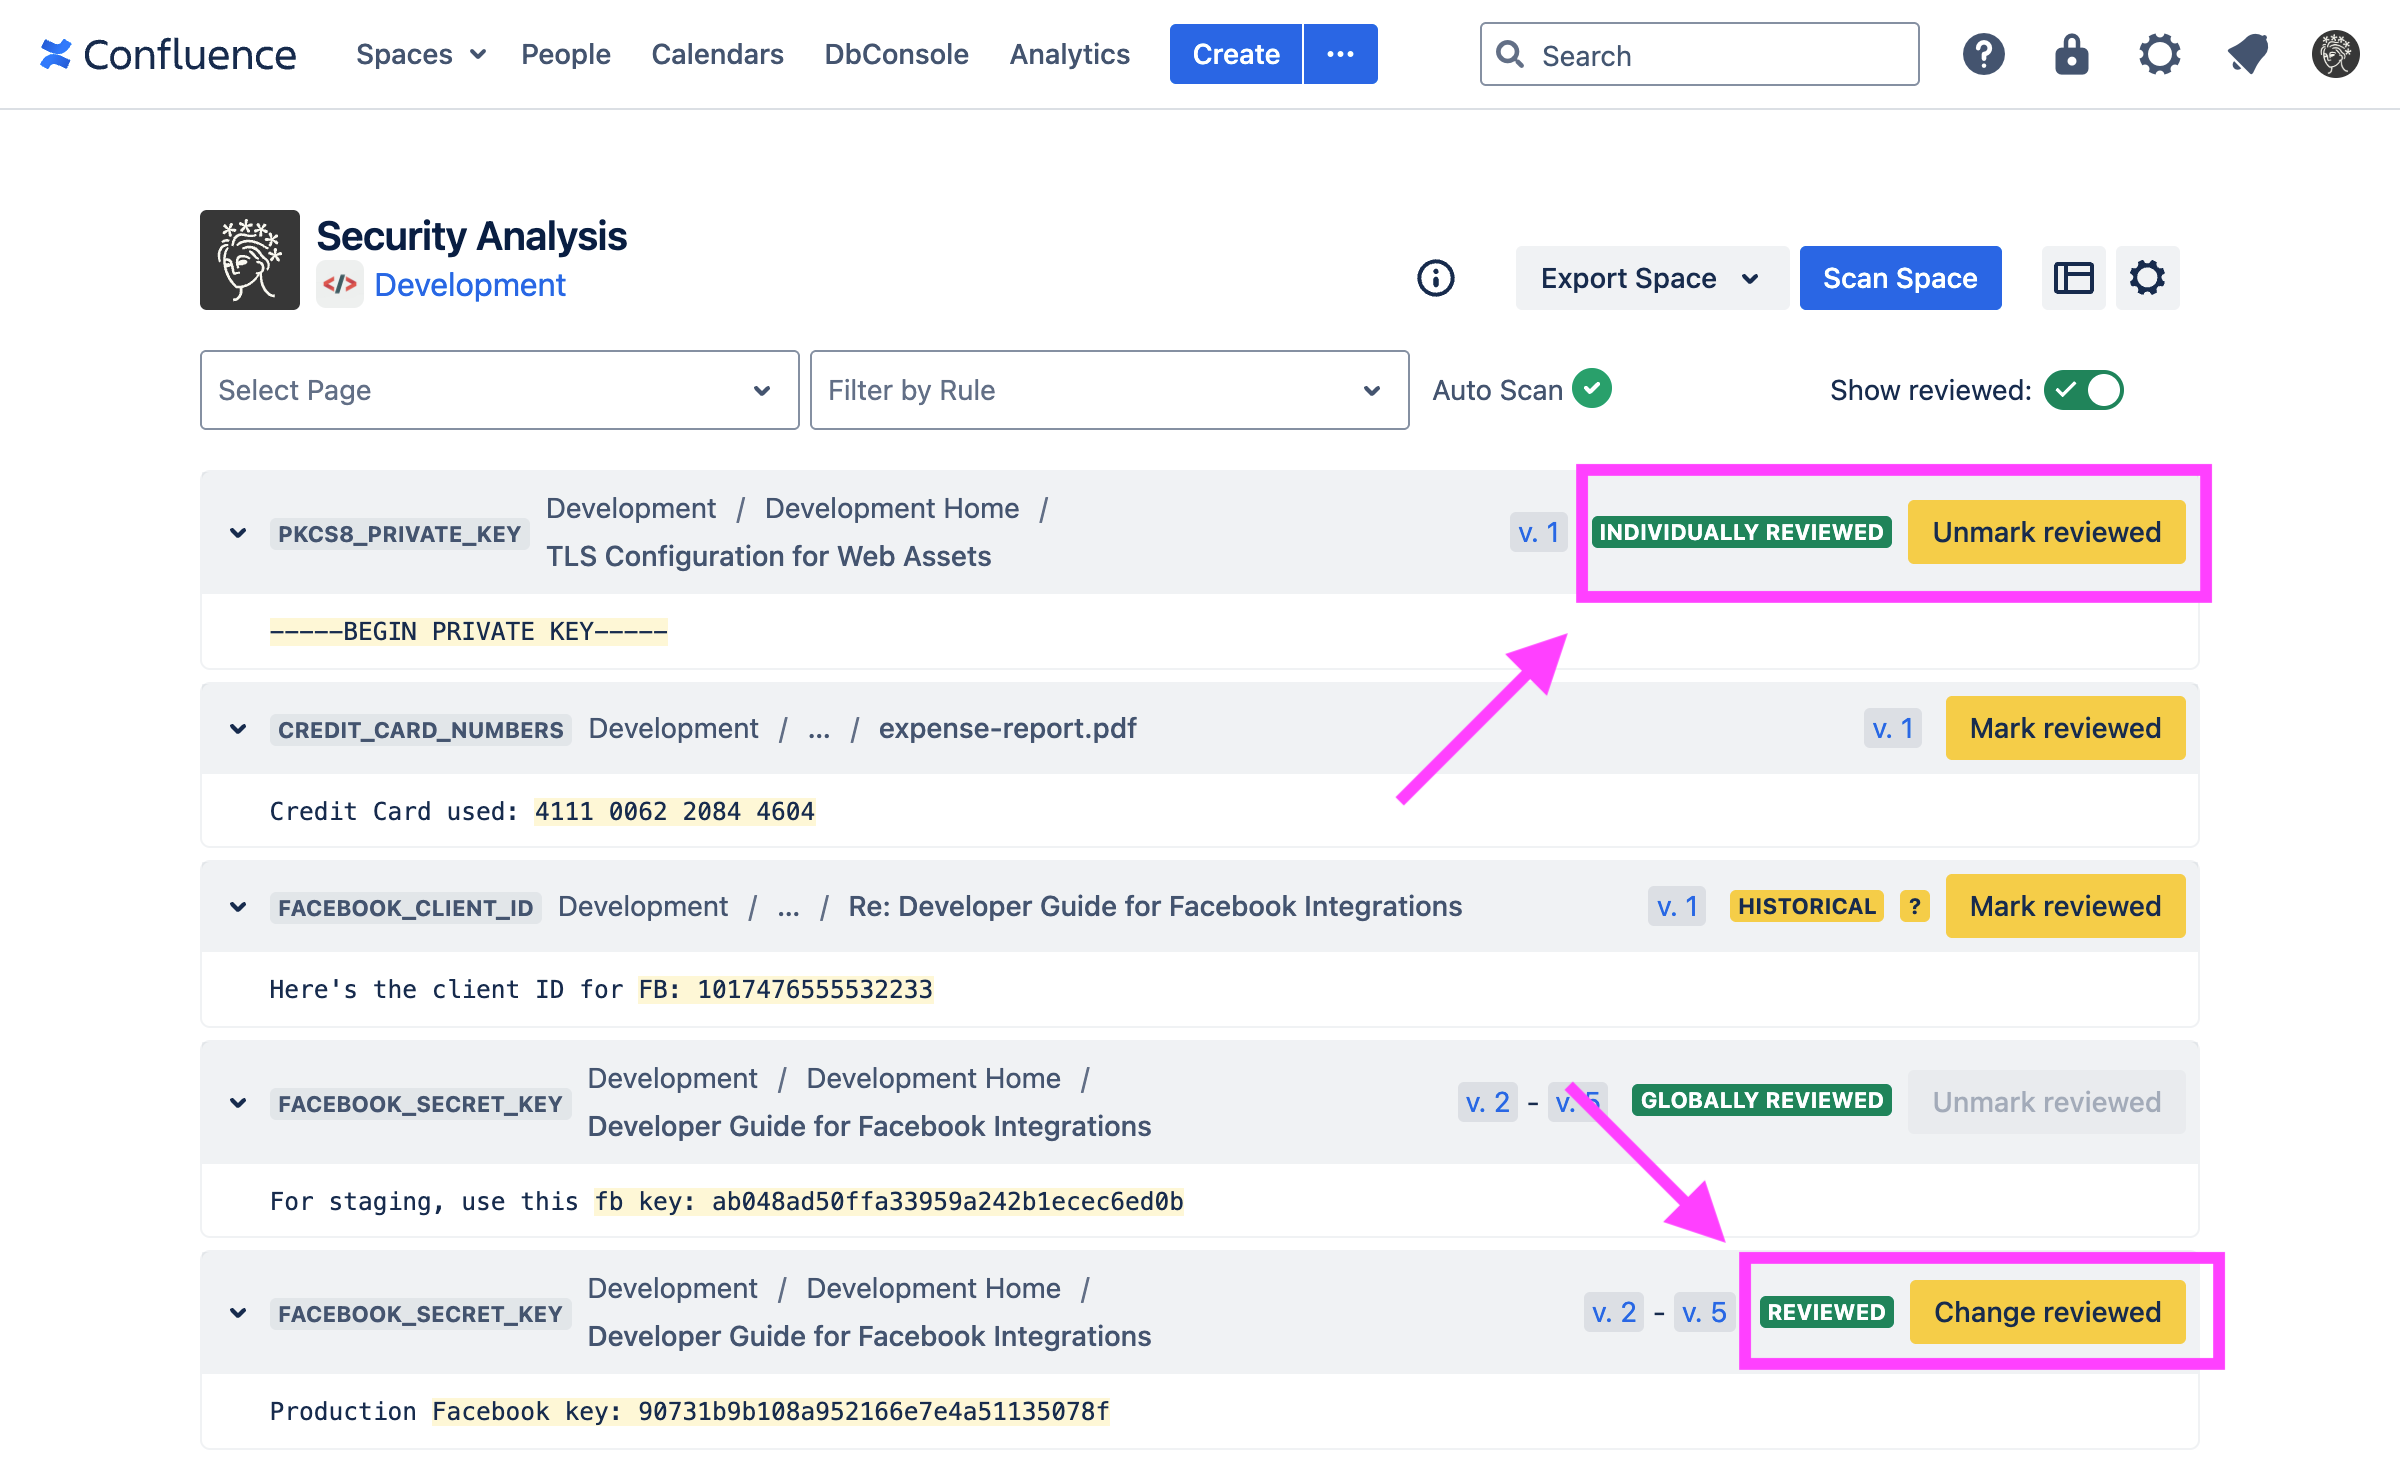
You can change the review status for a finding when it can be either individually reviewed or reviewed for the entire space. You can also unmark the review entirely. If a finding can only be individually reviewed, you will only be given the option to unmark it.
To review a finding more broadly than a space, consider [reviewing them globally](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Adding-new-global-false-positives).
Reviewed false positives are stored independently of any findings. In other words, after clicking "Mark Reviewed" on a finding, that reviewal persists and marks all future matching results as reviewed, even if the original finding is deleted.
### Exporting reviewed false positives
Information about reviewed false positives, such as who marked them reviewed and when, may be exported from the Security Analysis by clicking "Export Space" and then "Reviewed False Positives".
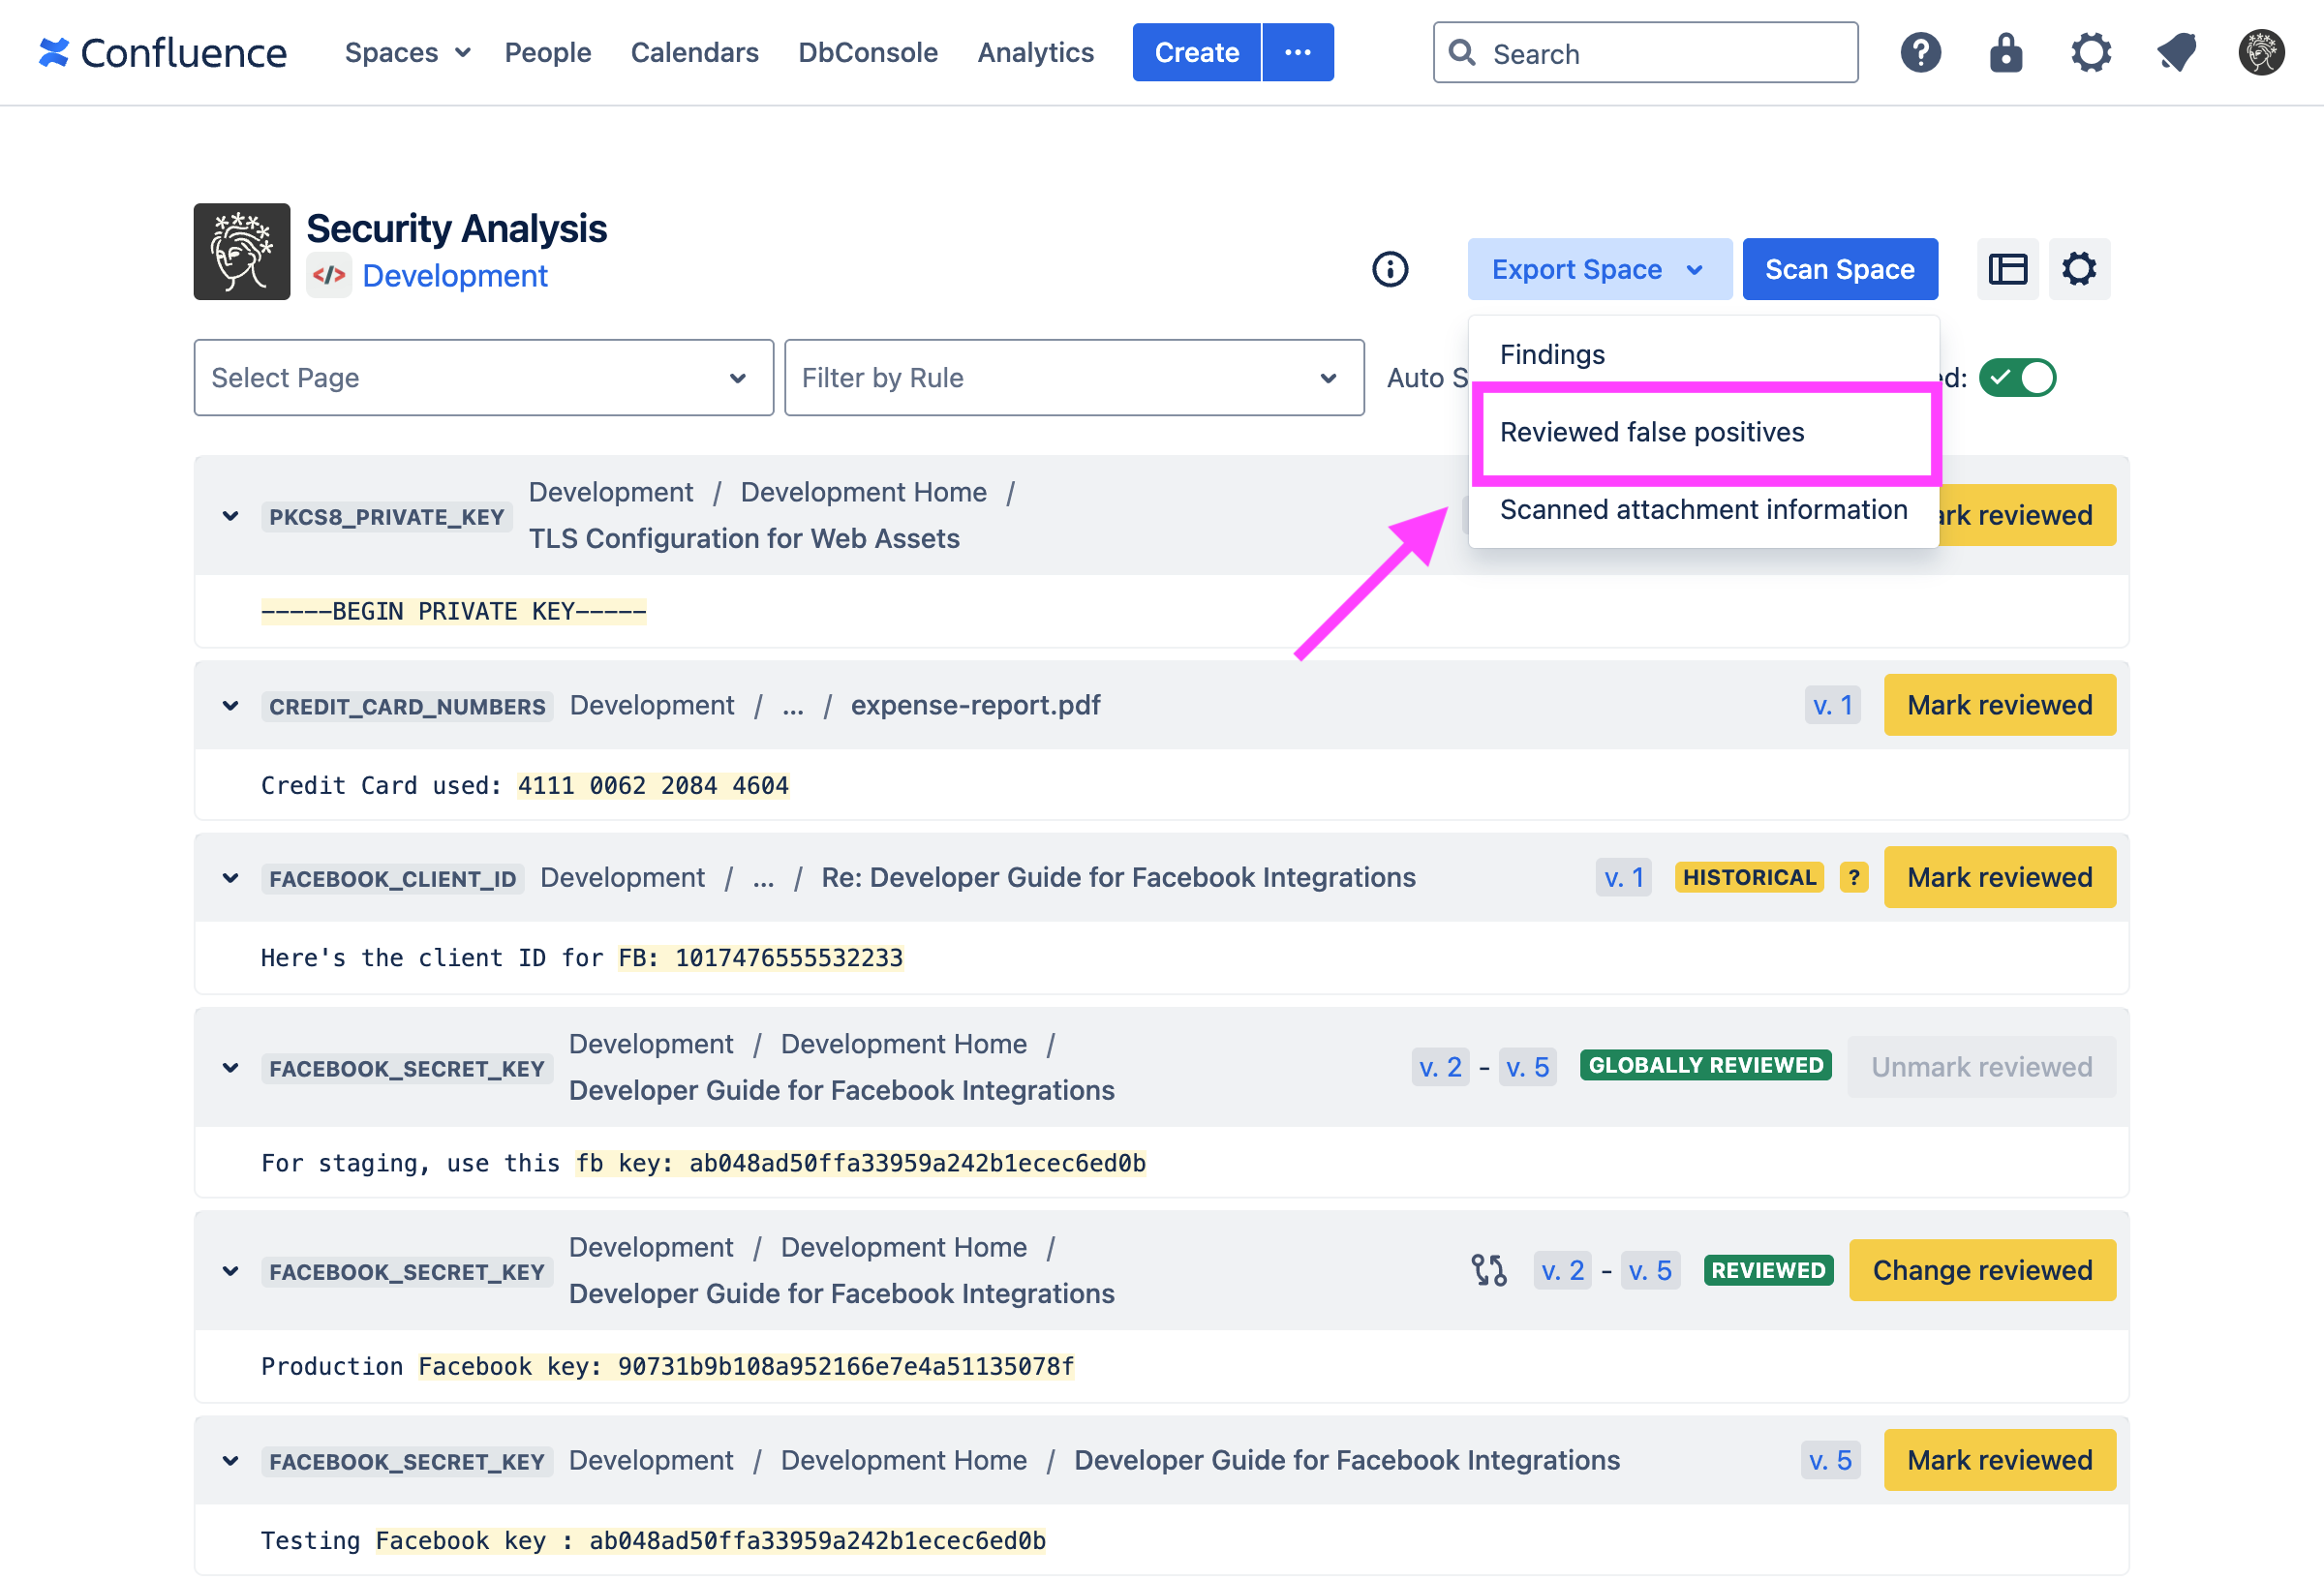
You can also export reviewed false positives in *all* your spaces from the Soteri Dashboard.
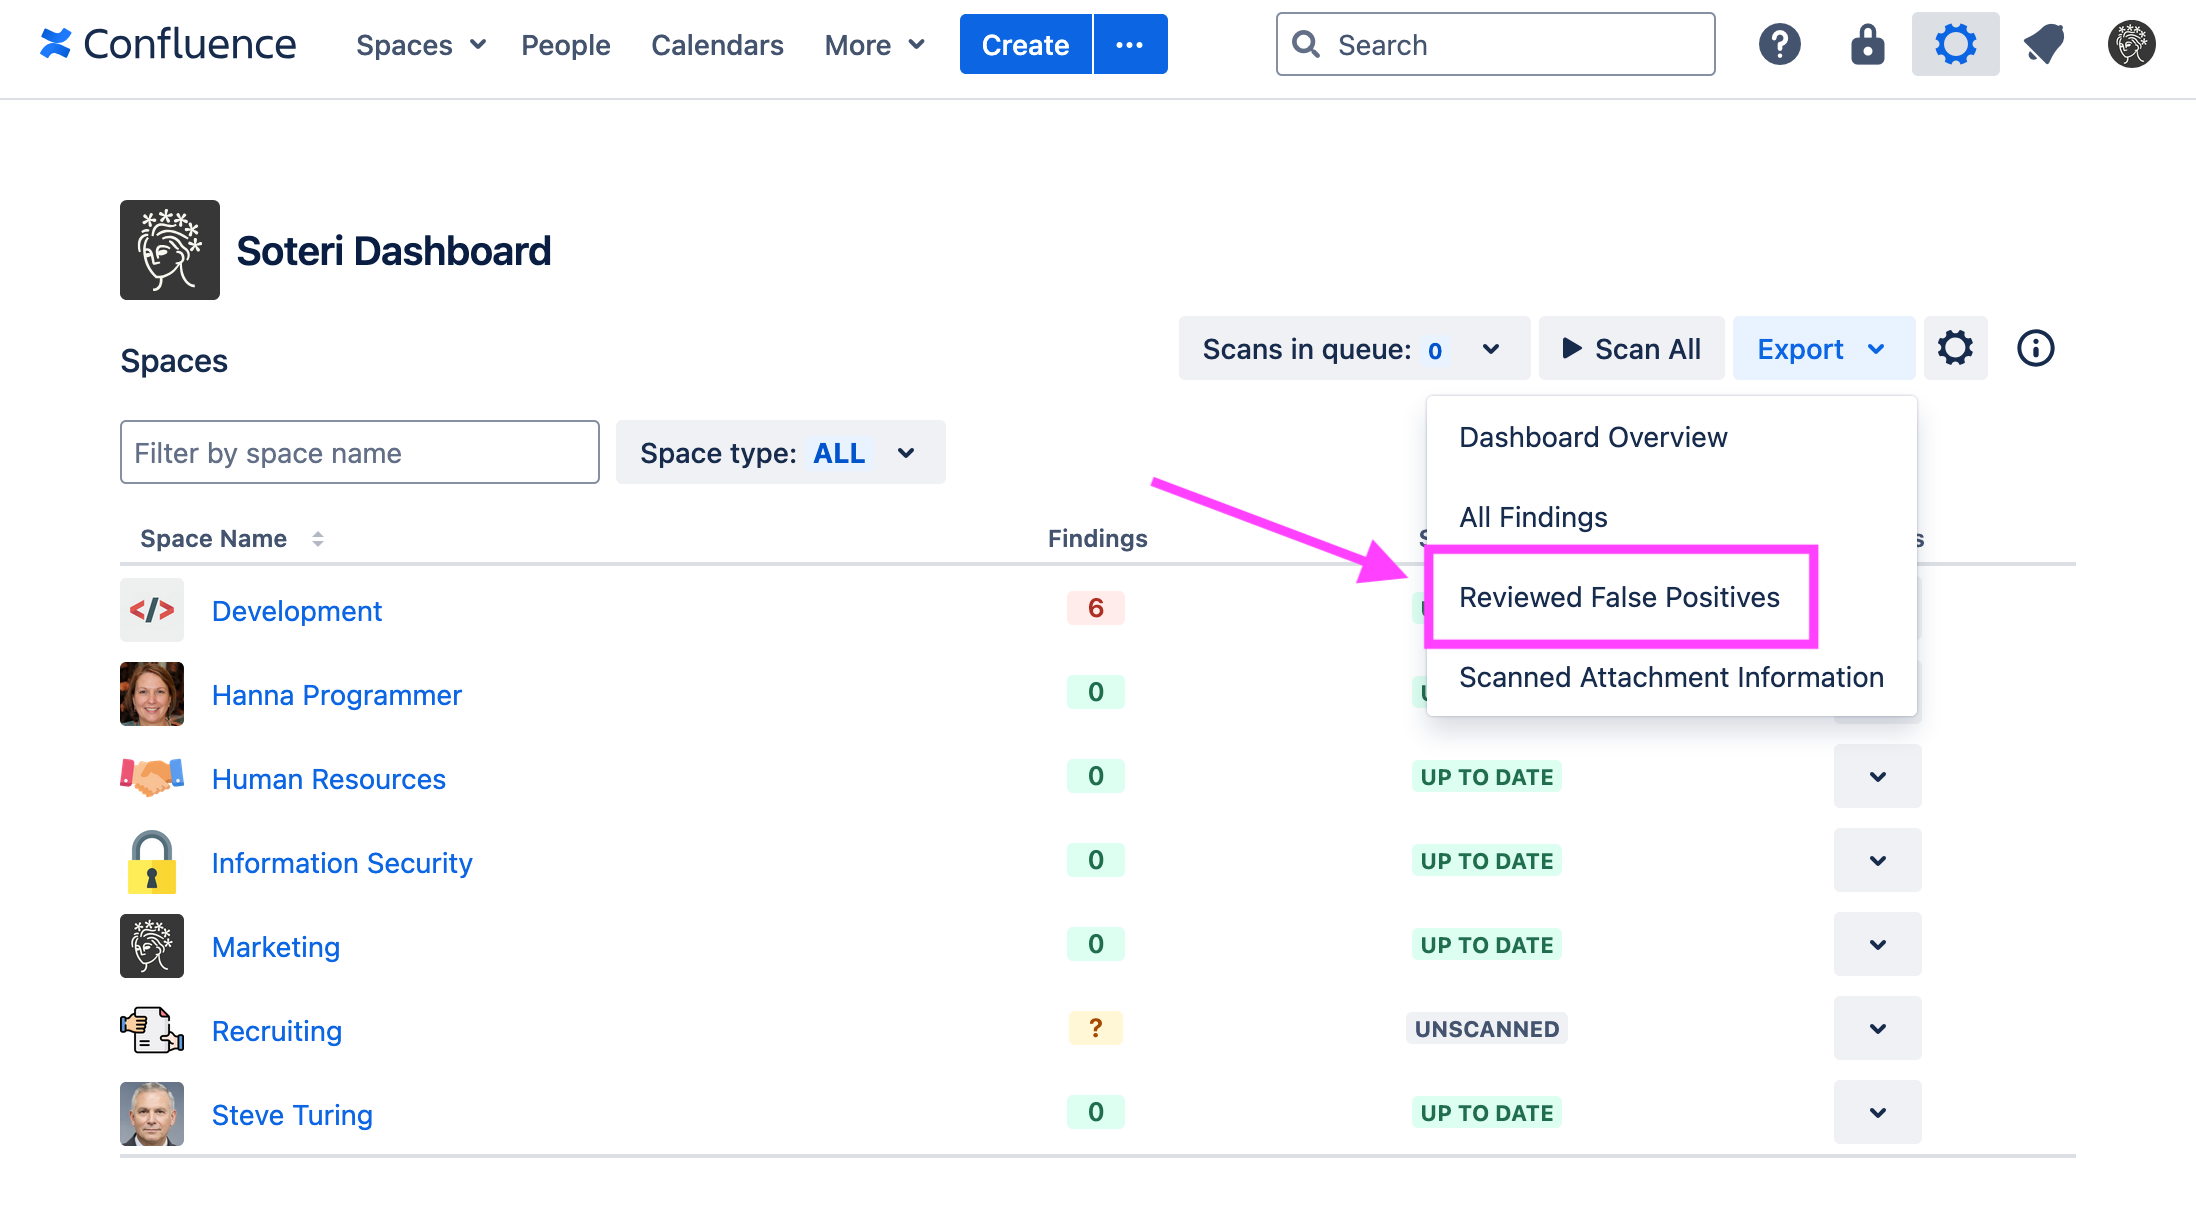
### Auditing who reviewed findings
When a finding is marked or unmarked reviewed, an audit log event is generated. This audit event includes who made the change, what rule generated the finding, and a link to the Security Analysis for viewing what exactly was reviewed. For more information, see [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md).
## Reviewing findings globally
Confluence administrators, or anyone granted explicit access (see [Granting Access to Additional Users and Groups](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) ) can add reviewed false positives which apply across all spaces in your Confluence instance using a CSV upload workflow.
Findings which match any of the global false positives show up as "Globally Reviewed" on the Security Analysis pages, and cannot be reviewed in the space scope.
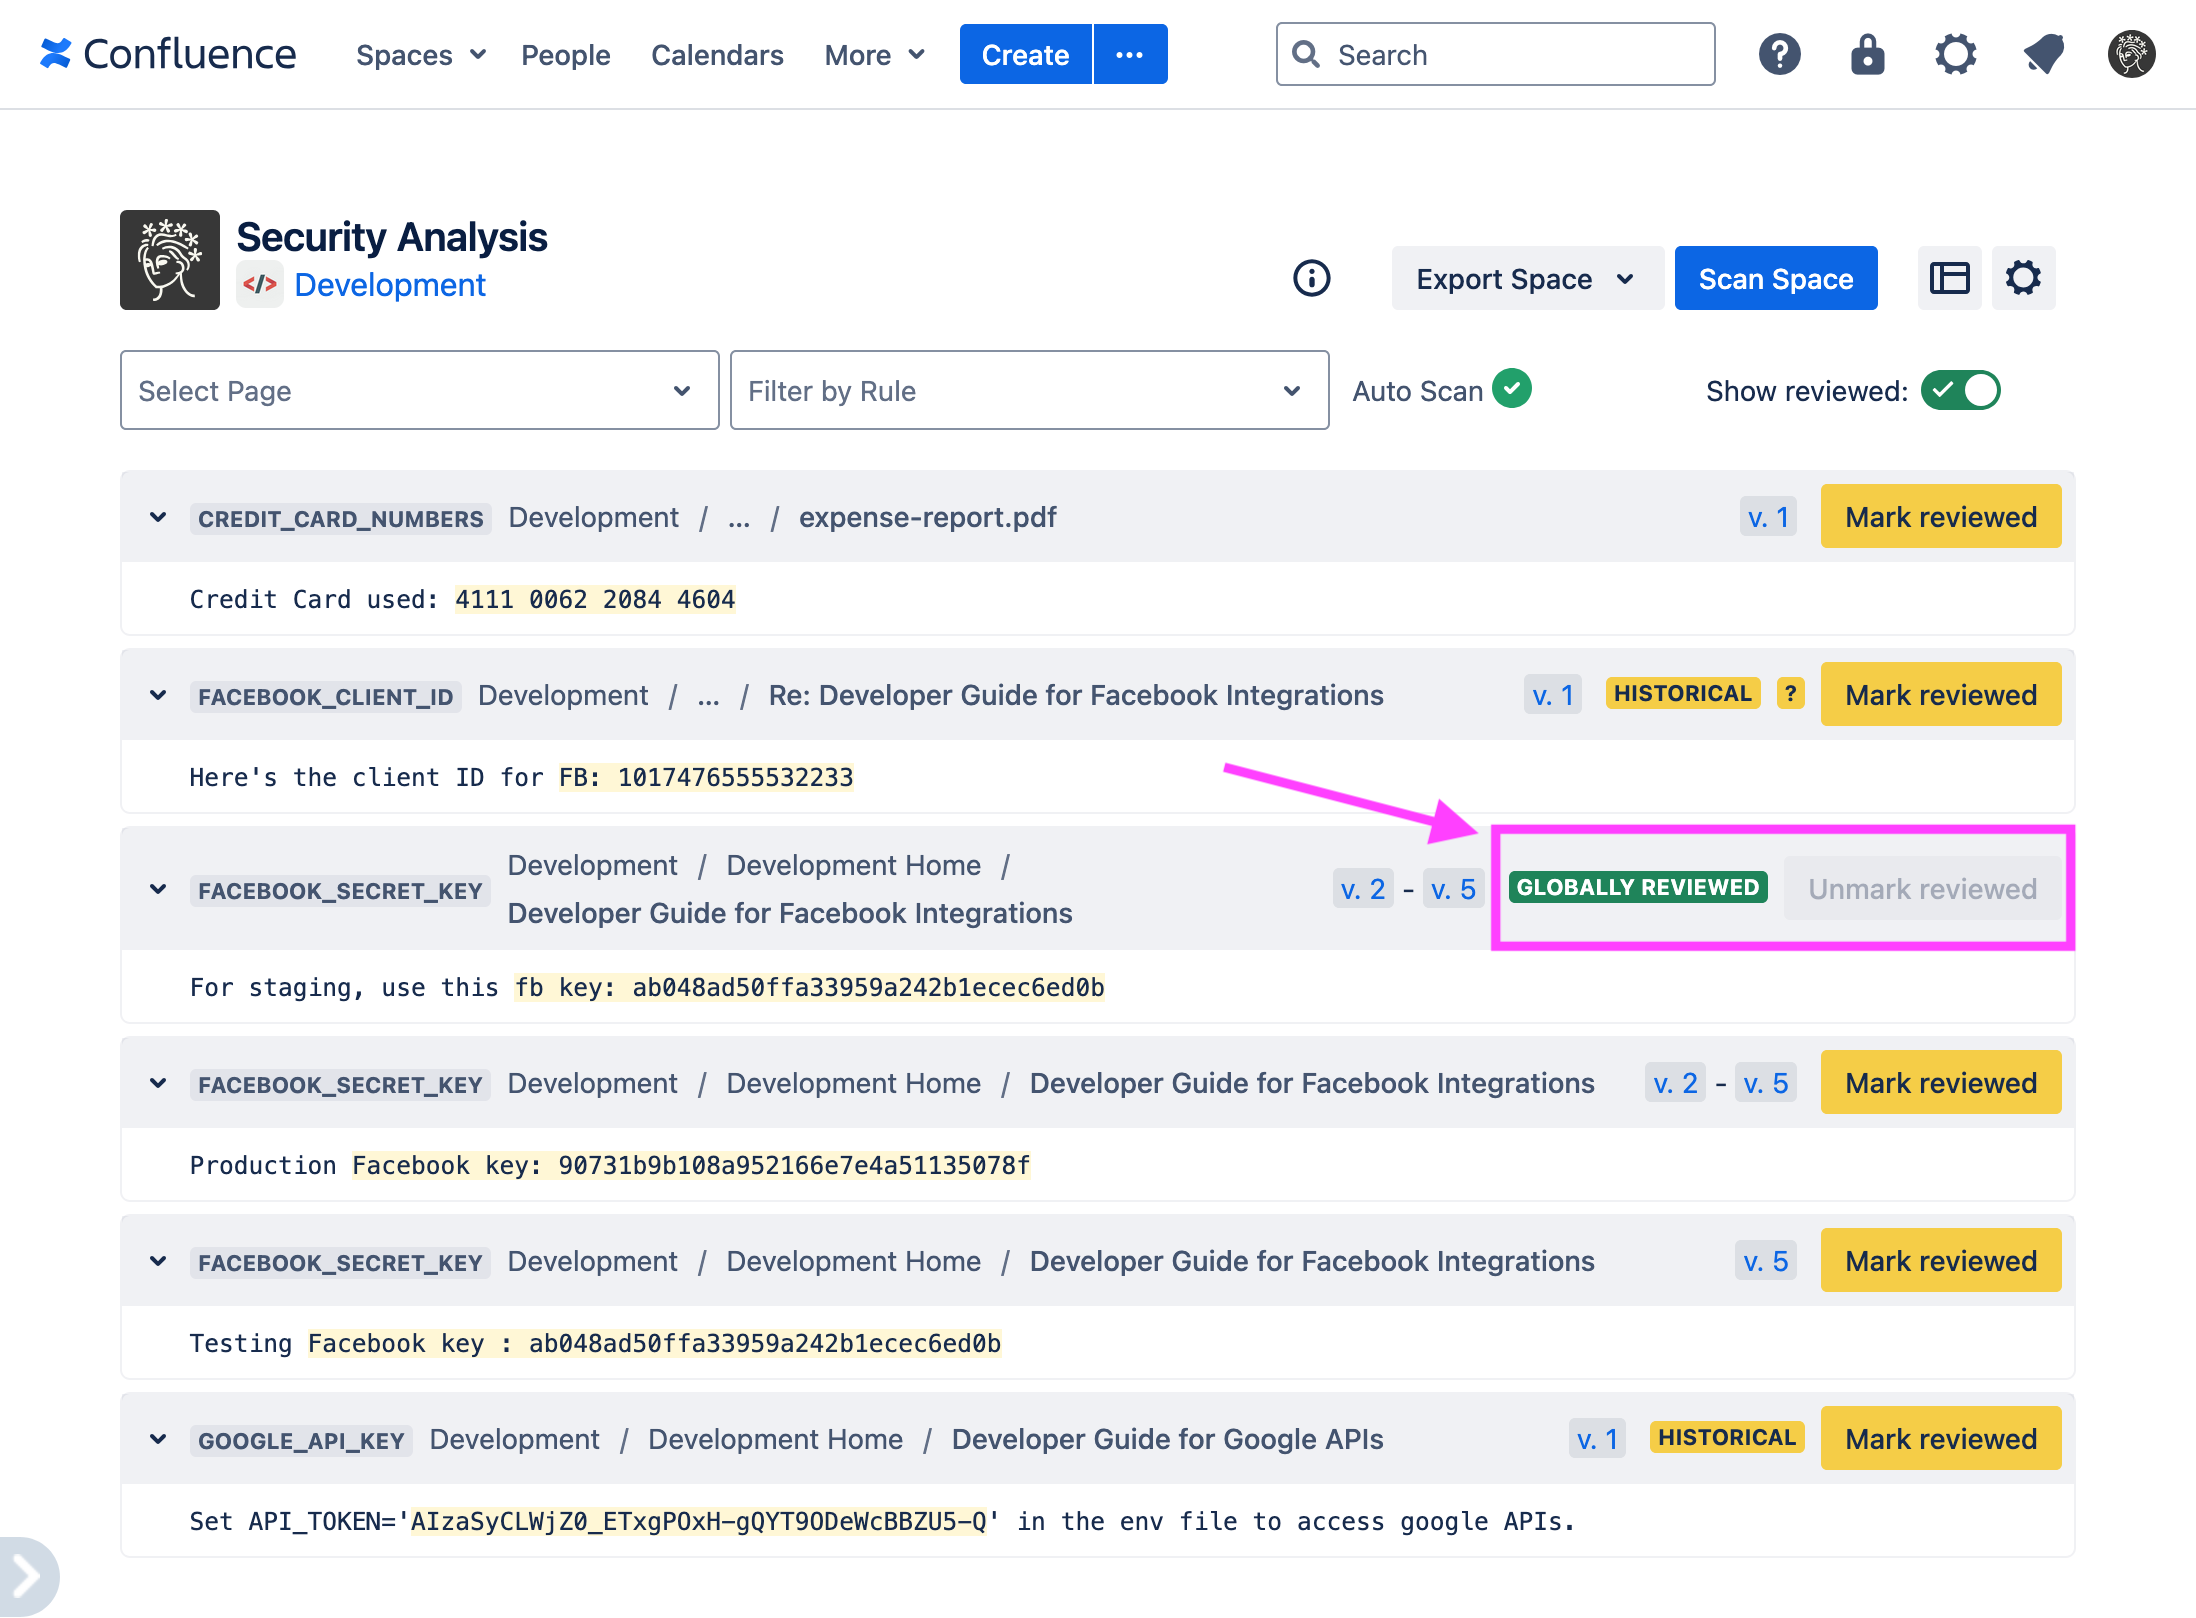
### Adding new global false positives
Navigate to the [settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md). Then, click on the "Add Reviewed" button under "Globally Review Findings":
Clicking on this button will open a modal which allows you to download a template for adding global false positives, and select an existing file to upload.
Uploaded files should be CSVs with a single column titled "Match text". Every row will be interpreted as a case-sensitive globally reviewed text to add.
You can copy over the "Match text" column in an [export](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) to create the upload file. However, note that some spreadsheet software---notably Microsoft Excel---rounds numbers and/or displays them in scientific notation by default. We recommend LibreOffice, Apple Numbers, or Google Sheets instead.
An audit log event is generated when globally reviewed false positives are added. See [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md) for more information.
### Deleting globally reviewed false positives
Navigate to the [settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md). Then, click on the "Remove Reviewed" button under "Globally Review Findings":
Clicking this button will open a modal which allows you to download a template for removing globally reviewed false positives, and select an existing file to upload.
Uploaded files should be CSVs with a single column titled "Match text". Every row will be interpreted as a case-sensitive globally reviewed text to remove.
You can un-review by copying the "Match text" from an export of globally reviewed findings. However, note that some spreadsheet software---notably Microsoft Excel---rounds numbers and/or displays them in scientific notation by default. We recommend LibreOffice, Apple Numbers, or Google Sheets instead.
An audit log event is generated when globally reviewed false positives are removed. See [Viewing Audited Events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md) for more information.
### Exporting globally reviewed false positives
Navigate to the [settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md). Then, click on the "Export" button under "Globally Review Findings":
Exports are in CSV format and include:
* The exact text that is considered reviewed
* Who reviewed it
* When it was reviewed
Globally reviewed false positives can also be exported via [REST API](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md).
---
version: "latest"
language: "en"
---
# How do I make sure all spaces are scanned, remain scanned, and remain secret-free?
As a Confluence administrators, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), there are a few things you can do to ensure that your instance is free of sensitive content while the content of its spaces changes.
1. First, make sure you are using appropriate scanning rules for your instance. This involves enabling the appropriate [built-in rules](https://docs.soteri.io/security-for-confluence-dc/1.7.3/enabling-and-disabling-global-scanning-rules) as well as creating appropriate [custom rules](https://docs.soteri.io/security-for-confluence-dc/1.7.3/defining-custom-detection-rules) that should apply for your organization.
2. Next, make sure that "Keep space scans up-to-date" is enabled as discussed [here](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md).
3. Next, make sure to enable e-mail alerts to content authors as discussed [here](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md).
4. Finally, in the [Soteri Dashboard](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md), push the **Scan All** button.
After all space scans are complete, your instance will be actively monitored for new issues, and when a potential issue is published, the responsible author will know right away so they can take the appropriate [mitigating action](https://docs.soteri.io/security-for-confluence-dc/latest/what-do-i-do-if-a-security-scan-finds-a-secret.md).
Administrators can also [view audited events](https://docs.soteri.io/security-for-confluence-dc/latest/viewing-audited-events.md#Audited-Events) keep track of newly published sensitive content and notifications sent to authors who published sensitive content.
Please bear in mind that, if you change which built-in rules are enabled, or if you change the custom rules that are enabled, then you will need to push the **Scan All** button again to make sure each space scan is up-to-date with the new rules.
---
version: "latest"
language: "en"
---
# Overview
It's a significant risk in Confluence -- any user can post access keys, passwords, and many other kinds of sensitive information in plain text, right into a wiki page, blog post, comment, or a file attached to a page.
Confluence has no built-in mechanism to detect content that contains sensitive credentials that could fall into the wrong hands, and typical workflows make this an all-too-easy omission, even by well intentioned users.
This poses an enormous security risk, as access to such information could lead to privilege escalation, either by malicious users who have network access to the Confluence instance, or by an external attacker who has bridged the perimeter security. Just imagine what someone could do with a password to a network device, an AWS access key, or financial account information.
To help prevent such situations, Security for Confluence integrates directly with Confluence, providing tools to automatically detect attempts to improperly store sensitive information, accidental or otherwise.
## Scanning spaces from the Soteri Dashboard
Scans may be triggered for spaces individually or, if you are a Confluence administrator, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), all at once. The easiest way to do either is via the [Soteri Dashboard](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md), which contains all spaces for which you have administration privileges.
To reach the Soteri Dashboard, click the padlock icon in the top-right toolbar in Confluence:
Then, to trigger a scan, you can either click the arrow icon next to the space, and select "Scan":
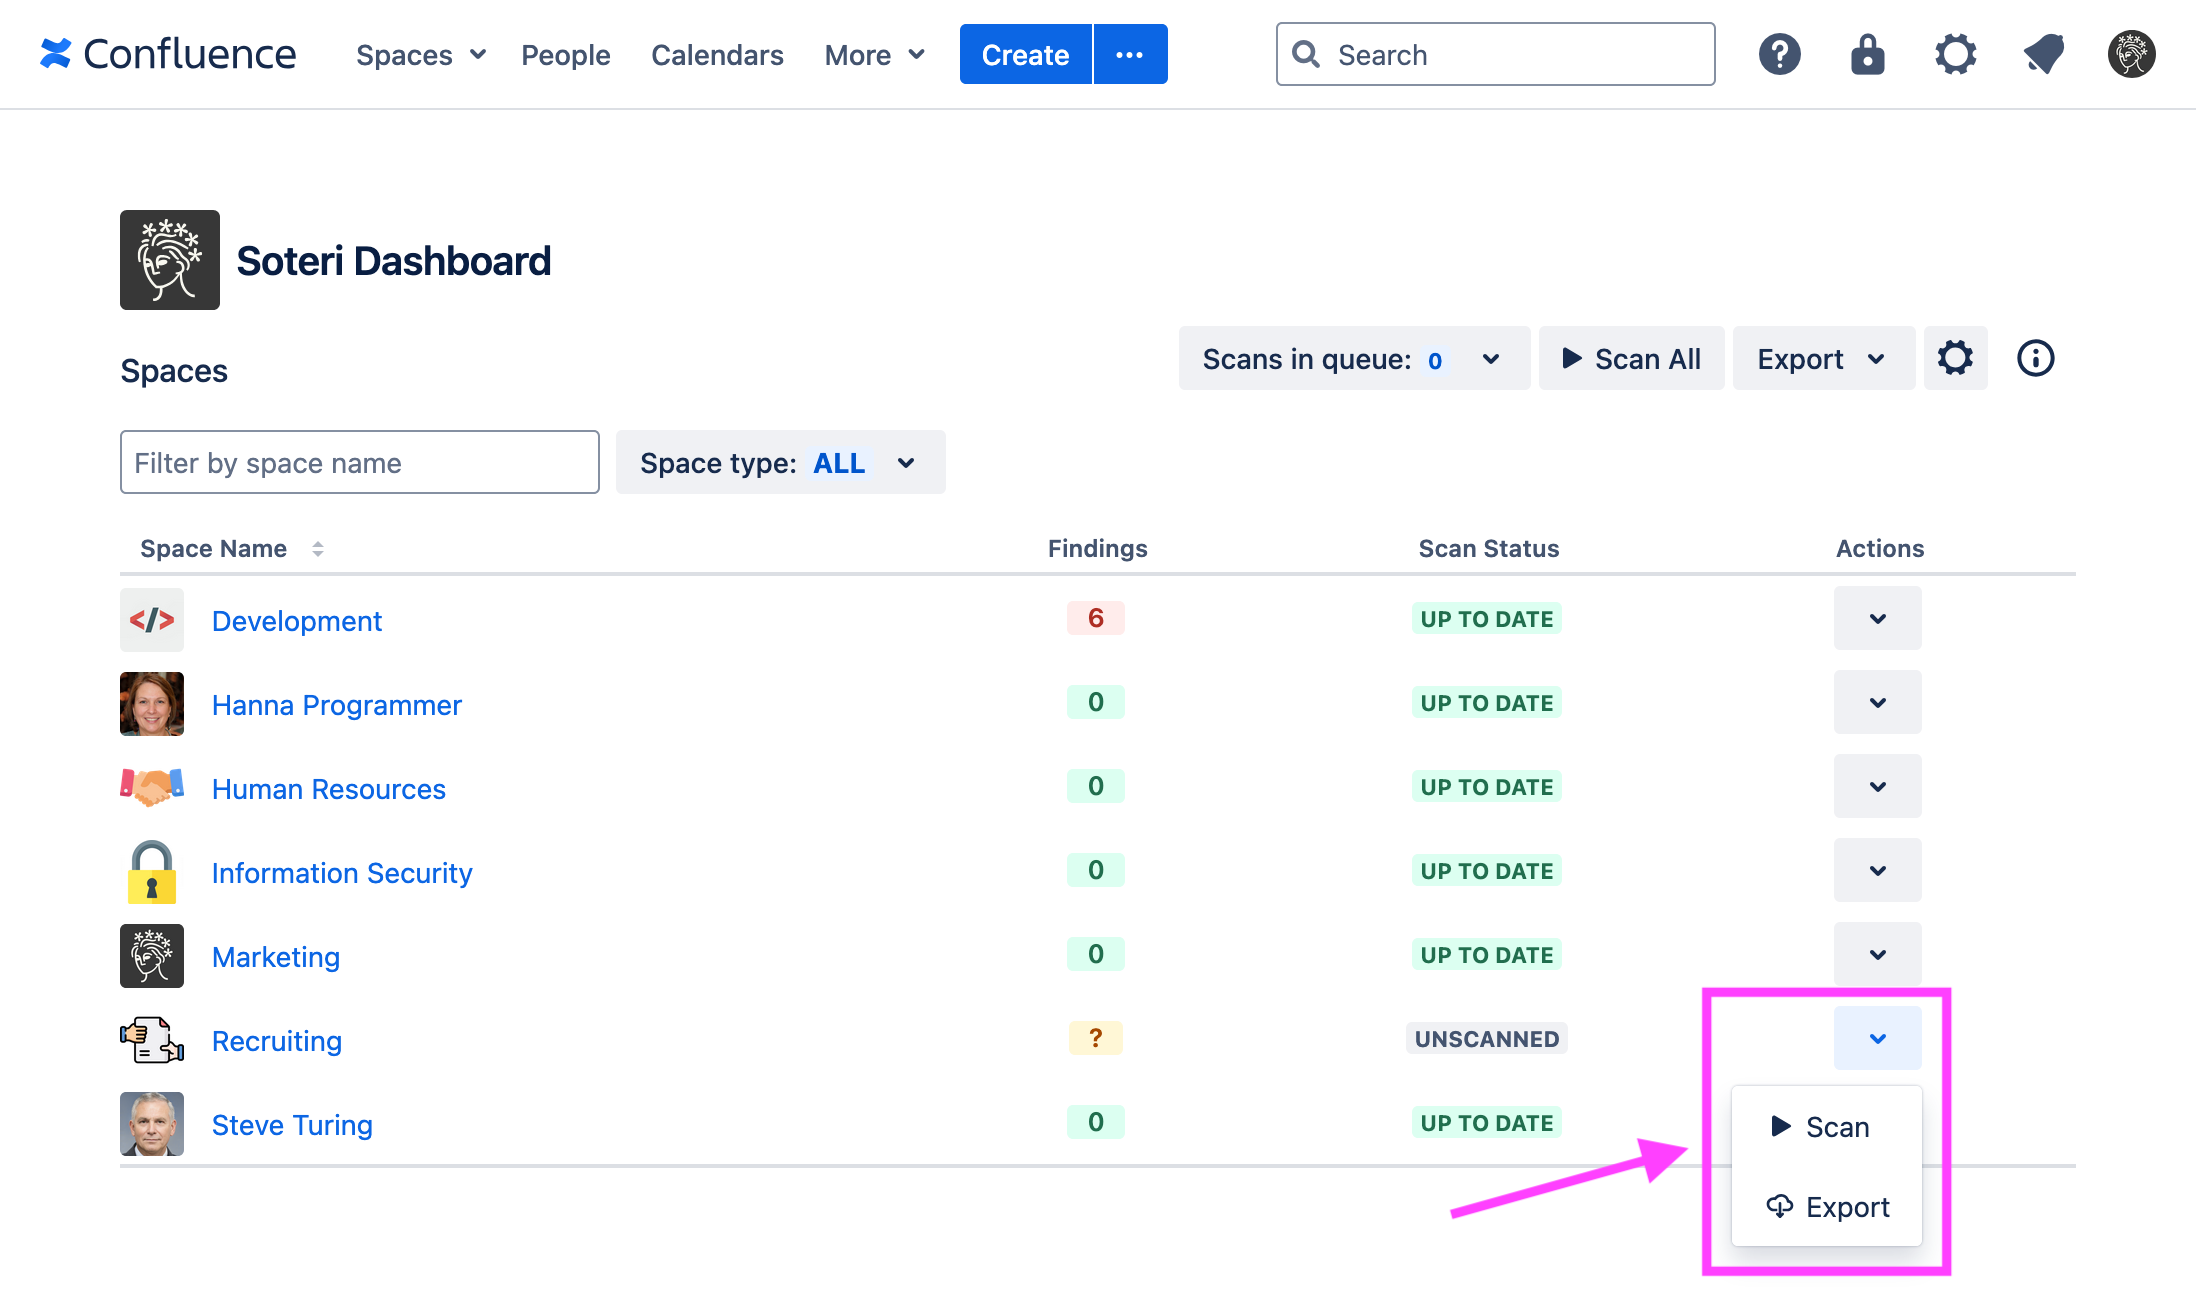
Or, if you are a Confluence administrator, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), click the "Scan All" button:
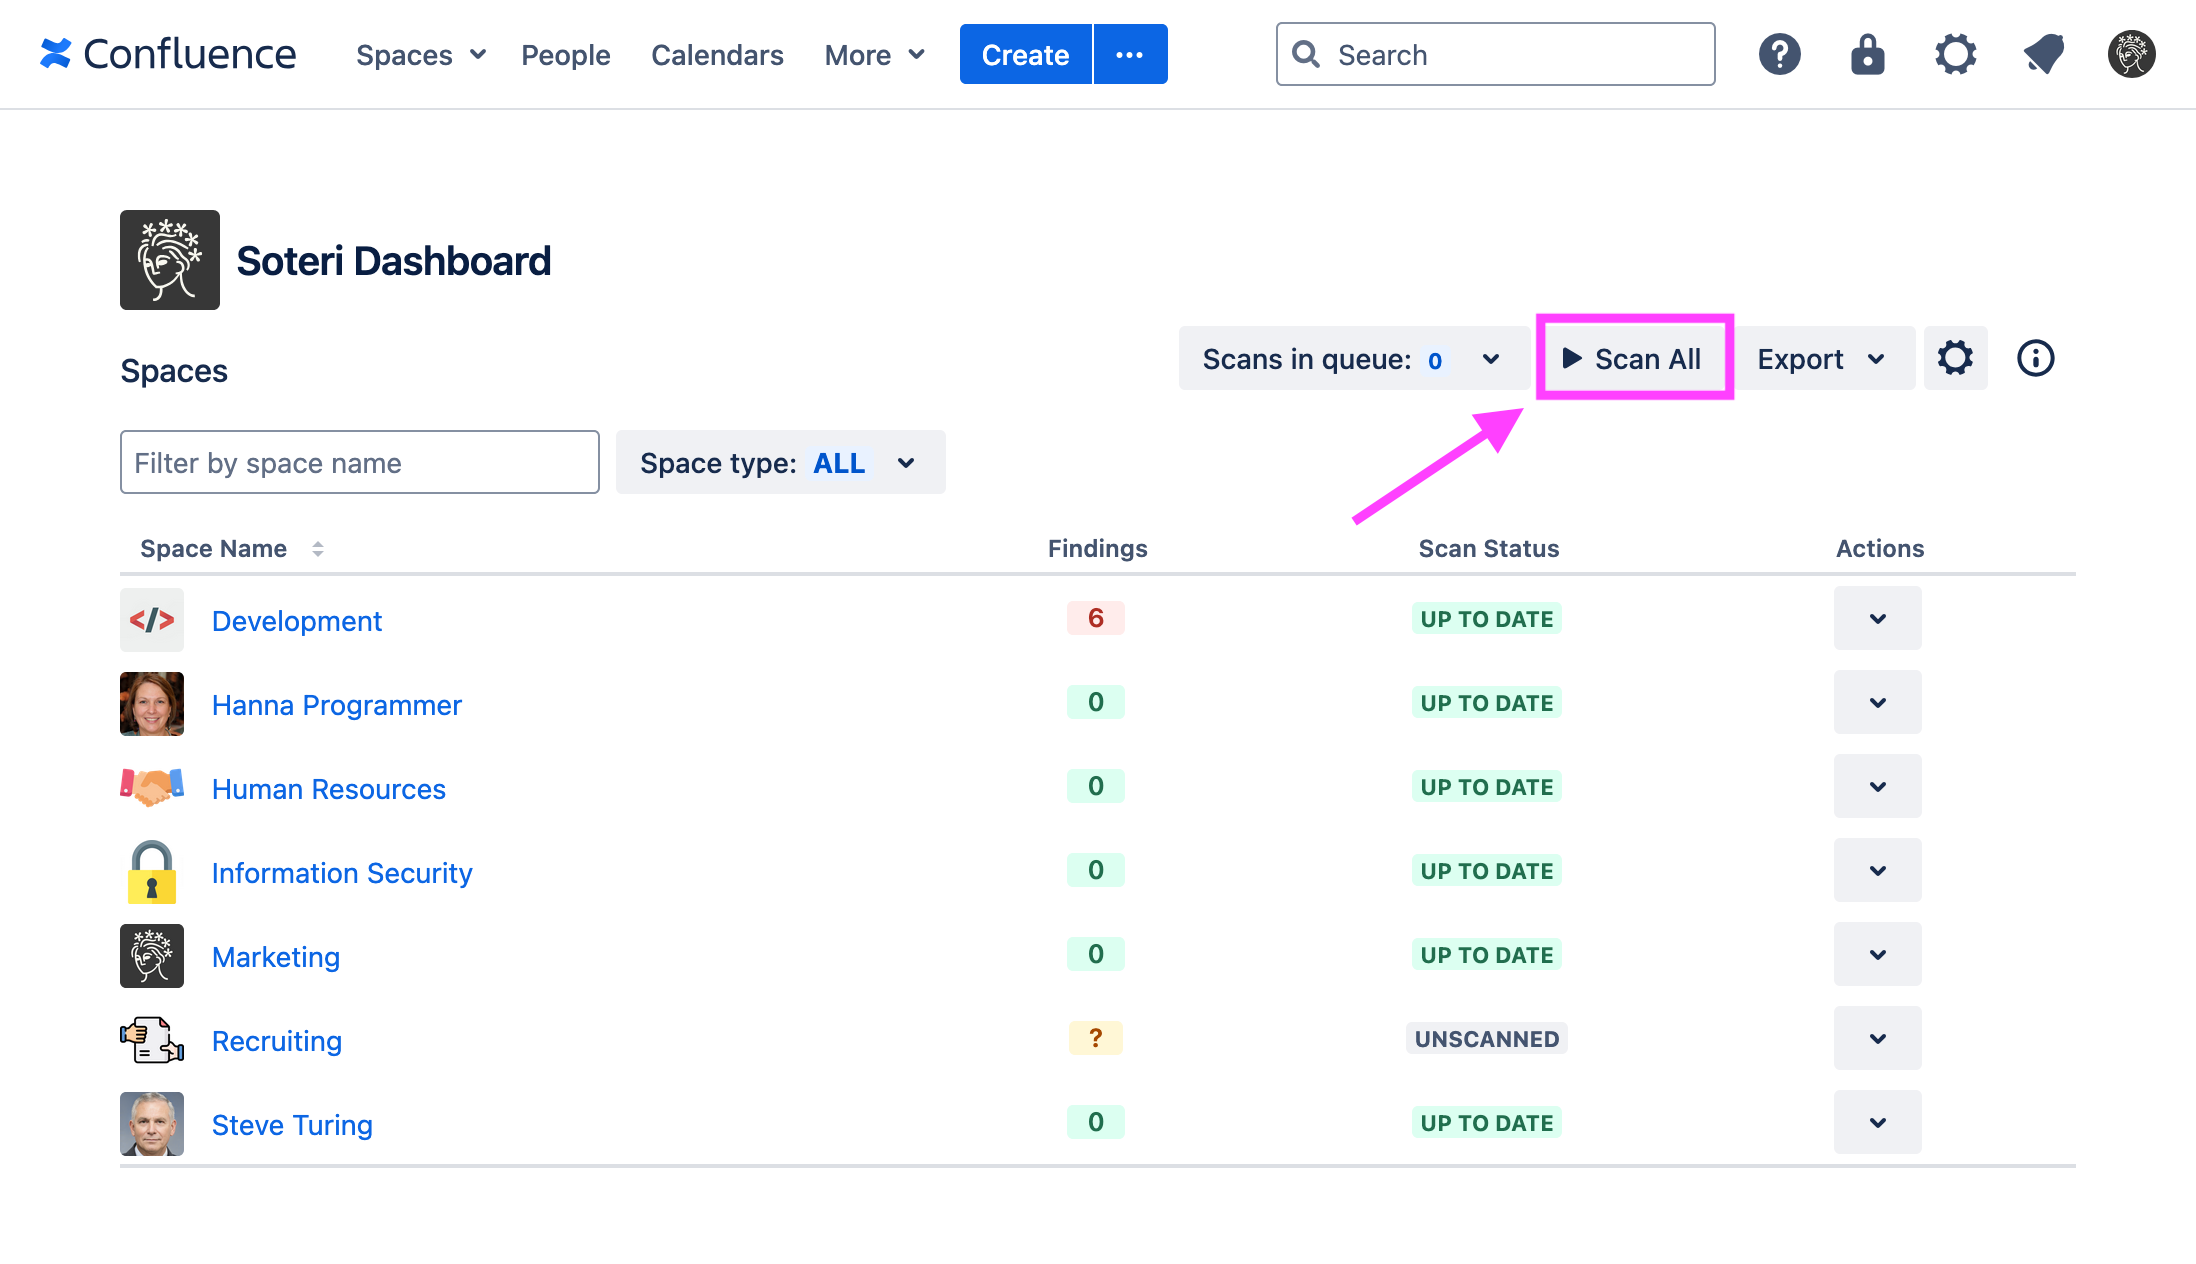
[Learn more about the Soteri Dashboard](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md).
## Viewing scan results in the Security Analysis
The [Security Analysis page](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md) allows you to view the results of a scan. To view a space's Security Analysis, you may either click the space's name in the Soteri Dashboard:
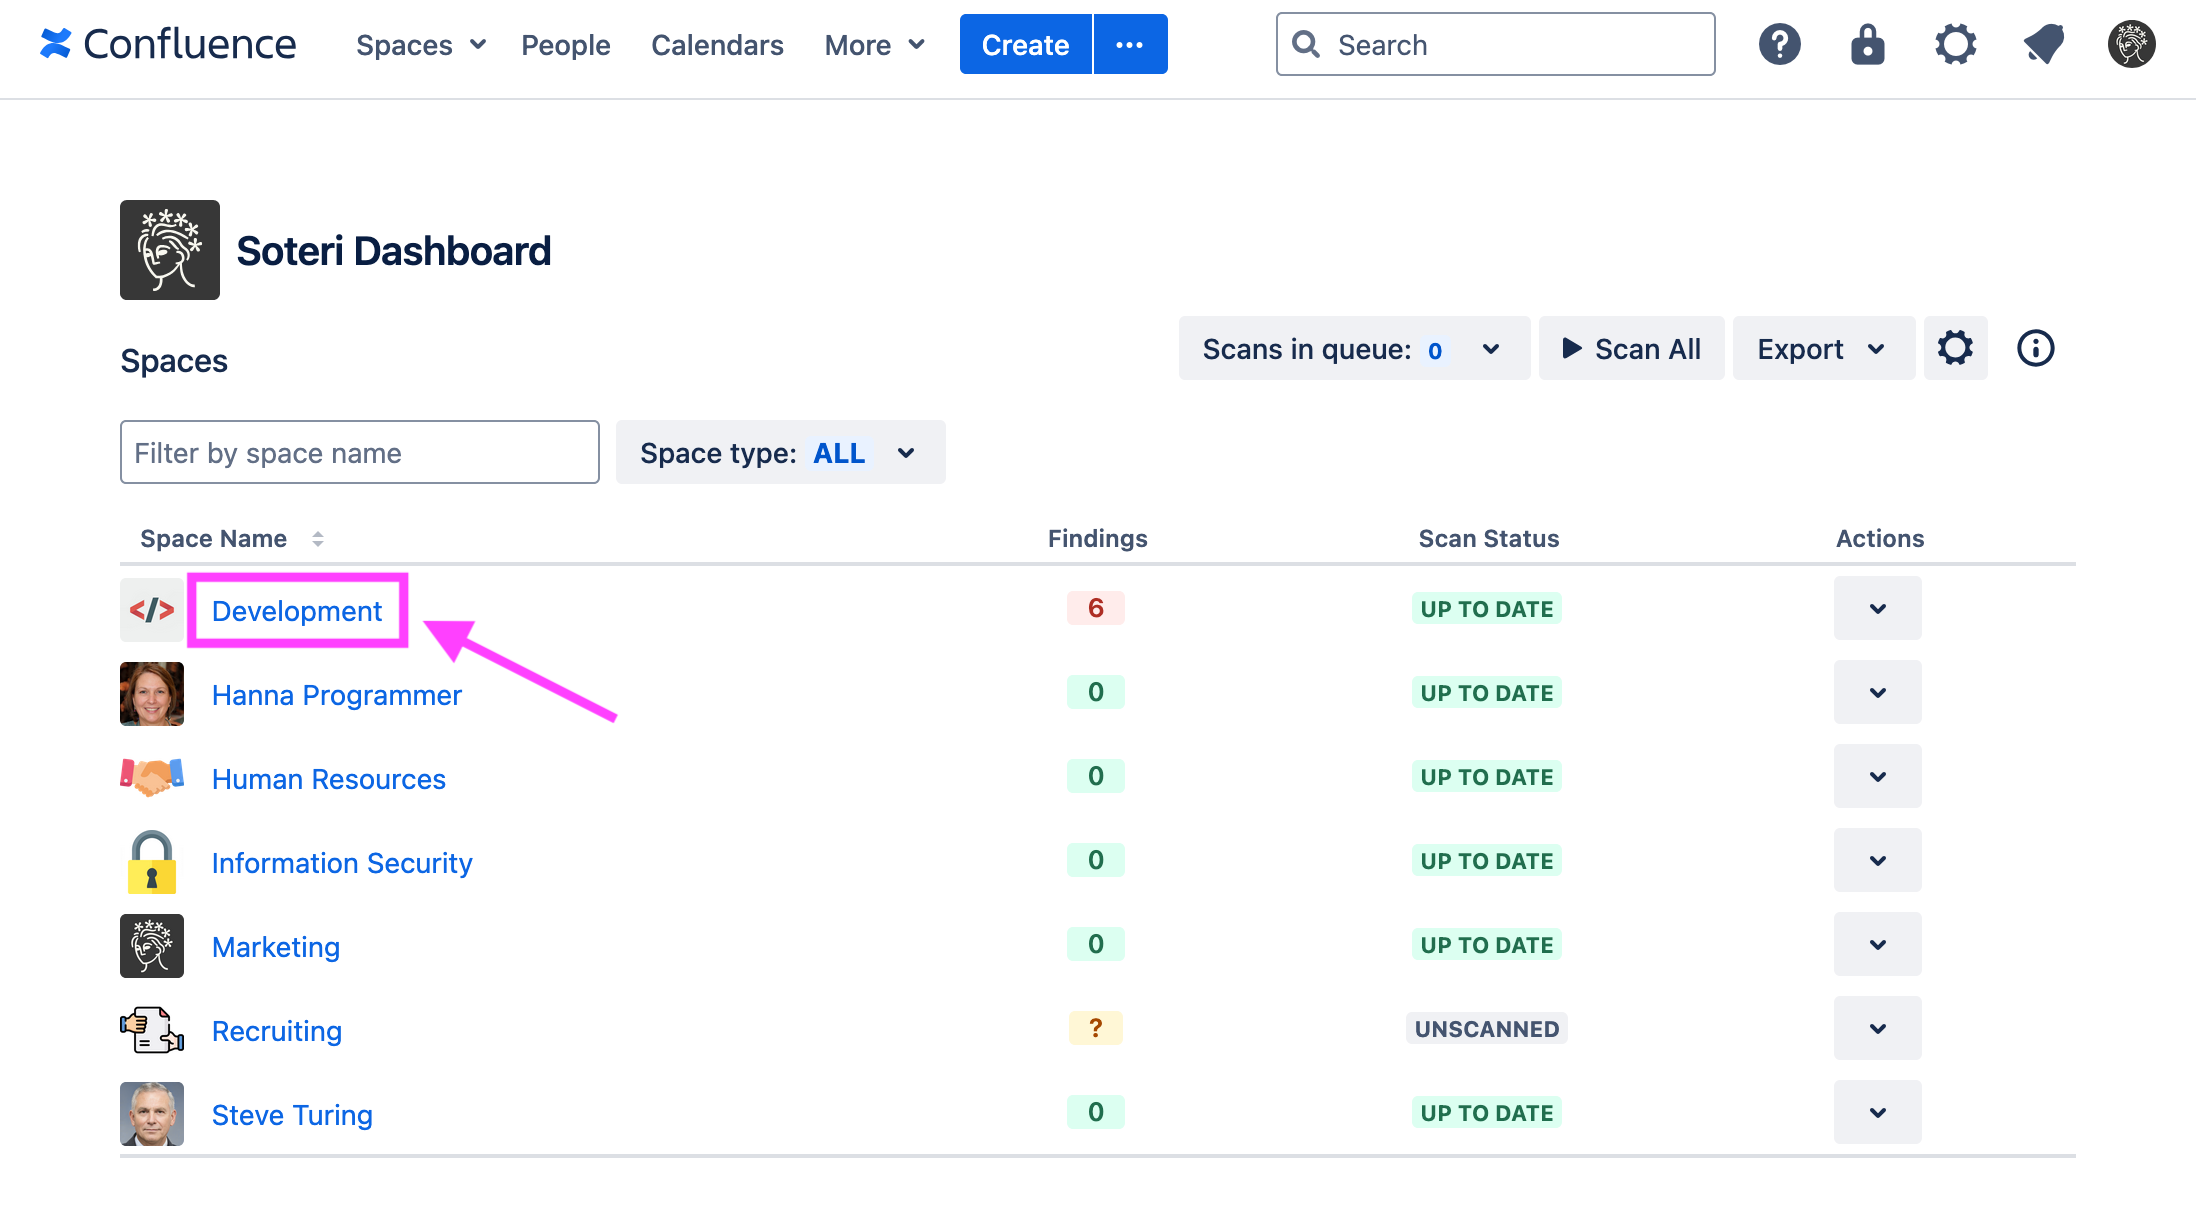
Or click "Security Analysis" while viewing the space normally in Confluence:
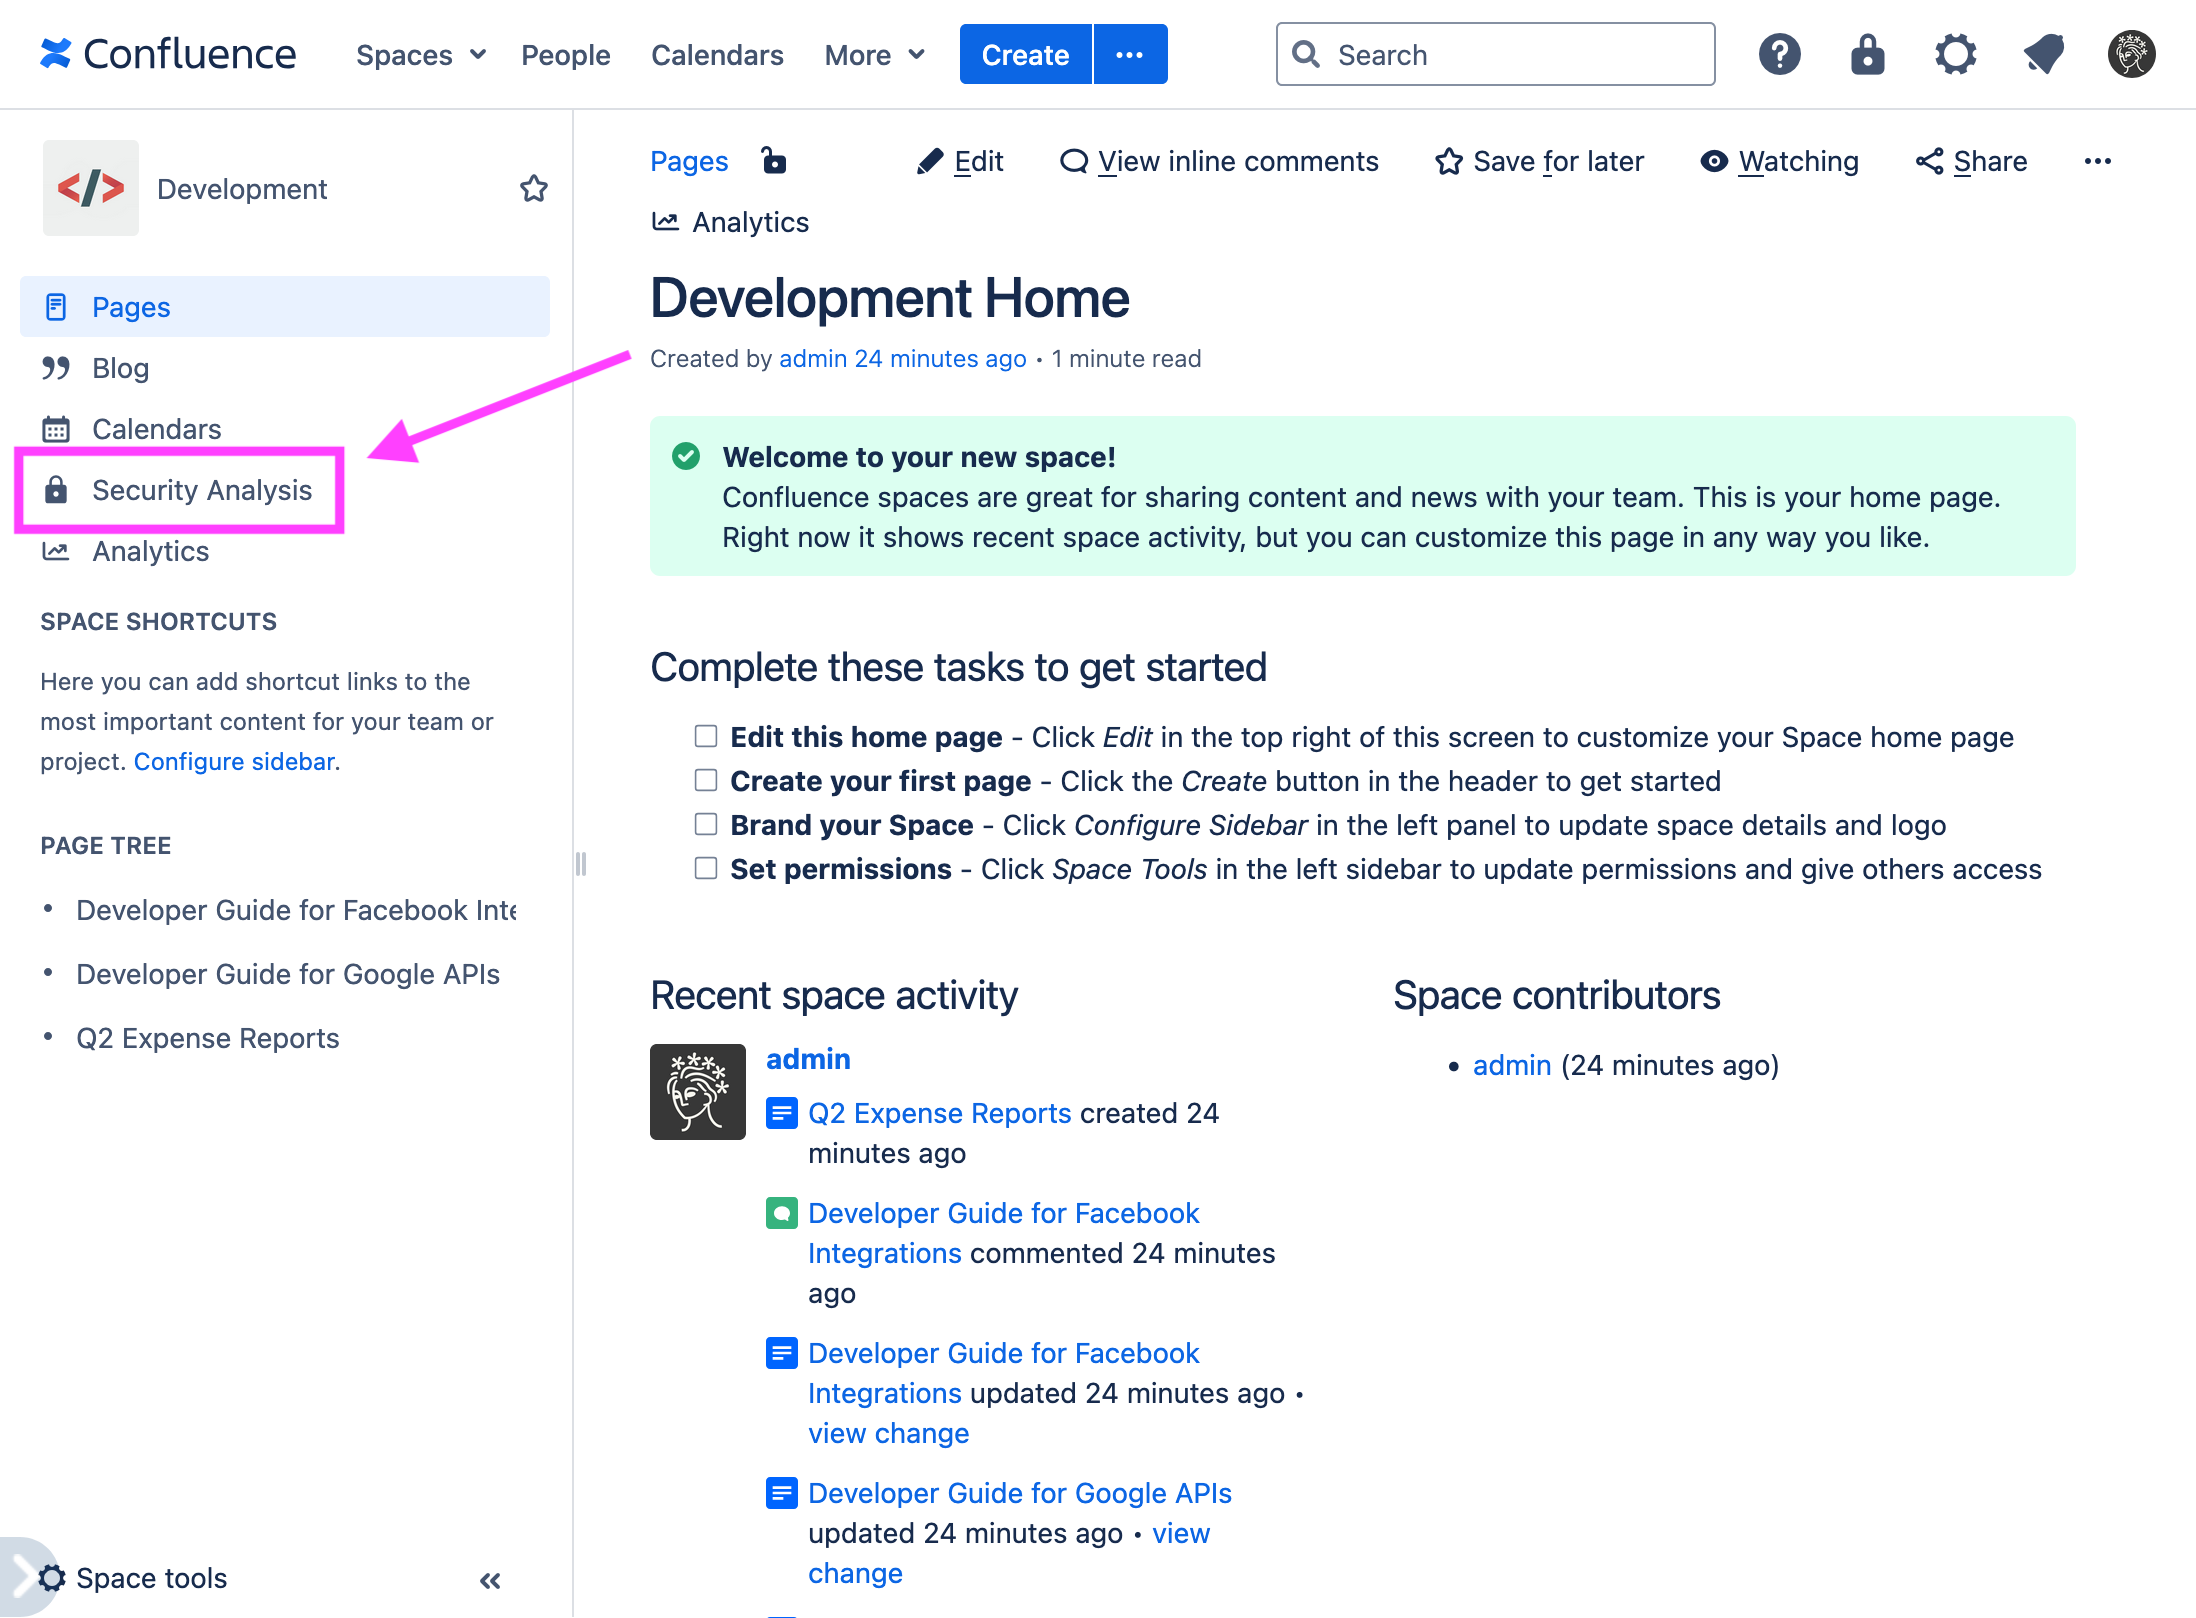
From the Security Analysis page, you can view and disposition scan findings for that particular space, including [hiding false positives](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md). You may also trigger a scan using the "Scan Space" button:
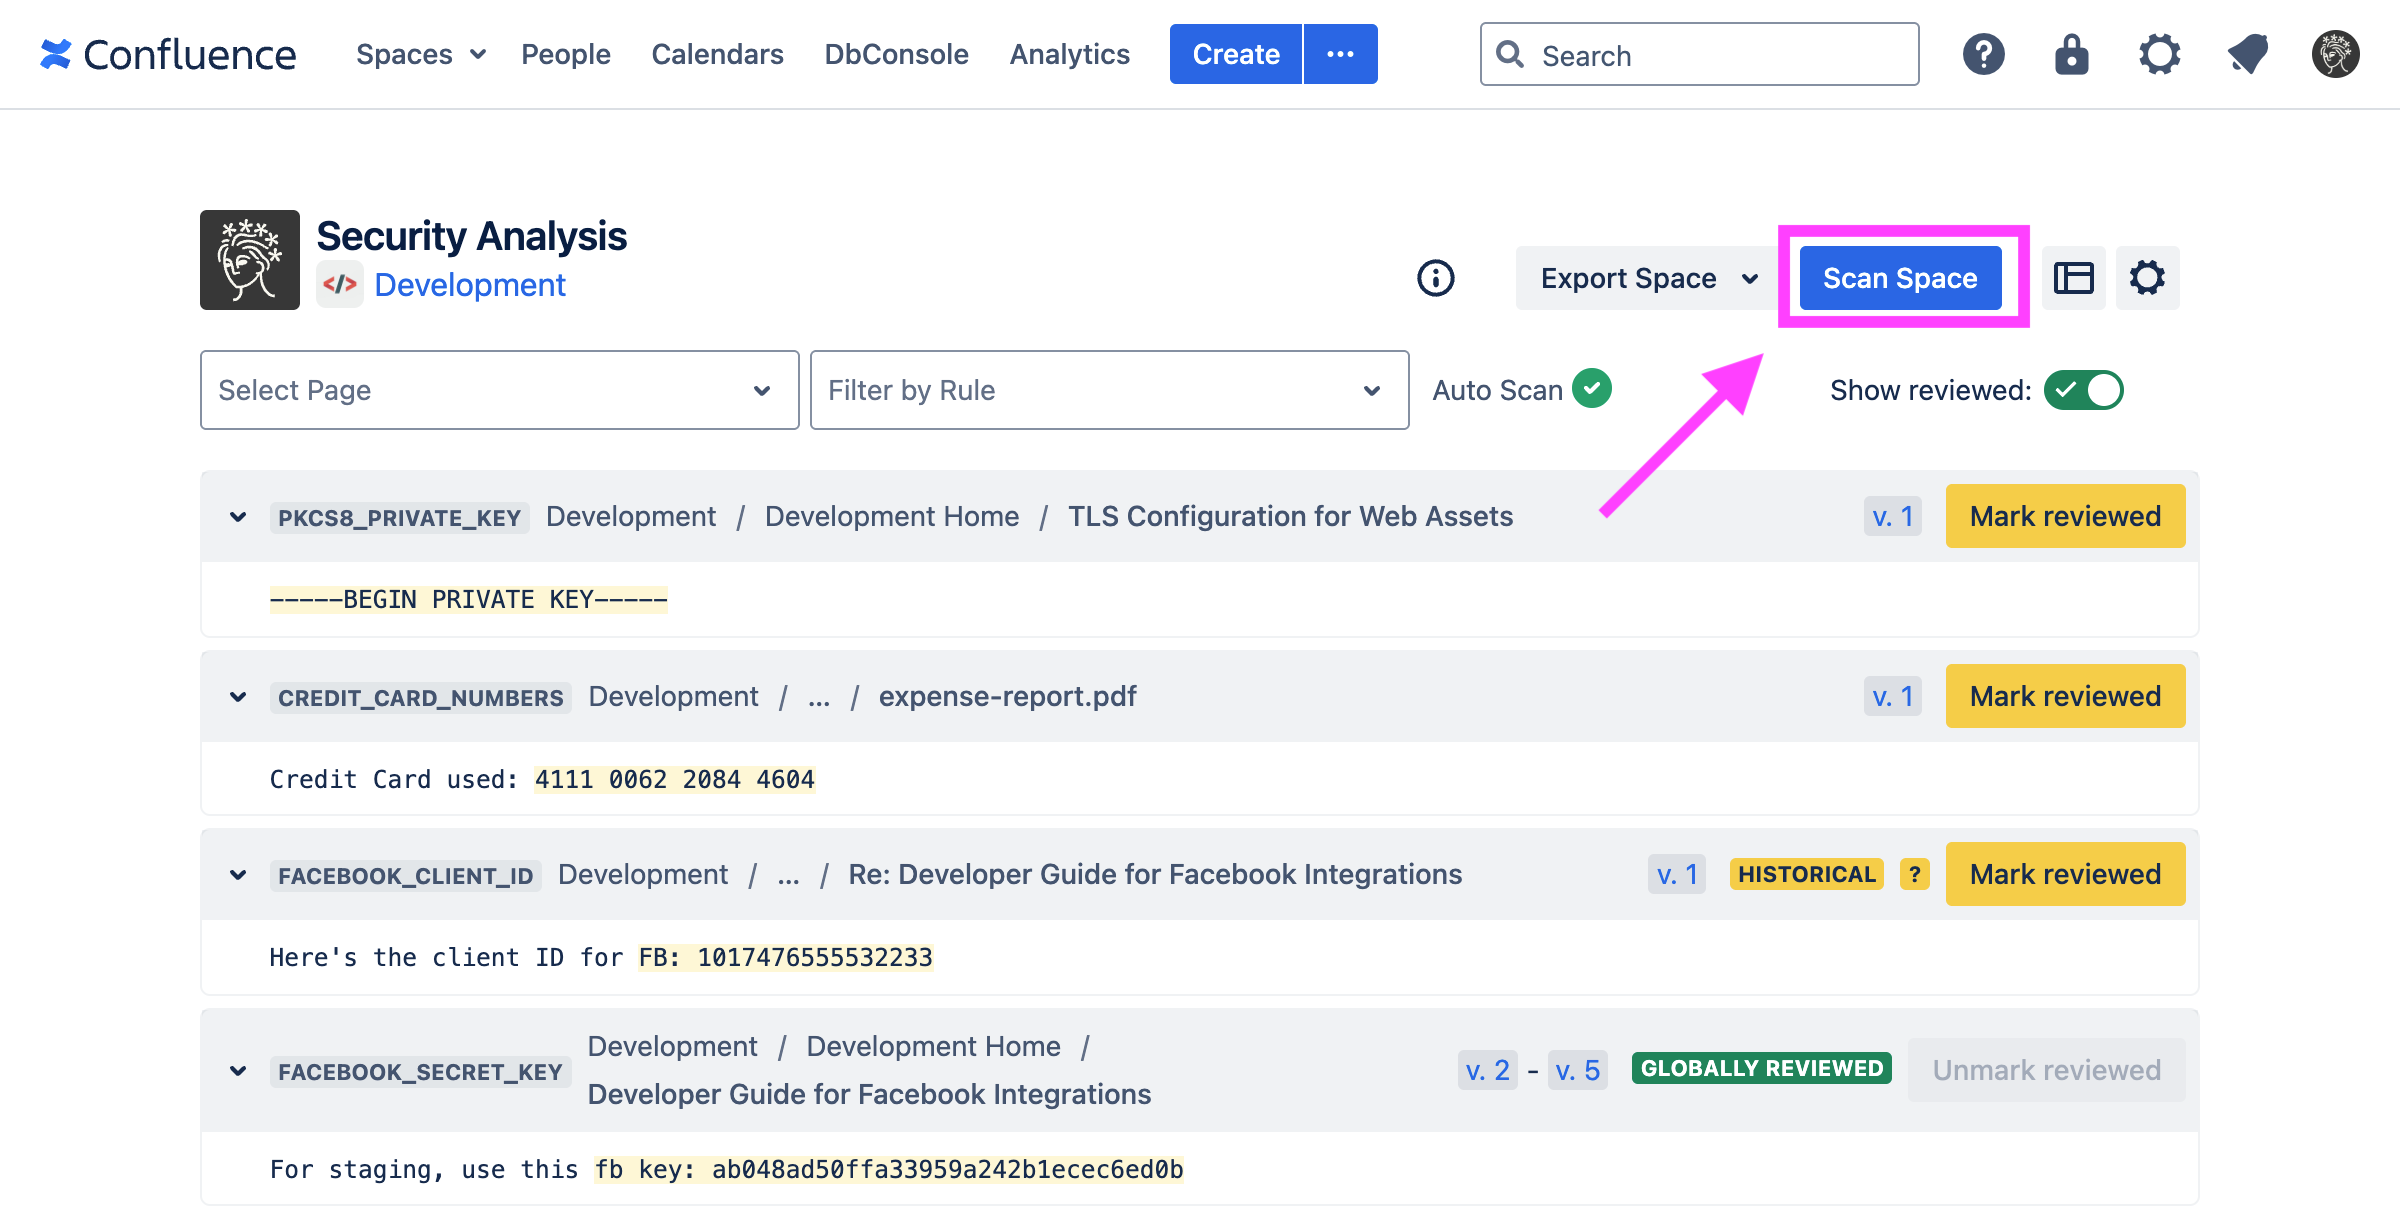
[Learn more about the Security Analysis page](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md).
## What can Security for Confluence Scan?
| **Content** | **Scanned** |
|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------|
| Page bodies |  |
| Blog posts |  |
| Attachments - See [Scanning Files Attached to Pages](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-files-attached-to-pages.md) for more information on supported file types. |  |
| Comments on pages, blog posts, and attachments |  |
| Drafts |  |
## Supported secrets and keys
Here is the list of vulnerabilities that are currently detected by [Soteri](https://marketplace.atlassian.com/vendors/1219549/soteri)'s built-in scanning rules.
## IT Services
| **Rule Name** | **Description** |
|------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| `AWS_CLIENT_ID` | [**AWS Identity and Access Management Client IDs**](https://docs.aws.amazon.com/IAM/latest/UserGuide/reference_identifiers.html#identifiers-unique-ids)uniquely reference users, access keys. These unique IDs can provide access to your AWS instance by allowing users to get keys. |
| `AWS_MWS_KEY` | [**AWS Marketplace Web Service API Keys**](https://docs.developer.amazonservices.com/en_US/dev_guide/DG_Registering.html)allow programmatic interfaces to Amazon Seller stores. |
| `AWS_SECRET_ACCESS_KEY` | [**AWS Secret Access Keys**](https://aws.amazon.com/blogs/security/wheres-my-secret-access-key/)allow for authenticated AWS CLI, SDK, and API access. |
| `AZURE_ACCESS_KEY` | [**Azure Access Keys**](https://docs.microsoft.com/en-us/azure/storage/common/storage-account-keys-manage?tabs=azure-portal)provide access to all data stored in Microsoft Azure. |
| `DYNATRACE_CLIENT_SECRET` | [**Dynatrace Client Secrets**](https://www.dynatrace.com/support/help/dynatrace-api/basics/dynatrace-api-authentication/)allow for access to your Dynatrace instance API. |
| `EC_PRIVATE_KEY` | **Elliptical Curve Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `FACEBOOK_CLIENT_ID` | **Facebook Application IDs** |
| `FACEBOOK_SECRET_KEY` | **Facebook Application Secrets** |
| `GENERIC_API_KEY` | **Generic API Key -**Contains logic to detect generic API Keys. |
| `GENERIC_PASSWORD` | **Generic Passwords** - Contains logic to detect generic passwords. *Note that this rule may generate many false positives, and is disabled by default.* |
| `GENERIC_SECRET` | **Generic Secrets** - Contains logic to detect generic secrets. |
| `GITHUB_KEY` | **Github Authentication Tokens** - This rule detects classic Github Authentication Tokens for [personal use](https://docs.github.com/en/github/authenticating-to-github/keeping-your-account-and-data-secure/creating-a-personal-access-token) (both "[classic](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-personal-access-token-classic)" and "[fine-grained](https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token#creating-a-fine-grained-personal-access-token)"), as well as for Github Application OAuth. |
| `GOOGLE_API_KEY` | **Google API Keys** |
| `GOOGLE_OAUTH` | **Google OAuth URLs** |
| `GOOGLE_OAUTH_ACCESS_TOKEN` | **Google OAuth Tokens** |
| `HEROKU_API_KEY` | **Heroku API Keys** |
| `LINKEDIN_CLIENT_ID` | **LinkedIn Client IDs** |
| `LINKEDIN_CLIENT_SECRET` | **LinkedIn Client Secrets** |
| `MAILCHIMP_API_KEY` | **Mailchimp API Key** |
| `MAILGUN_API_KEY` | **Mailgun API Key** |
| `PASSWORD_IN_URL` | **Generic Password in URL**- Contains logic to detect passwords embedded in URLs |
| `PAYPAL_BRAINTREE_ACCESS_TOKEN` | [**Paypal's Braintree Access Token**](https://developer.paypal.com/braintree/docs/guides/authorization/tokenization-key) |
| `PGP_PRIVATE_KEY` | [**PGP**](https://en.wikipedia.org/wiki/Pretty_Good_Privacy)**Private Keys** |
| `PKCS8_PRIVATE_KEY` | **PKSC8 Private Keys** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `PYPI_UPLOAD_TOKEN` | [**Python Package Index (PyPI) Upload Tokens**](https://pypi.org/help/#apitoken)allow verified publishing of python package to the global repository. |
| `RSA_PRIVATE_KEY` | We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SENDGRID_API_KEY` | [**Sendgrid API Keys**](https://docs.sendgrid.com/api-reference/api-keys/create-api-keys) |
| `SHOPIFY_PARTNER_API_ACCESS_TOKEN` | [**Shopify Partner API access Tokens**](https://shopify.dev/api/partner/getting-started)provide access to the a given store's API. |
| `SHOPIFY_SECRETS` | [**Shopify API Secrets**](https://shopify.dev/api/partner/getting-started) give access to all aspects of the general Shopify API -- this rule contains logic to detect Shared Secrets and Access Tokens for regular, Custom, and Private applications. |
| `SLACK` | [**Slack API Tokens**](https://api.slack.com/authentication/token-types) give access to various API features. |
| `SLACK_WEBHOOK` | [**Slack Webhooks**](https://api.slack.com/messaging/webhooks)are secret URLs which give similar access as API Tokens. |
| `SQUARE_ACCESS_TOKEN` | **Square Access Tokens** |
| `SQUARE_OAUTH_SECRET` | **Square OAuth Secrets** |
| `SSH_PRIVATE_KEY` | **Generic SSH Private Key** - We detect many common [SSH Private Key formats](https://www.atlassian.com/git/tutorials/git-ssh). |
| `SSH_PUBLIC_KEY` | **Public Key** -half of key-based authentication. Weak public keys can be brute-force cracked by modern computers, and can represent equal vulnerability to the private-key half of the pair. *Since properly-generated public keys are not a threat, this rule is disabled by default.* |
| `TROJAN_SOURCE` | **Trojan Source** detects left-to-right and right-to-left unicode control characters which can be used to obscure malicious code. For more information, see the [Trojan Source paper](https://www.trojansource.codes/trojan-source.pdf) and [CVE-2021-42574 in the NIST Database](https://nvd.nist.gov/vuln/detail/CVE-2021-42574). *Note:* the homoglyph attack described in this paper, and tracked as CVE-2021-42694 in the NIST Database, is **not** detected by this rule, as it can generate a lot of false positives for non-English languages. See "[Mitigating Trojan Source Attacks](https://docs.soteri.io/security-for-bitbucket/latest/mitigating-trojan-source-attacks)" for Soteri's recommendations if you're interested in detecting potential homoglyph attacks. |
| `STRIPE_API_KEY` | **Stripe API Key** |
| `TWILIO_ACCOUNT_ID` | **Twilio Account ID** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWILIO_API_KEY` | **Twilio API Key** - part of the [Twilio API](https://www.twilio.com/docs/usage/api/keys) |
| `TWITTER_CLIENT_ID` | **Twitter Client ID** |
| `TWITTER_SECRET_KEY` | **Twitter Secret Key** |
## Financial
| **Rule Name** | **Description** |
|---------------------------|-------------------------------------------------------------------------------------------------------------|
| `BANK_INFORMATION` | Detects bank account information like routing numbers, etc. which may accompany more sensitive information. |
| `CREDIT_CARD_NUMBERS` | Detects credit card numbers. |
| `SOCIAL_SECURITY_NUMBERS` | Detects United States Social Security Numbers. |
---
version: "latest"
language: "en"
---
# REST API For Scripting and Automation
Security for Confluence provides many REST API endpoints for a variety of tasks. Please contact [support](https://support.soteri.io/) if you need a particular endpoint which is not available.
## Getting started
### Authentication and basic parameters
Reference the [Confluence REST API](https://docs.atlassian.com/ConfluenceServer/rest/latest) for Confluence's built-in REST API, which is useful for getting lists of Spaces, content IDs in spaces, and so forth.
All requests use [basic HTTP authentication](https://en.wikipedia.org/wiki/Basic_access_authentication). It is natively supported by most clients, such as Python [requests](https://requests.readthedocs.io/en/latest/) and [curl](https://curl.se/).
All the URLs in the examples below are relative to the address of the Confluence instance - replace `{confluence-address}` with the address of your Confluence instance.
### Disabling XRSF checks
Some of these API calls will fail by default if called from a host that is not part of the Confluence instance. To enable calling these APIs remotely, you may add the following header as [documented here](https://confluence.atlassian.com/cloudkb/xsrf-check-failed-when-calling-cloud-apis-826874382.html):
Example (curl):
Bash
curl -u admin -H "X-Atlassian-Token: no-check" $URL
Example (Python):
Python
disable_xsrf_checks_header = {
"X-Atlassian-Token": "no-check"
}
requests.get(url, auth=(username, password), headers=disable_xsrf_checks_header)
## Running scans and getting results
Note that you must be a space administrator to run scans.
### Getting scan results for a space
Bash
curl -u admin "https://{confluence-address}/rest/security/latest/scan/space/{key}?reviewed={reviewed}&ruleIds={ruleIds}&page={page}&size={size}"
where
* `key` is the case-sensitive key for the space in question.
* `reviewed` is an optional parameter which can be used to filter the findings by if they're reviewed or not. If omitted, both reviewed and unreviewed findings are returned.
* `ruleIds` is an optional comma-separated list of rule IDs (e.g.: `ruleIds=AWS_SECRET_ACCESS_KEY,STRIPE_API_KEY,3`). Built-in rules are referred to by name (e.g.: `AWS_SECRET_ACCESS_KEY`), but custom rules have a numeric ID (e.g.: `3`). You can find rule IDs using the [REST API For Scripting and Automation \| Get a list of all scanning rules](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Get-a-list-of-all-scanning-rules) endpoint. If provided, only findings that match at least one of these rules will be returned.
* `page` is the 0-indexed page of findings results to fetch.
* `size` is an optional parameter to specify the number of results per page to fetch.
Confluence space keys are case-sensitive. You can verify the case of the space key on the space details page.
### Getting scan results for a page or blog post
Bash
curl -u admin "https://{confluence-address}/rest/security/latest/scan/content/{id}?createdWhen={createdWhen}&reviewed={reviewed}&ruleIds={ruleIds}&page={page}&size={size}"
where
* `id` is the content ID.
* `createdWhen` is an optional parameter specifying when the version of the page or blog post was created (e.g., `2021-08-15T17:54:36.860-05:00`).
* When specifying a version, only findings on the page or blog post will be returned, whereas omitting a version also gets findings on the page's attachments and comments.
* `reviewed` is an optional parameter which can be used to filter the findings by if they're reviewed or not. If omitted, both reviewed and unreviewed findings are returned.
* `ruleIds` is an optional comma-separated list of Rule IDs (e.g.: `ruleIds=AWS_SECRET_ACCESS_KEY,STRIPE_API_KEY,3`). Built-in rules are referred to by name (e.g.: `AWS_SECRET_ACCESS_KEY`), but custom rules have a numeric ID (e.g.: `3`). You can find rule IDs using the [REST API For Scripting and Automation \| Get a list of all scanning rules](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Get-a-list-of-all-scanning-rules) endpoint. If provided, only findings that match one of these rules will be returned.
* `page` is the 0-indexed page of findings results to fetch.
* `size` is an optional parameter to specify the number of results per page to fetch.
### Scanning all spaces
curl -u admin -X POST "https://{confluence-address}/rest/security/latest/scan/all
### Scanning a single space
curl -u admin -X POST "https://{confluence-address}/rest/security/latest/scan/space?key={key}"
where
* `key` is the case-sensitive key for the space in question.
### Scanning the full history of a piece of content
curl -u admin -X POST "https://{confluence-address}/rest/security/latest/scan/content?id={id}"
where
* `id` is the content ID.
### Scanning a single content version
curl -u admin -X POST "https://{confluence-address}/rest/security/latest/scan/content/version?id={id}&createdWhen={createdWhen}"
where
* `id` is the content ID.
* `createdWhen` is when the version of the content was created (e.g., `2021-08-15T17:54:36.860-05:00`).
### Cancel scheduled scans
You must be a Confluence administrator or a user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) to cancel scheduled scans.
Bash
curl -u admin -X DELETE "https://{confluence-address}/rest/security/latest/scan-queue/clear"
## Scanning rules
You must be a Confluence administrator or a user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) to view and modify scanning rules.
### Get a list of all scanning rules
This includes both built-in and custom rules.
curl -u admin "https://{confluence-address}/rest/security/latest/rules"
### Enable or disable a built-in scanning rule
curl -u admin -X PUT "https://{confluence-address}/rest/security/latest/rules/built-in/{name}?enabled={enabled}"
where
* `name` is the name of the rule in question (e.g., `AWS_CLIENT_ID` -- these rule names appear on the Settings page obtained via [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14663188495](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-and-disabling-global-scanning-rules.md)).
* `enabled` is the desired rule state, `true` or `false`.
### Create a new custom rule
curl -u admin -X POST "https://{confluence-address}/rest/security/latest/rules/custom" -H "Content-Type: application/json" --data '{"name":"rule name","regexp":"rule-regex","enabled":true}'
### Delete a custom rule
First, determine the ID of the custom rule by using the "Get a list of all scanning rules" endpoint above. Then,
curl -u admin -X DELETE "https://{confluence-address}/rest/security/latest/rules/custom/{rule-ID}"
## Reviewing findings
You must be able to edit content in a space in order to review findings. For more information, see [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14662664221](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md).
### Reviewing a finding for a space
curl -u admin -X POST -H "Content-Type: application/json" "https://{confluence-address}/rest/security/latest/review/space/{key}/create" --data '{"matchText":"$MATCH","ruleName":"$RULENAME"}'
where
* `key` is the case-sensitive key for the space in question.
* `$MATCH` is the exact string to be reviewed.
* `$RULENAME` is the name of the rule which generated this finding.
### Reviewing a finding for a page, attachment, or comment
curl -u admin -X POST -H "Content-Type: application/json" "https://{confluence-address}/rest/security/latest/review/space/{key}/content/{id}/create" --data '{"matchText":"$MATCH","ruleName":"$RULENAME"}'
where
* `key` is the case-sensitive key for the space in question.
* `id` is the content ID for the page, attachment, or comment.
* `$MATCH` is the exact string to be reviewed.
* `$RULENAME` is the name of the rule which generated this finding.
### Un-reviewing a finding for a space
curl -u admin -X POST -H "Content-Type: application/json" "https://{confluence-address}/rest/security/latest/review/space/{key}/delete" --data '{"matchText":"$MATCH"}'
where
* `key` is the case-sensitive key for the space in question.
* `$MATCH` is the exact string to be un-reviewed.
### Un-reviewing a finding for a page, attachment, or comment
curl -u admin -X POST -H "Content-Type: application/json" "https://{confluence-address}/rest/security/latest/review/space/{key}/content/{id}/delete" --data '{"matchText":"$MATCH"}'
where
* `key` is the case-sensitive key for the space in question.
* `id` is the content ID for the page, attachment, or comment.
* `$MATCH` is the exact string to be un-reviewed.
### Deleting all reviewed findings for a space
You must be a space admin to use this endpoint.
curl -u admin -X DELETE "https://{confluence-address}/rest/security/latest/review/space/{key}?confirm=true"
where
* `key` is the case-sensitive key for the space in question.
* `confirm` must be `true` to complete the operation.
### Deleting all individually-reviewed findings for a page, attachment, or comment
You must be a space admin to use this endpoint.
curl -u admin -X DELETE "https://{confluence-address}/rest/security/latest/review/space/{key}/content/{id}?confirm=true"
where
* `key` is the case-sensitive key for the space in question.
* `id` is the content ID for the page, attachment, or comment.
* `confirm` must be `true` to complete the operation.
## Exporting
You can export scan findings or reviewed findings.
### Exporting Dashboard Overview
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/dashboard/export?name={name}&type={type}"
where
* `name` is an **optional** search filter query parameter for a particular space name.
* `type` is an **optional** filter for only particular space types. May be "all", "personal", or "global". Defaults to "all".
### Exporting All Findings
#### For a particular space
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/space/{key}/findings?deduplicate={deduplicate}&historical={historical}"
where
* `key` is the case-sensitive key for the space in question.
* `deduplicate` is an **optional** query parameter that will override the [global deduplication setting](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Deduplicatefindingsinexports) if provided.
* `historical` is an **optional** query parameter that when true, only exports findings in [historical](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md#Historical-Findings) versions - when false, only exports findings in latest versions. Omitting this parameter exports all findings.
#### For all spaces
Only spaces you can administer are included.
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/findings?deduplicate={deduplicate}&historical={historical}"
where
* `deduplicate` is an **optional** query parameter that will override the [global deduplication setting](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings#id-(latest)ExportingFindings-Deduplicatefindingsinexports) if provided.
* `historical` is an **optional** query parameter that when true, only exports findings in [historical](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md#Historical-Findings) versions - when false, only exports findings in latest versions. Omitting this parameter exports all findings.
### Exporting Reviewed False Positives
#### For a particular space
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/reviewed/space/{key}/findings"
where
* `key` is the case-sensitive key for the space in question.
#### For all spaces
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/reviewed/findings"
### Exporting Attachment Scan Information
#### For a particular space
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/attachments/space/{key}"
where
* `key` is the case-sensitive key for the space in question.
#### For all spaces
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/export/attachments"
### Cancel running exports
This API cancels all exports on all nodes. Canceled exports will return an error if they have not started returning data, or will end with an "Export cancelled" line if they have. You must be a Confluence administrator or a user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) to cancel exports.
curl -u admin -X PUT "https://{confluence-address}/rest/security/latest/export/stop"
## Global reviewed false positives
Globally reviewed false positives can be managed by Confluence administrators or those those with[explicit access given through the plugins settings page](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md).
### Uploading new globally reviewed false positives
This endpoint accepts CSV uploads in a format described on [Hiding false positives, revoked credentials, etc.](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md) .
curl -u admin -F file=@'{filename}' "https://{confluence-address}/rest/security/latest/global-reviewed/create"
where
* `confluence-address` is the URL of your Confluence server.
* `filename` is the CSV you want to upload.
#### Deleting globally reviewed false positives
This endpoint accepts CSV uploads in a format described on [Hiding false positives, revoked credentials, etc.](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md) .
curl -u admin -F file=@'{filename}' "https://{confluence-address}/rest/security/latest/global-reviewed/delete"
where
* `confluence-address` is the URL of your Confluence server.
* `filename` is the CSV you want to upload.
#### Deleting all globally reviewed false positives
curl -u admin -X DELETE "https://{confluence-address}/rest/security/latest/global-reviewed?confirm=true"
where
* `confluence-address` is the URL of your Confluence server.
* `confirm` must be set to true to complete the operation.
## Viewing and Changing Settings
You can view and change settings as an admin via the API.
### Viewing Settings
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/settings"
### Changing Settings
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/settings?autoScan={bool}&emailForNewFindings={bool}&customEmailText={text}&scanAttachments={bool}¶llelScans={int}&logLevelOverride={level}&includePlaintextInExports={bool}&deduplicateExports={bool}&maxRuleTimeout={int}" -XPUT
You may provide the query parameters for the specific settings you want to change; any settings not included will not be changed.
#### Available Parameters for Settings
* `autoScan` (`true` or `false`) - Whether to keep space scans up to date. Equivalent to the `Keep space scans up to date` setting switch, as described in the [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14686257183](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md) page.
* `emailForNewFindings` (`true` or `false`) - Whether to email authors who publish sensitive content. Equivalent to the `Email authors when they publish potentially sensitive content` setting switch, as described in the [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14710177805](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md) page.
* `customEmailText` (text, [URL-encoded](https://developer.mozilla.org/en-US/docs/Glossary/Percent-encoding)) - The custom text to include in the email to authors who publish sensitive content. Equivalent to the `Customize emails` text entry box, as described in the [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14710177805](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md) page.
* `scanAttachments` (`true` or `false`) If attachment scanning is enabled, as described on [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/15039627270](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-files-attached-to-pages.md).
* `parallelScans` (an integer) -- Configure number of scans in parallel per node, as described in the [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14790492163](https://docs.soteri.io/security-for-confluence-dc/latest/scan-performance.md) page.
* `logLevelOverride` (one of `TRACE`, `DEBUG`, `INFO`, `WARN` (default), or `ERROR`) - Configure the system log to include messages at this level as **Warn** messages. The `Enable additional logging` sets this to `DEBUG` as described in the [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14663188524](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-debug-logging.md) page.
* `includePlaintextInExports` - When enabled, [exported findings](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) will contain the full text of the finding in the CSV output. When disabled, the CSV will contain a link to the report in its place. See: [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14662467640/Exporting+Findings#Redacting-findings-in-exported-reports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md#Redacting-findings-in-exported-reports).
* `deduplicateExports` - When enabled, [exported findings](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) with the exact same text are deduplicated across the history of a given page. This behavior presents an export similar to the layout of the [Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md) page. See: [https://soteri.atlassian.net/wiki/spaces/SFCDC/pages/14662467640/Exporting+Findings#Deduplicate-Findings-in-Exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md#Deduplicate-Findings-in-Exports).
* `maxRuleTimeout` (an integer) - Configure the number of seconds a single rule can run on a single line, as described in [Scan Performance](https://docs.soteri.io/security-for-confluence-dc/latest/scan-performance.md) . Setting the value to 0 uses the default value (20 seconds).
### Viewing the List of Users with Explicit Access
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/settings/entity-permissions"
### Modifying the List of Users with Explicit Access
The current explicit access list will be deleted and replaced with the new list when using this API.
curl -u admin -O -J "https://{confluence-address}/rest/security/latest/settings/entity-permissions" -XPUT --data-binary '[{ "type": "{USER or GROUP}", "idOrKey": "{user key or group name}"}]'
---
version: "latest"
language: "en"
---
# Scan Performance
## Viewing and changing parallel scans
Security for Confluence distributes scanning to every Confluence Data Center node, and **by default runs** **2** scans in parallel per node. This number can be configured in the UI or via the REST API. Scans beyond the number of scans run in parallel are stored in a queue. This queue is accessible to all Confluence nodes.
### Changing parallel scans via the UI
To change number of scans in parallel per node, visit the [Soteri Settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md). You can see a dropdown where you can choose number of parallel scans per node.
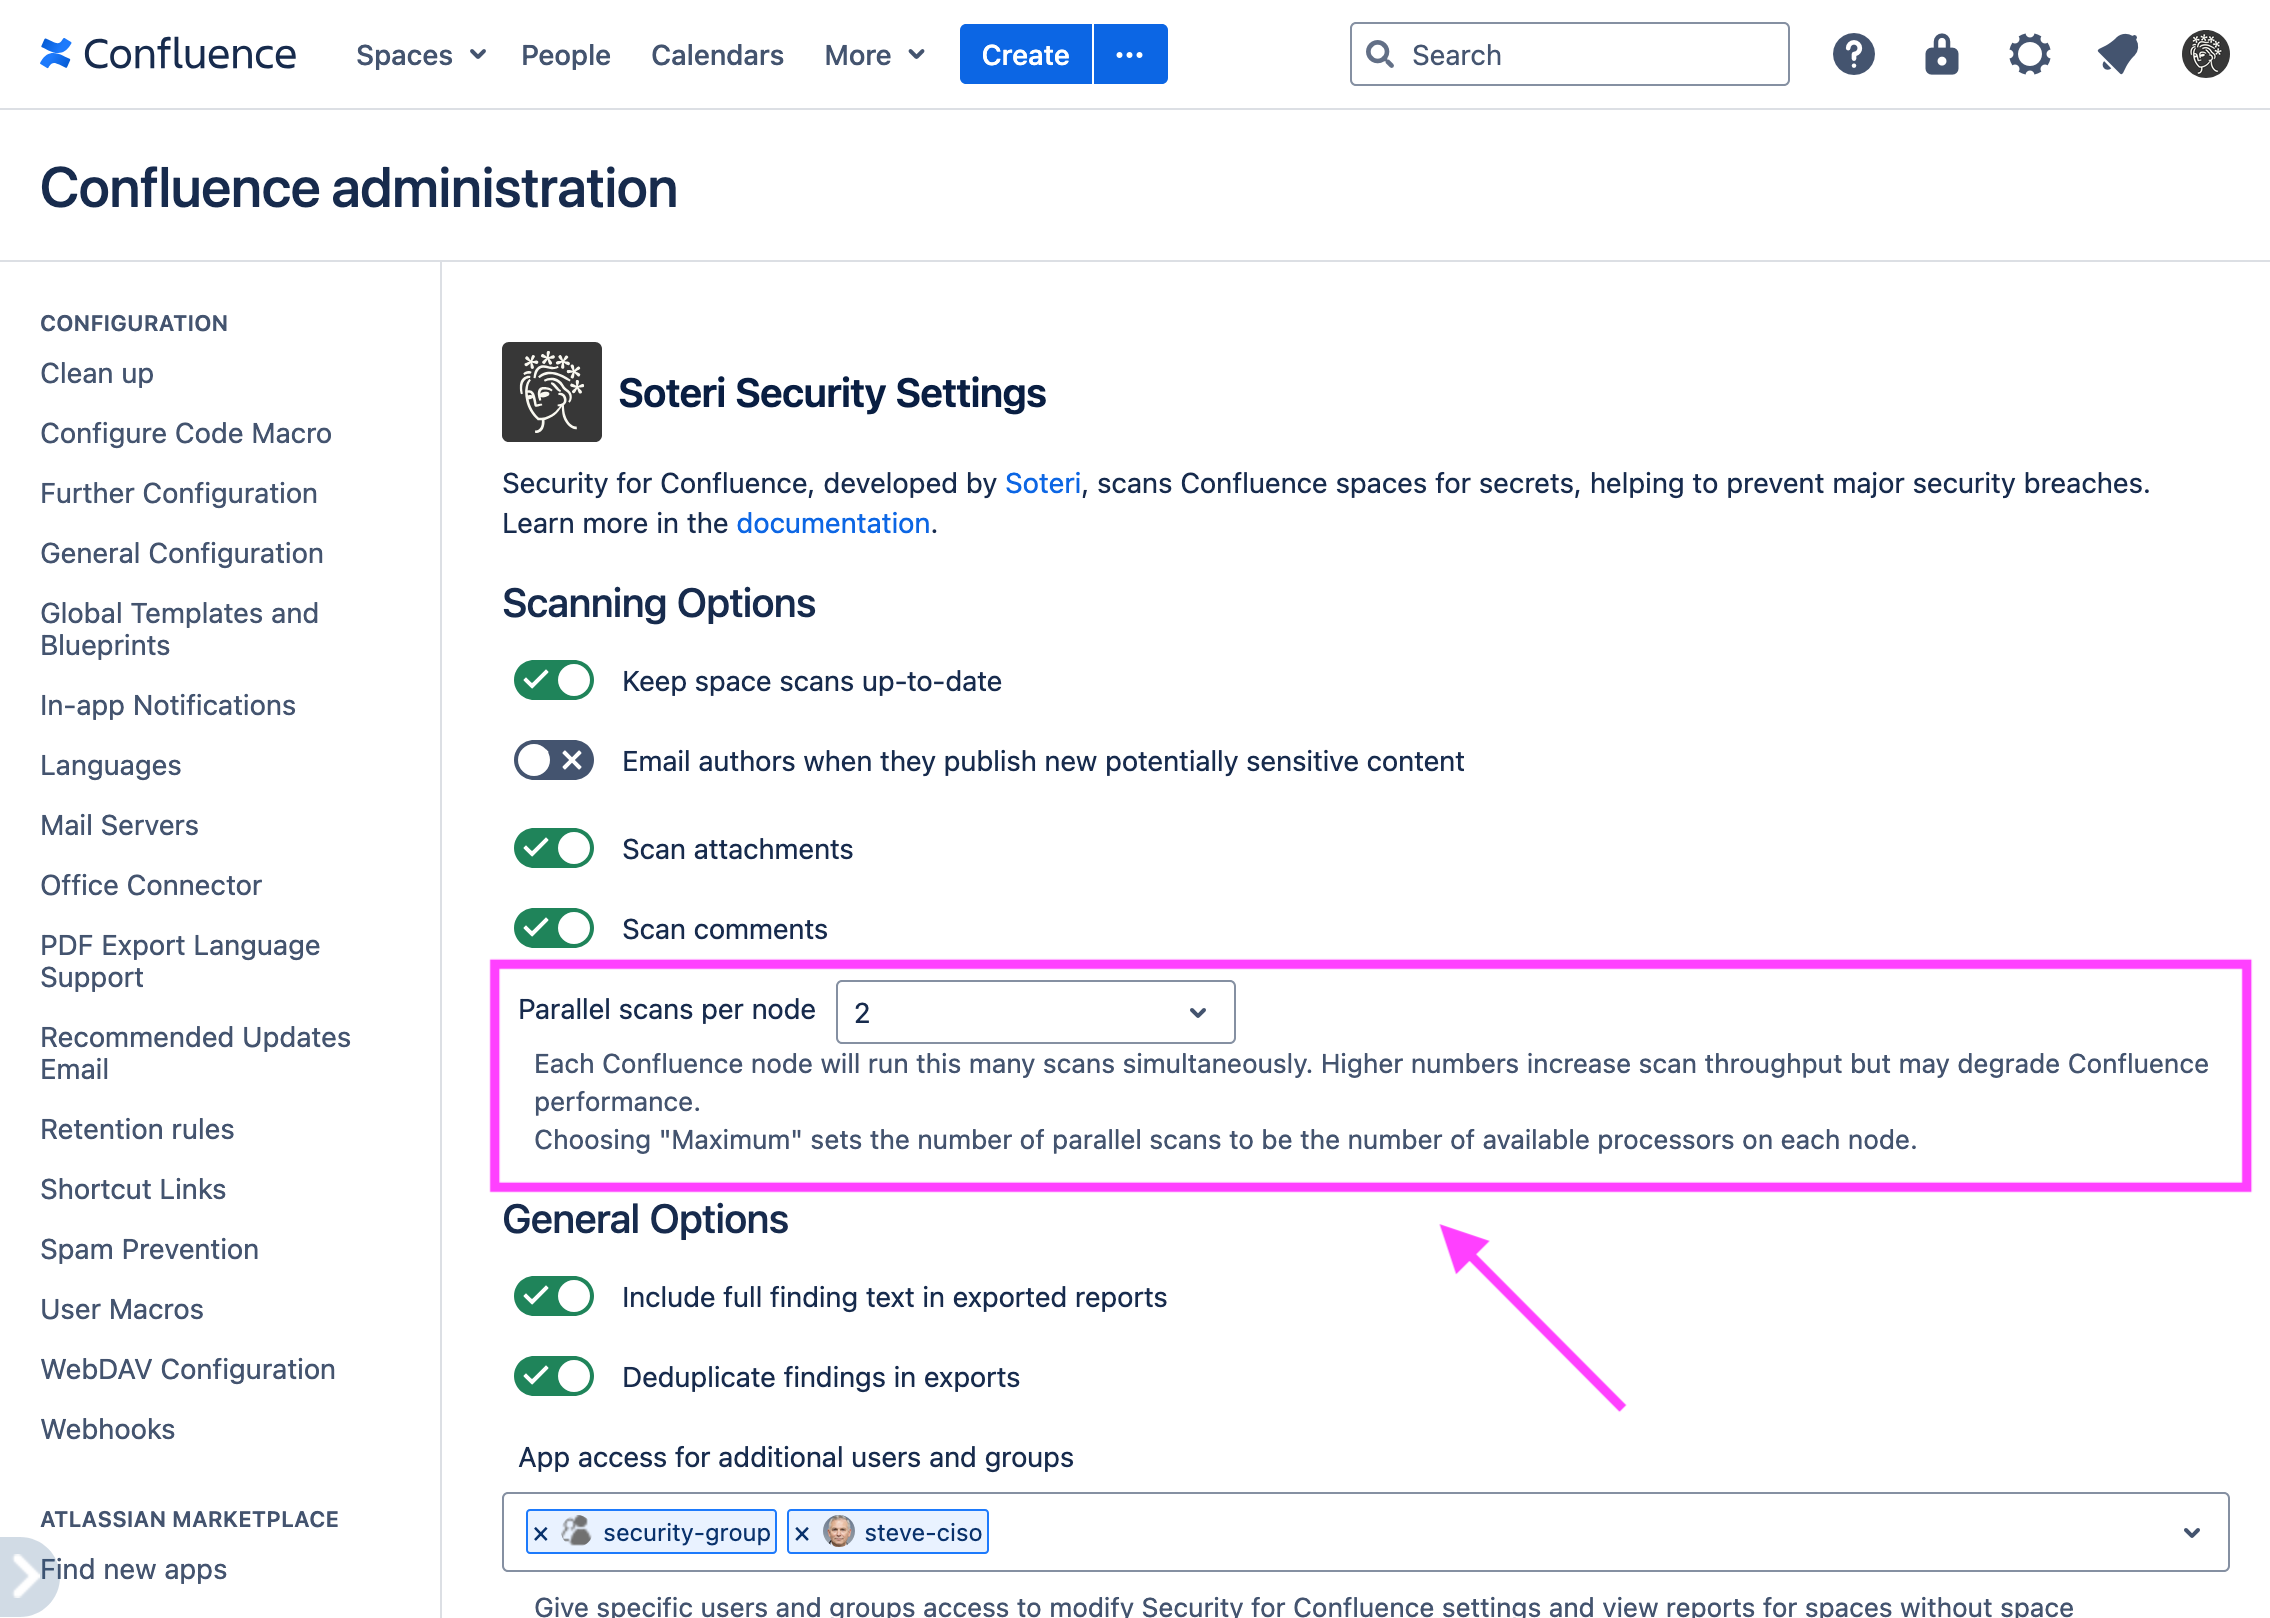
### Troubleshooting number of available processors
In certain situations, the number of processors detected by Security for Confluence might not match the number of processors actually available to the server. If you are running in a Docker deployment and believe you should have more processing power available, you should update your JVM flags as discussed in
### Changing parallel scans via the REST API
For information on REST API usage, see [REST API For Scripting and Automation \| Viewing and Changing Settings](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Viewing-and-Changing-Settings)
* This call returns a positive integer which is the configured number of parallel scans.
* To maximize scanning performance, you can specify the value `0` to use all available CPUs.
### Changing maximum rule timeout via the REST API
For information on REST API usage, see [REST API For Scripting and Automation](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md)
By default, Security for Confluence limits the time used to apply one rule to a line to 20 seconds. If your pages or attachments contain very long lines, you may want to increase this time.
The maximum timeout is used for lines which are 10MB or larger, while shorter lines will use proportionally less time. If the maximum is lower than the default (20s), it will be used for all lines; this may be useful for very resource constrained environments.
## Modifying which Confluence nodes run scans
If you have multiple Confluence Data Center nodes running, you can choose which ones run scans. This feature is currently only supported via the REST API.
### Name the nodes that should participate in scanning
Note that Confluence Data Center will not prevent you from naming nodes identically. If two nodes are named identically, and Security for Confluence is configured such that scans should run on that node name, then scans will run on **both** nodes.
Use Confluence's concept of naming cluster nodes to name the nodes you wish to participate in scanning. See the "Changing the node identifier" section in Atlassian's documentation on [Adding and removing Data Center nodes](https://confluence.atlassian.com/doc/adding-and-removing-data-center-nodes-659783919.html#AddingandRemovingDataCenterNodes-Changingthenodeidentifier).
### See and change which nodes are running scans
To see which nodes are participating in scanning:
Bash
curl -u admin -X GET https://{confluence.server}/rest/security/latest/cluster/scan-nodes
where
* `admin` is your Confluence admin user (you'll be prompted for a password), and
* `confluence.server` is the URL of your Confluence server.
This will return a JSON formatted response which looks like this:
JSON
{
"scanNodeNames": [],
"message": "Scan node configuration is empty. All nodes will participate in scanning"
}
To change which nodes run scans:
Bash
curl -u admin -X PUT https://{confluence.server}/rest/security/latest/cluster/scan-nodes -H "Content-Type: application/json" -d '{"scanNodeNames": [{scanNodeNames}]}'
where
* `admin` is your Confluence admin user (you'll be prompted for a password),
* `confluence.server` is the URL of your Confluence server, and
* `scanNodeNames` is a list of the node names you want to participate in scanning; e.g., `"confluence-scan-node1", "confluence-scan-node2"`.
To reset back to the default behavior, where all nodes participate in scanning, send a `DELETE` to the same endpoint:
curl -u admin -X DELETE https://{confluence.server}/rest/security/latest/cluster/scan-nodes
or, you can make `scanNodeNames` empty:
Bash
curl -u admin -X PUT https://{confluence.server}/rest/security/latest/cluster/scan-nodes -H "Content-Type: application/json" -d '{"scanNodeNames": []}'
Both have the same effect.
---
version: "latest"
language: "en"
---
# Scanning Comments
By default, Security for Confluence scans comments:
* Top-level comments (also known as footer comments) on pages and blog posts
* Inline comments on pages and blog posts
* Comments on attachments
If you've upgraded Security for Confluence from a version prior to **3.2.0** you will need to enable comment scanning by following the steps below.
## Enabling and disabling comment scanning
You can enable or disable comment scanning by [navigating to the settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md) and toggling the "Scan Comments" setting.
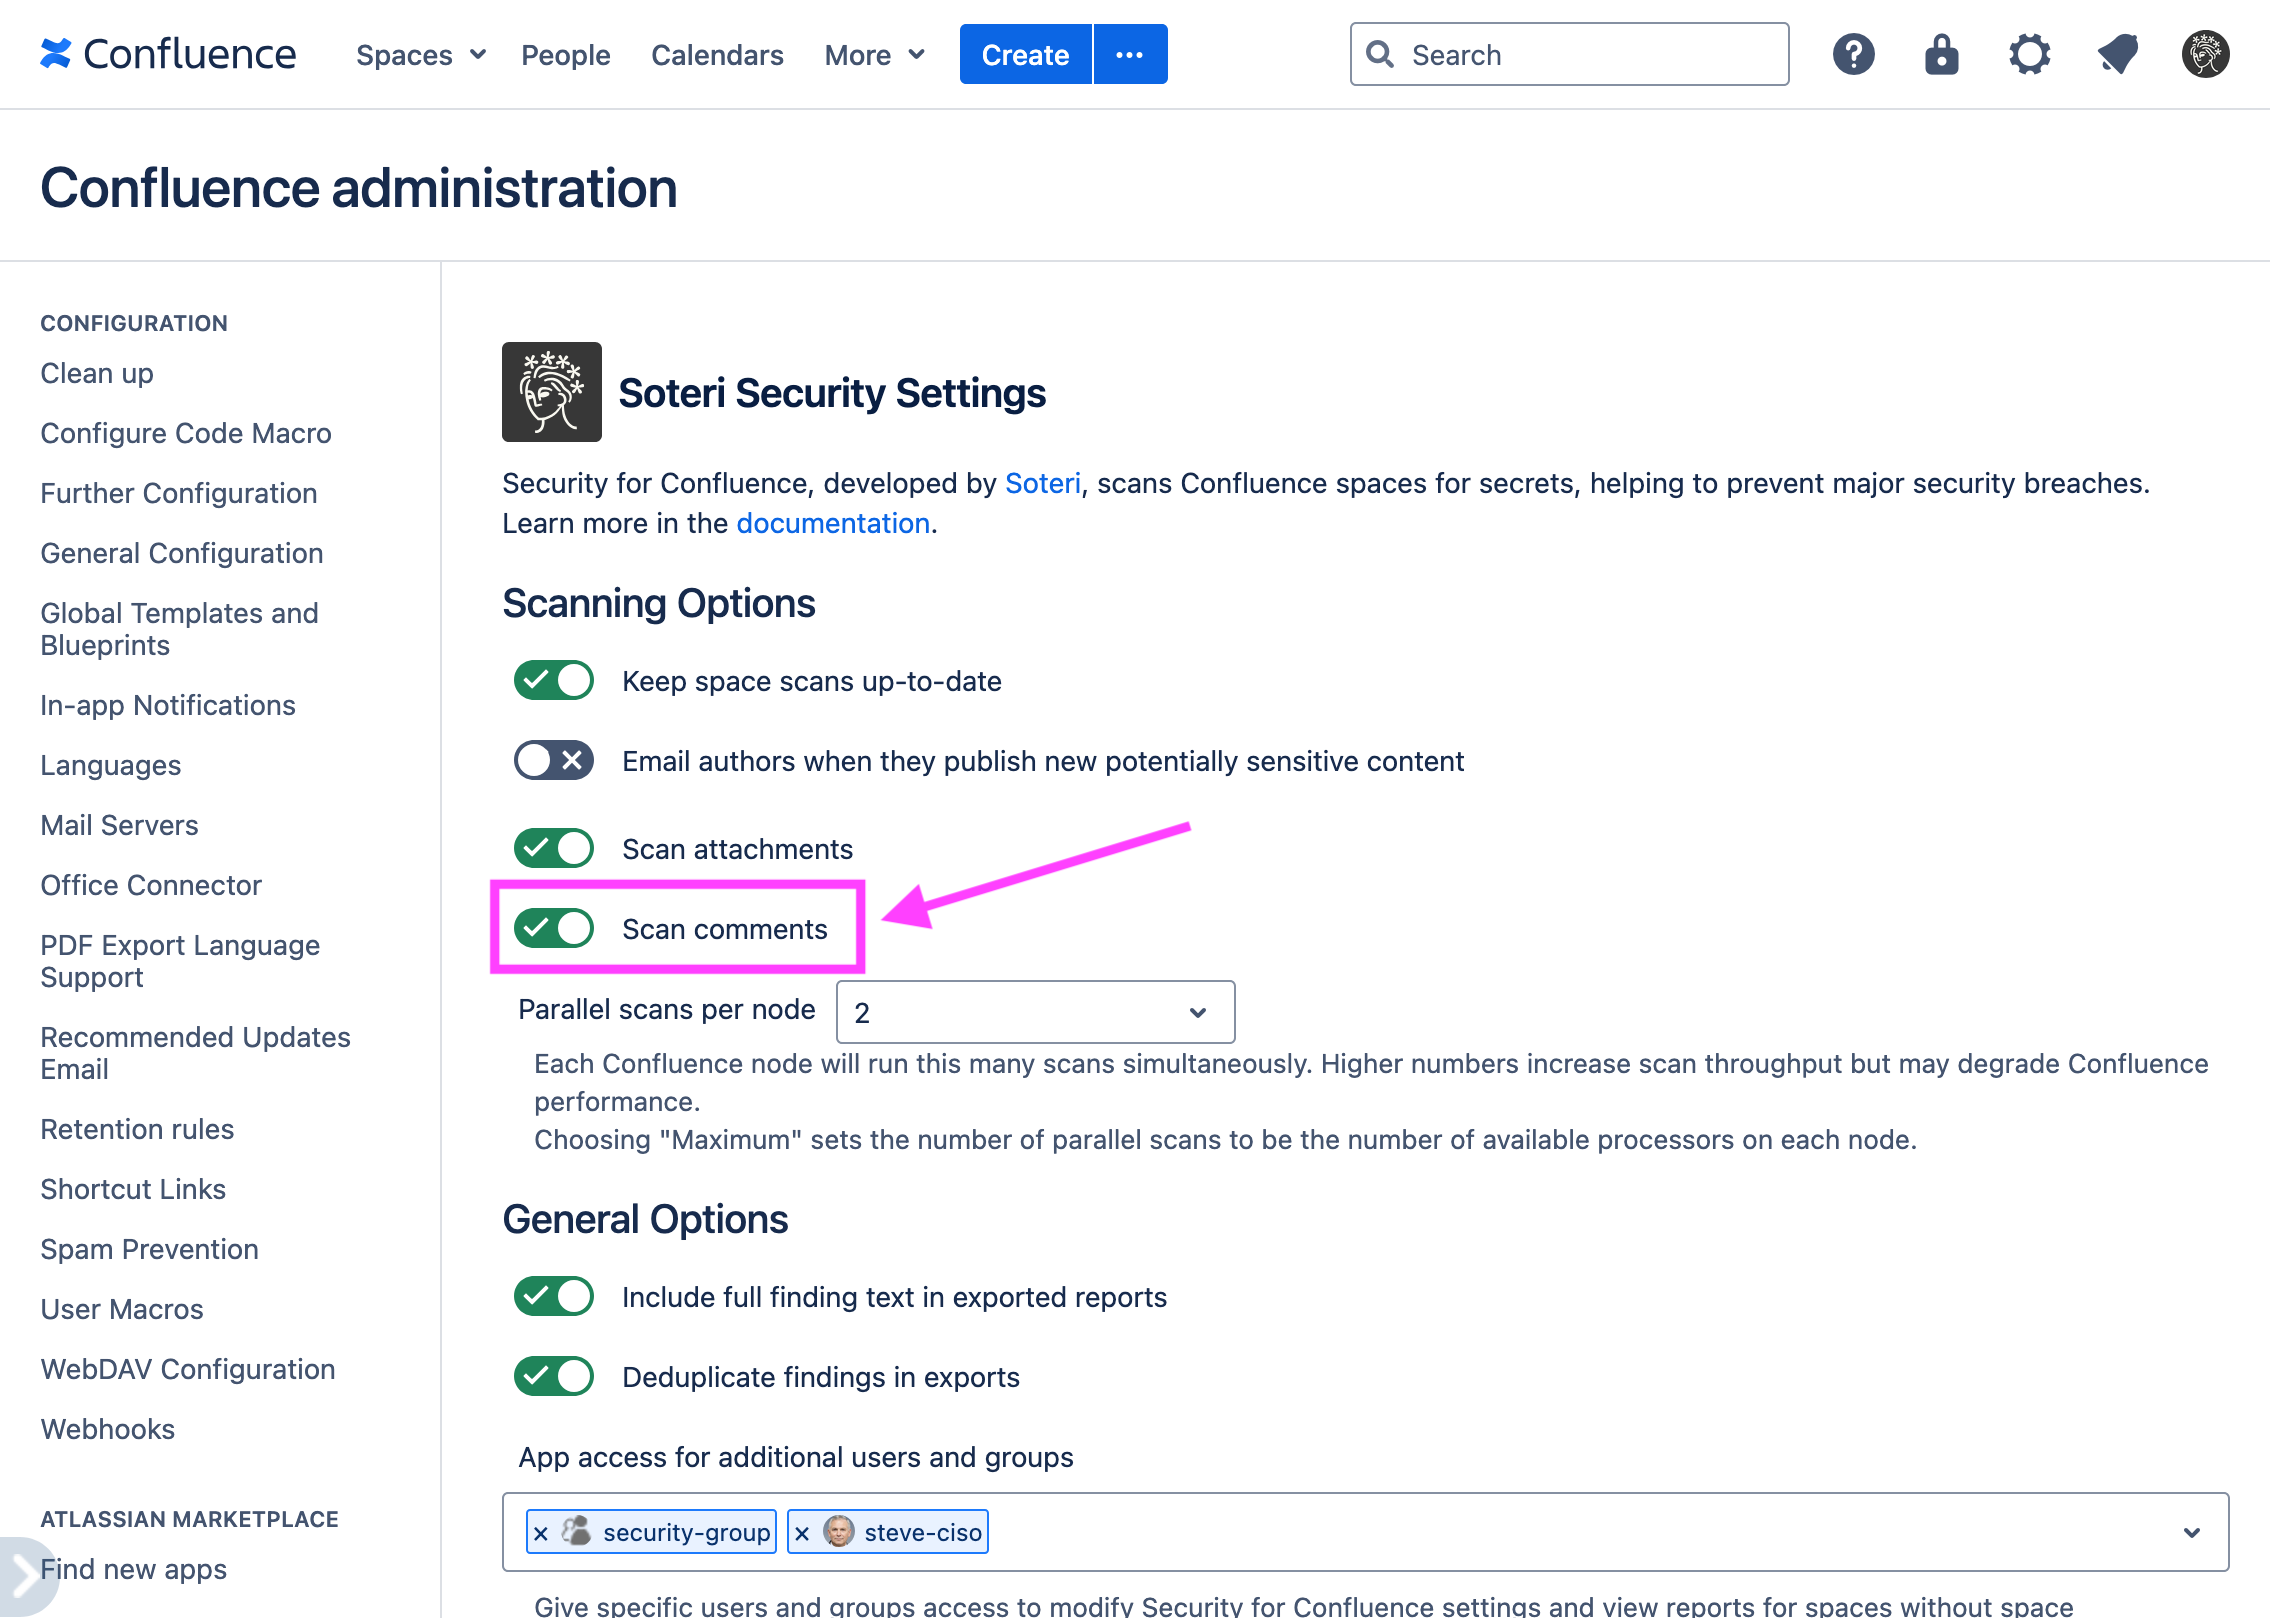
Changing the "Scan Comments" setting will cause existing scans to be considered to have outdated settings, which can be resolved by re-scanning.
## Removing secrets in comments
Confluence keeps previous versions of comments, and even though they are not viewable in the UI, they are still accessible via the REST API. Additionally, unlike pages, blog posts, and attachments, Confluence does not let you delete individual versions of comments. Thus, **the only way to fully remove a secret in a comment is to delete the entire comment**.
This can be confusing for scan findings in historical comment versions in particular, because the only link Security for Confluence can provide is to the *latest* version of the comment. Accordingly, in the [Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md), findings for historical versions of comments have an extra informational tooltip stating that findings in historical comment versions can only be removed by deleting the entire comment.
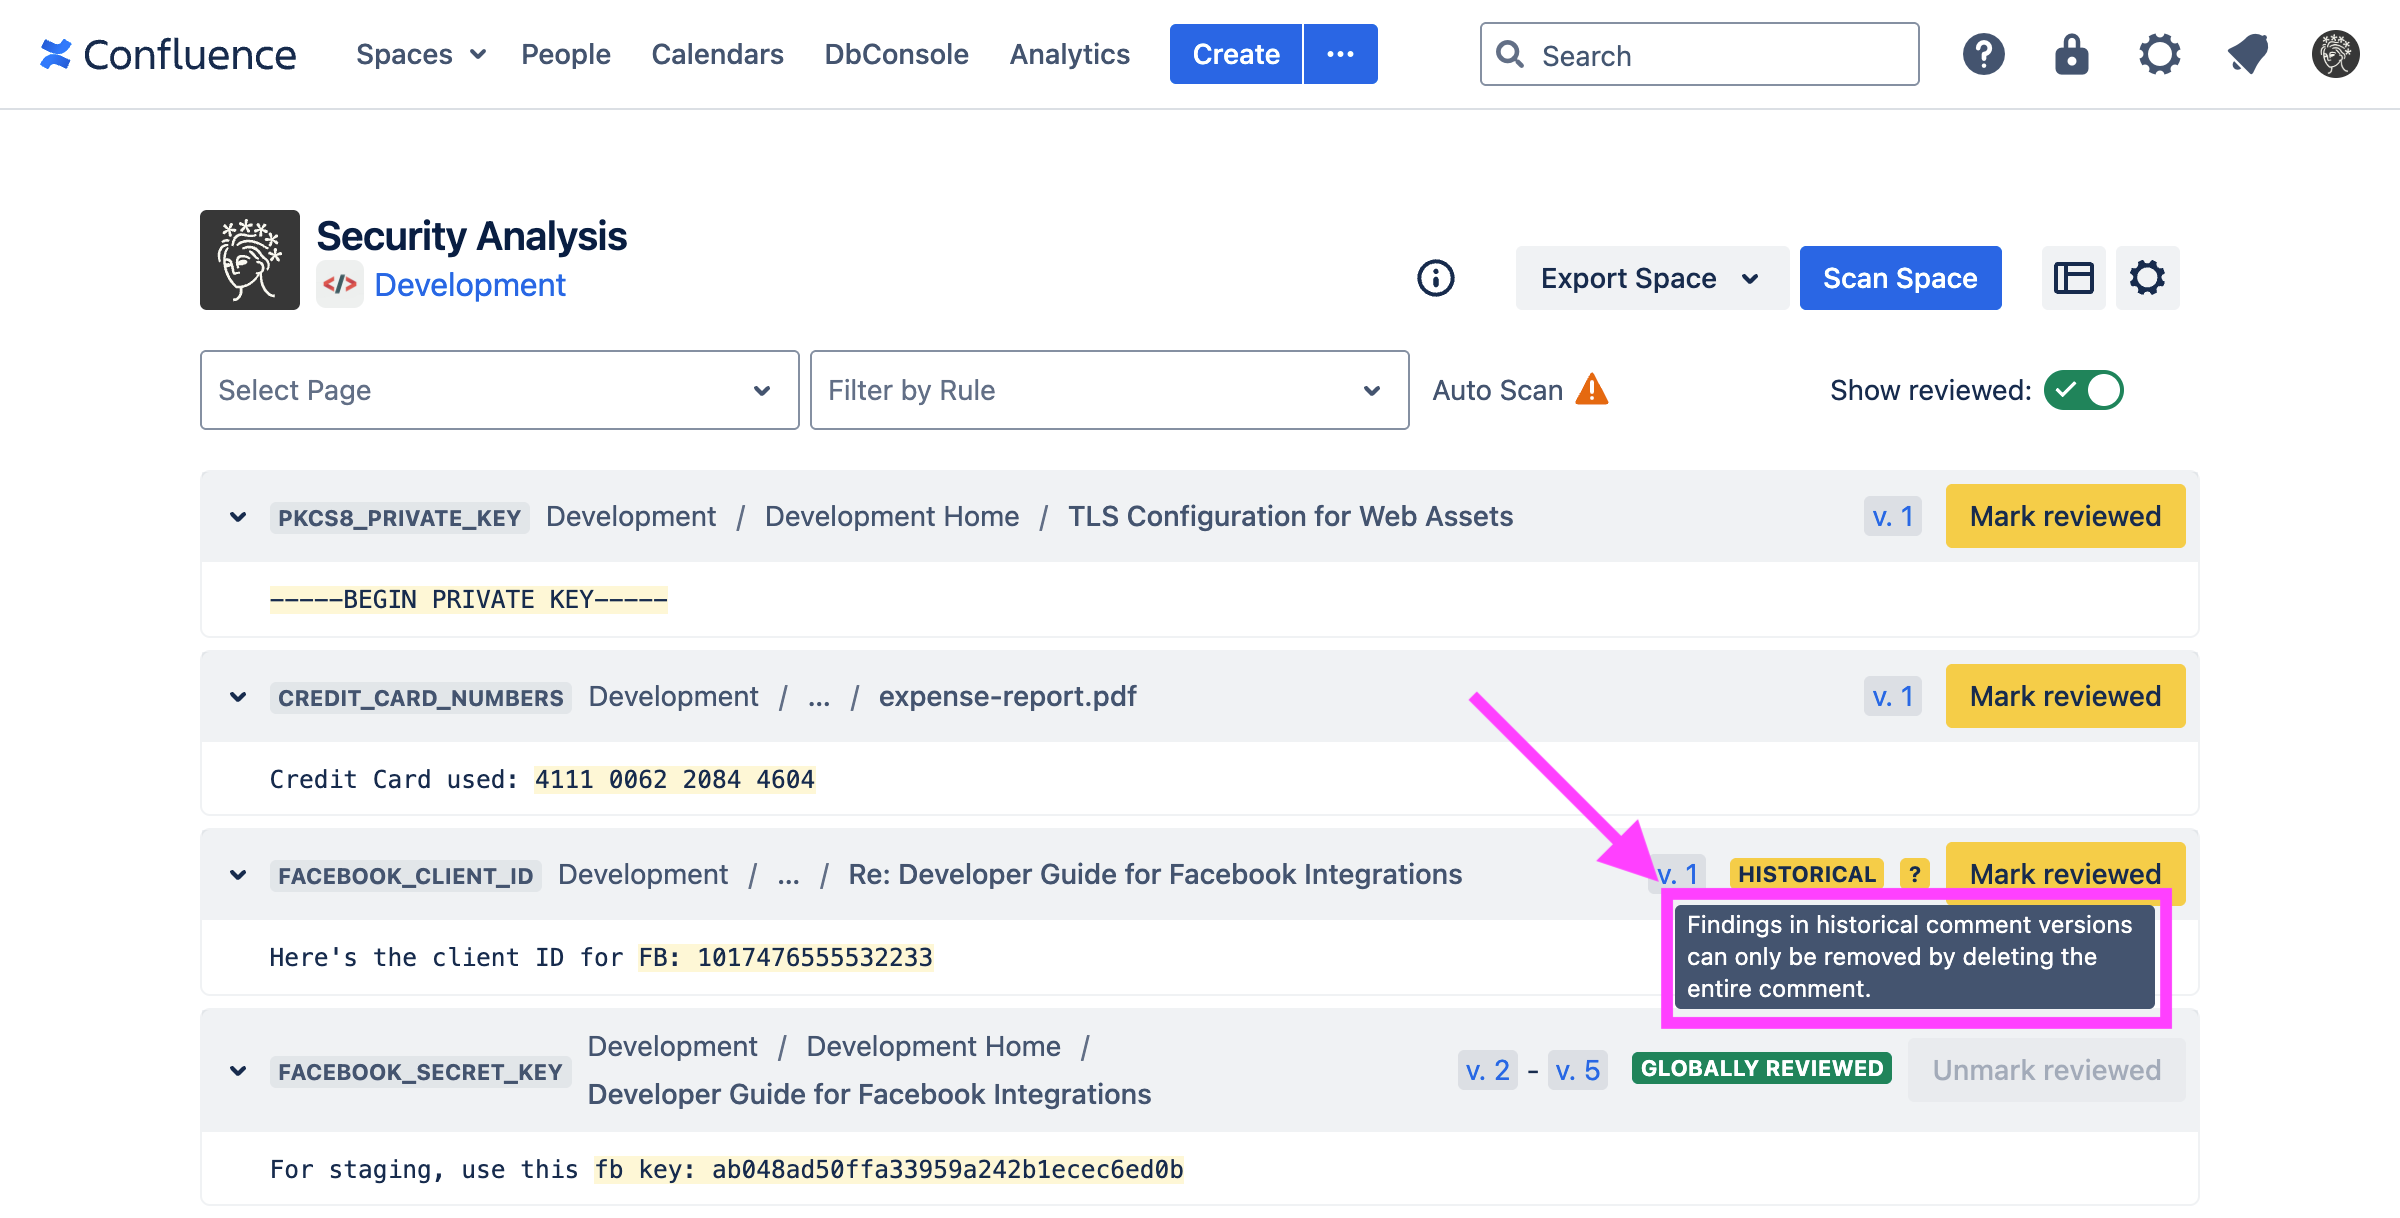
---
version: "latest"
language: "en"
---
# Security Analysis: Viewing scan results for a space
The Security Analysis for a given space allows administrators to view and handle scan findings for the space.
Only space administrators, Confluence administrators, or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md), can access a space's **Security Analysis**.
There are two ways to reach a space's Security Analysis. First, you can reach it from the [Soteri Dashboard](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md), by clicking the name of the space:
Or, while viewing the space in Confluence, you can click "Security Analysis" in the side panel:
The space's scan status and all findings in the space will be displayed. Findings with the same match text across multiple versions of a piece of content are *deduplicated* ---that is, when a finding appears in multiple content versions, the *range* of versions is shown.
For deduplicated findings, the first and last versions of the content that the finding appears in will be shown, even if the finding is not present in all intermediate versions.
Click on page version links to view the actual page and see who edited it and when. This is useful for tracking down users who published the finding.
You can select a page in the dropdown list to get the scan status and findings for a particular page, and you can also filter to a specific page version. When viewing results for a specific page version, similar findings are **not** deduplicated.
When a page version is selected, only scan findings in the text of that specific version are shown. Findings in attachments or comments on the page are **not** included.
Above, we see a few scan findings for a particular page version. The specific text that matched the listed rule's regex is highlighted. Specifically, this is the *group 0* match: what the entire expression captured. For more information, see the [Java 8 Regular Expression documentation](https://docs.oracle.com/javase/8/docs/api/java/util/regex/Pattern.html).
You can also filter the list to only show findings matching certain rules. Use the "Filter by Rule" field to search for rules to filter.
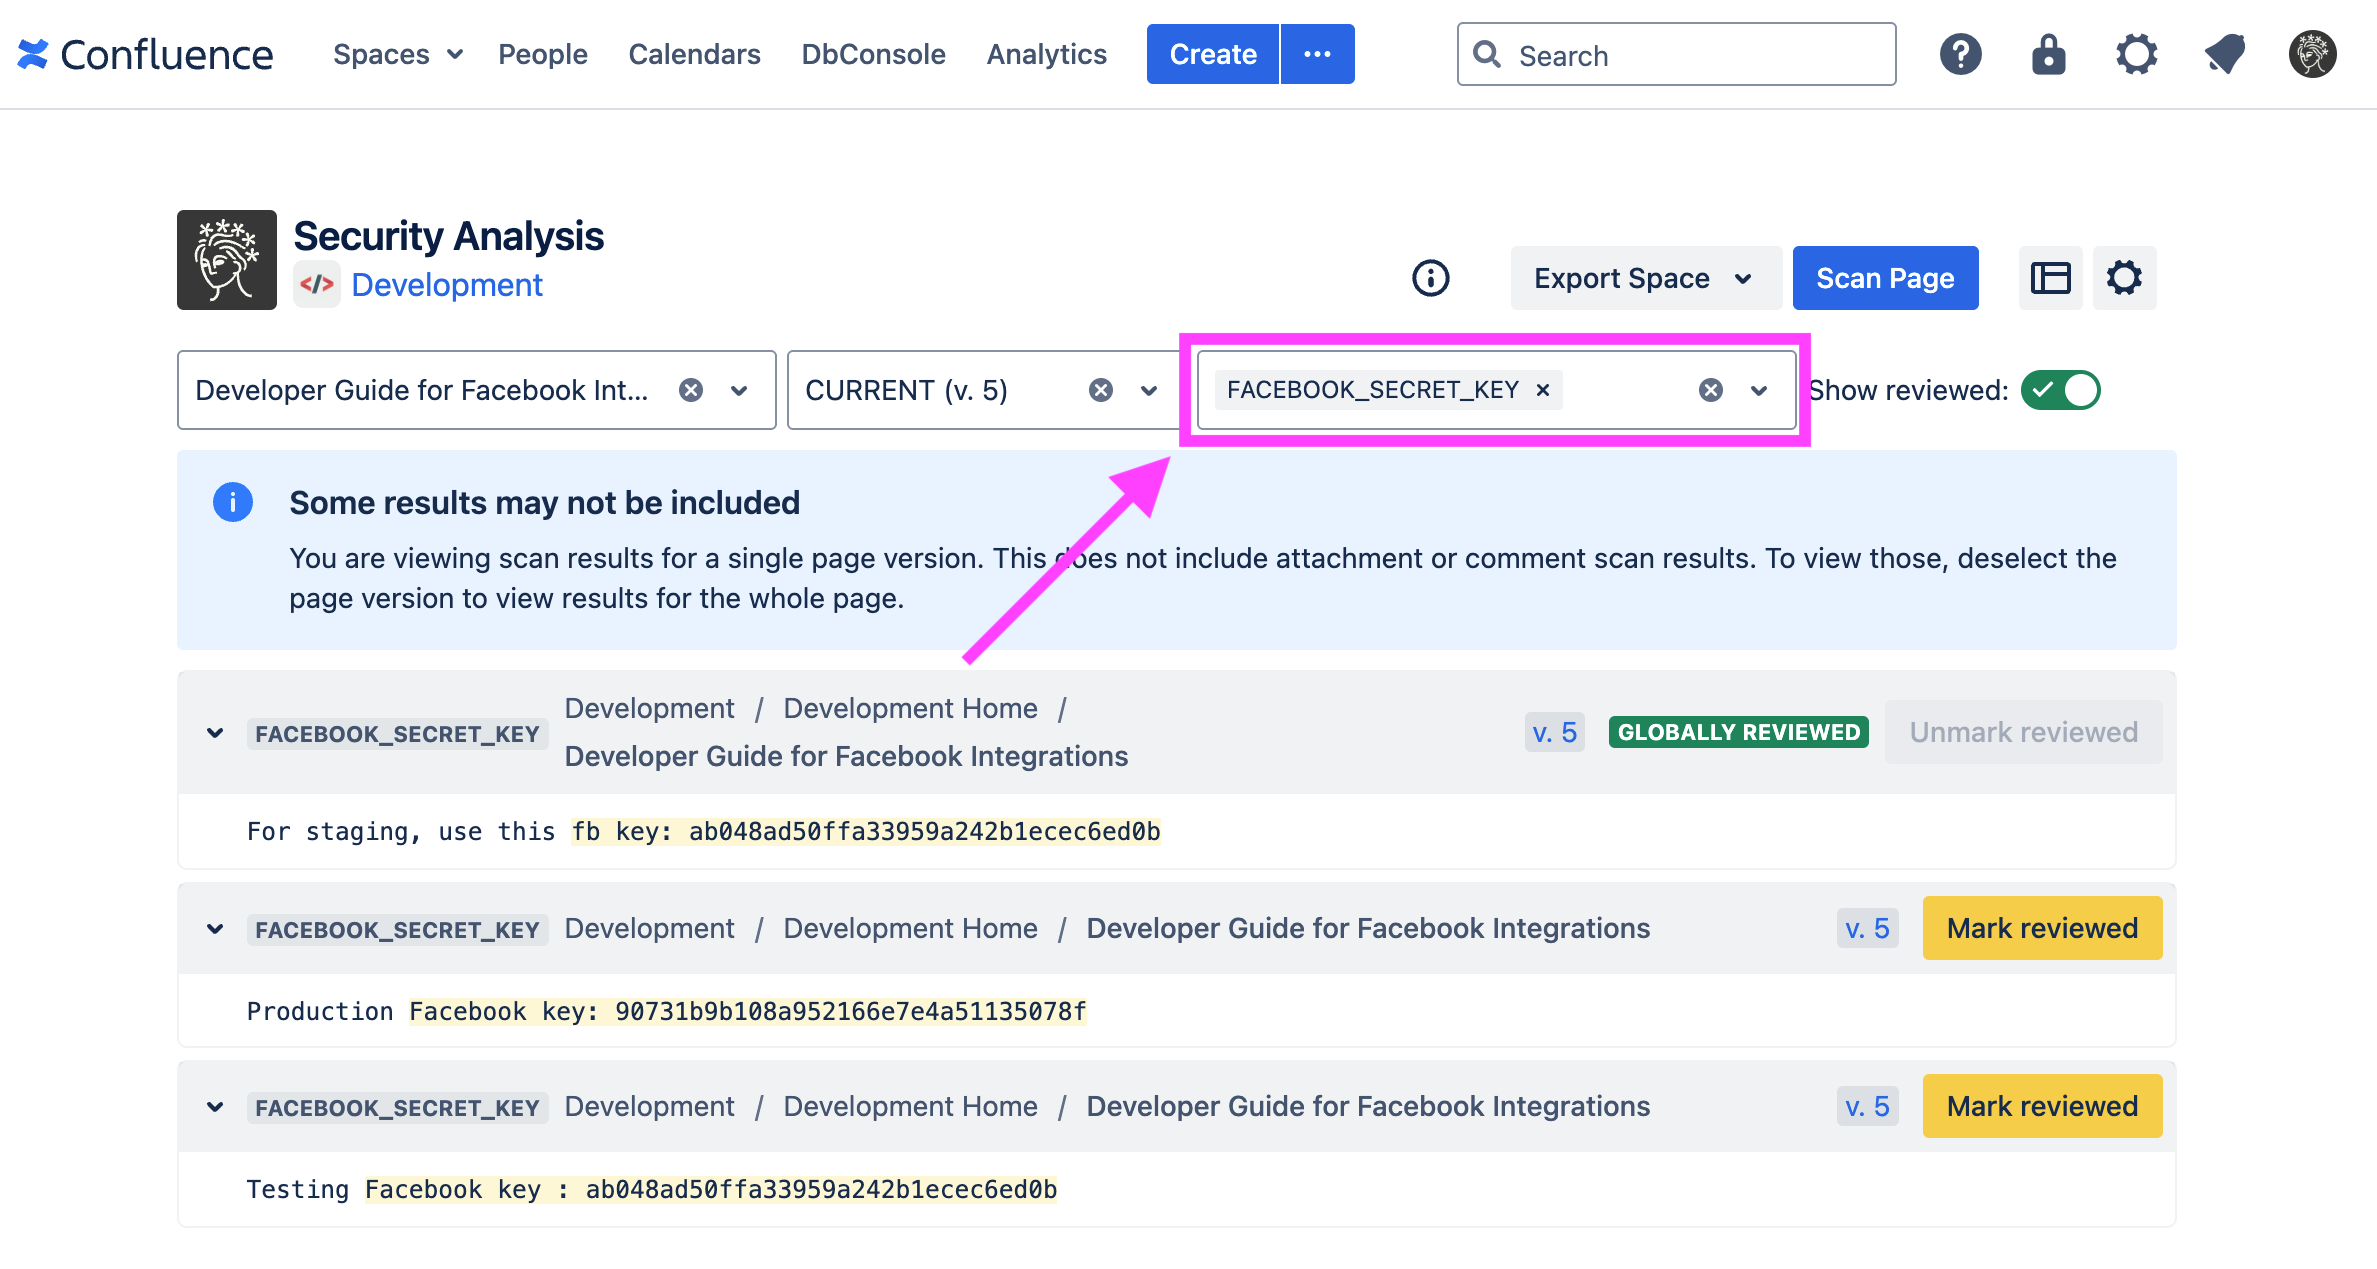
## Historical Findings
Scan findings that aren't present in the latest published version of a piece of content are considered 'historical'. Any such scan findings will appear as 'historical' the Security Analysis.
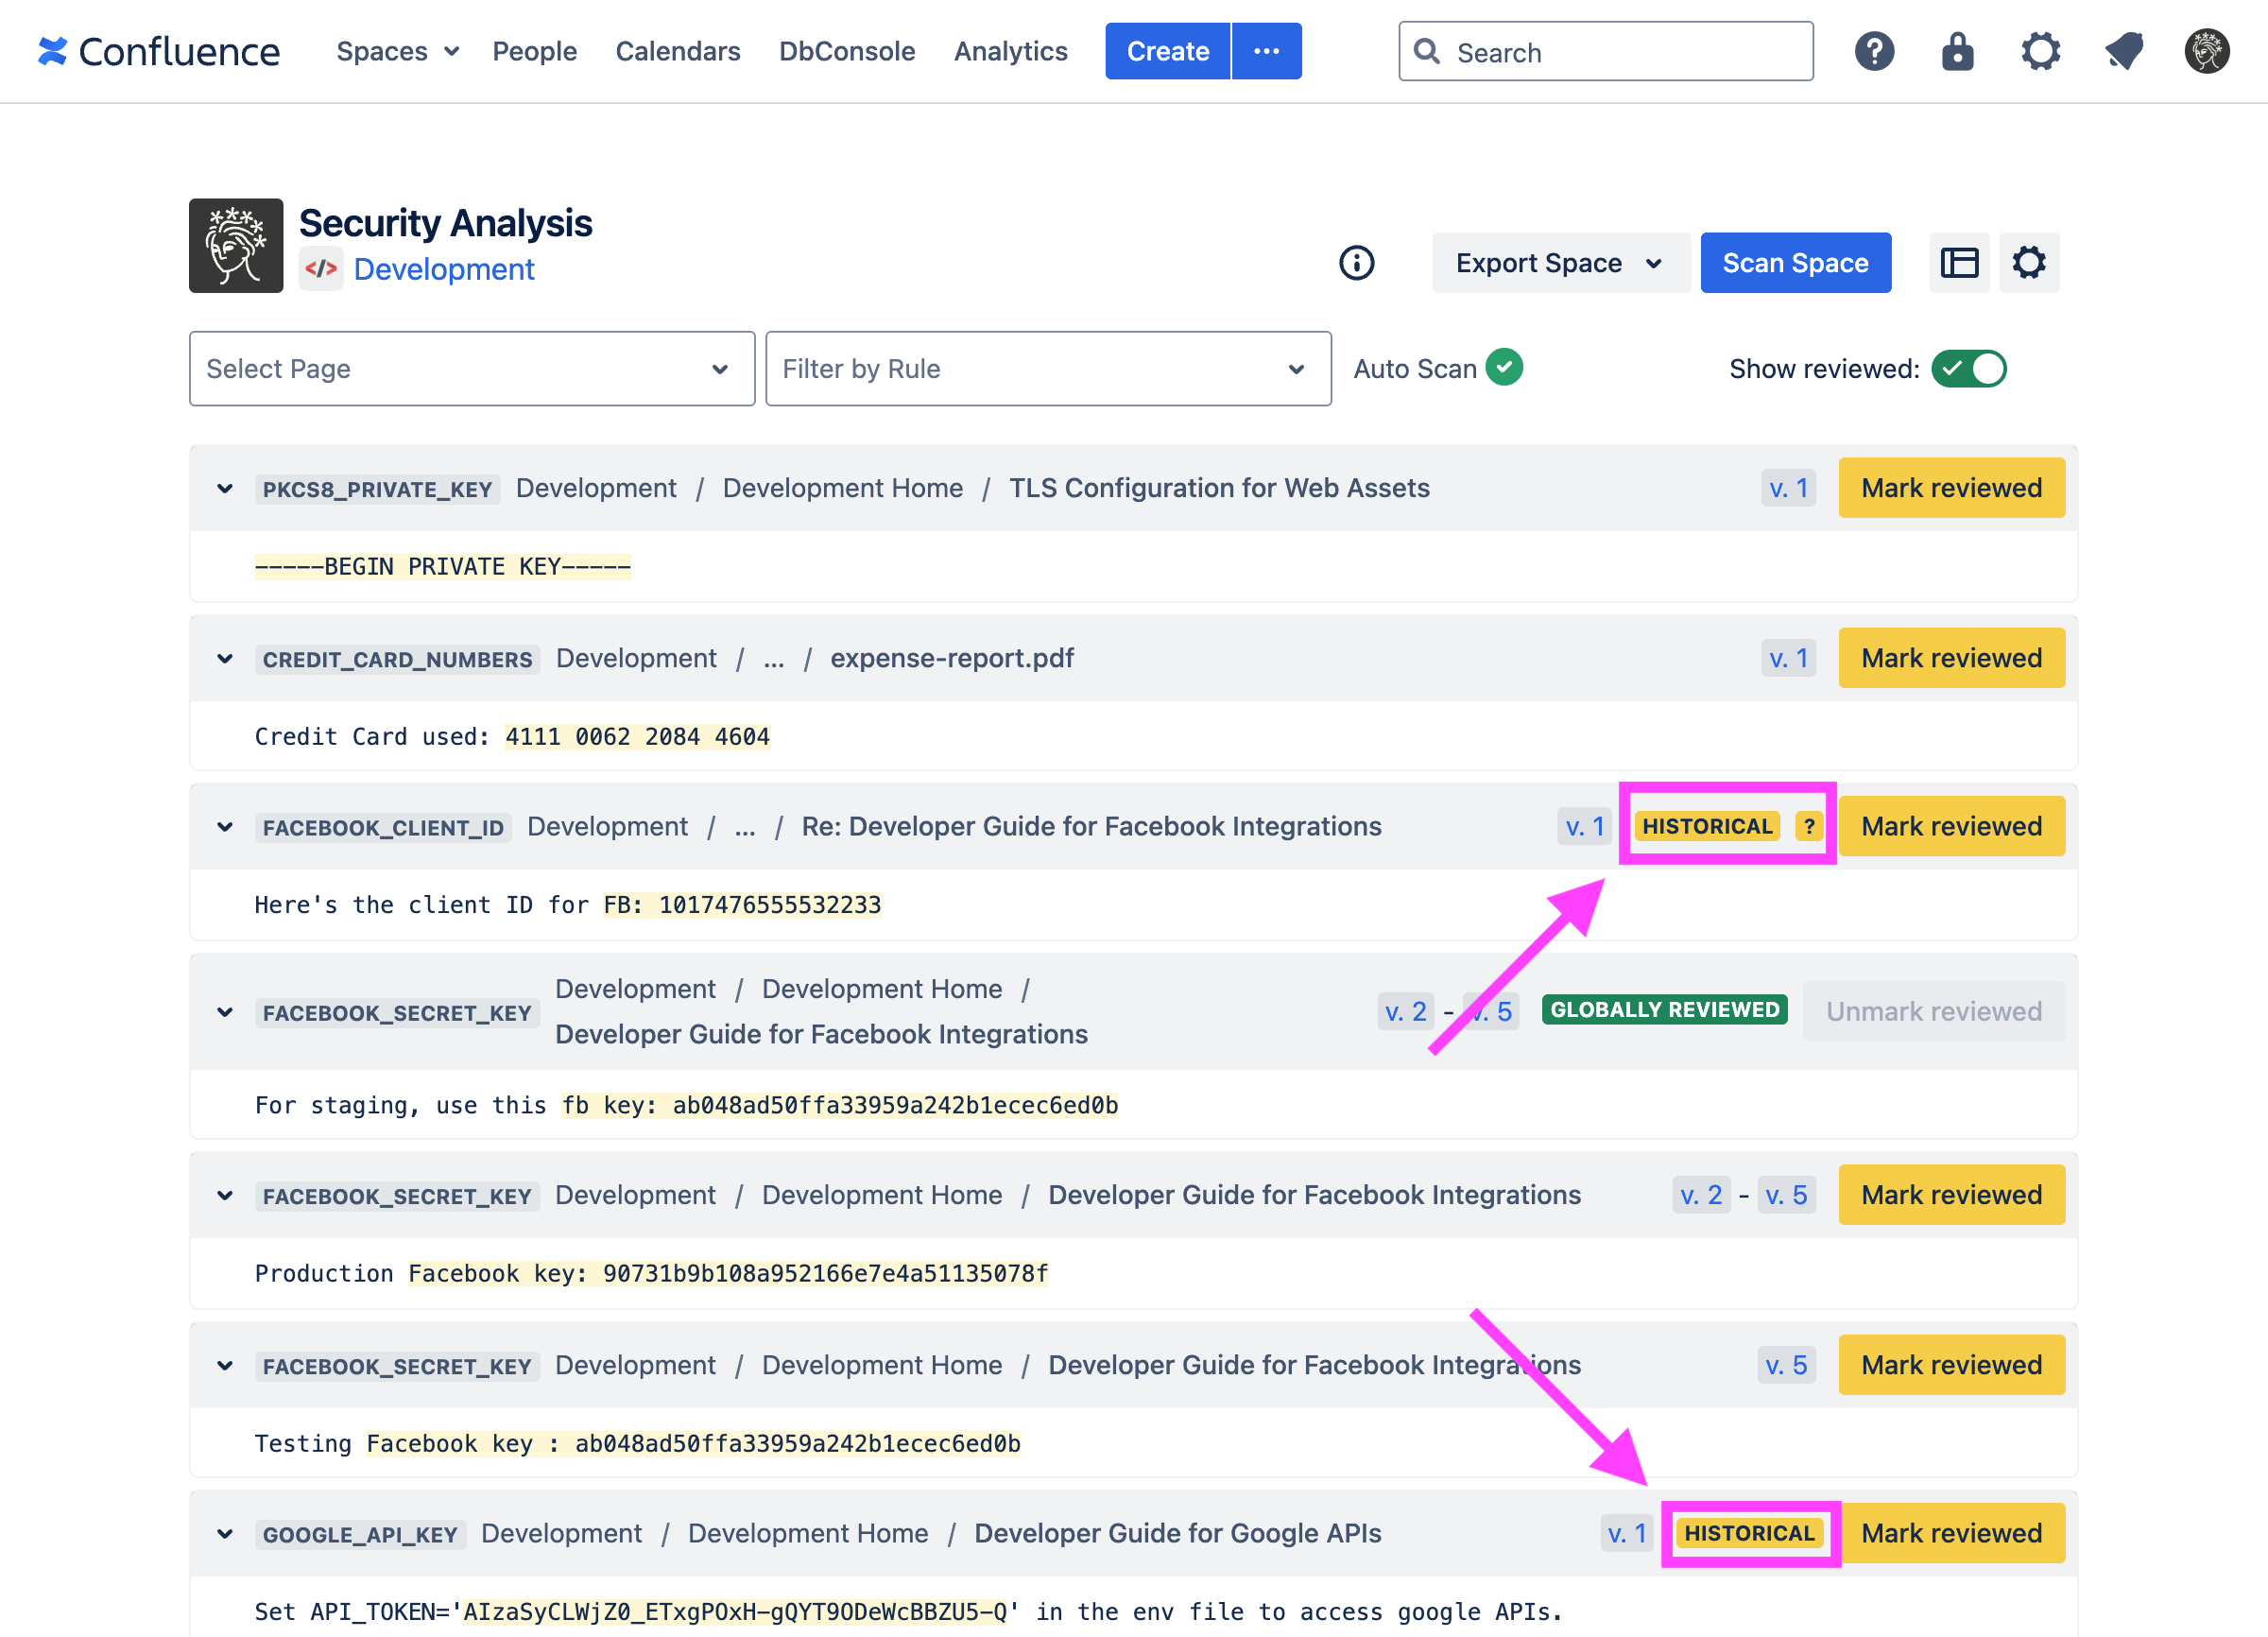
For scan findings in historical versions of comments, there is an extra indicator and tooltip about remediation, as described in [Scanning Comments \| Removing secrets in comments](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-comments.md#Removing-secrets-in-comments).
## Scan warnings
The Security Analysis will warn you if a previous scan is stale or outdated.
### Stale scan
If content in a previously scanned space is added, removed, or updated, and [automatic scanning](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md) is disabled, then the Security Analysis will indicate that the space's scan results are **stale**, and the space should be re-scanned.
The space scan stale result warning
#### Outdated scan
Additionally, if a space is scanned, but a global detection rule is later toggled, then the Security Analysis will indicate that the space scan results are **outdated**.

The space scan outdated result warning
This warning also appears for each page where global rules have changed since its last scan.

The page scan outdated result warning
---
version: "latest"
language: "en"
---
# Scanning Files Attached to Pages
By default, Security for Confluence scans files attached to pages or blog posts.
* Most common document types are supported.
* Any files which are 50MB or larger are skipped.
* Archives (e.g. `.zip`, `.rar`, and `.gz`) are not supported yet.
## Supported File Types
| **File Type** | **File Extensions** |
|----------------------------------------|----------------------------------------------------------------------------------------------------------------------|
| PDFs | `.pdf` |
| Microsoft Word Documents | `.docx`, `.doc`, `.docm`, `.dotx`, `.dotm`, `.dot` |
| Microsoft Excel Spreadsheets | `.xlsx`, `.xls`, `.xltx`, `.xltm`, `.xslm`, `.xslb`, `.xlt`, |
| Microsoft Powerpoint Presentations | `.pptx`, `.ppt`, `.pot`, `.potm`, `.potx`, `.pps`, `.ppsm`, `.ppsx`, `.pptm` |
| Microsoft OneNote Pages | `.one` |
| Email Messages | `.eml`, `.msg,` `.oft`, `.pst`, `.mbox` |
| XPS Documents | `.xps` |
| Rich Text Documents | `.rtf` |
| Ebooks | `.epub` |
| OpenOffice / LibreOffice Documents | `.odt`, `.fodt`, `.ott` |
| OpenOffice / LibreOffice Spreadsheets | `.ods`, `.fods`, `.ots` |
| OpenOffice / LibreOffice Presentations | `.odp`, `.fodp`, `.otp` |
| WordPerfect Documents | `.wpd`, `.wp`, `.wpt`, `.qpw` |
| Plain text formats | Any extension not listed above is scanned as plain text. For example, `.txt`, `.csv`, `.html` and source code files. |
We do not currently support scanning "[Strict OOXML](https://www.loc.gov/preservation/digital/formats/fdd/fdd000401.shtml)" Office documents. These files will have either `.docx`, `.pptx`, or `.xlsx` extensions. When scanning, these files will be skipped, and will show up as unsupported in attachment scan exports.
## Enabling and Disabling Attachment Scanning
We recommend leaving attachment scanning enabled, for the best security coverage. Nevertheless, you can turn attachment scanning on or off by [navigating to the settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md), and toggling the "Scan attachments" setting.
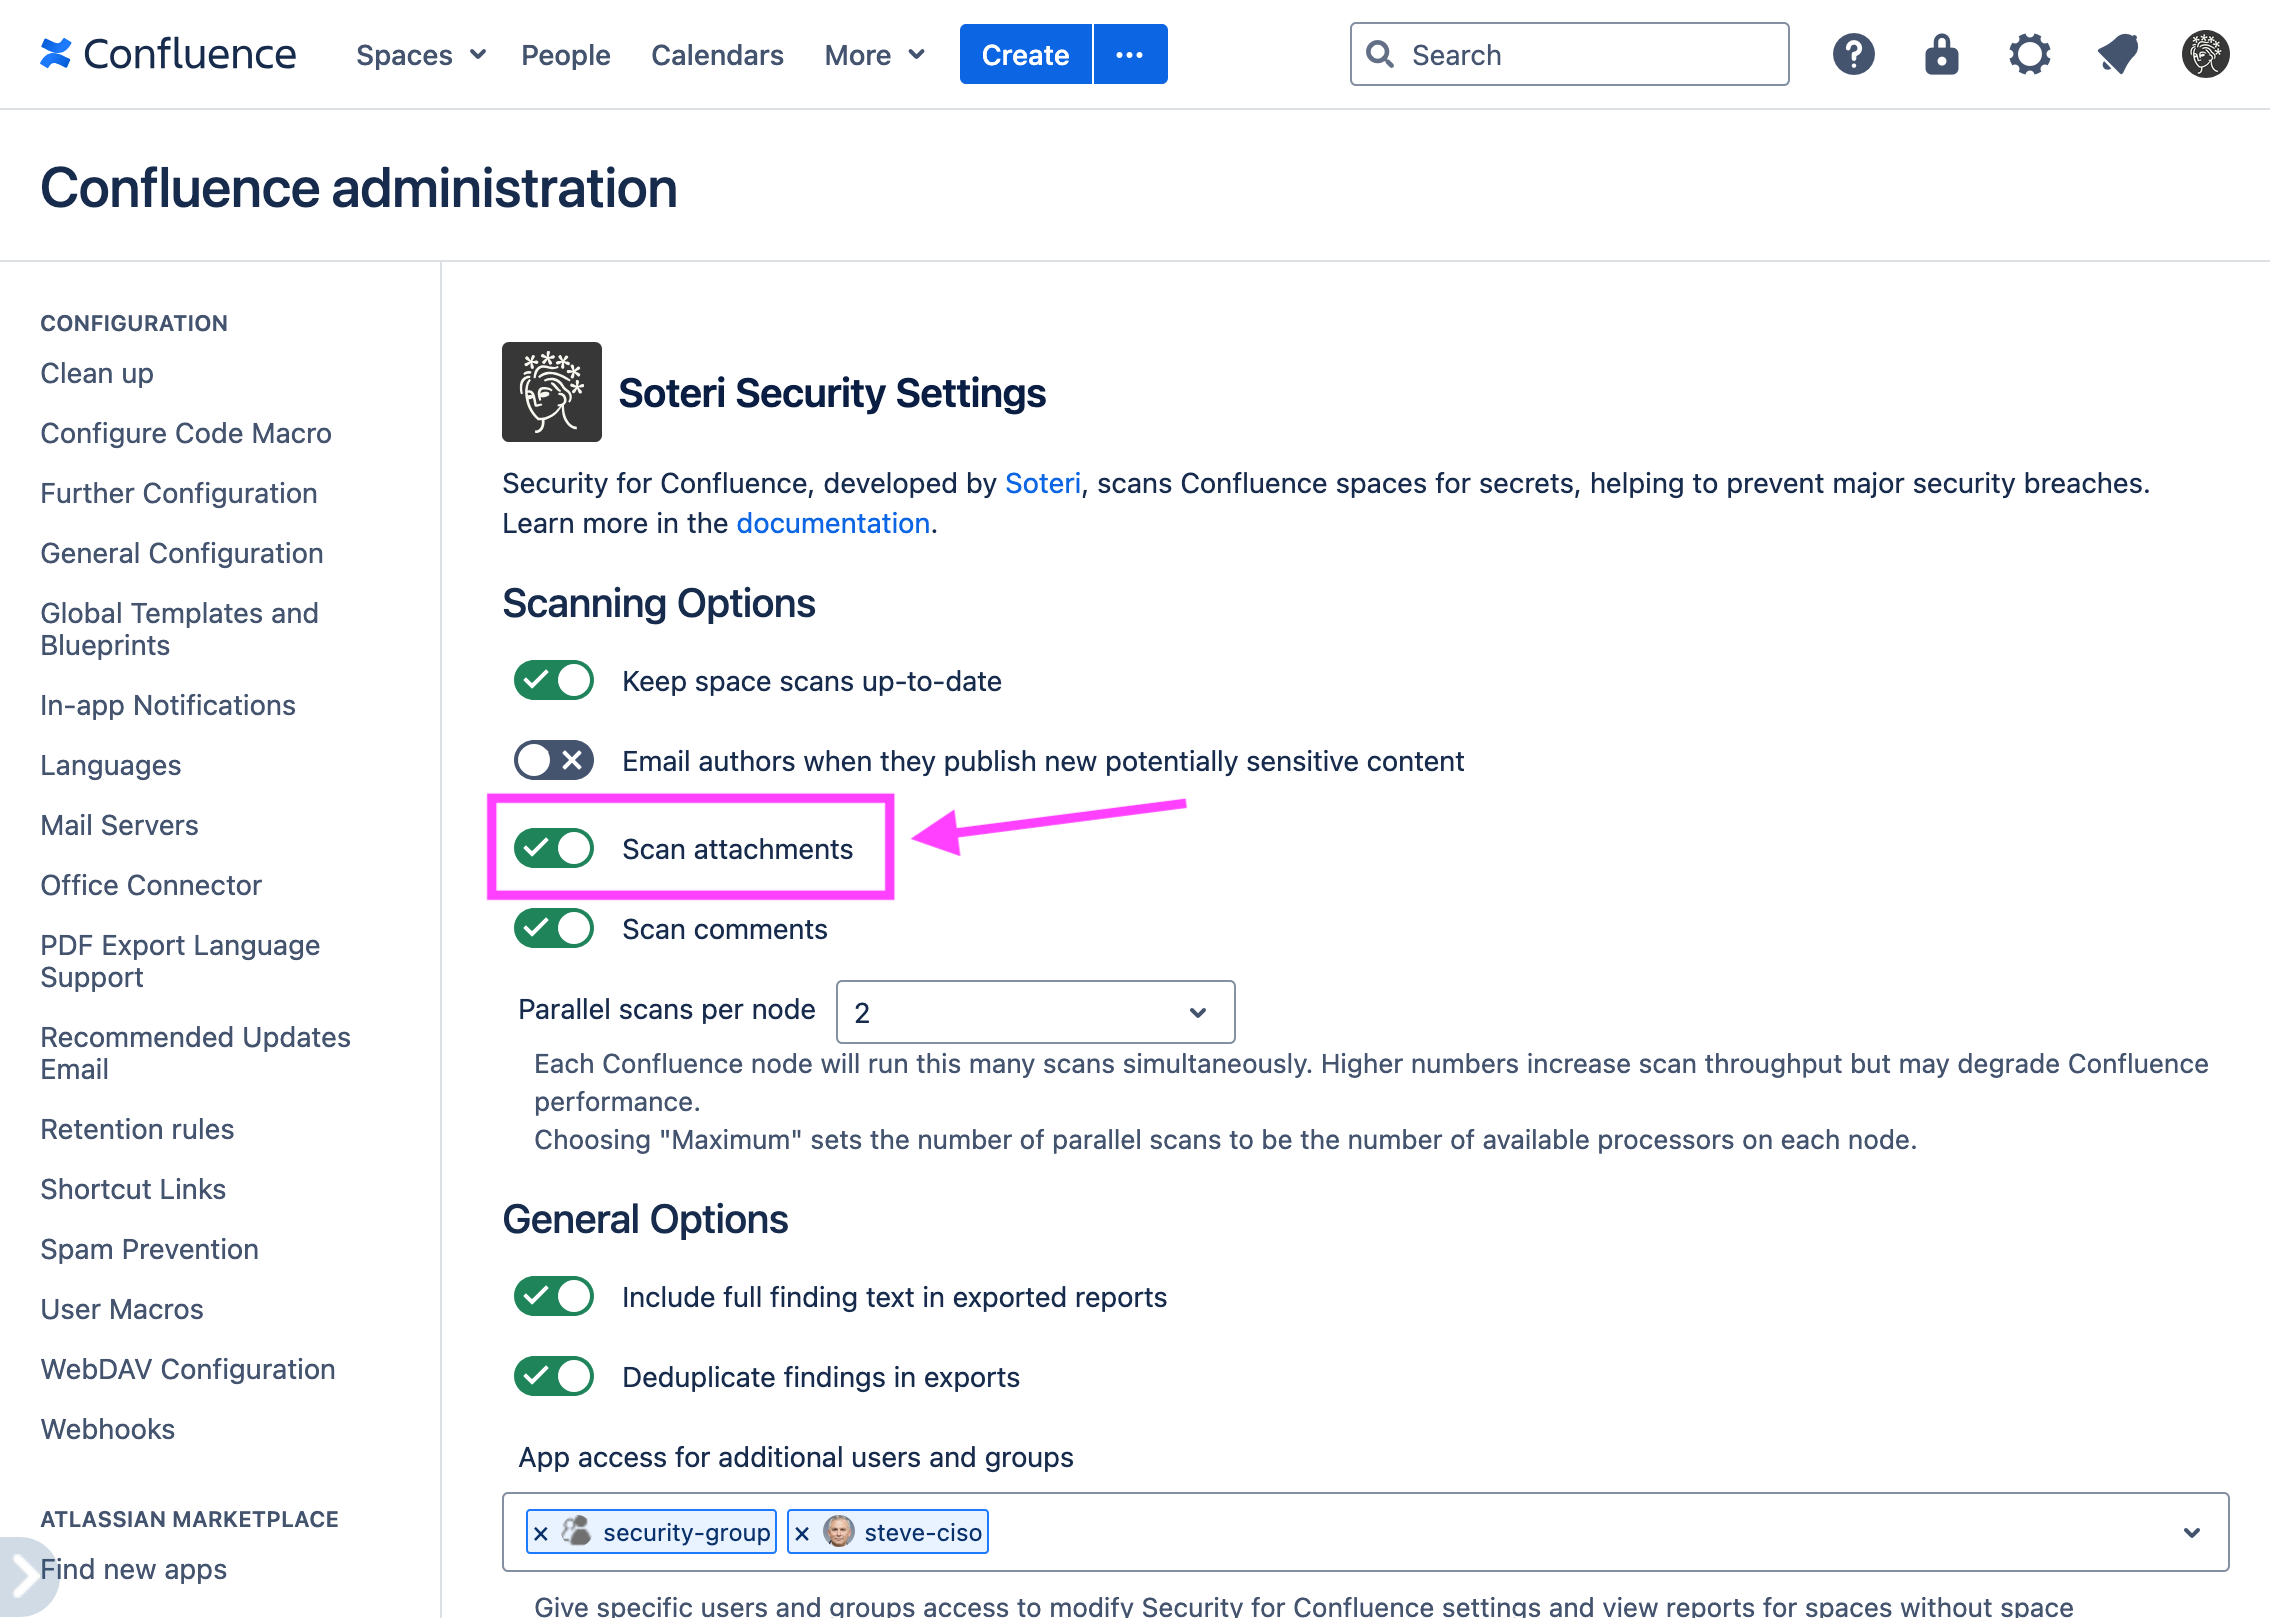
## Exporting Information About Scanned Attachments
To get information about which attachments Security for Confluence scanned, skipped, or failed to scan, you can export information about scanned attachments. These exports are CSV formatted with the following columns:
* Space key
* Parent page title
* Parent page ID
* File name
* Attachment ID
* Attachment version number
* File Size
* Scan status - will be one of the following:
* UNSCANNED
* SCANNED
* FAILED
* Reason for not scanning - If the file is not scanned, then this will have a reason code:
* UNSUPPORTED_FORMAT
* ENCRYPTED
* TOO_BIG
* PARSE_ERROR
* NOT_FOUND
* MALFORMED
* EXCEEDED_MEMORY_LIMIT
* EXCEEDED_TIME_LIMIT
* Error message - an optional error message which may indicate why scanning the attachment failed.
From [the Soteri Dashboard](https://docs.soteri.io/security-for-confluence-dc/latest/the-soteri-dashboard-viewing-confluence-s-overall-.md), you can export attachment scan information for all attachment versions in all spaces you can view reports for:
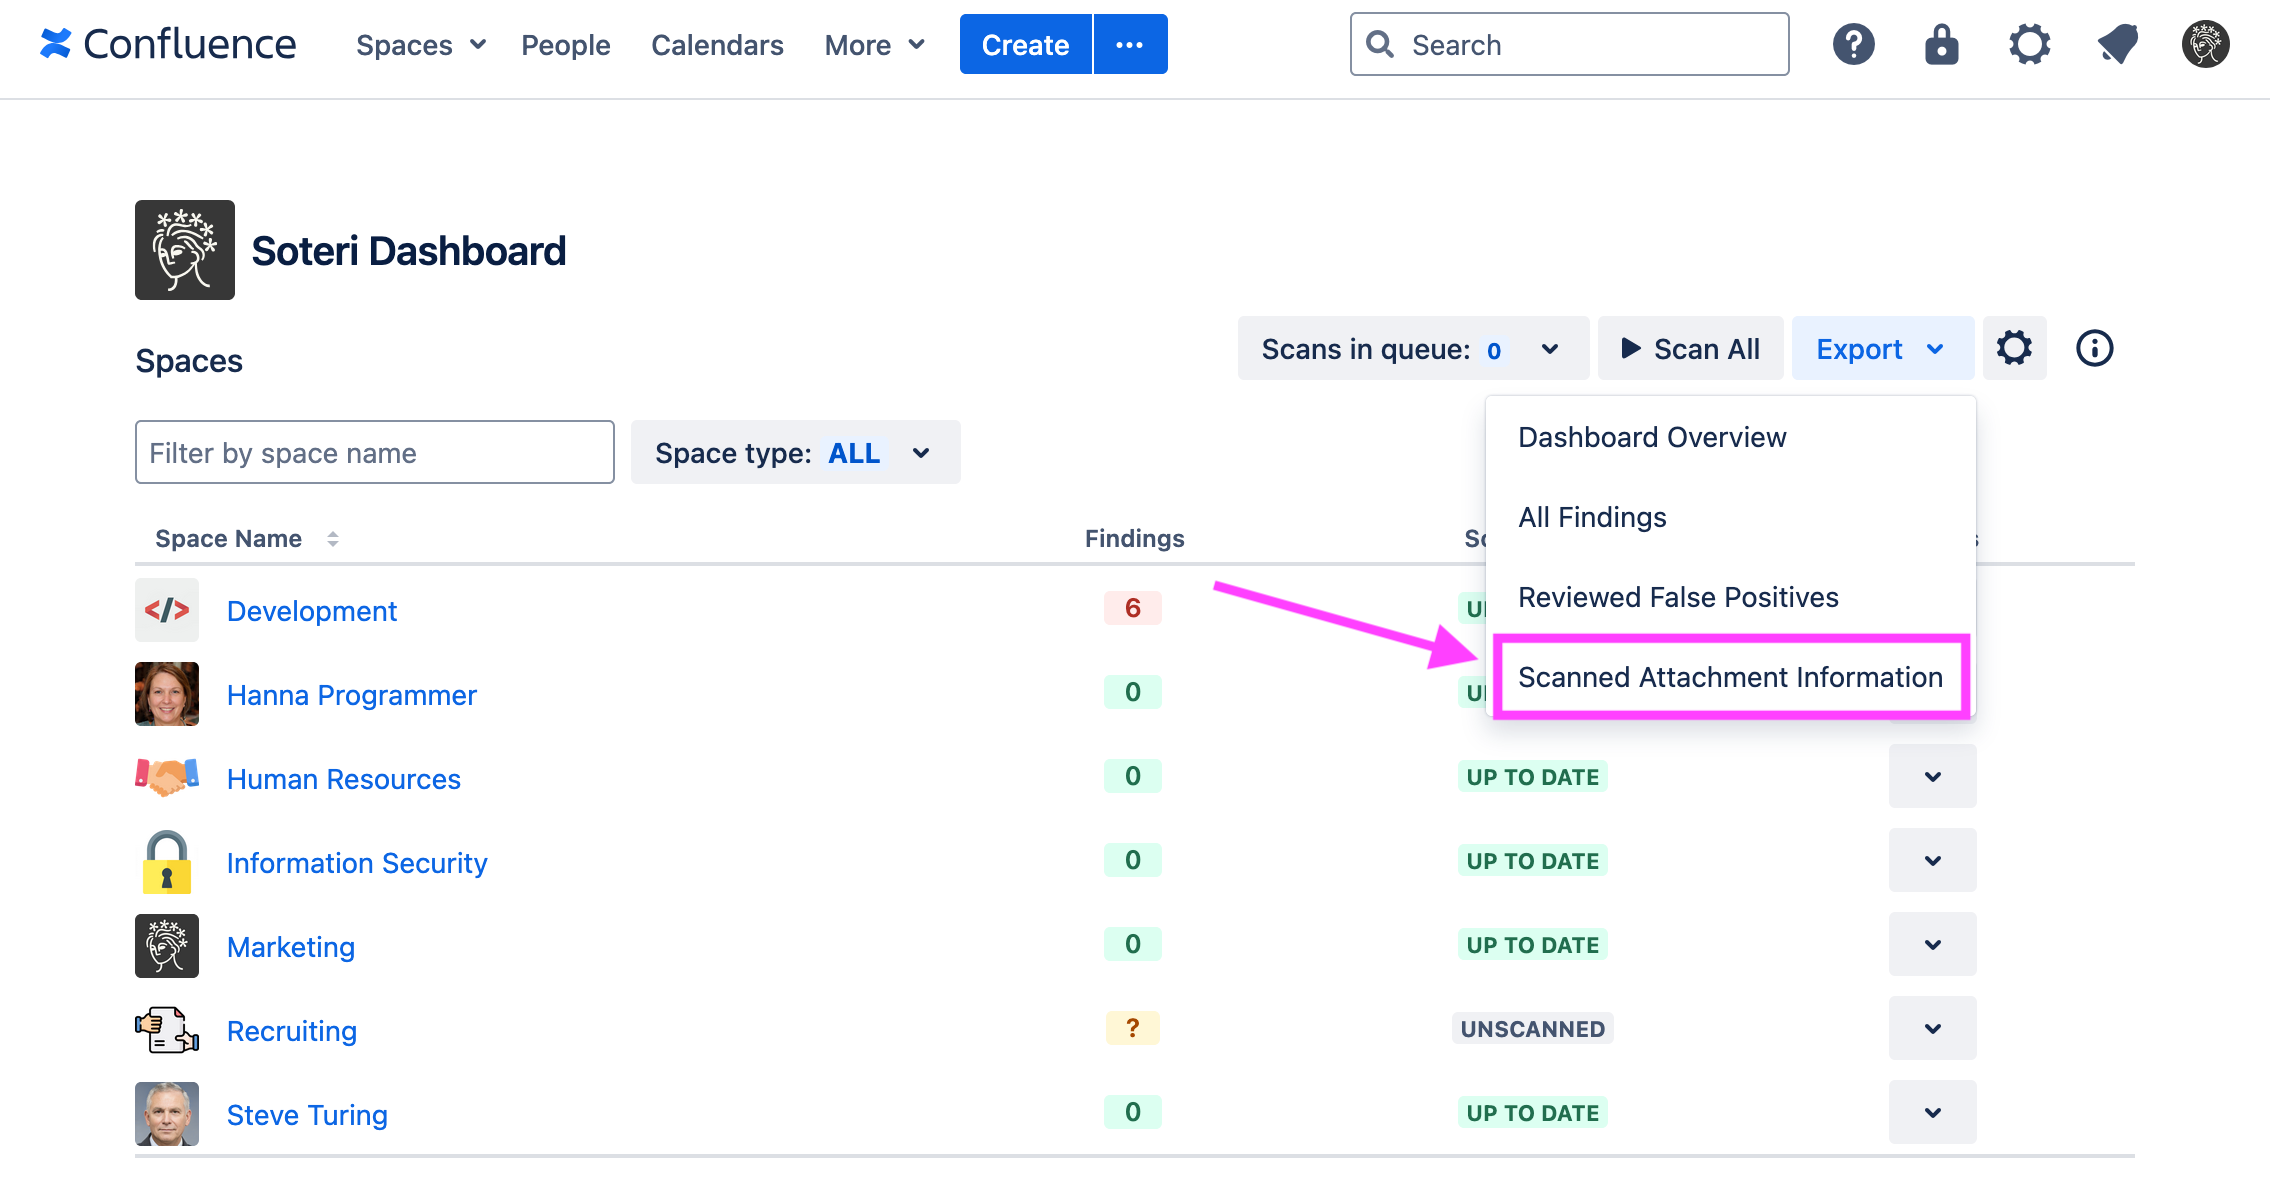
From [the Security Analysis](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-content-for-vulnerabilities.md) page, you can export attachment scan information for a specific space:
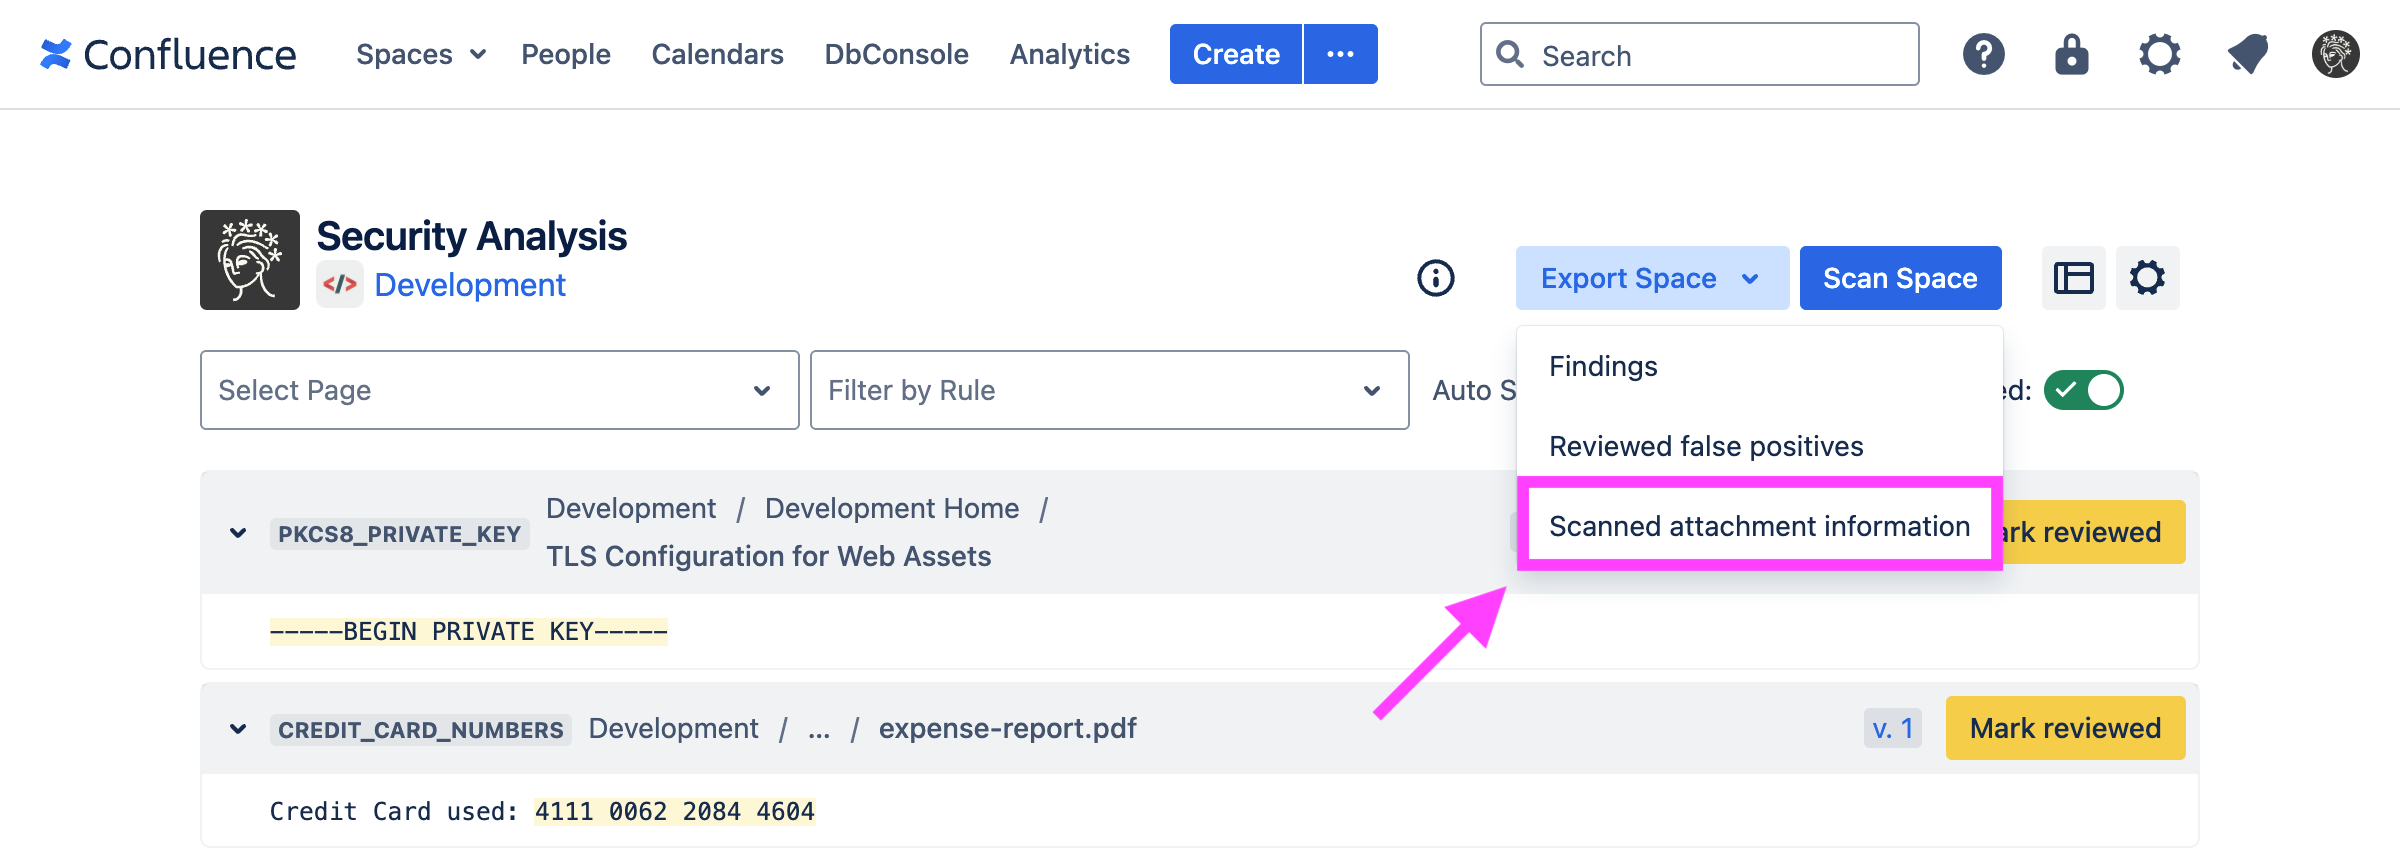
You can also export this information using our [REST API](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md).
---
version: "latest"
language: "en"
---
# Security for Confluence Data Center Cookbook
The following recipes are provided for informational purposes only and any code here is provided on an "as-is" basis. The reader assumes all risk of any use of the code in this Cookbook. THERE IS NO WARRANTY ON THIS SOFTWARE, EXPRESS OR IMPLIED, AND ALL WARRANTIES ARE EXPRESSLY DISCLAIMED HEREIN, INCLUDING THE IMPLIED WARRANTY OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR PURPOSE.
## Integrate Security for Confluence Data Center with Jira
### Introduction
While Security for Confluence provides a rich interface for processing your findings, it may be the case that utilizing a Jira project with tickets for each finding fits with your organizational goals in terms of metrics and disposition frequency. For example, Jira tickets allow comments where the person who processes the finding can track the work required to rotate a secret, or track the nuance in a particularly odd false-positive, or provide a custom outcome when a finding is marked "Reviewed". Jira tickets can also be linked to other related projects easily, which could allow them to be delegated to teams responsible for the affected content itself, for example.
The following solution uses the Soteri Security for Confluence Data Center REST API and the Jira Data Center REST API to pull findings from Soteri API and create issues using the Jira API. While Jira Cloud is not covered here, it is certainly possible to adapt this script to create Jira Cloud tickets.
In this recipe you will learn:
* How to use the Soteri Security for Confluence Data Center REST API to gather information about findings needed to make actionable tasks in a service management product
* How to generate Jira tickets using the Jira Data Center REST API from Soteri Security for Confluence findings
* How to ensure your findings and your tickets are synchronized and not duplicated.
### Steps
1. Create a new Python project using your preferred dependency management system. For example, you could create a python3 virtual environment:
$ virtualenv security-for-confluence-jira-integration-env
# ...
$ source security-for-confluence-jira-integration-env/bin/activate
2. Install the following required dependencies: `click`, `atlassian-python-api`, and `strictyaml` (for Prometheus-flavored configuration).
$ pip install click atlassian-python-api strictyaml
3. Create the following configuration file in `/etc/soteri/security-for-confluence-jira-integration.yaml`.
Relying on OS permissions to protect credentials on disk **may not be approved by your organizational security policy** - in which case, you will need to find an alternative way to provide your Confluence and Jira credentials.
confluence:
url: http://your-instance-here/confluence
username: your-username
password: your-password
jira:
url: http://your-instance-here/jira
username: your-username
password: your-password
custom_field_id: 10201
project_key: INFOSEC
issue_type_id: 10100
4. Create the following integration script:
`security-for-confluence-jira-integration.py`
Python
#!/usr/bin/env python
import sys
from hashlib import sha512
import click
from atlassian import Confluence, Jira
from strictyaml import load
def get_findings(confluence):
for space in confluence.get_all_spaces()['results']:
base_url = f'/rest/security/latest/scan/space/{space['key']}'
page = 0
size = 100
total: int|None = None
while total is None or page*size < total:
resp = confluence.get(f"{base_url}?page={page}&size={size}")
total = resp['findings']['totalCount']
for finding in resp['findings']['values']:
yield finding | {"spaceKey": space['key']}
page += 1
def format_jira_payload(finding, issue_hash_field, project_key, issue_type_id, url):
space_key = finding['spaceKey']
content_id = finding['contentId']
version = finding['versionNumber']
lines = f"{finding['path']}:{finding['lineOffsetStart']}-{finding['lineOffsetEnd']}"
report_link = (f"{url}/plugins/servlet/soteri/security-scan-report?"
f"spaceKey={space_key}&id={content_id}&versionNumber={version}")
text_hash = sha512((finding['text']+lines).encode()).hexdigest()
return {
"project": {"key": project_key},
"summary": f"{finding['ruleName']} finding in {space_key} - {finding['pageName']}:{lines}",
"description": f"""
h3. A potential secret leak was detected by Soteri Security for Confluence:
Title: {finding['pageName']}
Rule: {finding['ruleName']}
Lines: {lines}
Link: {finding['url']}
[Report Link|{report_link}]
""",
"issuetype": {"id": issue_type_id},
f"customfield_{issue_hash_field}": text_hash
}
def init_config(filename):
with open(filename, 'w') as file:
file.write("""confluence:
url: http://your-instance-here/confluence
username: your-username
password: your-password
jira:
url: http://your-instance-here/jira
username: your-username
password: your-password
custom_field_id: NNNNN
project_key: INFOSEC
issue_type_id: 10100""")
@click.command()
@click.option("--config-filename", default='/etc/soteri/security-for-confluence-jira-integration.yaml',
help="YAML configuration filename")
@click.option("--dry-run", is_flag=True, help="Don't make any changes")
@click.option("--init", is_flag=True, help="Generate a YAML config")
def cli(config_filename, dry_run, init):
if init:
init_config(config_filename)
click.echo(f"Initialized config file at {config_filename}")
sys.exit(0)
with open(config_filename) as config_file:
config = load(config_file.read())
confluence = Confluence(**config['confluence'].data)
jira = Jira(**config['jira'].data)
issue_hash_field = config['custom_field_id'].data
project_key = config['project_key'].data
issue_type_id = config['issue_type_id'].data
confluence_url = config['confluence']['url'].data
issues = [format_jira_payload(finding, issue_hash_field, project_key, issue_type_id, confluence_url)
for finding in get_findings(confluence)]
for issue in issues:
search_string = (f"project = {project_key} AND "
f"cf[{issue_hash_field}] ~ '{issue["customfield_"+issue_hash_field]}'")
if jira.jql(search_string)['total'] == 0:
if dry_run:
click.echo(f"Would have created issue {issue}")
else:
click.echo(f"Created {issue["summary"]}")
jira.create_issue(issue)
else:
click.echo(f"Skipping already-created issue with summary '{issue['summary']}'")
click.echo("Finished.")
if __name__ == '__main__':
cli()
5. Create a [custom field](https://support.atlassian.com/jira-cloud-administration/docs/create-a-custom-field/) in your Jira instance which will hold the cryptographic hash of the finding and the lines. This ensures that we can associate issues to the unique findings even if they've been dispositioned. It is recommended to make this a single-line text field type.
6. Get the [custom field id](https://confluence.atlassian.com/jirakb/find-my-custom-field-id-number-in-jira-744522503.html) for the custom field you just made. Save this under `custom_field_id` in the YAML configuration file you made above.
7. Decide which project you would like to create Jira issues in. Save that project's key under `project_key` in the YAML configuration file you made above.
1. Ensure that your custom field is visible in the creation interface. You can accomplish this by going to Jira Administration → Issues → Screens → "Issue Creation Screen" for the name of your project. In the "Configure Screen" view, add your new custom field.
8. Find the issue type you would like to create. You can create a new issue type, or you can find the issue type ID under Jira Administration → Issues → Issue Types → Edit (next to your issue type). The Issue type ID will be in your browser's location bar:
`/jira/secure/admin/EditIssueType!default.jspa?id=10100`
In this case, you would save `issue_type_id: 10100` in the YAML configuration file you made above.
9. With Jira configured and your configuration file completed, it's time to test:
`security-for-confluence-jira-integration.py --dry-run`
Which will tell you which issues it would have created.
If everything is good, run without the `--dry-run` flag.
Created CREDIT_CARD_NUMBERS finding in DEV - expense-report.pdf:/body/div[2]/p[2]:18-37
Created FACEBOOK_SECRET_KEY finding in DEV - Developer Guide for Facebook Integrations:/body/div/p[1]:22-62
Created FACEBOOK_SECRET_KEY finding in DEV - Developer Guide for Facebook Integrations:/body/div/p[2]:11-57
Created FACEBOOK_SECRET_KEY finding in DEV - Developer Guide for Facebook Integrations:/body/div/p[3]:8-55
Created GOOGLE_API_KEY finding in DEV - Developer Guide for Google APIs:/body/div/p:15-54
Finished.
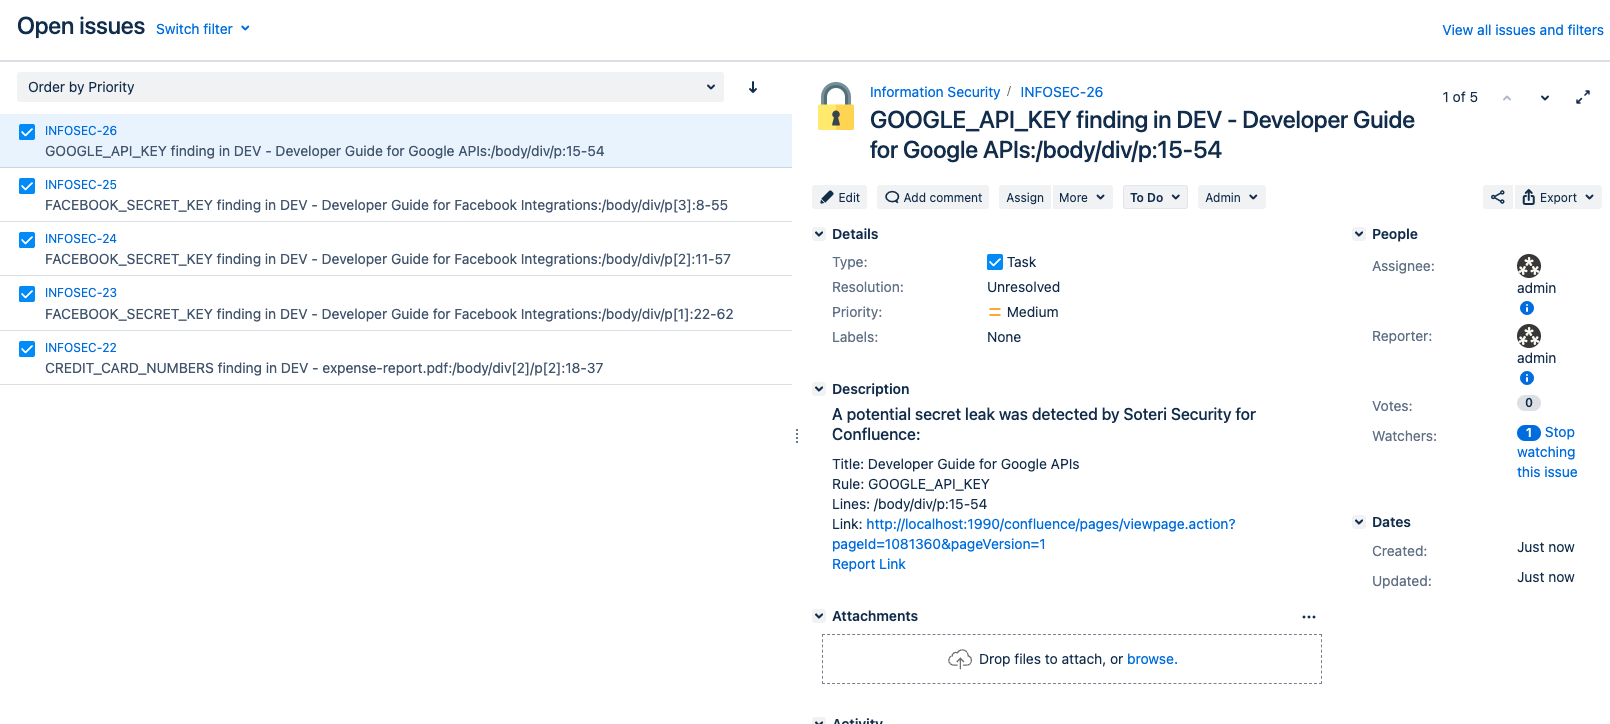
10. Now, you could schedule the script as a cron job. You can accomplish this by adding something like the following line to your system's crontab:
`0 0 * * * /home/integrator/security-for-confluence-jira-integration-env/bin/python /home/integrator/security-for-confluence-jira-integration.py`
---
version: "latest"
language: "en"
---
# The Soteri Dashboard: Viewing Confluence's overall security status
The **Soteri Dashboard** allows users to view the scan statuses of Confluence spaces. It can be accessed from anywhere within Confluence by clicking the padlock icon at the top-right of the screen:
Here is an example:
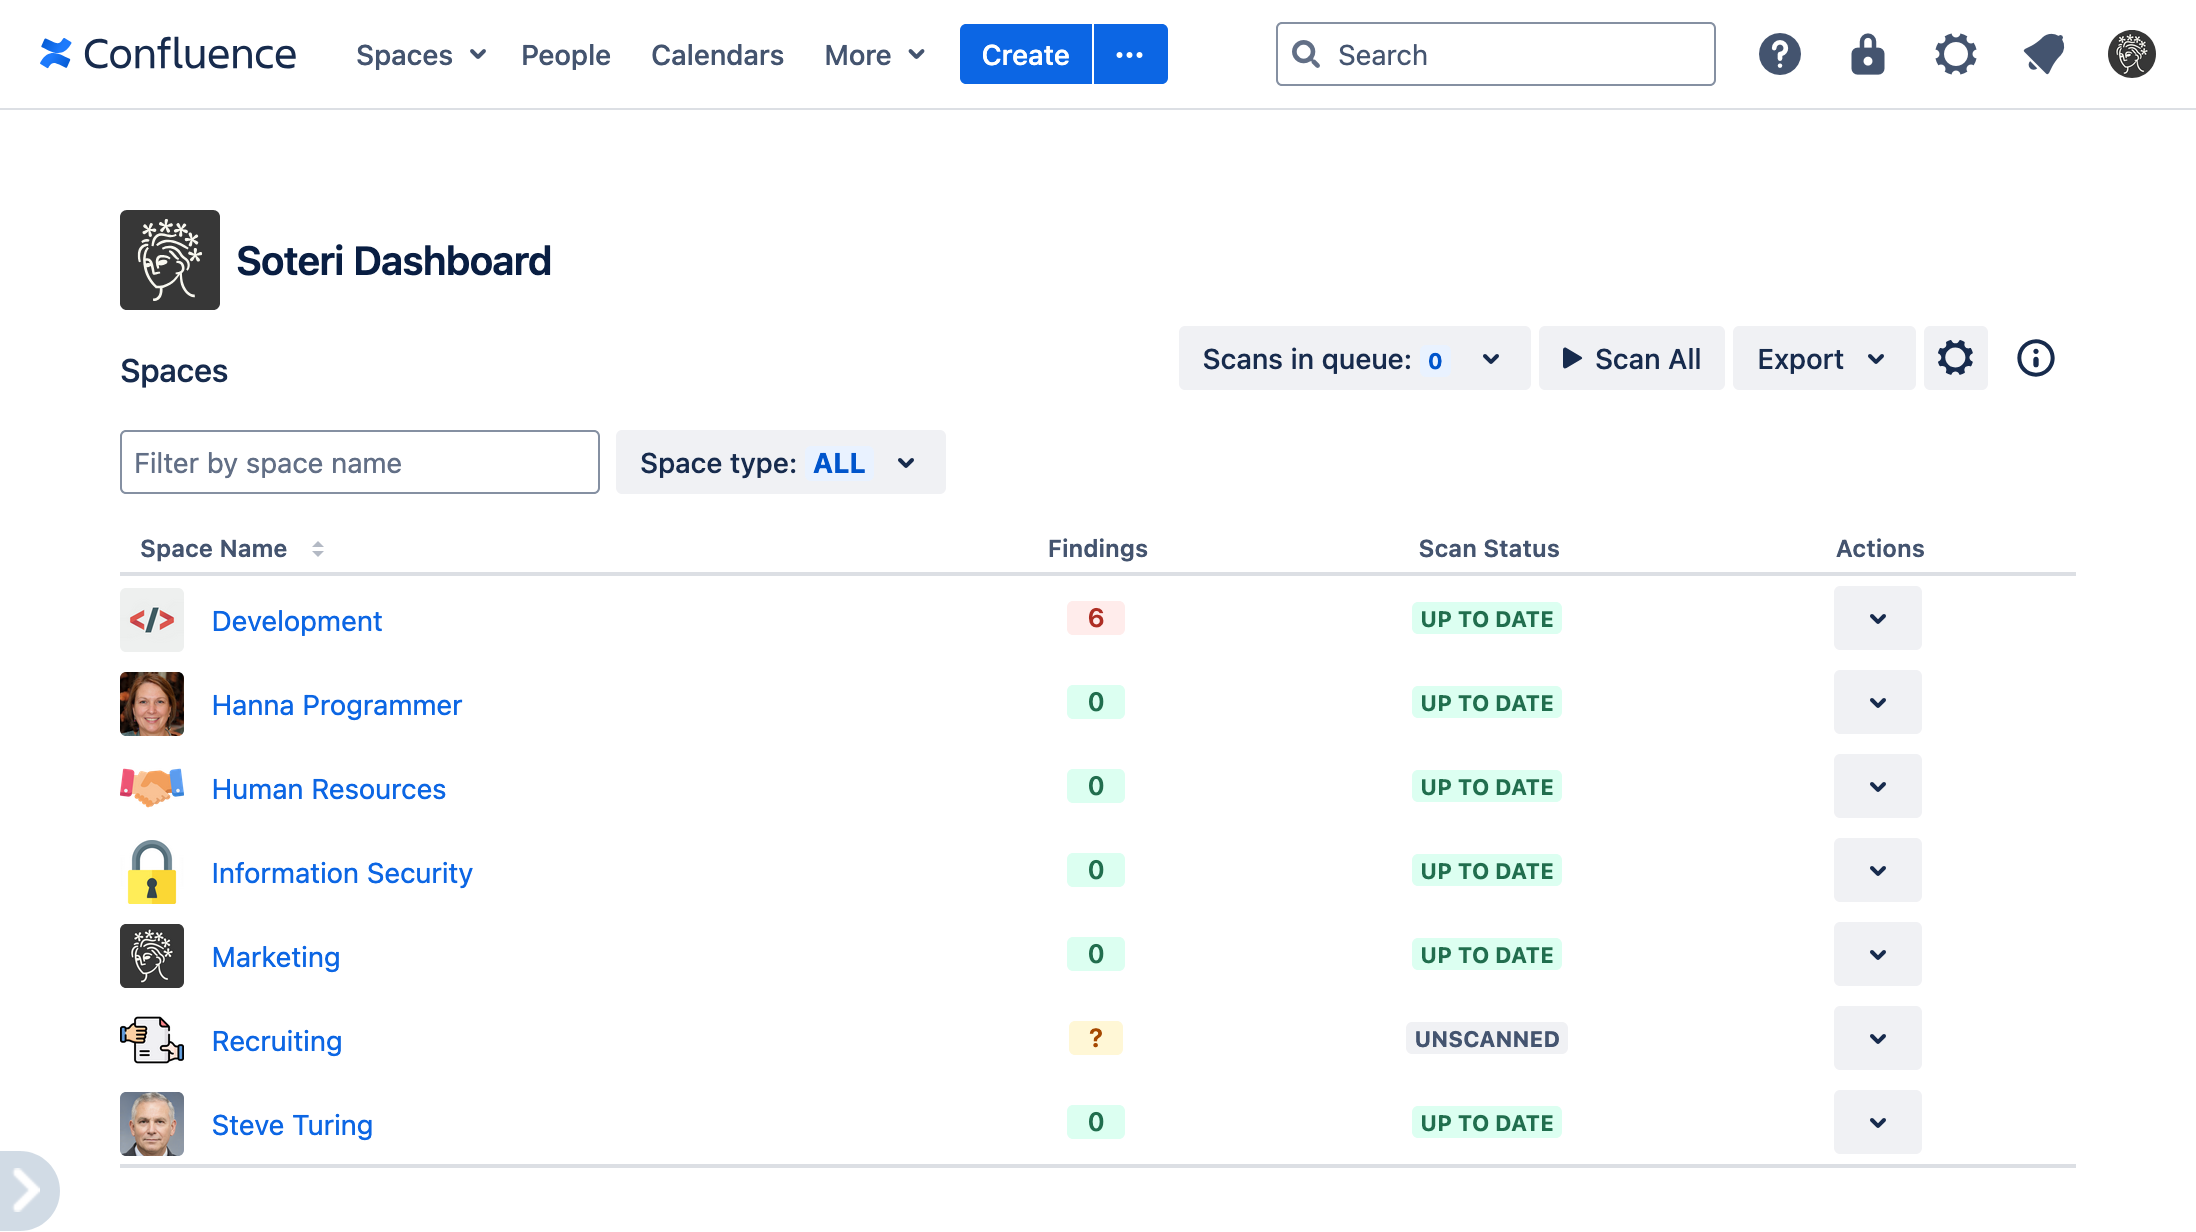
Space administrators can see the status for any space that they administer. [Users given explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) can view the scan status for any space that they have permission to view.
Each space will appear, along with the following:
* The number of unique scan findings per page in that space.
* The scan's status. This can be:
* **Up To Date**: The space has been fully scanned and either has the Security Hook enabled to scan all future content, or no changes have been made to the space since it was last scanned.
* **Outdated**: The space has been fully scanned, but changes have been made since that happened.
* **Settings Changed:** The configured scanning rules have changed since the last time this space was scanned.
* **Scanning**: A scan of the space is in progress.
* **Unscanned**: The space has not been scanned.
* **Scan Error**: There was an issue doing a scan of this space. Click the space name to learn more.
* A dropdown menu of actions you can perform for that space.
Note that the findings count does not include any [findings which have been marked as reviewed](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md).
You can use the provided "Filter by space name" input to search for particular spaces, and the "Space type" dropdown to view normal spaces, private spaces, or both (the default).
Clicking on the gear icon in the upper right will take you to the Security for Confluence [Settings](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-and-disabling-global-scanning-rules.md) page.
## Triggering Scans for an Individual Space
Clicking on a space's "Actions" dropdown menu reveals the options "Scan" and "Export":
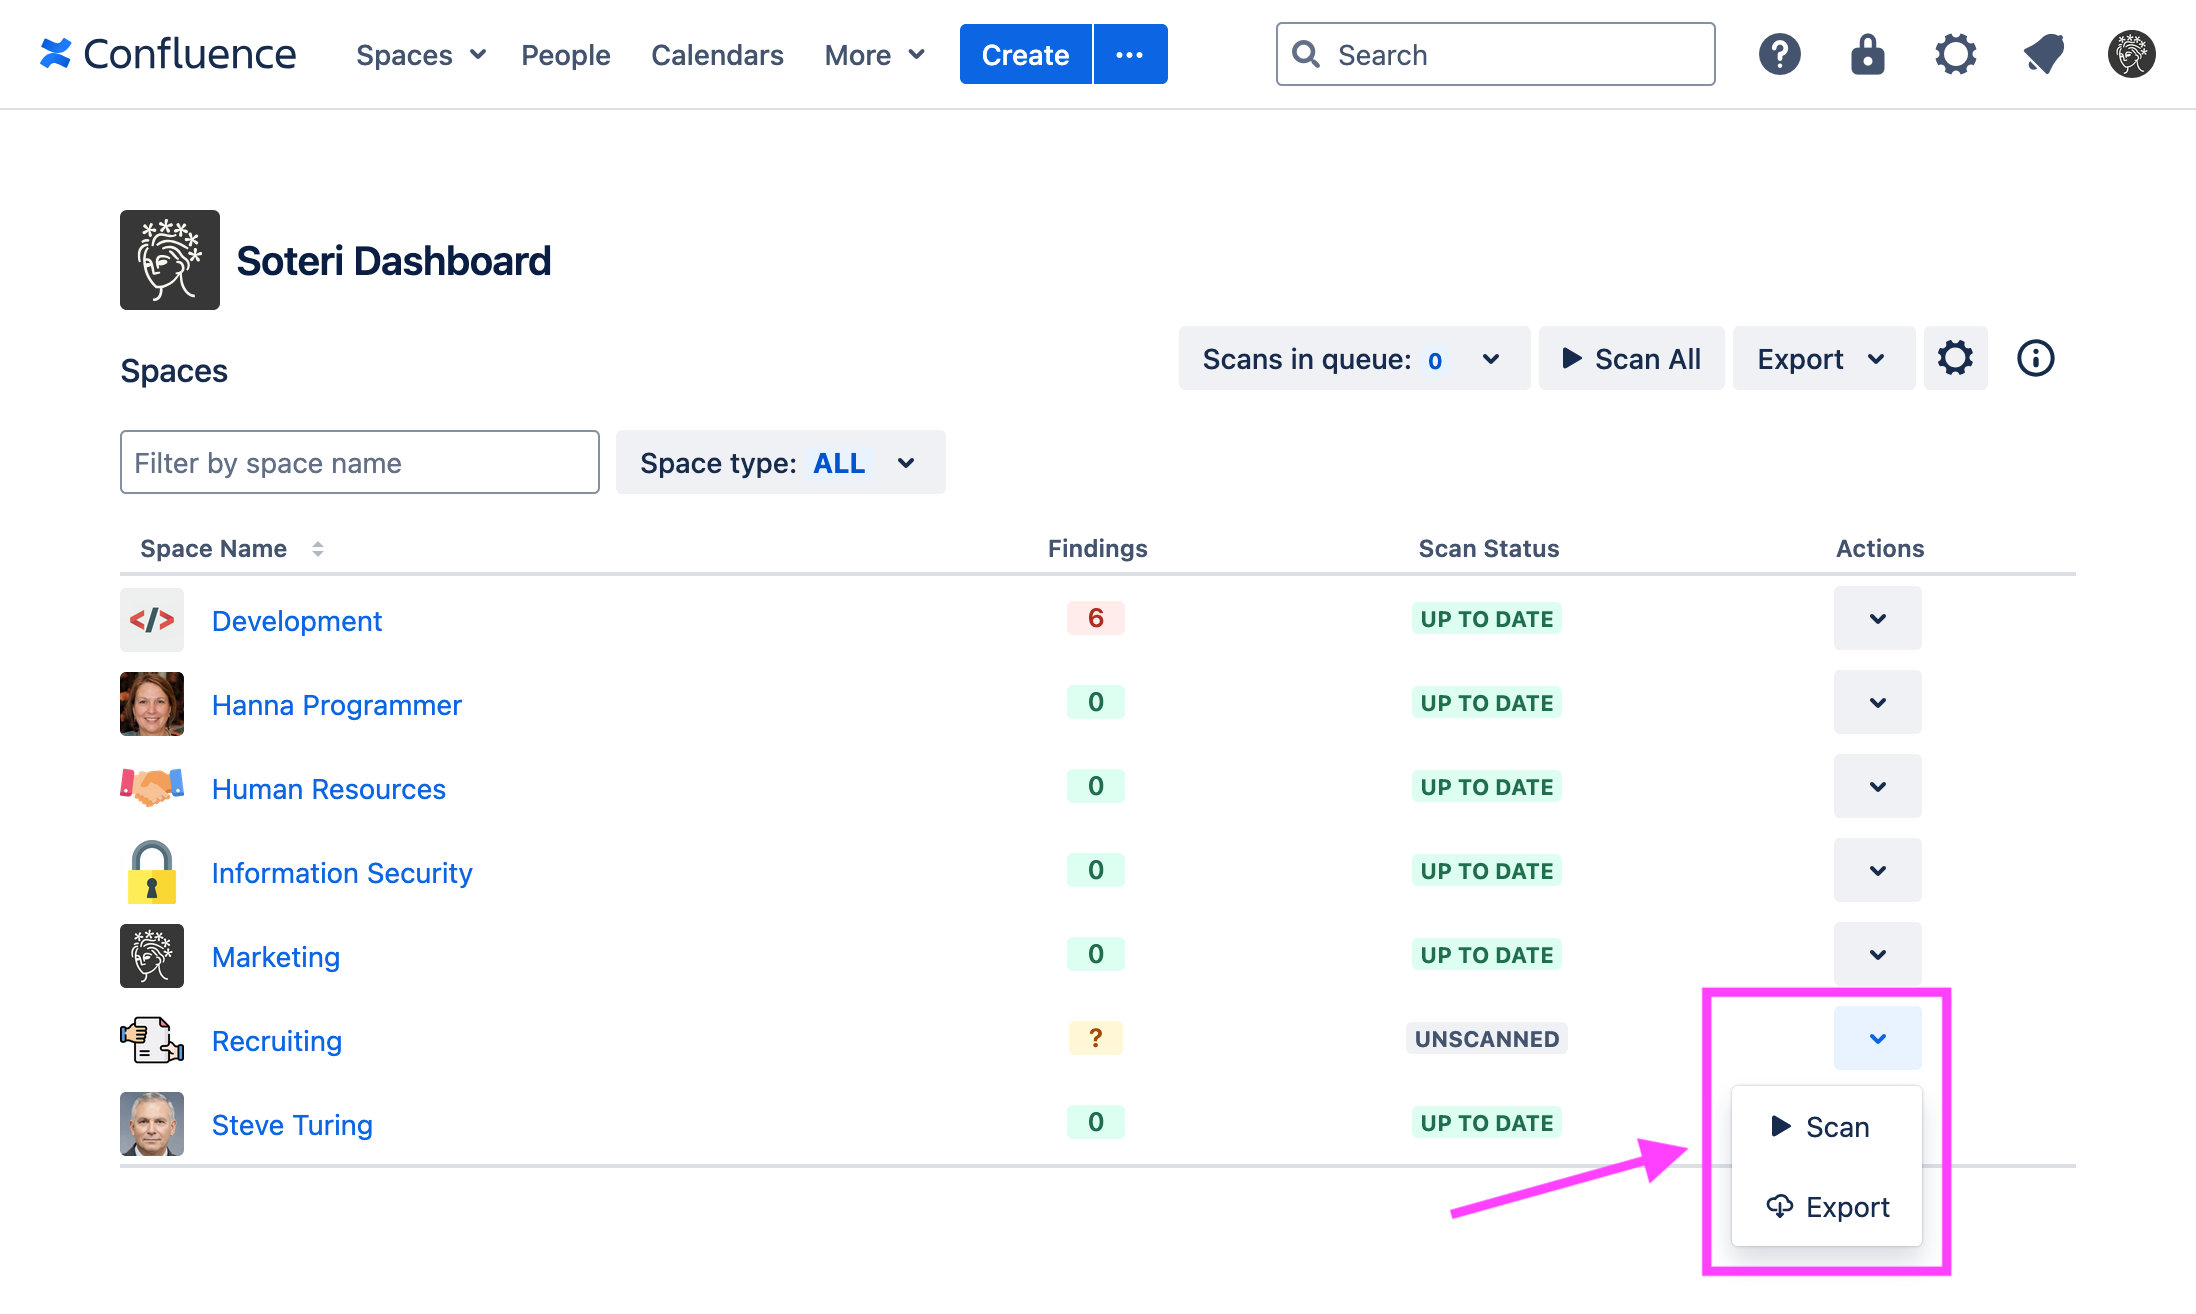
Choosing "Scan" will trigger a scan for new and modified pages in that space. Choosing "Export" will download a list of all findings for that space in CSV format. Read more about exports [here](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md).
Clicking on a space's name in the Soteri Dashboard will take you to that space's Security Analysis, where you can trigger scans on a per-page basis.
If any vulnerabilities are found, we recommend following our advice [here](https://docs.soteri.io/security-for-confluence-dc/latest/what-do-i-do-if-a-security-scan-finds-a-secret.md).
## Triggering Scans for All Spaces
Confluence administrators or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) who access the Dashboard will see the **Scan All** button.
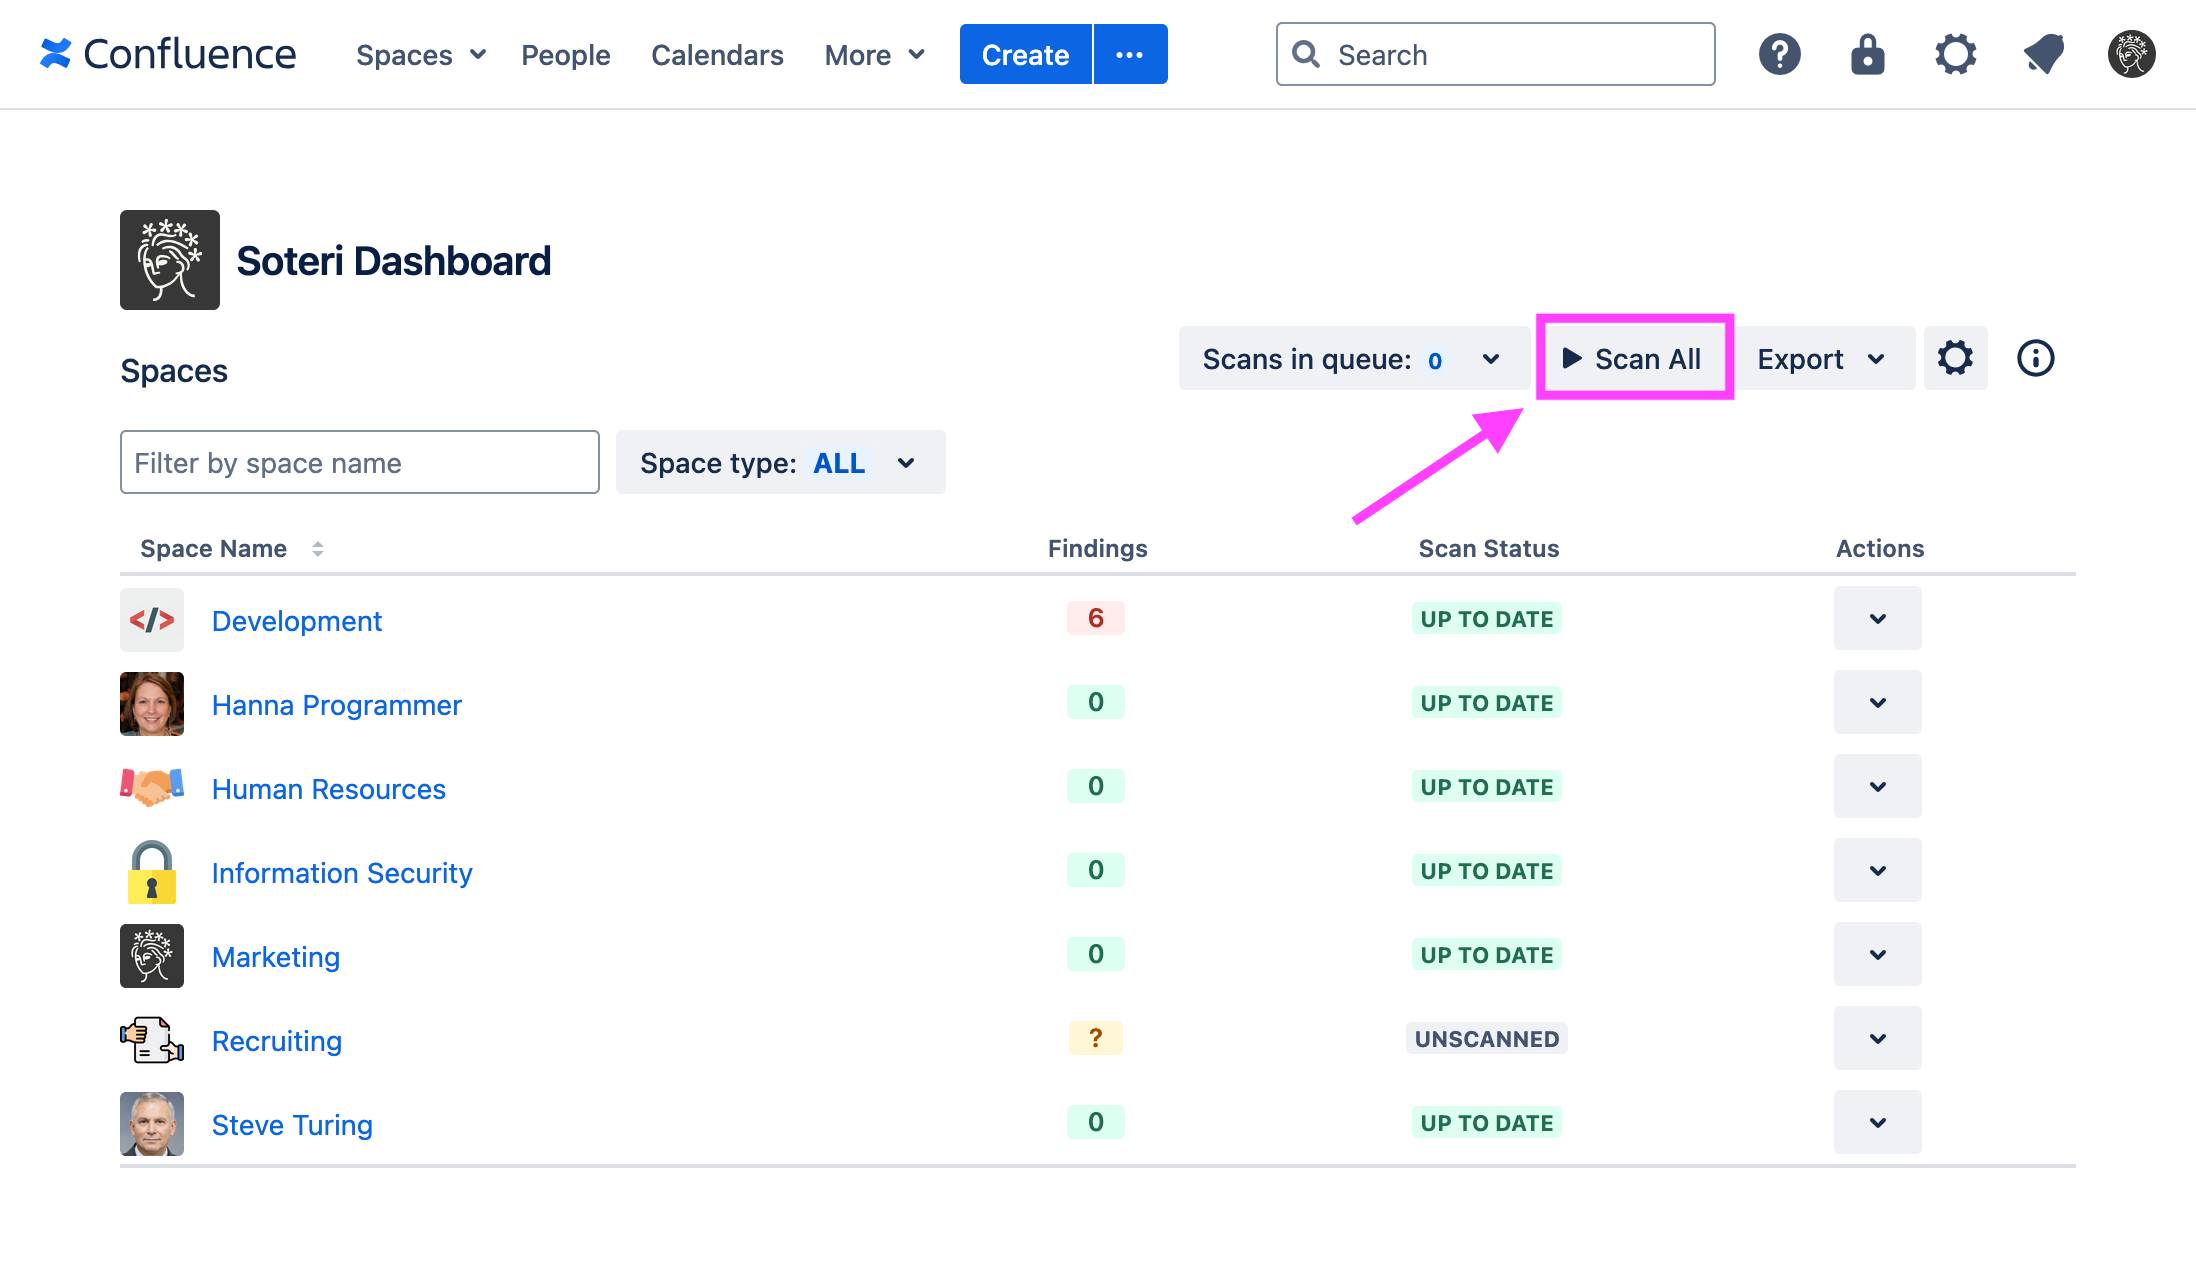
Pushing this button will trigger scans for every space in the Confluence instance.
The scan queue indicator shows how many pages are waiting to be scanned:
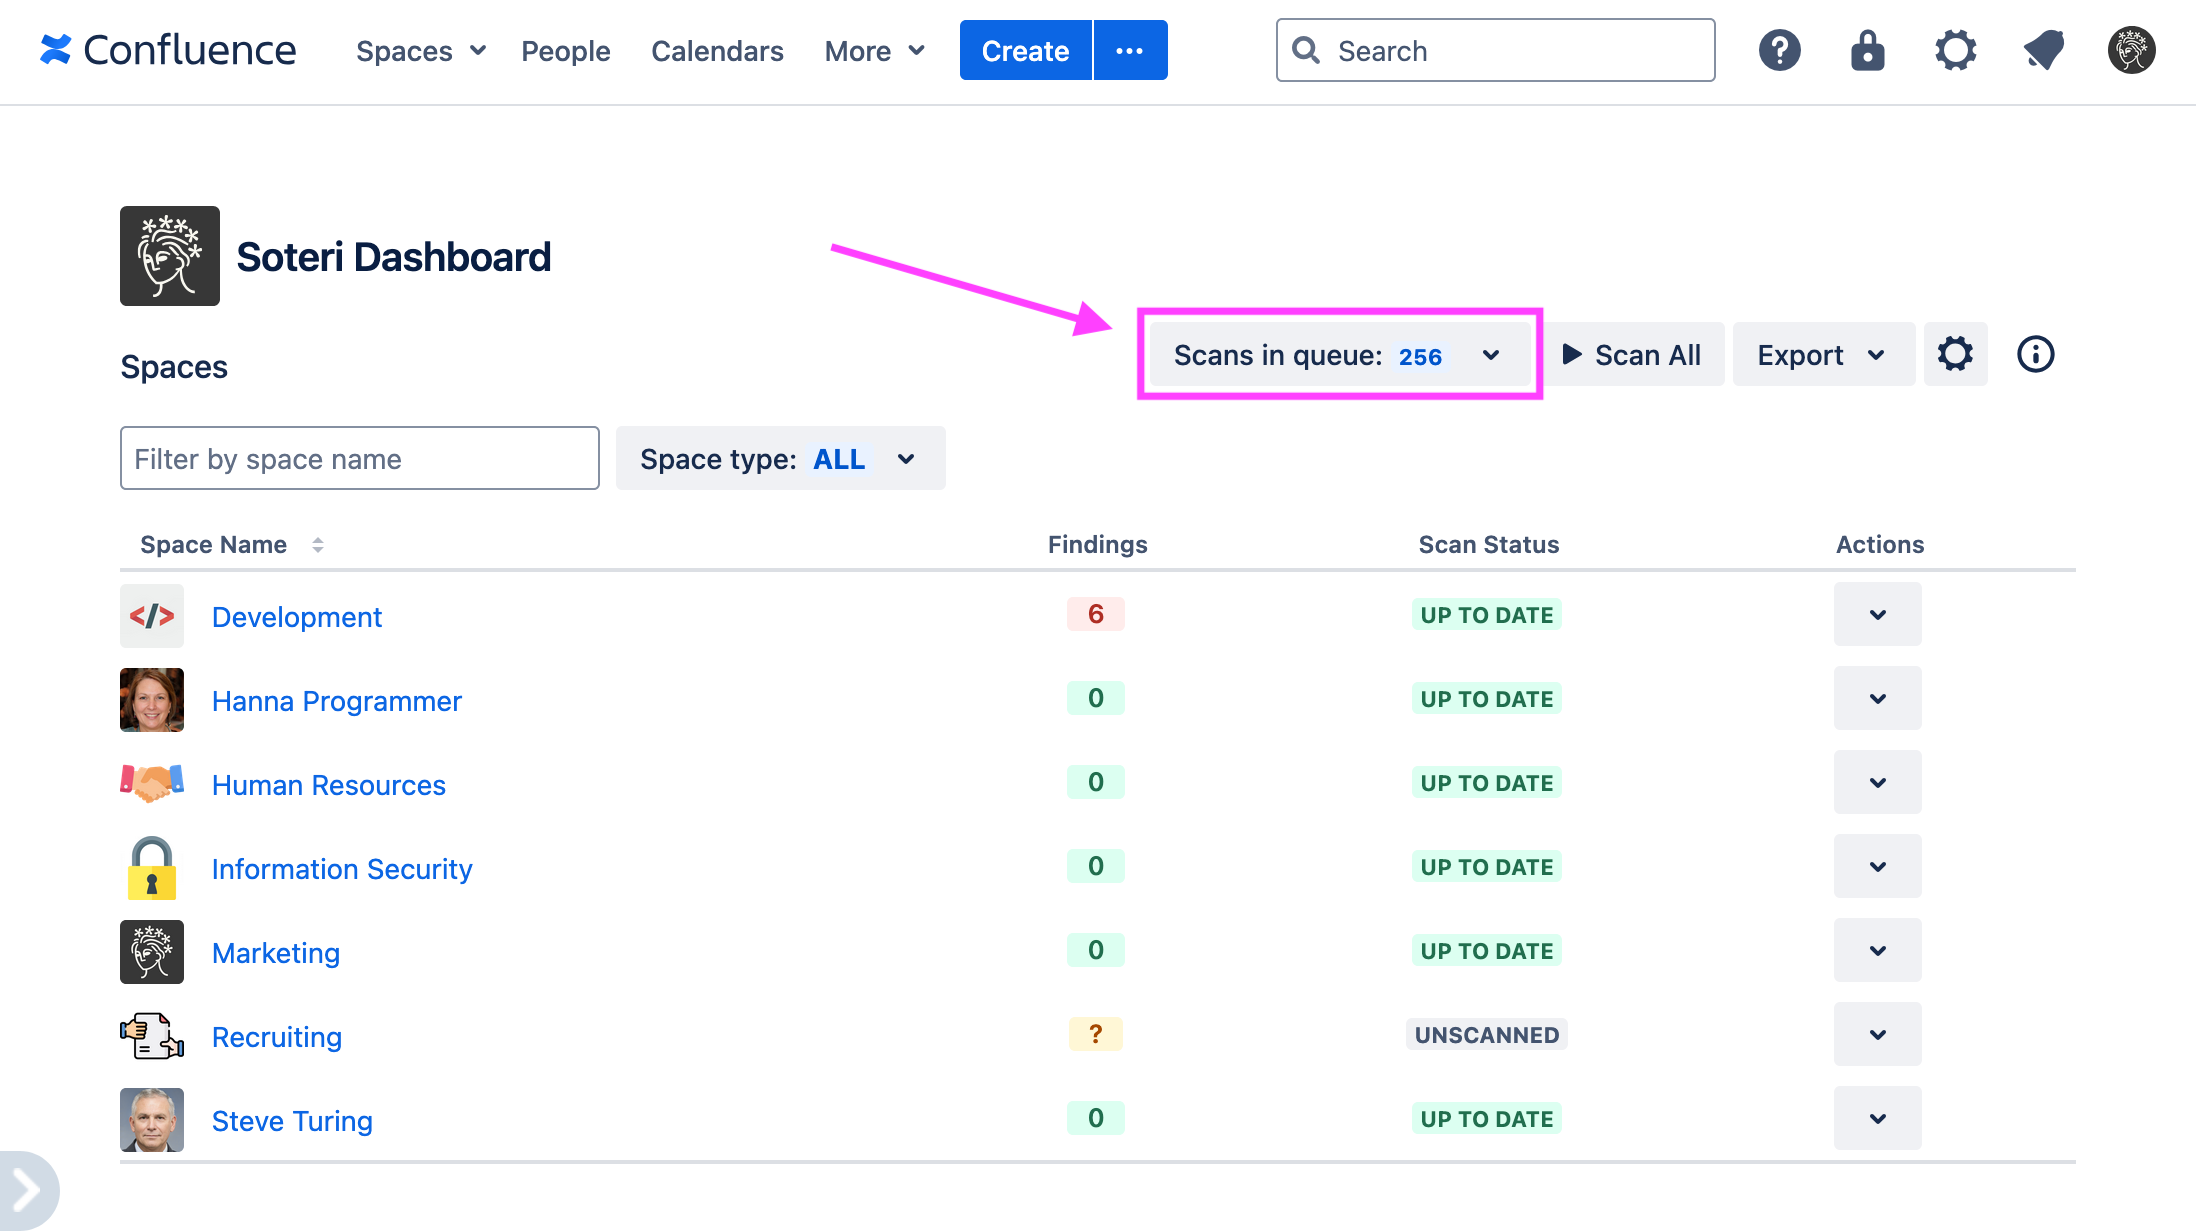
## Cancelling Scheduled Scans
Confluence administrators or any user granted [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md) who access the dashboard can click on the scan queue indicator to reveal the **Cancel Scans** button. Clicking this button will cancel all scheduled scans. Scans scheduled as part of the "[Keep space scans up to date](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md)" option will not be affected.
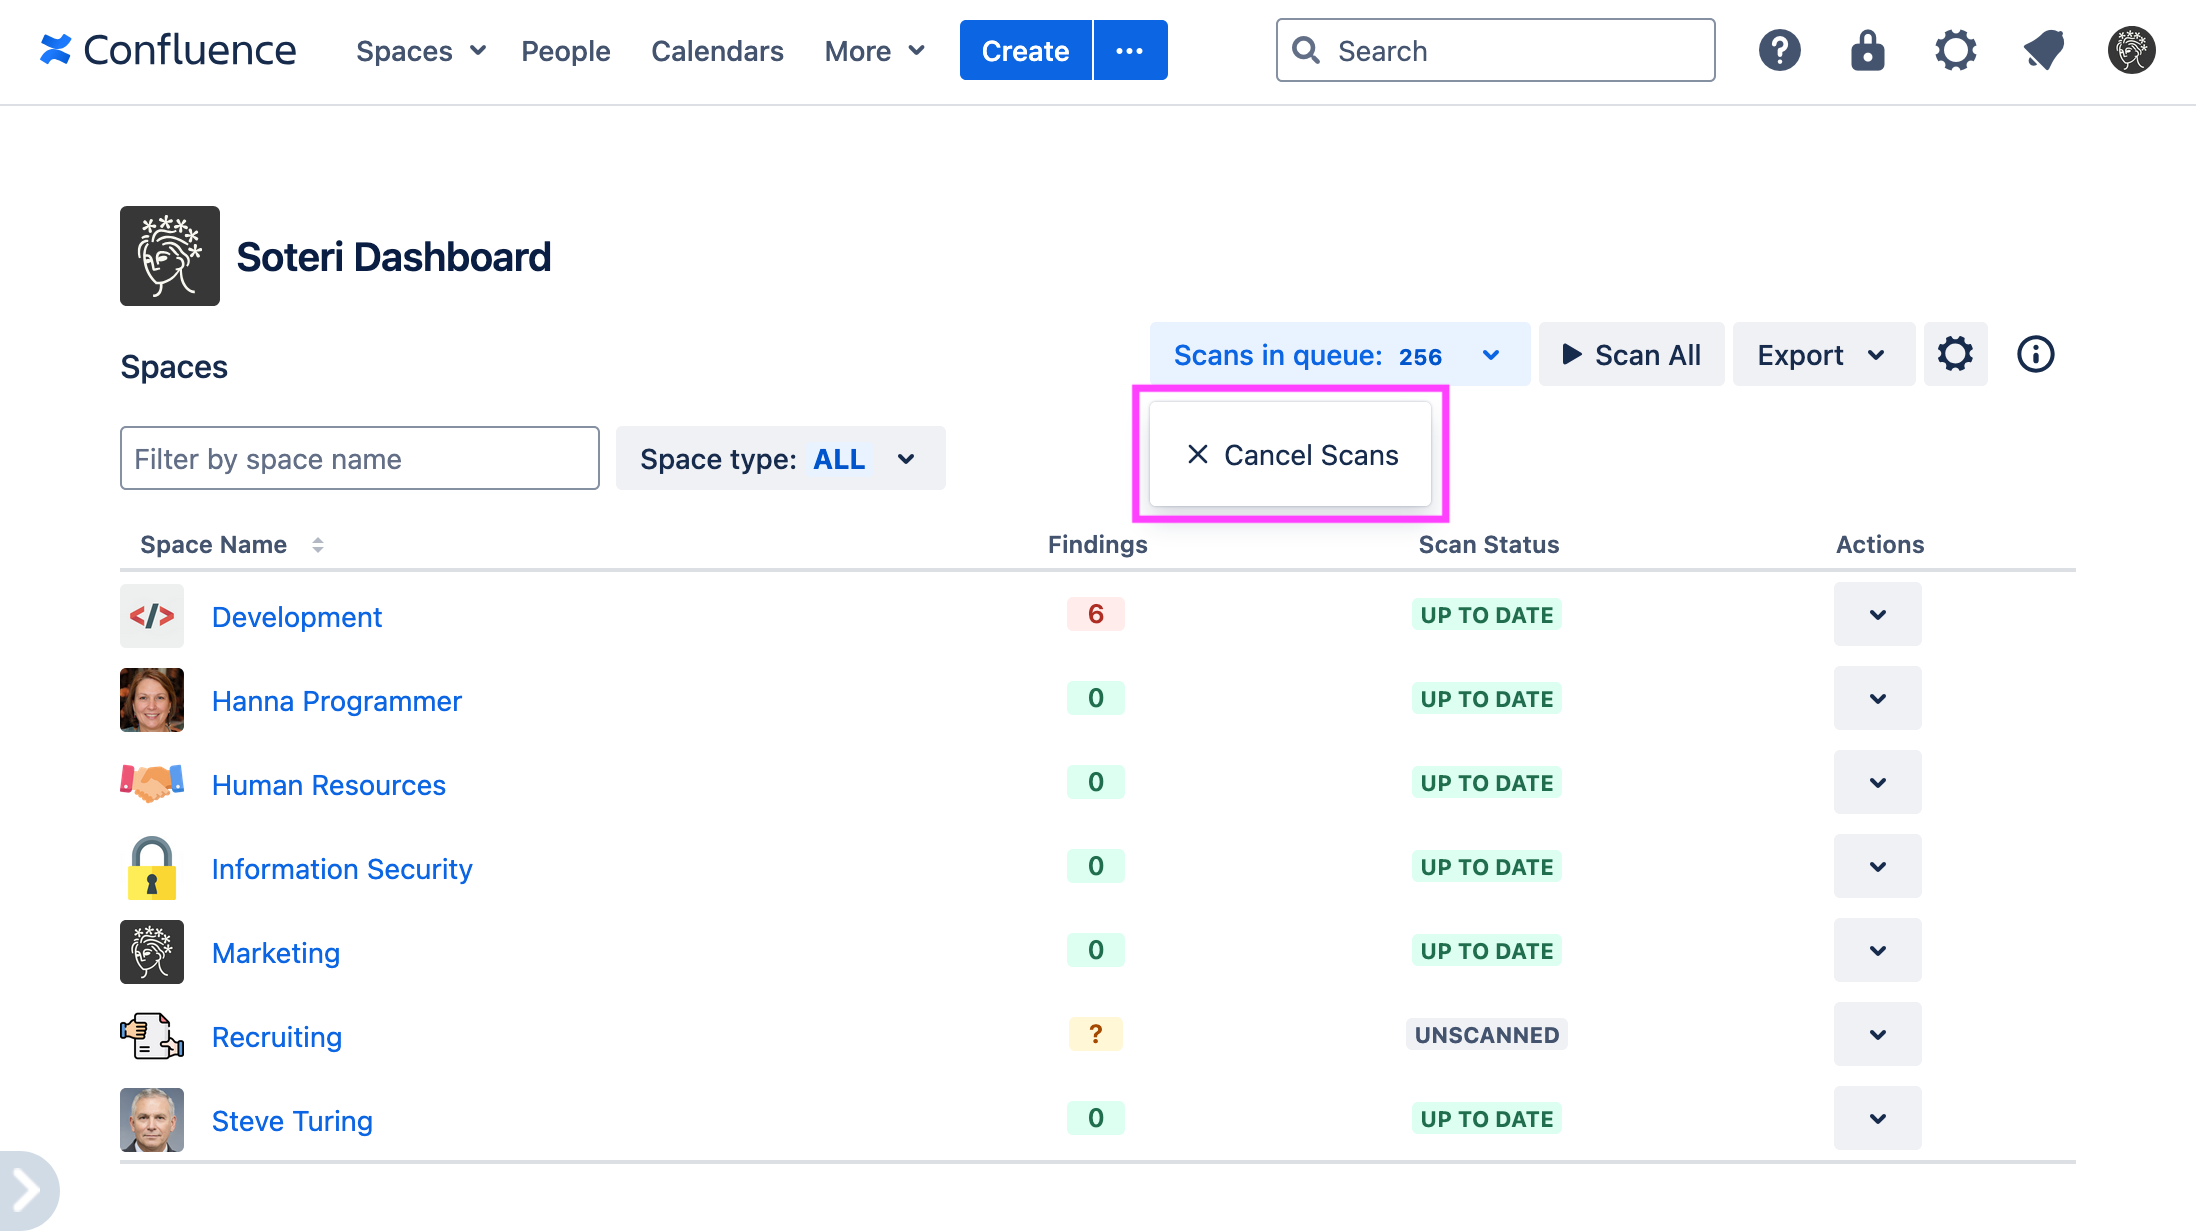
## Exporting the dashboard overview
Security for Confluence allows users to export the list of spaces visible on the dashboard together with their individual scan status, up to date status, and the number of unreviewed findings in that space.
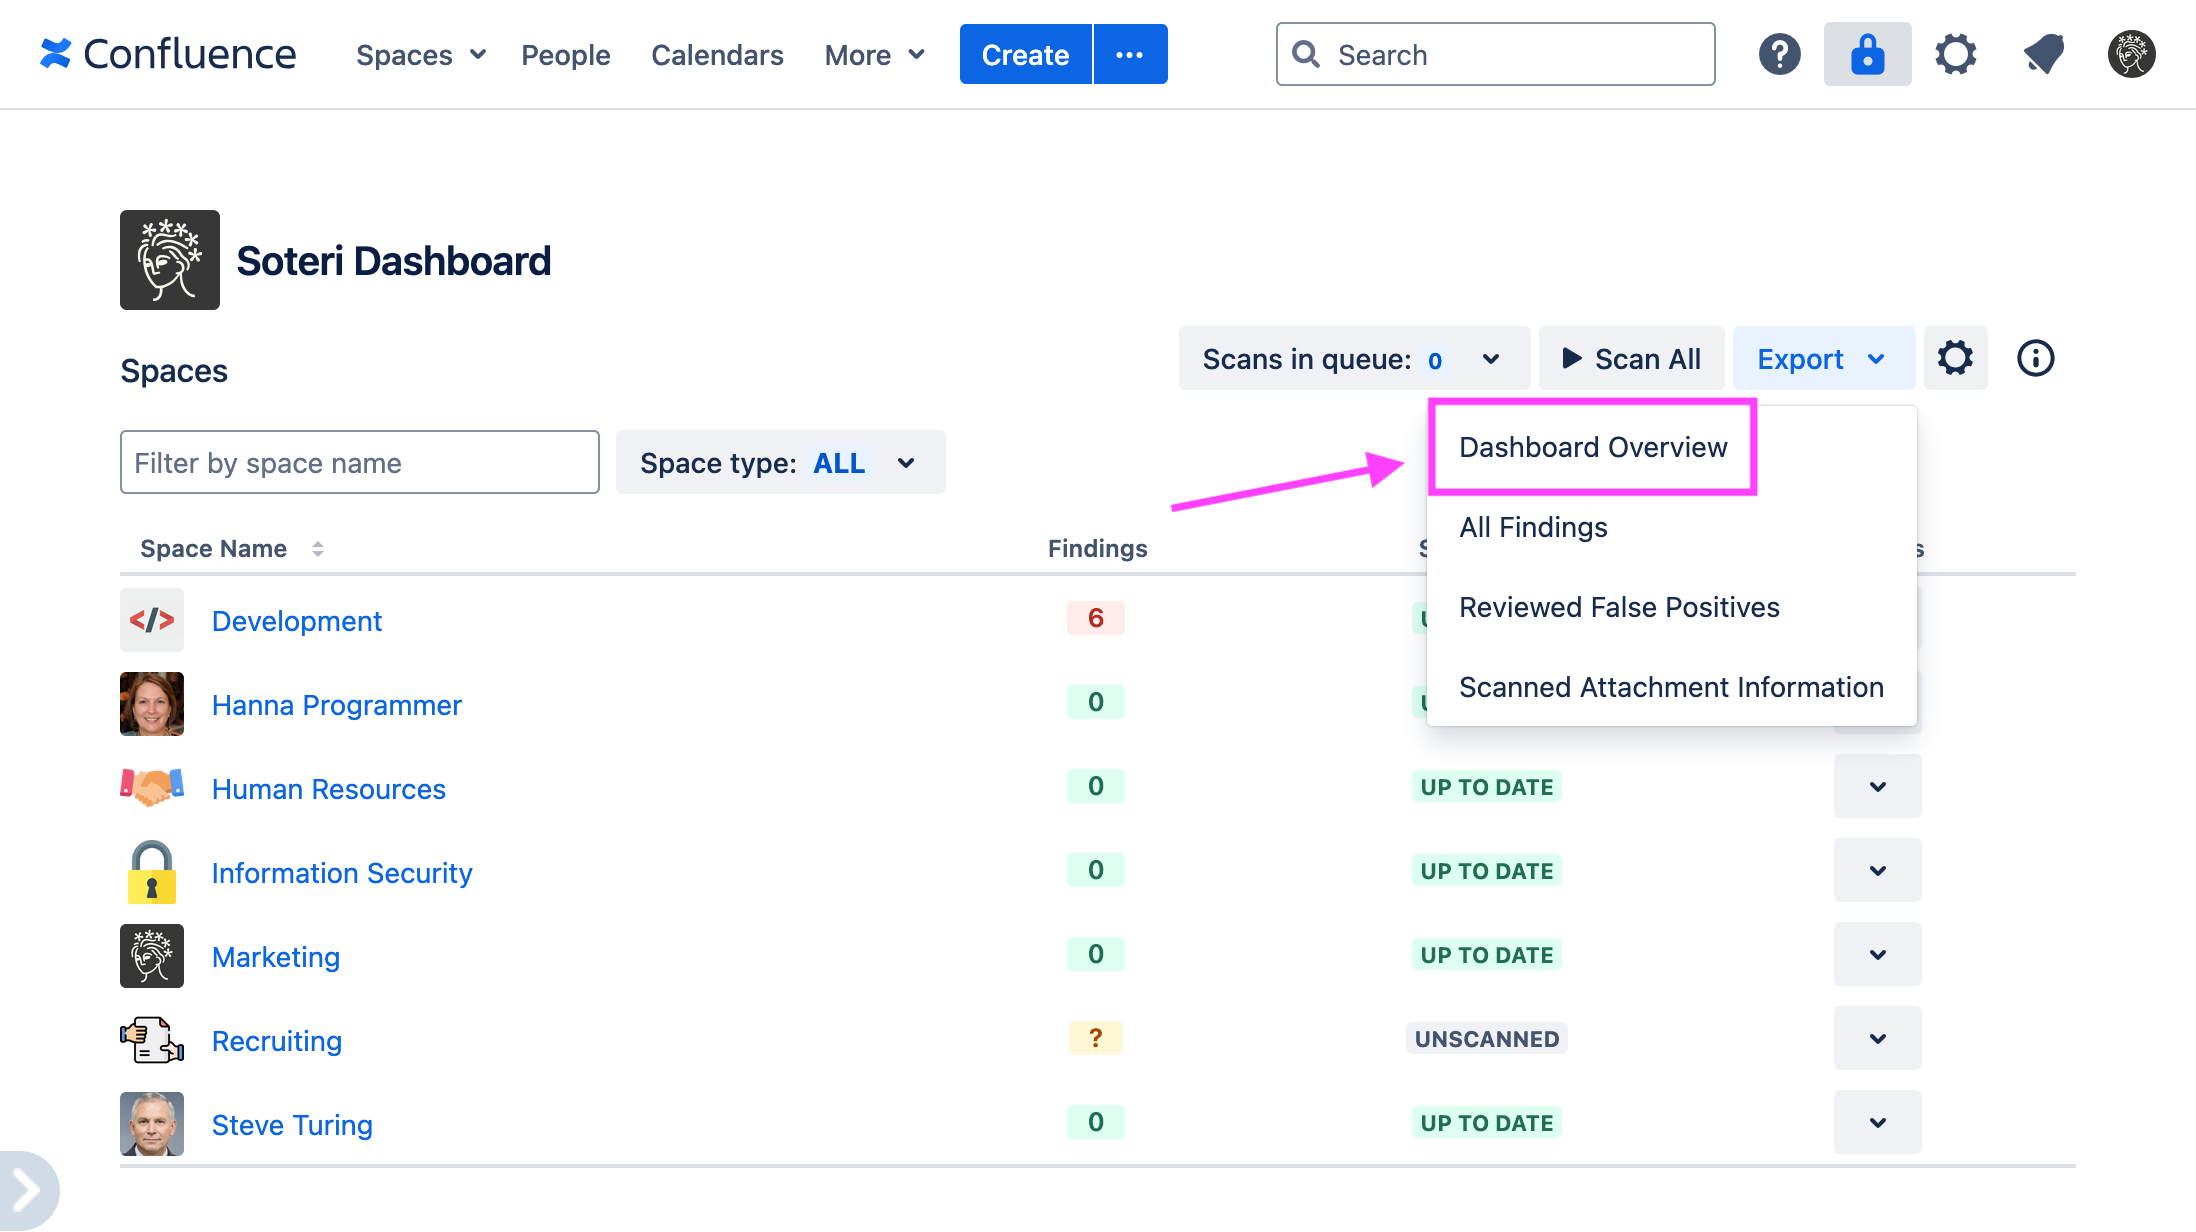
You can also export the dashboard overview using the [REST API](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Exporting-Dashboard-Overview).
---
version: "latest"
language: "en"
---
# Viewing Audited Events
To help administrators keep track of various events, **Security for Confluence**places entries in Confluence's Audit Log.
## Accessing the Audit Log
From the Confluence administration page, select **Audit log** (under "Administration") from the sidebar. This brings up the "Advanced audit log" page:
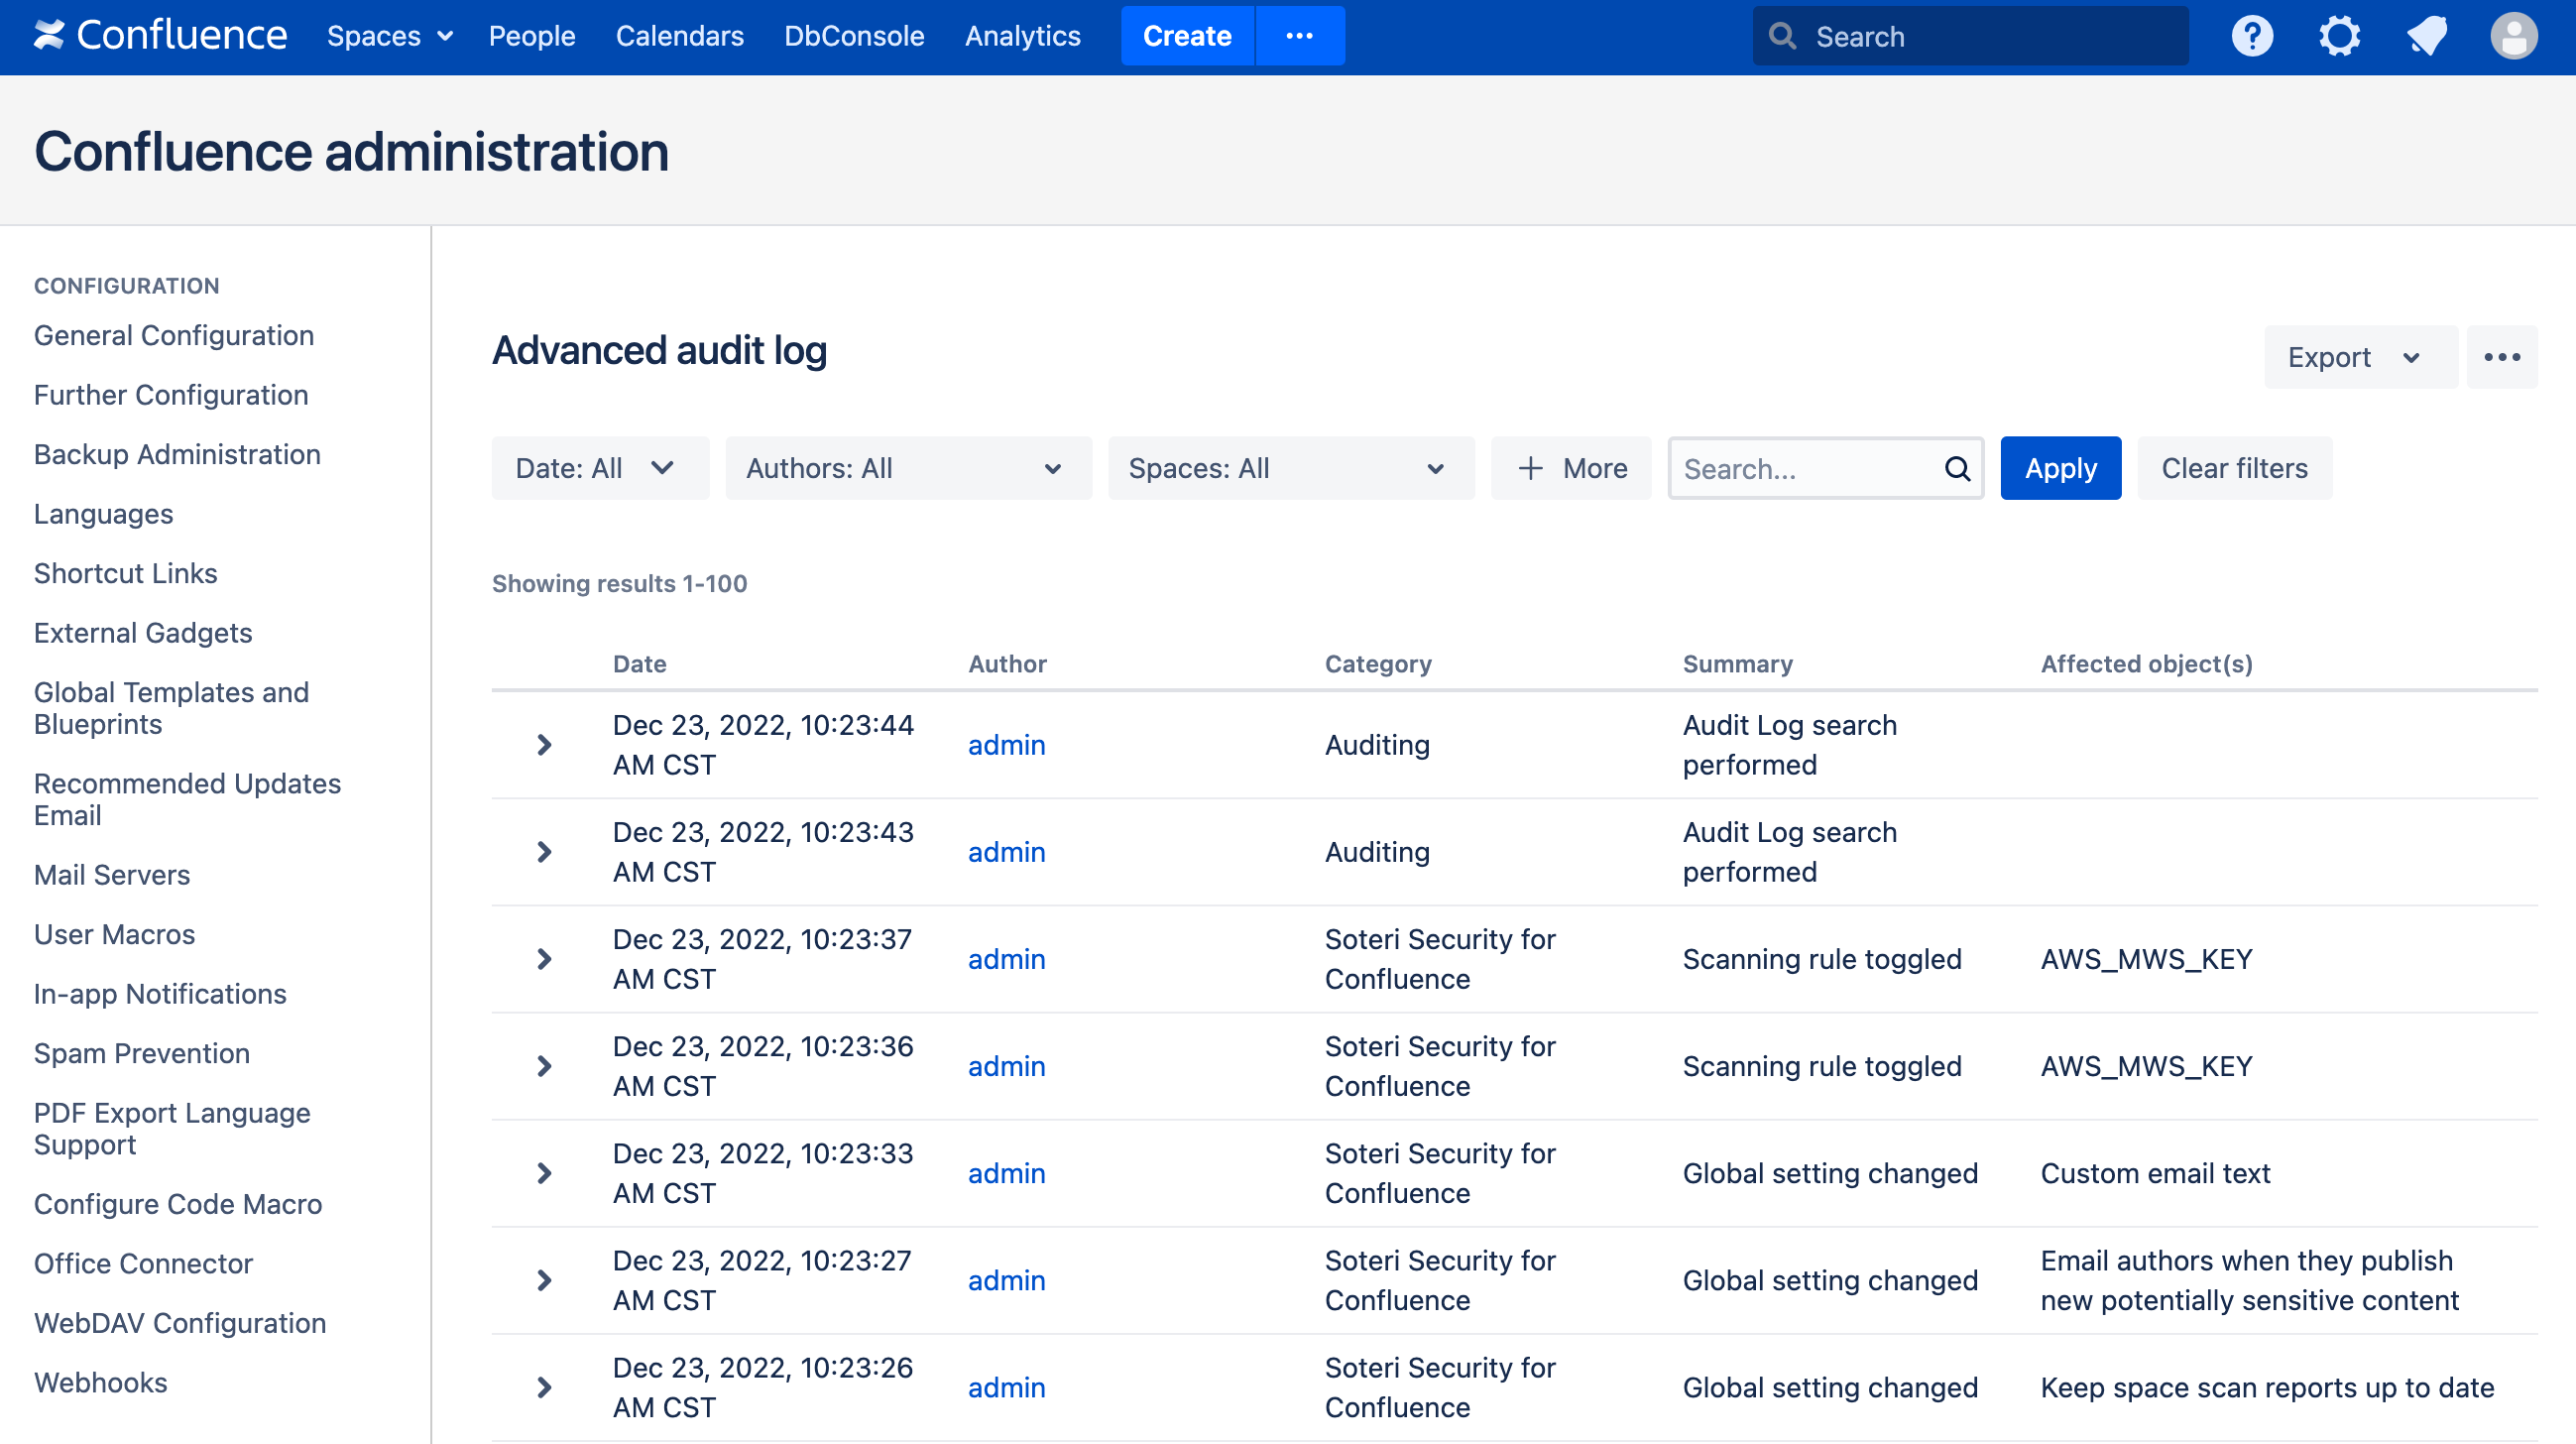
From here, click on the**+ More button** . A new **Categories** drop-down will appear. From that, select "Soteri Security for Confluence" to view only Security for Confluence audit log events. You can expand events to see more details:
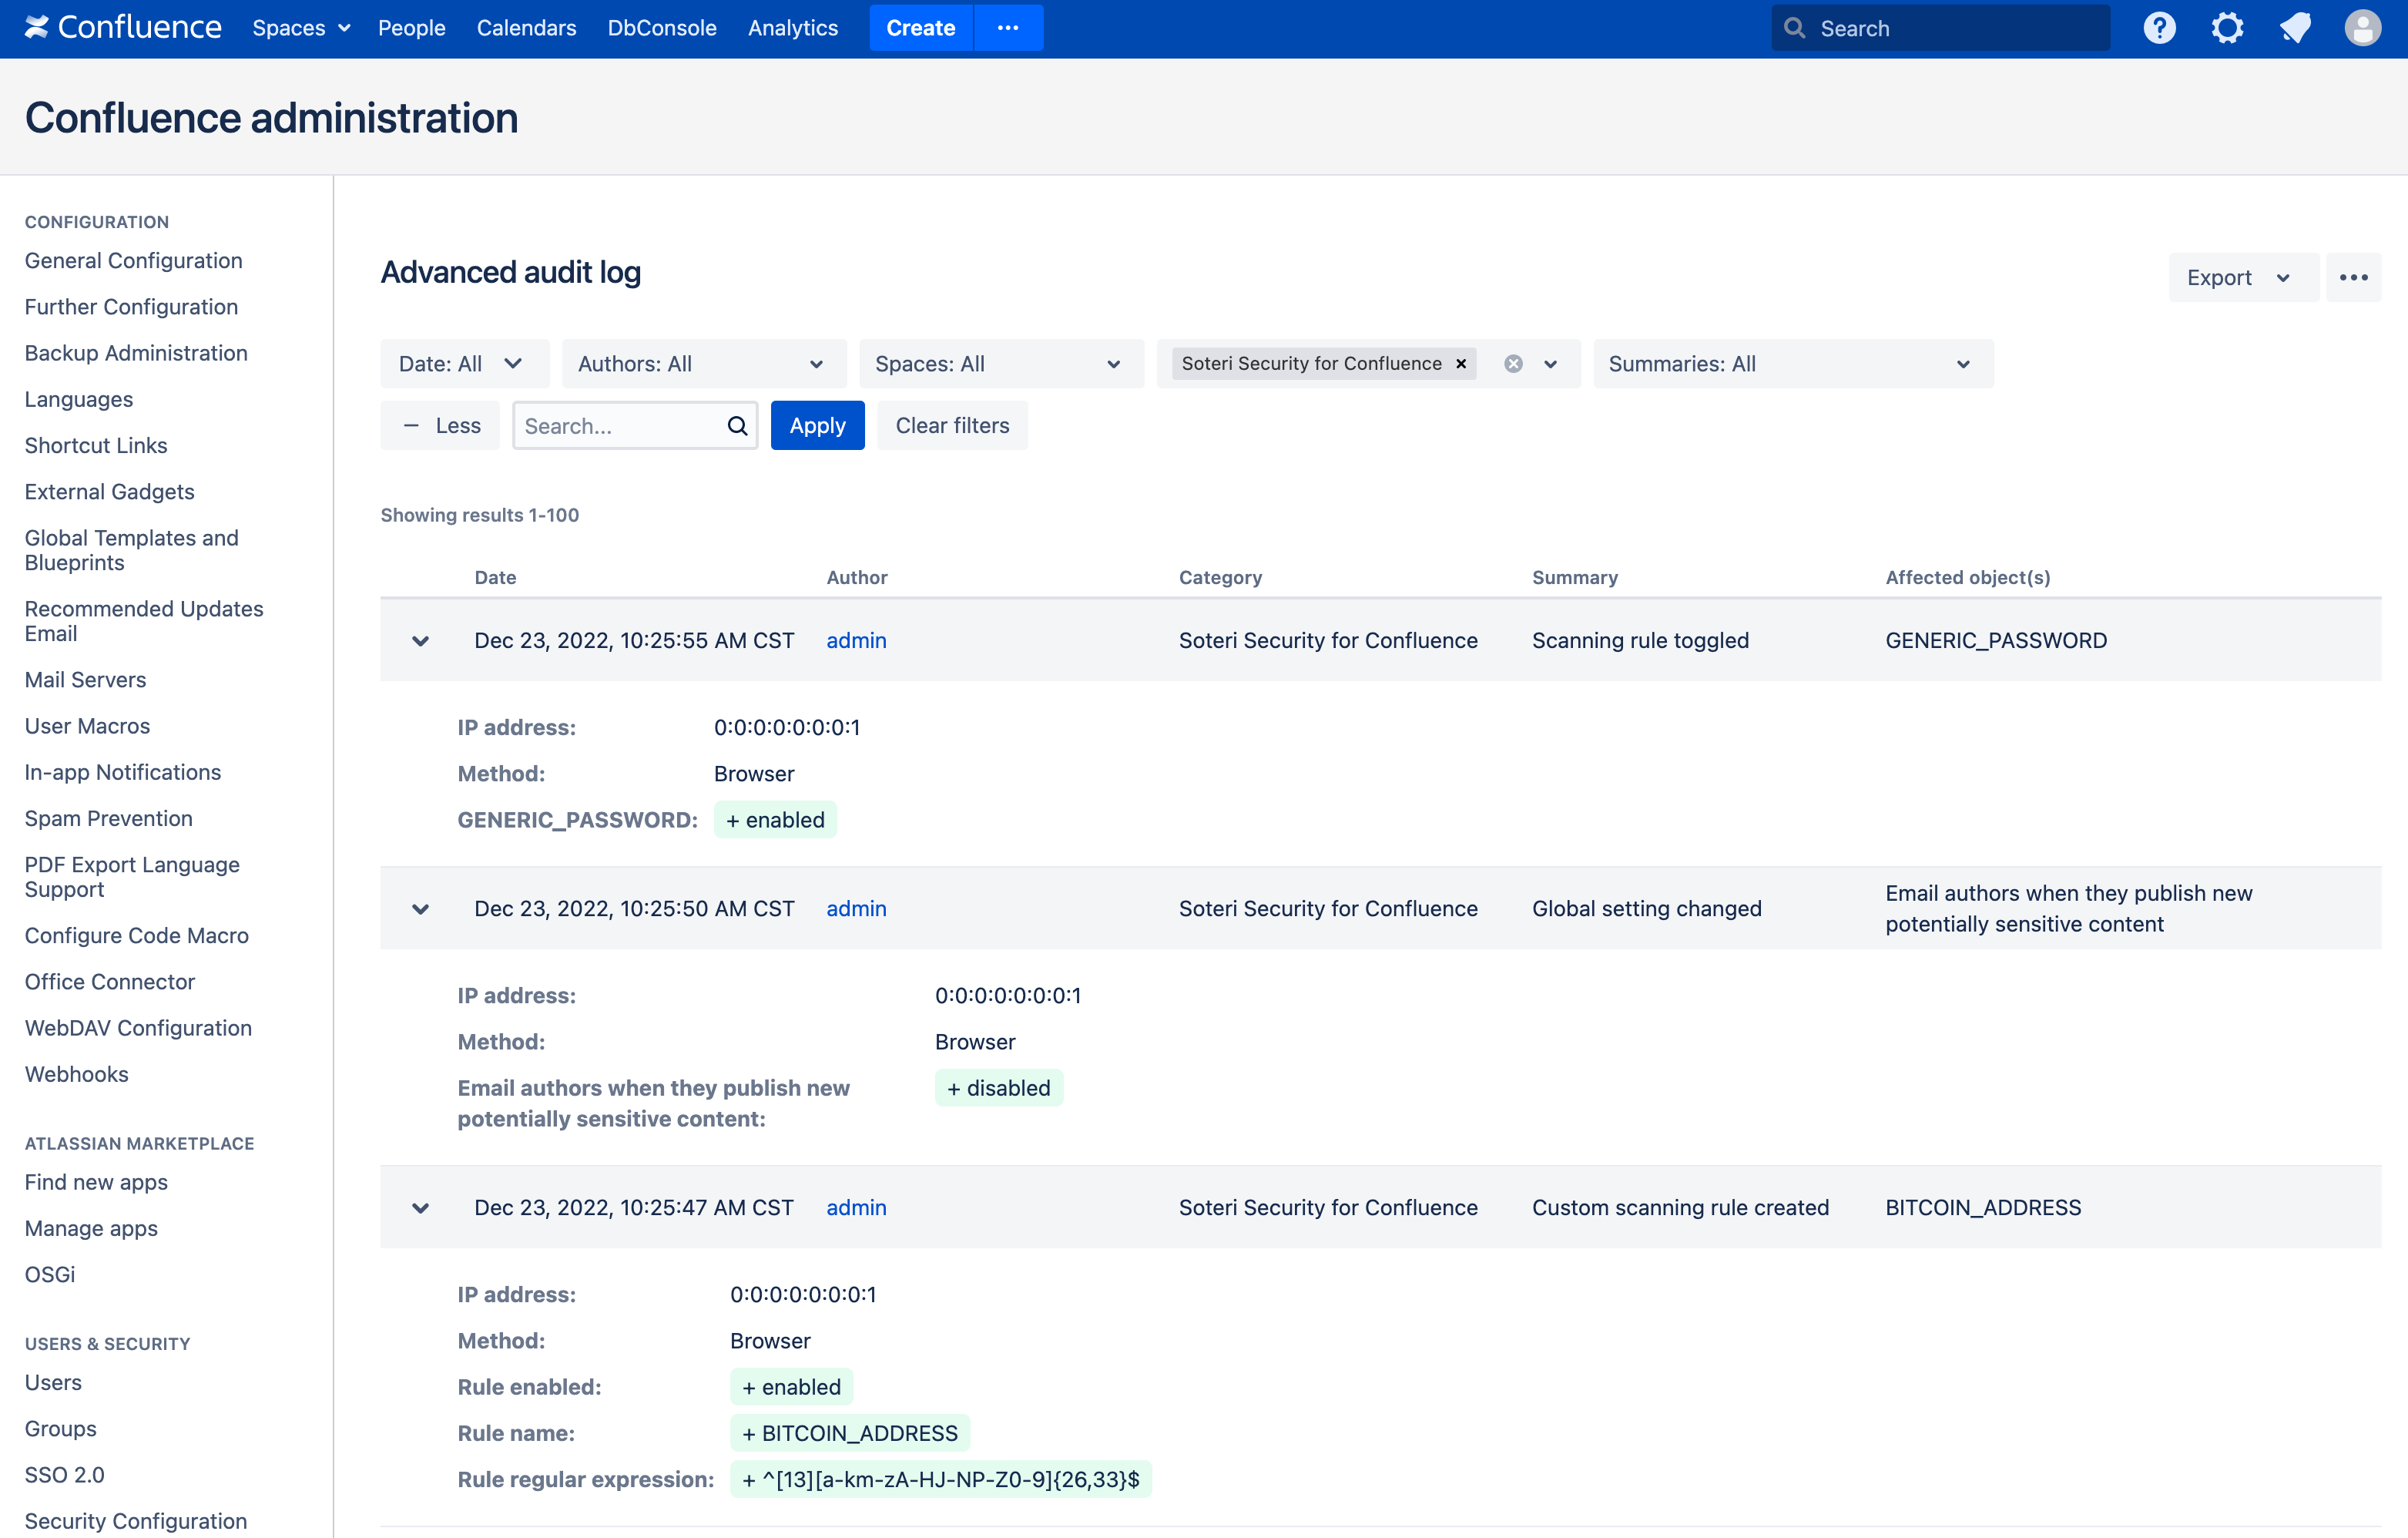
Confluence audit log access is only available to Confluence Administrators.
## Audited Events
The following **Security for Confluence** events are currently recorded in the audit log:
| **Audit Event Category** | **Description** |
|--------------------------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Scanning rule toggled | When a user [toggles a built-in rule](https://docs.soteri.io/security-for-confluence-dc/latest/enabling-and-disabling-global-scanning-rules.md). |
| Global setting changed | When a user changes a setting on the [settings page](https://docs.soteri.io/security-for-confluence-dc/latest/accessing-the-settings-page.md). |
| App administrator setting changed | When a user or group is added or removed from the list of users and groups with [explicit app access](https://docs.soteri.io/security-for-confluence-dc/latest/granting-access-to-additional-users-and-groups.md). |
| Custom scanning rule created | When a user creates a new [custom rule](https://docs.soteri.io/security-for-confluence-dc/latest/defining-custom-detection-rules.md). |
| Custom scanning rule updated | When a user changes a [custom rule](https://docs.soteri.io/security-for-confluence-dc/latest/defining-custom-detection-rules.md). |
| Custom scanning rule deleted | When a user deletes a [custom rule](https://docs.soteri.io/security-for-confluence-dc/latest/defining-custom-detection-rules.md). |
| Notification email sent: potentially sensitive content | When a [notification email](https://docs.soteri.io/security-for-confluence-dc/latest/email-notifications-for-content-authors.md) is sent due to potentially sensitive content being published. |
| User edit introduced potentially sensitive content | When a user edit [introduces potentially sensitive content](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md). This includes new and edited pages, blog posts, comments, and attachment uploads. * The events are only generated when the [Keep space scans up to date](https://docs.soteri.io/security-for-confluence-dc/latest/automatically-scanning-content.md) option is enabled and the space has already been fully scanned. * The events will state "System" as the author. The actual author of the edit will be listed under "affected object(s)". |
| Scan finding reviewed | When a user marks a scan finding [reviewed](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md). |
| Scan finding reviewed individually | When a user marks a scan finding [reviewed for the specific page, comment, or attachment](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Reviewing-findings-in-the-scope-of-a-page,-comment,-or-attachment-only). |
| Scan finding un-reviewed | When a user unmarks a scan finding [reviewed](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md). |
| Scan finding un-reviewed individually | When a user unmarks a scan finding [reviewed for the specific page, comment, or attachment](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Reviewing-findings-in-the-scope-of-a-page,-comment,-or-attachment-only). |
| All scan findings un-reviewed | When a user unmarks all findings [reviewed](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md) for a space. |
| All individual scan findings un-reviewed | When a user unmarks all individual findings [reviewed for a specific page, comment, or attachment.](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Reviewing-findings-in-the-scope-of-a-page,-comment,-or-attachment-only) |
| Content scan triggered | When a user triggers a [scan](https://docs.soteri.io/security-for-confluence-dc/latest/overview.md#Scanning-spaces-from-the-Soteri-Dashboard) of a specific piece of content. |
| Space scan triggered | When a user triggers a [scan](https://docs.soteri.io/security-for-confluence-dc/latest/overview.md#Scanning-spaces-from-the-Soteri-Dashboard) of a specific space. |
| Whole instance scan triggered | When a user triggers a [scan](https://docs.soteri.io/security-for-confluence-dc/latest/overview.md#Scanning-spaces-from-the-Soteri-Dashboard) of the entire instance. |
| Scheduled scans canceled | When scheduled scans are [cancelled](https://docs.soteri.io/security-for-confluence-dc/latest/overview.md#Scanning-spaces-from-the-Soteri-Dashboard) by a user. |
| Dashboard overview exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md#Exporting-the-dashboard-overview) the dashboard overview. |
| Findings exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) findings for a specific space. |
| All findings exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) all findings. |
| False positives exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) reviewed findings for a specific space. |
| All false positives exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) all reviewed findings. |
| Attachment scan information exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) scanned attachment information for a specific space. |
| All attachment scan information exported | When a user [exports](https://docs.soteri.io/security-for-confluence-dc/latest/exporting-findings.md) all scanned attachment information. |
| Globally reviewed false positives exported | When a user [exports globally reviewed false positives](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Exporting-globally-reviewed-false-positives). |
| Globally reviewed false positives changed | When a user [changes globally reviewed false positives](https://docs.soteri.io/security-for-confluence-dc/latest/hiding-false-positives-revoked-credentials-etc.md#Adding-new-global-false-positives). |
| Cancelled exports | When a user [cancels running exports](https://docs.soteri.io/security-for-confluence-dc/latest/rest-api-for-scripting-and-automation.md#Cancel-running-exports). |
## REST API
Confluence provides a REST API for accessing all audit log events. For instance, you can fetch recent audit events with a REST API call that looks like this:
curl -u admin https://{confluence.server}/rest/api/audit
Reference the [REST API documentation for your Confluence version](https://docs.atlassian.com/ConfluenceServer/rest/7.13.7/#api/audit) for more information.
## External Integration
The Confluence audit log can be integrated with external SIEM tools (like the ELK stack) to do things like notify administrators when Security for Confluence settings are changed, or potentially sensitive content is published. Reference [Atlassian's Guide to audit log integration for more information](https://confluence.atlassian.com/doc/audit-log-integrations-in-confluence-1005333794.html).
---
version: "latest"
language: "en"
---
# What content can Security for Confluence Scan?
Currently, Security for Confluence scans:
* Pages
* Blog posts
* Attachments
* See [Scanning Files Attached to Pages](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-files-attached-to-pages.md) for more information on supported file types
* Comments, including top-level comments on pages and blog posts, inline comments on pages and blog posts, and comments on attachments
Note that drafts are not yet scanned.
---
version: "latest"
language: "en"
---
# What do I do if a security scan finds a secret?
*All secrets detected by a security scan should be considered compromised.*Once a secret is published, anyone who had read access to the page could have obtained a copy. Locking down the permissions on the page, deleting it, or deleting all the page versions which contained the secret are all good steps, but they don't sufficiently remediate the risk.
Soteri recommends to:
* Change the secret.
* If a password is found, change it.
* If an access token is found, generate a new access token and update your services to use the new token. Once all your services have been updated, revoke the old token.
* Delete the secret from Confluence. Secrets improperly stored in Confluence, revoked or not, send the signal to users that secrets can be stored this way.
Secrets in comments cannot be removed without deleting the entire comment. Also see [Scanning Comments \| Removing secrets in comments](https://docs.soteri.io/security-for-confluence-dc/latest/scanning-comments.md#Removing-secrets-in-comments)
---
version: "latest"
language: "en"
---
# What is the GENERIC\_PASSWORD rule and why is it disabled by default?
The GENERIC_PASSWORD rule is off by default because it's a bit different than the other rules -- rather than matching a very specific key type, with minimal false positives, it searches for general occurrences and variations of the term "password". This rule is meant to catch the unintentional use of passwords in code or documentation.
However, due to its broad nature, this rule generates many false positives; to enable it would require your organization to set up a process to review and disposition them. We feel that you would better know if your organization would have the resources available for such a process.
---
version: "latest"
language: "en"
---
# Why are newline matchers not allowed in custom rules?
Security for Confluence Data Center scans line-by-line, so newline matchers will never be matched. Existing rules which contain newlines will continue to run, but cannot be edited without removing the newline characters.
List of disallowed sequences:
* `\n`, `\x0a`, `\x0A`, `\u000a`, `\u000A`
* `\r`, `\x0d`, `\x0D`, `\u000d`, `\u000D`
* `\R`
[Next Page](https://docs.soteri.io/llms-full.txt/1)