latest 6.2.x 6.1.x 6.0.x 5.8.x 5.7.x 5.6.x 5.5.x 5.4.x 5.3.x 5.2.x 5.1.x 5.0.x 4.18.x 4.17.0 4.16.x 4.15.x 4.14.x 4.13.0 4.11.x 4.8.0 4.7.0 4.6.0 4.5.0 4.4.0 4.2.0 4.1.0 4.0.0 3.22.0 3.21.0 3.20.0 3.19.0 3.18.0 3.17.0 3.16.0 3.15.0 3.14.0 3.13.0 3.12.0 3.11.0 3.10.0 3.9.0 3.8.0 3.7.0 3.6.0 3.5.0 3.4.0 3.3.0 3.2.0
Auto Light Dark
Auto Light Dark
latest 6.2.x 6.1.x 6.0.x 5.8.x 5.7.x 5.6.x 5.5.x 5.4.x 5.3.x 5.2.x 5.1.x 5.0.x 4.18.x 4.17.0 4.16.x 4.15.x 4.14.x 4.13.0 4.11.x 4.8.0 4.7.0 4.6.0 4.5.0 4.4.0 4.2.0 4.1.0 4.0.0 3.22.0 3.21.0 3.20.0 3.19.0 3.18.0 3.17.0 3.16.0 3.15.0 3.14.0 3.13.0 3.12.0 3.11.0 3.10.0 3.9.0 3.8.0 3.7.0 3.6.0 3.5.0 3.4.0 3.3.0 3.2.0

Repository-level Scan Report

Developers (anyone with repository write access) can scan their repositories for vulnerabilities, including any custom vulnerabilities defined in the global rules.
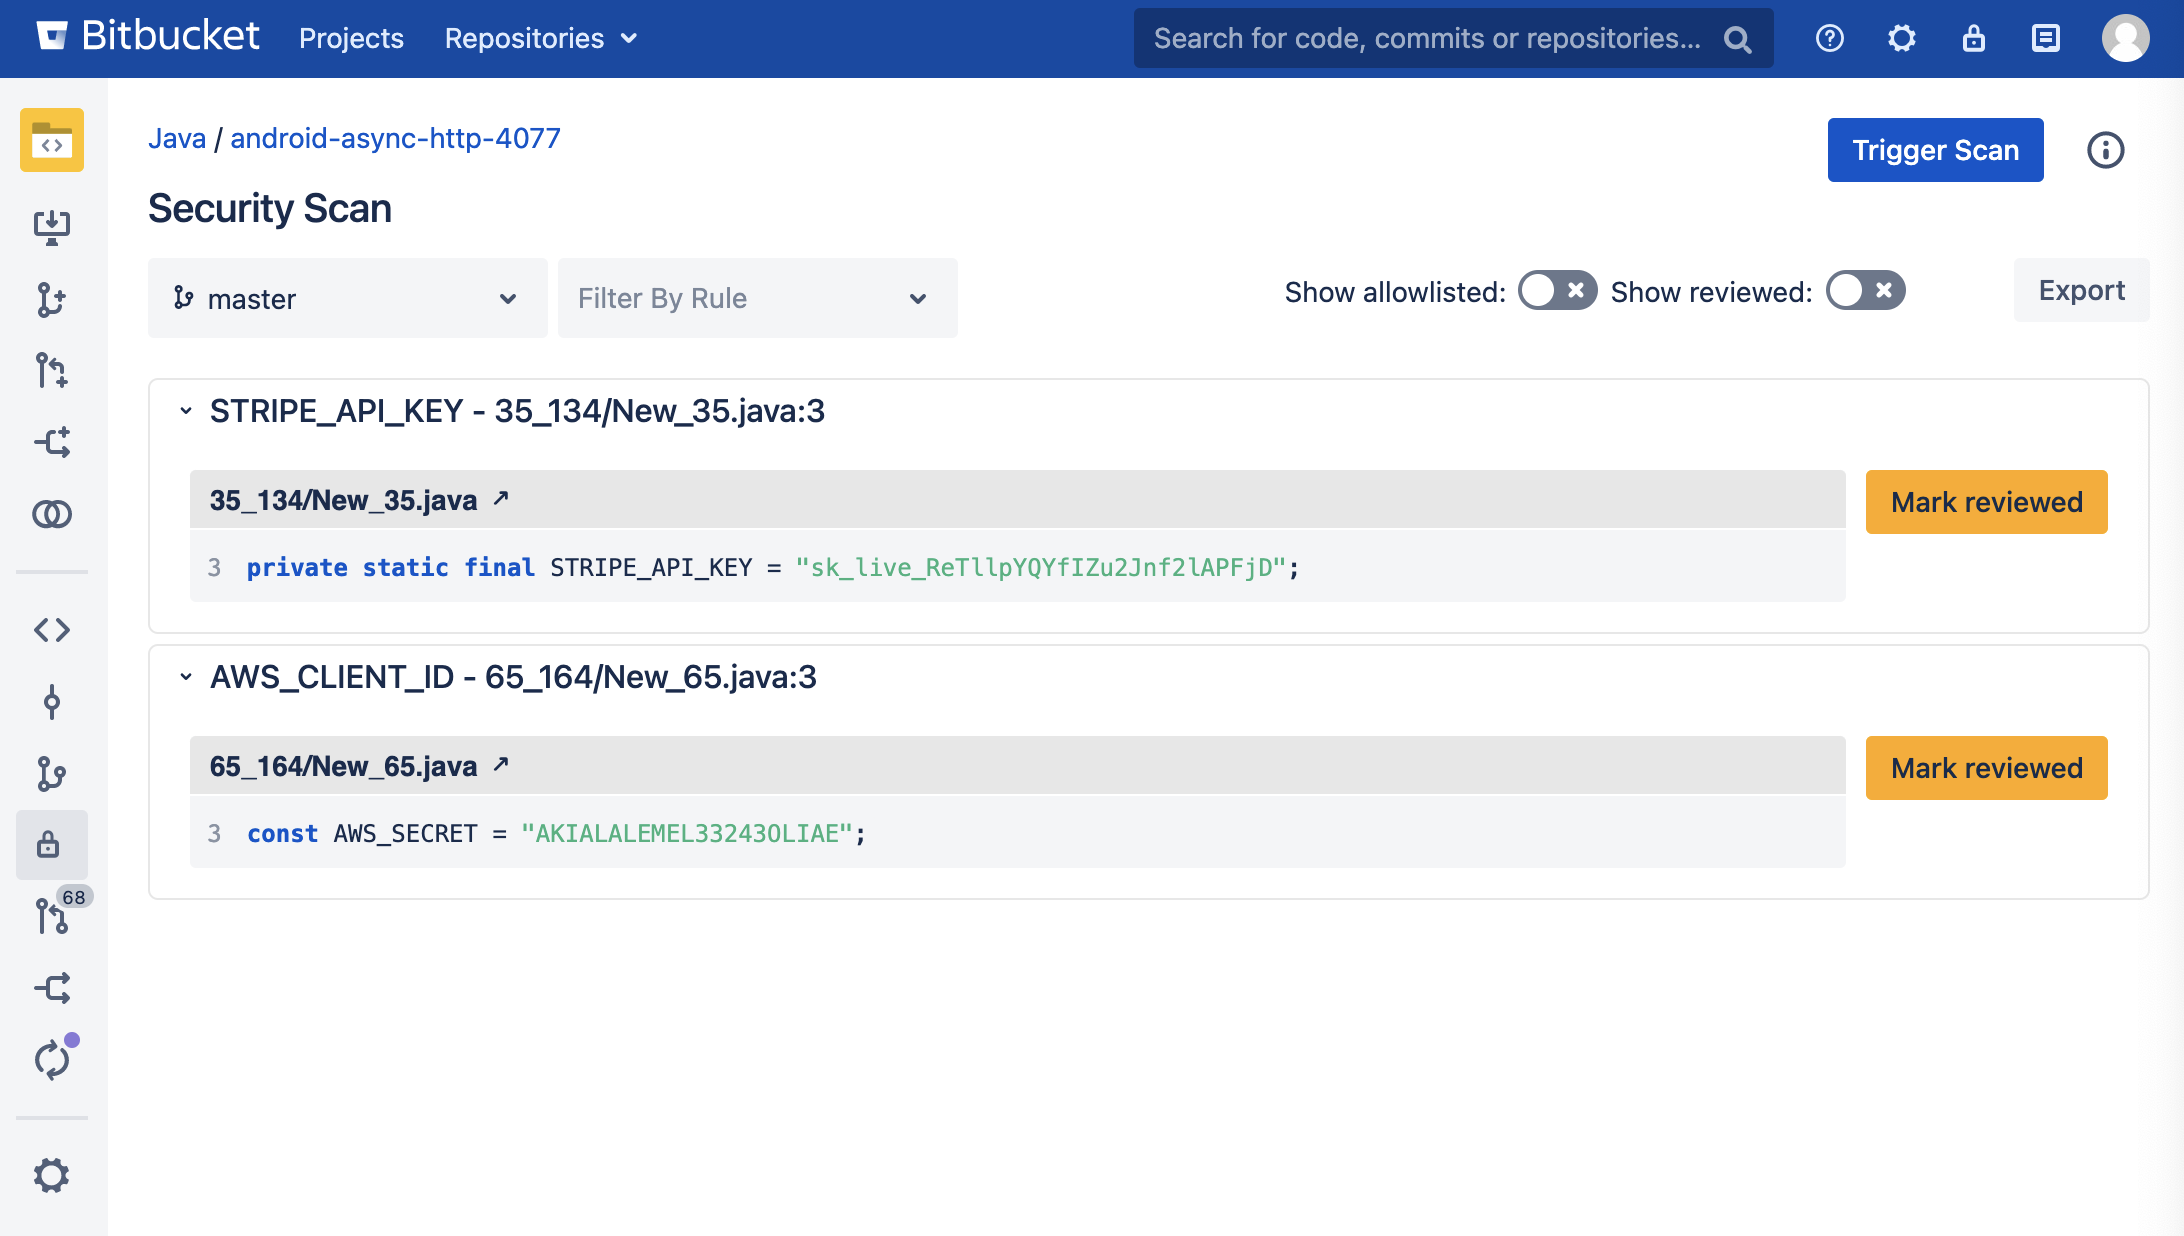
image-20210917-000836.png
The repository scan report page


To view and trigger a repository scan, you will need Repository Administrator permissions. Navigate to your repository of choice, and then go to the new Security Tab.
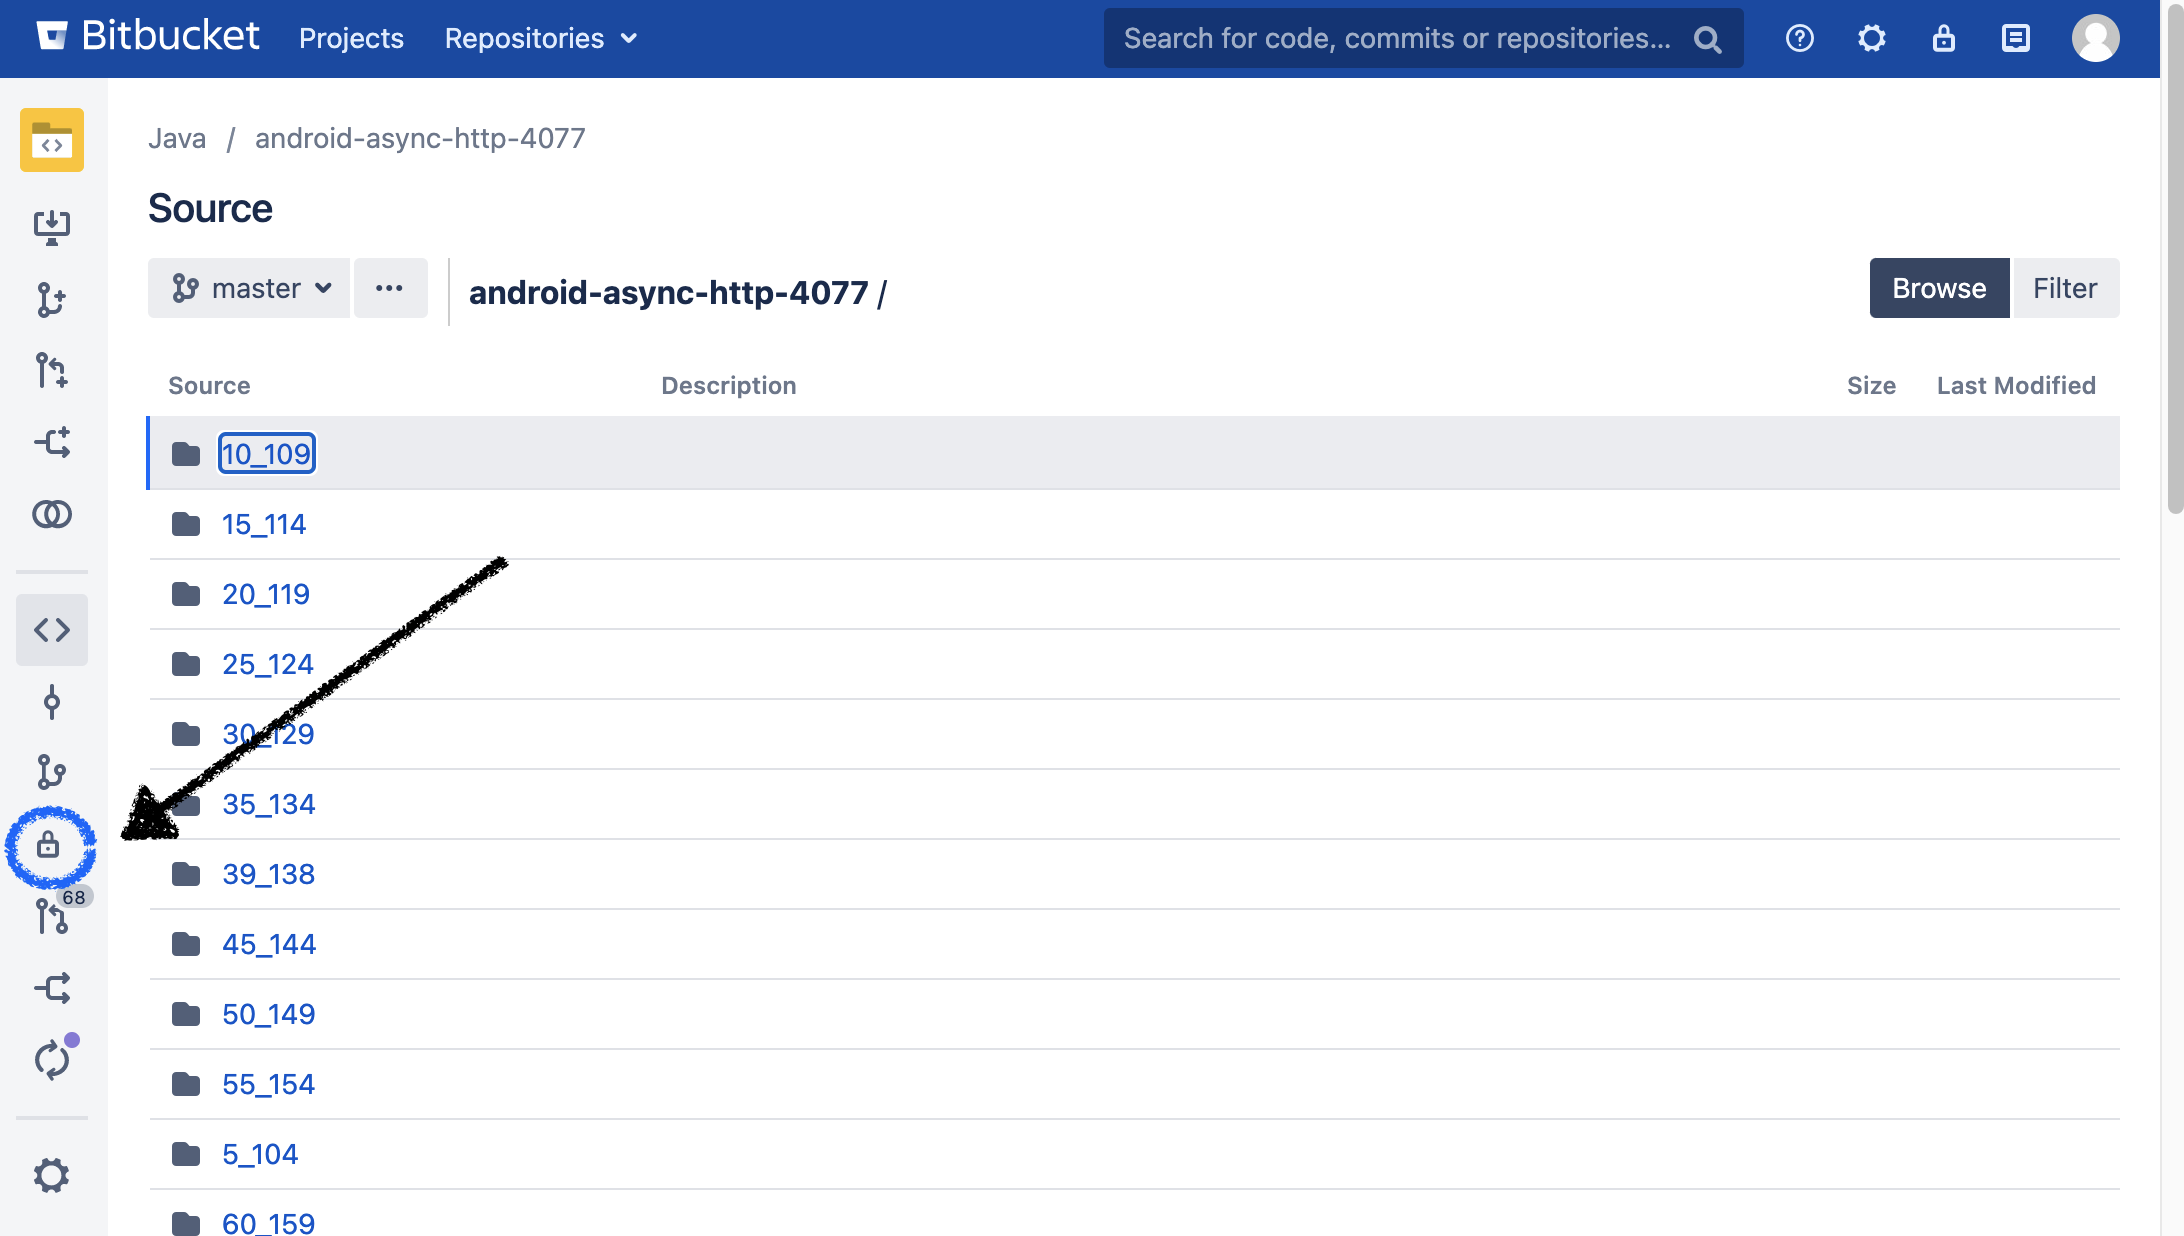
image-20210917-001236.png


Once in the security tab click the Trigger Scan button:
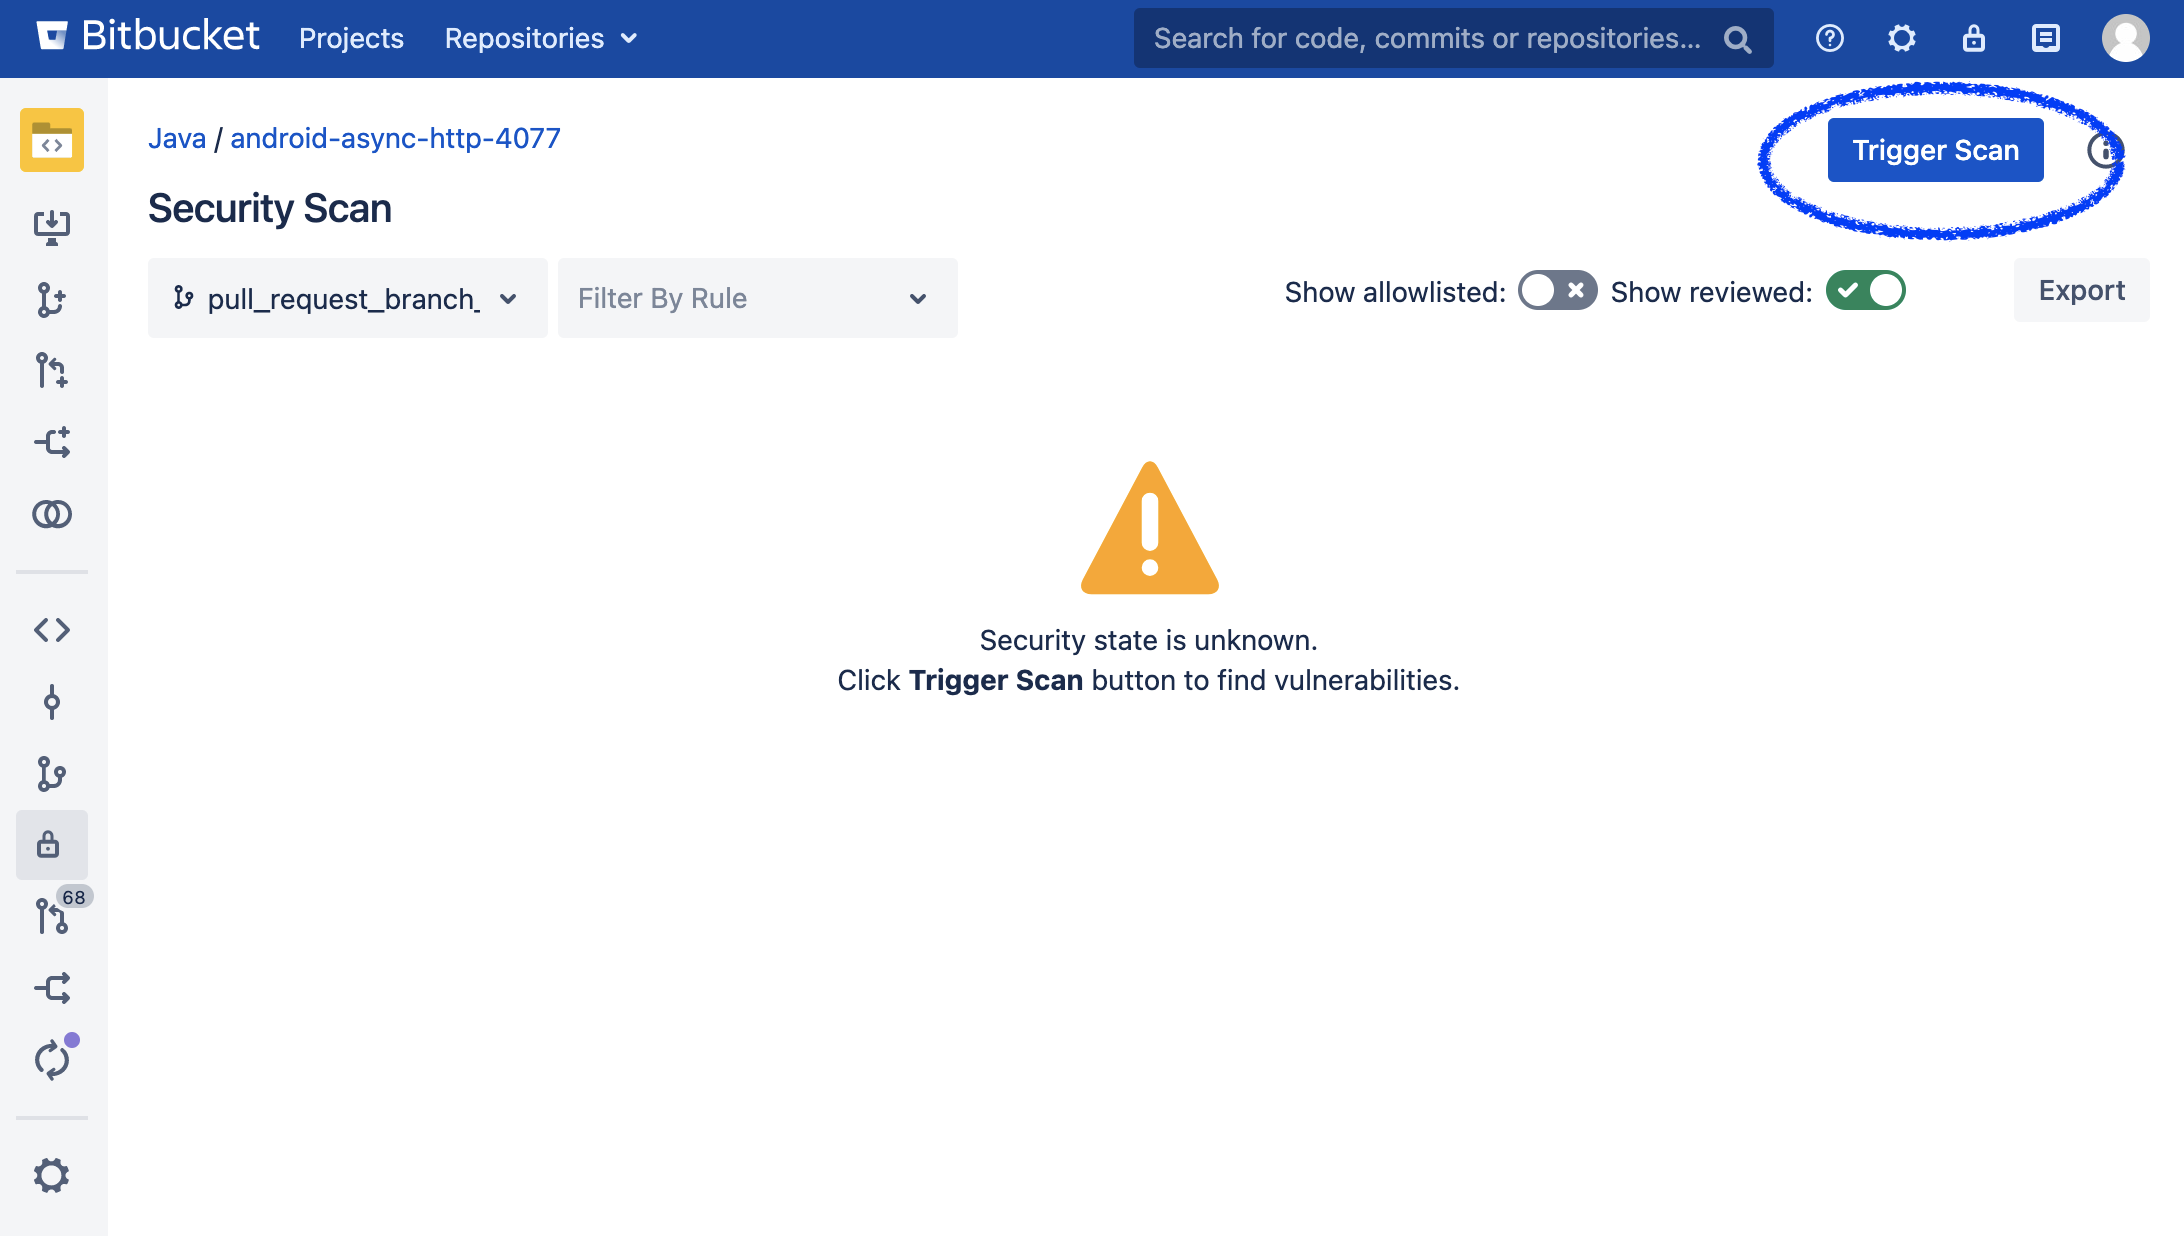
image-20210917-001335.png


This will cause either a scan to start or be scheduled if Bitbucket already has multiple scans ongoing. Results will start to populate as the app finds vulnerabilities in files within the repository:
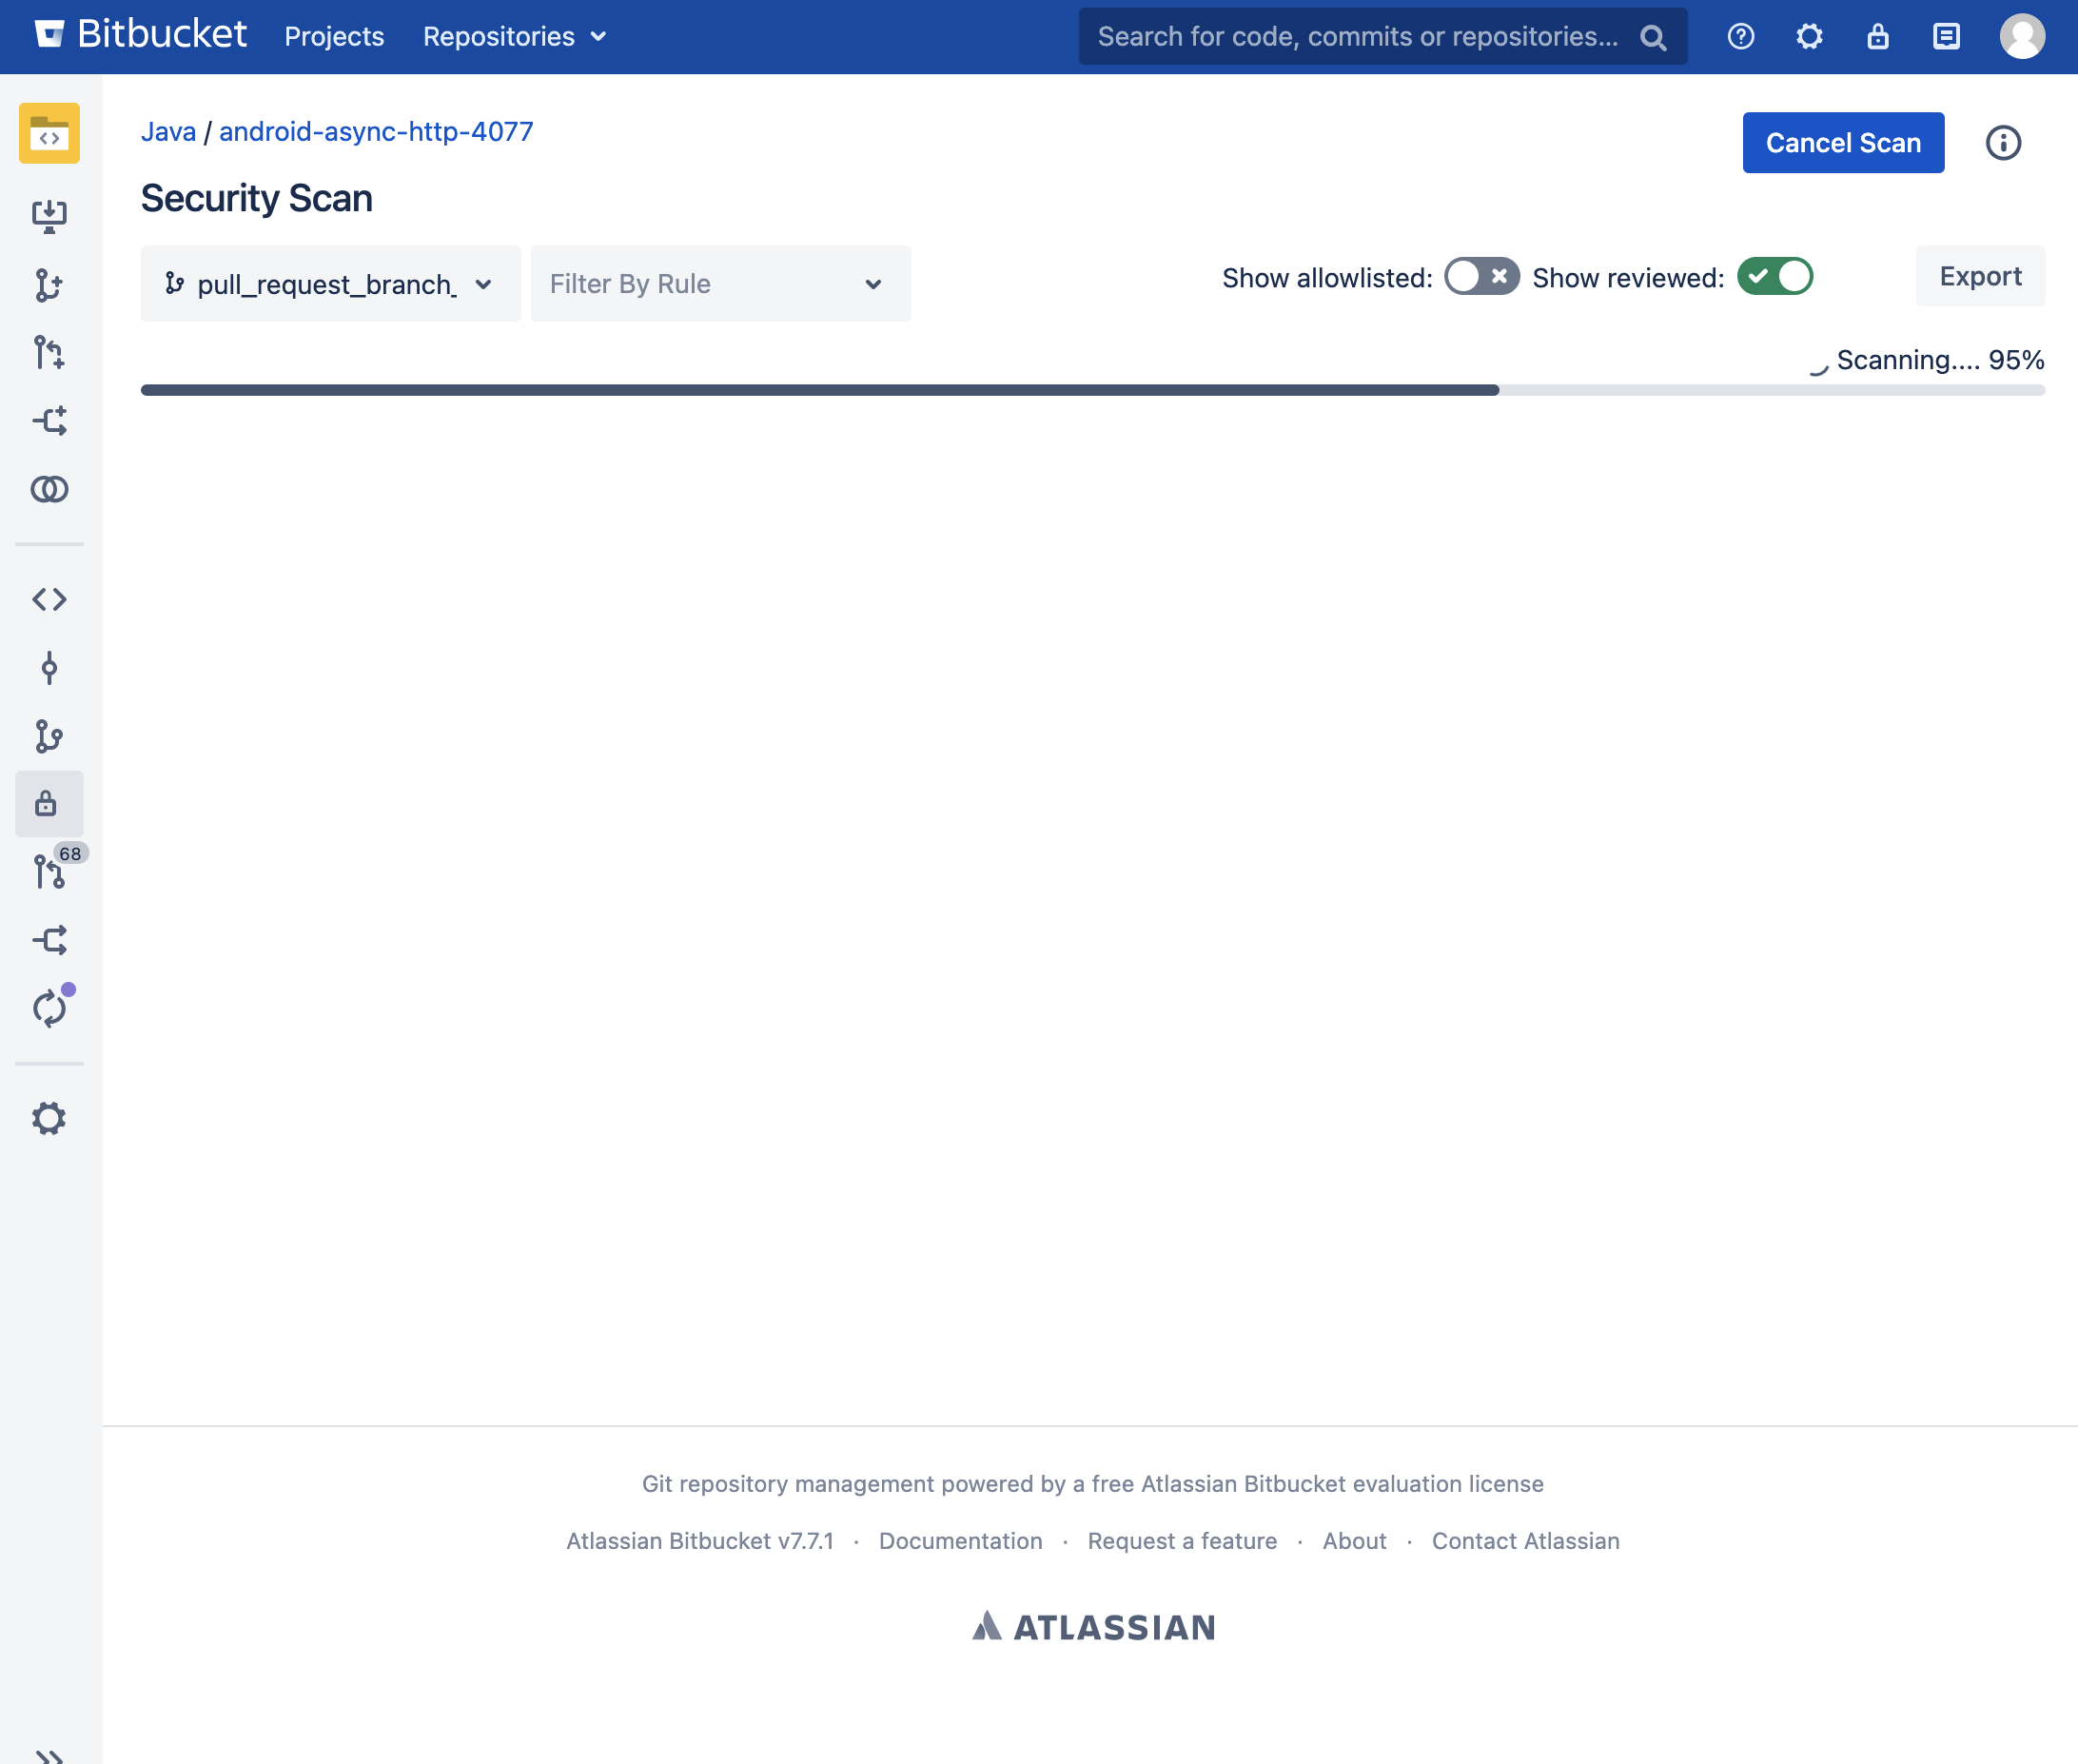
image-20210917-001412.png


Results of the scan can also be filtered by vulnerability type, and you can also choose the branch you would like to perform a scan on.